Check Point Patches Actively Exploited Management Server Zero-Day
Summary
Check Point says attackers are exploiting CVE-2026-93616, a path traversal flaw allowing unauthenticated script execution on several Management Server products. It released a hotfix and recommends temporary mitigations for customers unable to patch.
Key points
- CVE-2026-93616 is a path traversal flaw that can let unauthenticated attackers upload and execute arbitrary scripts.
- Check Point says the vulnerability is actively exploited and that a handful of customers have been attacked.
- Affected products include Security Management Server, Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent.
- Check Point addressed the flaw in the R82.20 Security Hotfix.
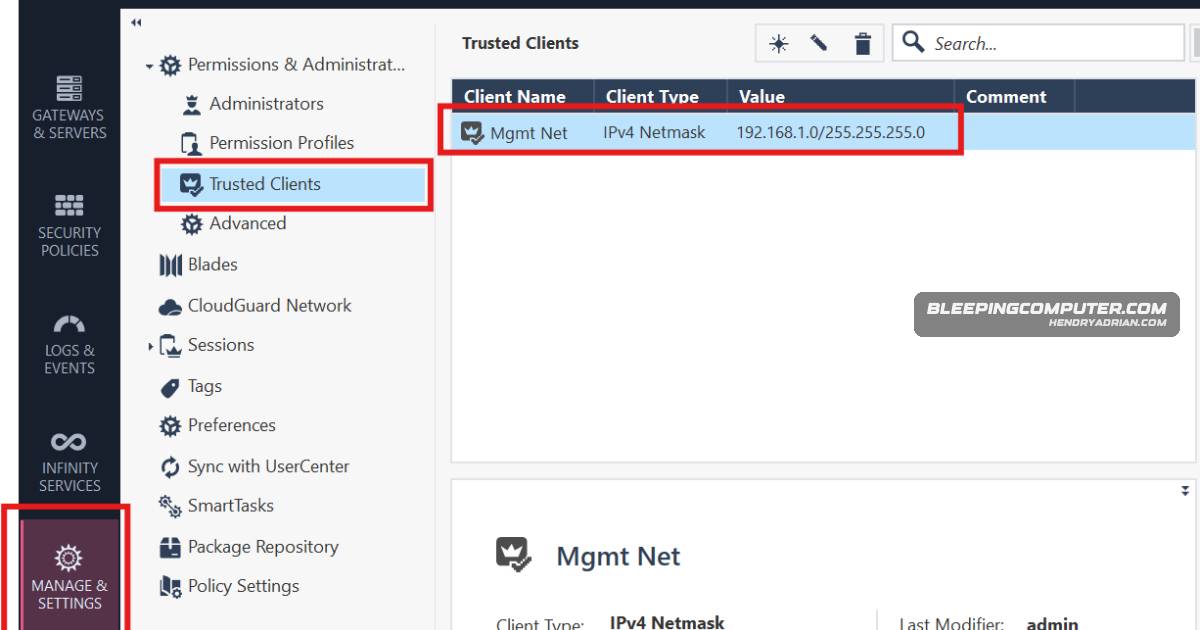
- Customers unable to patch immediately are advised to place vulnerable systems behind a firewall and restrict SmartConsole Trusted Clients to trusted IP addresses.
- Check Point advises security teams to check for signs of successful exploitation using indicators in its security advisory.
Article Details
- Vulnerability Types
- Path traversal
- Arbitrary script execution
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Place vulnerable systems behind a firewall.
- Restrict access to trusted IP addresses using Trusted Clients in SmartConsole.
CVE
Vendors
Products
Log ServerThe bug affects Security Management Server, Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent.Multi-Domain Log ServerThe bug affects Security Management Server, Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent.Multi-Domain Security Management ServerThe bug affects Security Management Server, Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent.Security Management ServerCheck Point Software released emergency hotfixes for CVE-2026-93616, a critical path traversal flaw in Security Management Server products that allowed unauthenticated attackers to upload and run arbitrary scripts.SmartConsole#CheckPointSmartEventThe bug affects Security Management Server, Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent.