
CISA Says Ransomware Gangs Are Exploiting Critical TeamCity Flaw
Summary
CISA says ransomware gangs are exploiting CVE-2026-63077, an unauthenticated command-execution flaw in TeamCity. JetBrains patched it in versions 2025.11.7 and 2026.1.3; administrators are urged to patch or restrict access.
Key points
- CISA added CVE-2026-63077 to its Known Exploited Vulnerabilities catalog and says ransomware gangs are exploiting it.
- The flaw lets unauthenticated attackers bypass authentication and execute operating-system commands through the TeamCity agent polling protocol.
- JetBrains patched the vulnerability in TeamCity On-Premises versions 2025.11.7 and 2026.1.3.
- JetBrains confirmed exploitation in the wild on August 7 and shared indicators of compromise.
- CISA gave U.S. federal agencies three days to secure their networks after adding the flaw to its catalog.
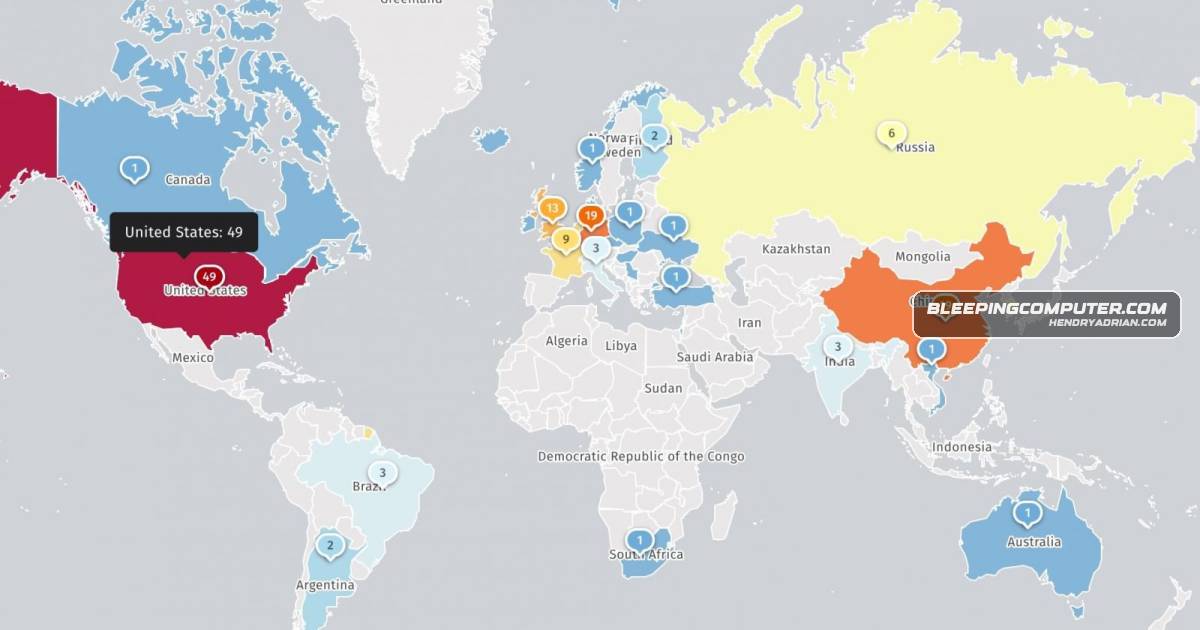
- Shadowserver was tracking just over 160 unpatched, internet-exposed TeamCity servers, down from an initial 700.
- Administrators are urged to patch exposed servers immediately or, if they cannot patch, restrict access to trusted networks.
Article Details
- Vulnerability Types
- Authentication bypass
- Remote command execution
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Limit access to trusted networks if servers cannot be patched immediately.
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe flaw allows unauthenticated attackers to execute arbitrary operating system commands with the privileges of the TeamCity server process.T1190 · Exploit Public-Facing ApplicationRansomware gangs are exploiting the TeamCity vulnerability against exposed servers.
CVE
Threat Actors
Vendors
Products
JetBrains TeamCityCISA warned that ransomware gangs are now exploiting a critical JetBrains TeamCity flaw, CVE-2026-63077, which allows unauthenticated attackers to bypass authentication and run arbitrary commands on affected servers.Zimbracyber agencies warned that APT29 hackers linked to Russia’s Foreign Intelligence Service (SVR) were targeting vulnerable JetBrains TeamCity and Zimbra servers “at a mass scale.”