cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

Check Point Reports Targeted Attacks on Management Server Zero-Day and Attempts Against VPN Flaw

Check Point says attackers used a management-server zero-day in limited attacks on July 23 and began trying to exploit a separate VPN flaw on September 12. Fixes and mitigation guidance are available for both.
Sep 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

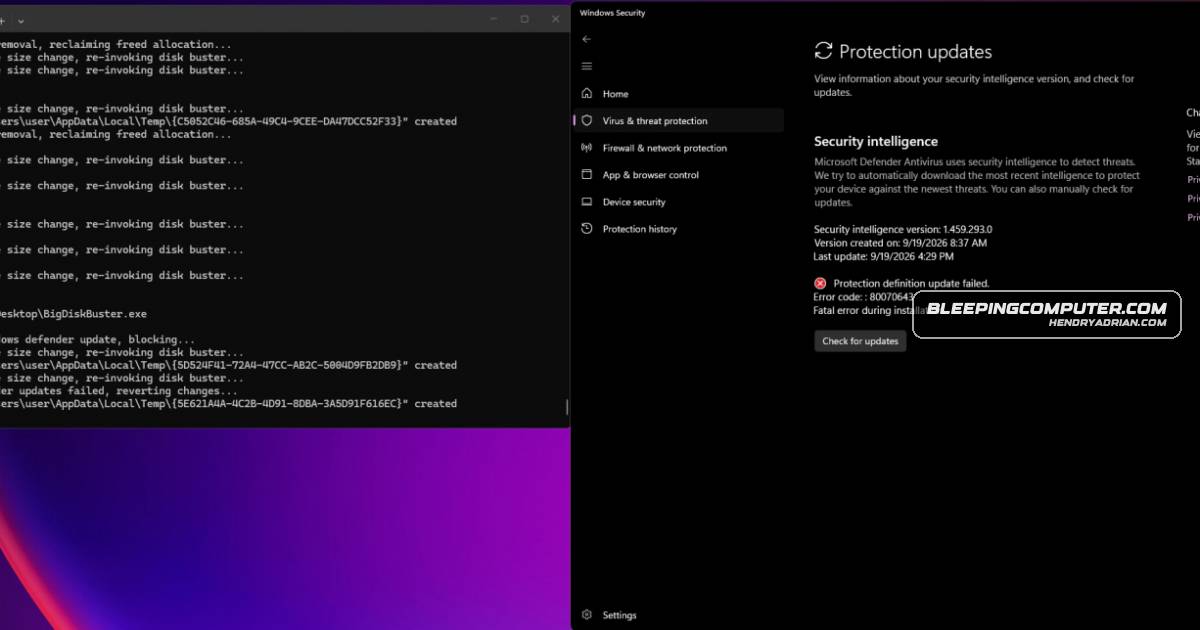
Researcher releases BigDiskBuster zero-day that blocks Microsoft Defender updates

Researcher Abdelhamid Naceri says BigDiskBuster can block Microsoft Defender signature and platform updates while running in the background. The article reports that some of Naceri’s disclosed Windows and Defender flaws remain unpatched.

Sep 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

D-Link warns of unauthenticated zero-day flaw in legacy DIR-822A routers

D-Link says an unauthenticated DHCP-server buffer overflow in legacy DIR-822A routers has a public PoC and no patch yet. It is investigating a second flaw and advises restricting internet exposure and management access.

Sep 22, 2026
Vulnerability & Exploit · securityweek.com

Researcher Releases BigDiskBuster PoC to Disrupt Microsoft Defender Updates

Abdelhamid Naceri, who used the names Nightmare Eclipse and others, released BigDiskBuster, a reportedly buggy PoC that prevents Defender updates. Microsoft says Defender detects and prevents observed activity and advises customers to update.

Sep 22, 2026
Vulnerability & Exploit · netspi.com

CVE-2026-78902: Crafted DNS Reply Enables XSS-to-RCE on pfSense

A flaw in pfBlockerNG on pfSense lets a crafted DNS reply trigger stored XSS when an administrator views Reports, potentially leading to root access. Netgate fixed the issue in pfBlockerNG 3.2.16_1.

Sep 22, 2026
Vulnerability & Exploit · securityweek.com

WordPress Patches Click2Shell Flaw That Could Enable Remote Code Execution

WordPress patched Click2Shell, a flaw that lets an unauthenticated attacker use a crafted URL and a logged-in administrator’s visit to install a theme and potentially execute PHP code on the site.

Sep 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Zyxel Switch Flaw

CISA ordered federal agencies to patch CVE-2026-7273 in Zyxel GS1900 switches. The flaw enables LAN-based command execution via crafted HTTP requests; GreyNoise reported 996 switches compromised and sensitive data exfiltrated.

Sep 22, 2026
Vulnerability & Exploit · fieldeffect.com

F5 Releases Hotfixes for Actively Exploited BIG-IP APM RCE Flaw

F5 reports active exploitation of CVE-2026-94127, a heap-based buffer overflow enabling unauthenticated RCE on specifically configured BIG-IP APM virtual servers. Hotfixes are available; F5 also provides an iRule mitigation.

Sep 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

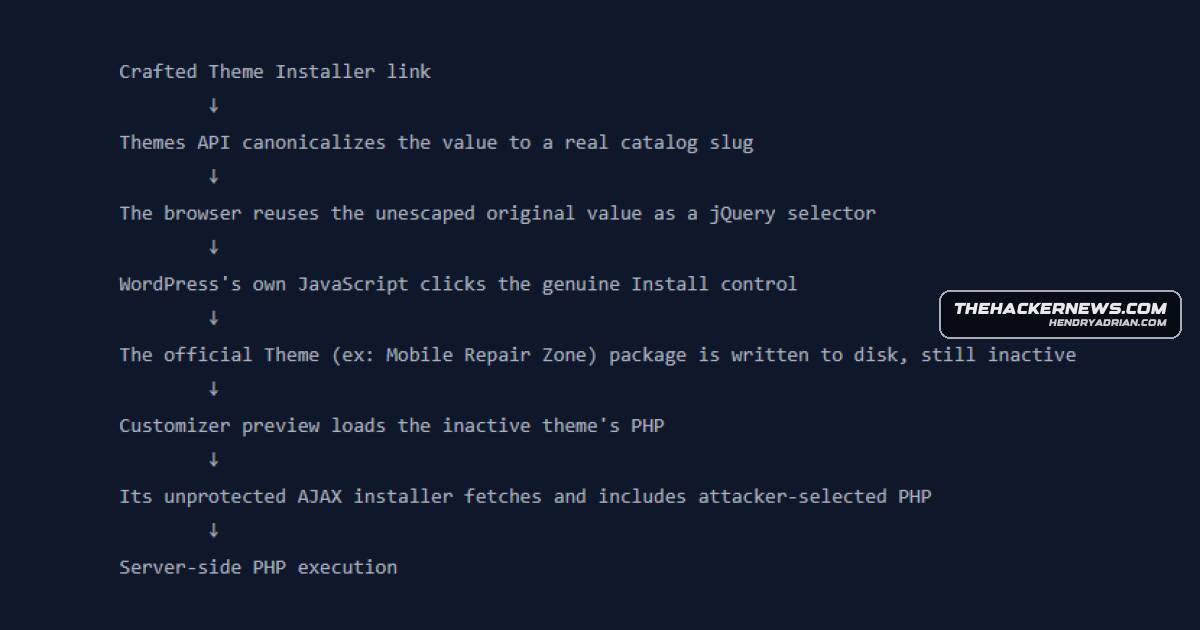
WordPress Click2Shell flaw enables server-side PHP execution via crafted link

Click2Shell chains a WordPress Core CSRF flaw with theme installation to enable server-side PHP execution when a logged-in administrator visits a crafted link. WordPress fixed the issue in version 7.1.1; technical details and a PoC are public.

Sep 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns Three Linux Kernel Flaws Are Under Active Exploitation

CISA says attackers are exploiting three Linux kernel flaws, including a critical 14-year-old vulnerability. Federal agencies must patch and conduct forensic triage; incident details have not been disclosed.

Sep 21, 2026
Vulnerability & Exploit · arstechnica.com

Meta Muse zero-day let local apps hijack assistant accounts; hotfix released

Researcher Patrick Wardle found that local apps or commands could redirect Muse’s cloud transcription and expose its account token, enabling account control. Meta said it released a hotfix patching the flaw.

Sep 21, 2026
Vulnerability & Exploit · securityweek.com

CISA Adds Three Exploited Linux Kernel Flaws to KEV Catalog

CISA added three Linux kernel vulnerabilities to its KEV catalog, citing potential denial of service, memory disclosure, crashes, and memory corruption. It urged federal agencies to patch them within three days; exploitation details were not shared.

Sep 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

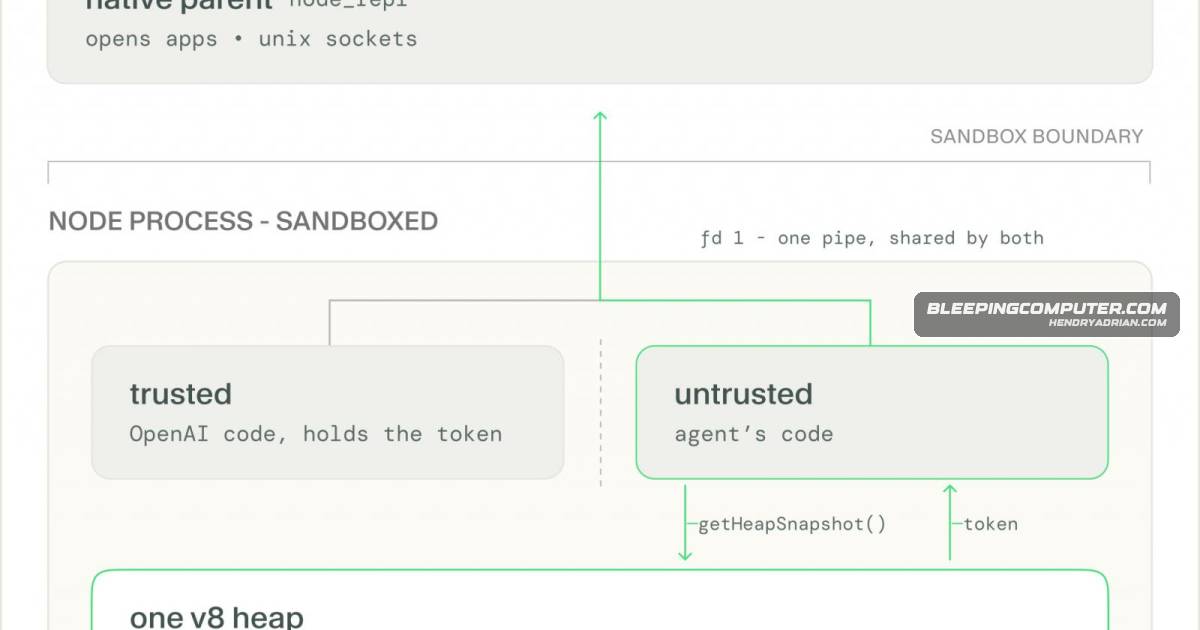
Researchers Detail Two OpenAI Codex Sandbox Escapes

Researchers described Heapjack and Overpatch, two flaws that could bypass OpenAI Codex sandbox restrictions and run commands on a developer’s machine. OpenAI patched both; users should update Codex Desktop or CLI.

Sep 20, 2026
Vulnerability & Exploit · thehackernews.com

SolarWinds Patches Access Rights Manager Flaw Enabling Unauthenticated RCE

SolarWinds patched CVE-2026-28326, a high-severity hard-coded-key flaw that could enable unauthenticated RCE in Access Rights Manager versions 2026.2 and earlier. It also released fixes for vulnerabilities in Web Help Desk and Serv-U.

Sep 19, 2026
Vulnerability & Exploit · cyberscoop.com

HEIF Heist Flaw in Image Decoders Could Enable Data Theft and Remote Code Execution

Researchers found that malicious HEIF, HEIC, and AVIF files could exploit flaws in libheif and libde265. The issue was patched, but unpatched deployments may remain at risk; researchers also reported using a chained flaw to access OpenAI repositories.

Sep 18, 2026
Vulnerability & Exploit · thehackernews.com

WordPress 7.1.1 Fixes Click2Shell Flaw That Can Lead to Server Code Execution

WordPress 7.1.1 fixes Click2Shell, which can trick a logged-in administrator into installing a theme from WordPress[.]org. Chained with a separate theme flaw, it can enable server code execution; no public exploitation has been reported.

Sep 18, 2026
Vulnerability & Exploit · thehackernews.com

Public Exploits Released for Four Linux Kernel Flaws That Can Grant Local Root

Working exploits are public for four patched Linux kernel flaws that can grant local root. Older kernels remain at risk; the article reports no real-world exploitation and recommends updating or temporarily disabling affected features.

Sep 18, 2026
Vulnerability & Exploit · helpnetsecurity.com

Plugin4Shell flaw enables zero-click code execution in four AI coding agents

AIR reports Plugin4Shell, a zero-click RCE in four AI coding agents that lets attackers bypass plugin SHA pinning. Anthropic and OpenAI patched; Microsoft has not, and Google deprecated Gemini CLI.

Sep 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

Check Point Patches Critical Flaw Enabling Root Code Execution on Management Servers

Check Point patched CVE-2026-91843, an unauthenticated stack overflow enabling root remote code execution on Security Management Server and Log Server systems, and provided mitigation and detection guidance.

Sep 18, 2026
Vulnerability & Exploit · cyberscoop.com

Cisco patches actively exploited maximum-severity ISE zero-day

Cisco says attackers exploited a maximum-severity Cisco ISE zero-day before a patch was available. The flaw enables remote authentication bypass and device takeover; Cisco released indicators of compromise and says no workaround is available.

Sep 18, 2026
Vulnerability & Exploit · fieldeffect.com

Critical SAP Extended Passport flaw can enable system compromise; patches available

CVE-2026-44756 is a critical SAP Extended Passport memory-corruption flaw reachable through HTTP(S), SAP GUI, and RFC. SAP released fixes; researchers report exploitation can enable OS command execution on affected hosts.

Sep 18, 2026
Vulnerability & Exploit · thehackernews.com

Critical Unbound DNSSEC Flaw Could Enable Remote Code Execution; Version 1.26.1 Fixes Nine Vulnerabilities

Unbound versions through 1.26.0 are affected by a DNSSEC validator heap overflow that may allow remote code execution via a malicious zone. Version 1.26.1 fixes it and eight other flaws; exploitation has not been reported.

Sep 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Actively Exploited ISE Authentication Bypass

Cisco says attackers are exploiting CVE-2026-76460, an authentication bypass in ISE and ISE-PIC. No workaround exists; Cisco and CISA urge patching, and Cisco advises investigating logs and re-imaging systems if compromise is suspected.

Sep 17, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches Actively Exploited Critical ISE Authentication Bypass Zero-Day

Cisco patched CVE-2026-76460, an actively exploited authentication bypass affecting ISE and ISE-PIC. The flaw can enable root command execution; Cisco recommends upgrading, while iACLs can prevent remote exploitation.

Sep 17, 2026
PreviousPage 29 of 65 Next
© 2026 cyber.hendryadrian.com