
GitLab Incoming Email Token Can Let Attackers Commit Code and Run CI Jobs as Account Holders
Summary
Aikido Security found that GitLab’s non-expiring incoming-email token can let anyone who obtains it create commits and trigger CI jobs with the account holder’s permissions, bypassing IP restrictions and 2FA. Users can reset the token.
Key points
- Aikido Security reported that GitLab’s incoming-email token is shared across projects accessible to the account and does not expire.
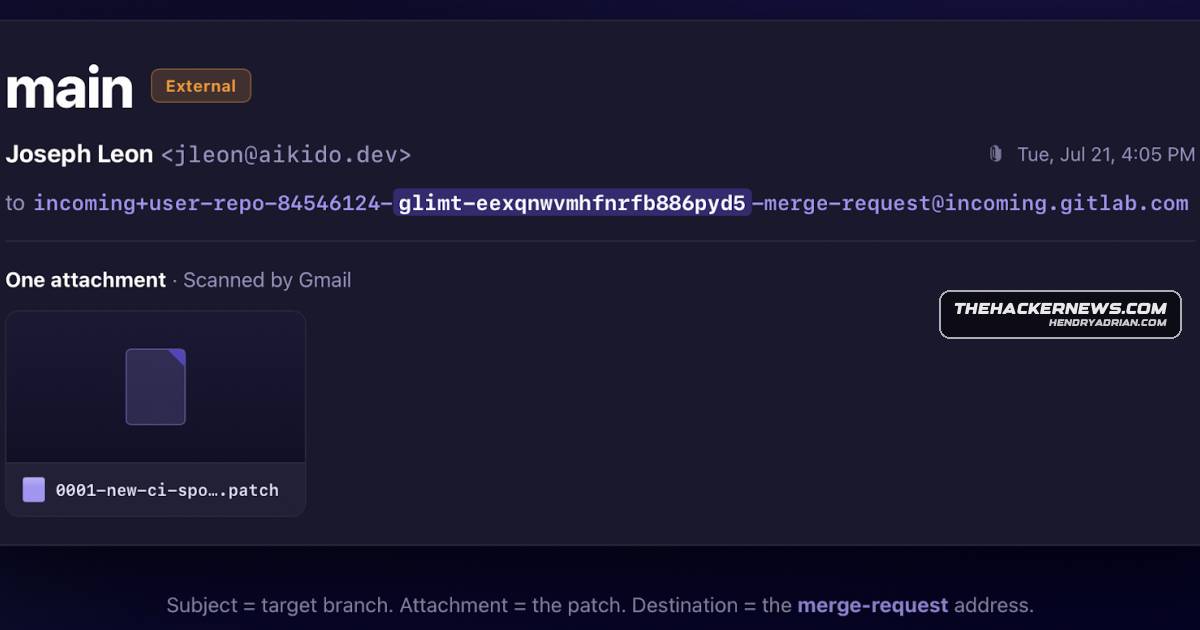
- Anyone with the token can email issues or merge requests; GitLab does not verify the sender’s identity.
- An attacker can email a patch to a target branch, potentially including main, and have GitLab commit it as the account holder.
- If the patch changes .gitlab-ci.yml and the user’s permissions allow it, the attacker can trigger CI jobs as that user.
- Incoming-email actions bypass IP restrictions and 2FA; the impact depends on the account’s permissions. Aikido said it demonstrated a commit reaching main despite an IP restriction.
- Users can reset the token from the personal access tokens page; self-managed instance administrators can disable incoming email instance-wide.
- GitLab is considering limiting incoming emails to verified account addresses, but that change is not yet in place.
Article Details
- Vulnerability Types
- Long-lived credential exposure and abuse
- Authentication and IP restriction bypass
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- unavailable
- Workarounds
- Reset the incoming email token to invalidate existing project email addresses.
- On self-managed instances, disable incoming email for the instance.
Products
GitLabGitLab’s incoming email address is effectively a long-lived credential that can be abused to create issues, merge requests, and even commit code as the account holder if it is leaked.GitLab DedicatedGitLab Dedicated does not appear to be affected, because GitLab limits the feature to self-managed and GitLab.com, but Aikido said it could not test Dedicated directly.