
Attackers Actively Exploit Critical Roundcube SQL Injection Flaw
Summary
Canada’s Cyber Centre says attackers are exploiting CVE-2026-48842, a pre-authentication SQL injection flaw in Roundcube’s virtuser_query plugin. Admins should upgrade to patched versions or disable the plugin.
Key points
- The Canadian Centre for Cyber Security says CVE-2026-48842 is being exploited in the wild.
- The flaw is a pre-authentication SQL injection vulnerability in Roundcube’s virtuser_query plugin.
- Successful exploitation can bypass authentication, run malicious database commands, and potentially steal database data.
- Roundcube versions 1.6.16 and 1.7.1 include fixes for the flaw.
- Administrators unable to patch immediately are advised to disable or remove virtuser_query.
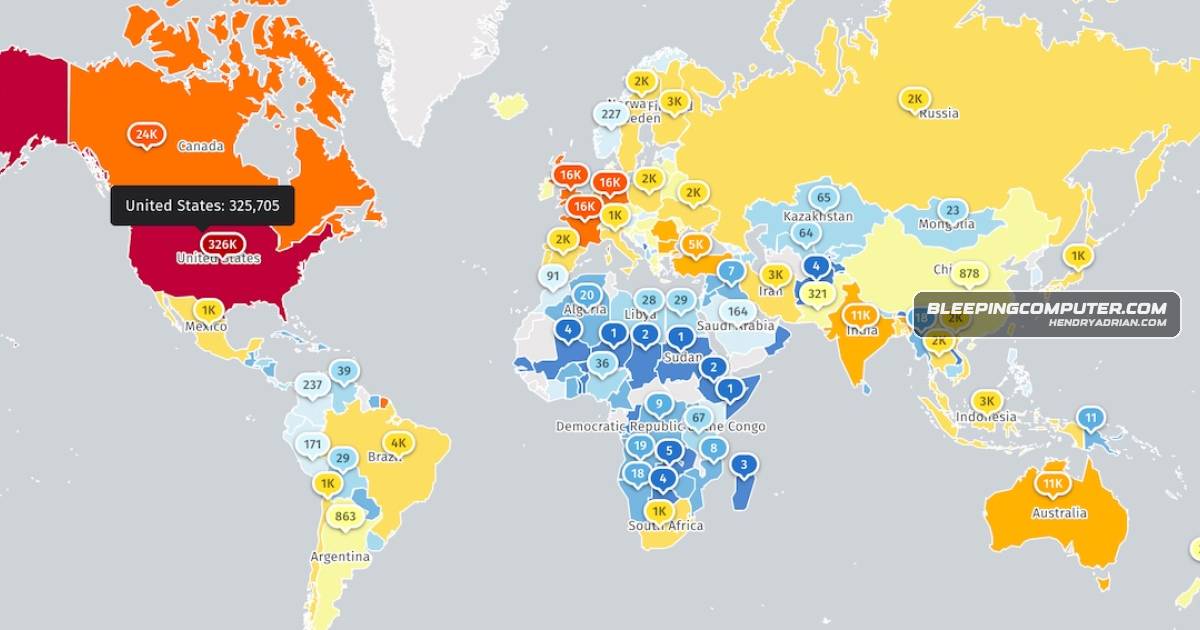
- Shadowserver tracks more than 523,000 Roundcube instances exposed online; the article says it is unknown how many are honeypots or already patched.
Article Details
- Vulnerability Types
- Pre-authenticated SQL injection
- Severity
- High
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Disable or remove the virtuser_query plugin if unable to upgrade immediately.