
F5 Patches Actively Exploited BIG-IP APM Zero-Day Enabling Remote Code Execution
Summary
F5 patched actively exploited CVE-2026-94127, a BIG-IP APM flaw that can enable remote code execution when specific OAuth authorization server settings are configured. CISA added it to its KEV Catalog and set a federal patch deadline.
Key points
- CVE-2026-94127 affects BIG-IP APM configured with an OAuth Authorization Server profile, an access policy, and an OAuth profile on a virtual server.
- F5 says the vulnerability has been exploited and warns that deployments using APM only as an OAuth Client or Resource Server are not affected.
- F5 released security updates; administrators unable to patch immediately can apply an iRule from F5 Support as a mitigation.
- F5 recommends checking for indicators of compromise when multiple OAuth authentication failures and suspicious commands are followed by a TMM SIGABRT.
- CISA added the flaw to its Known Exploited Vulnerabilities Catalog and directed U.S. federal agencies to secure affected systems by Friday.
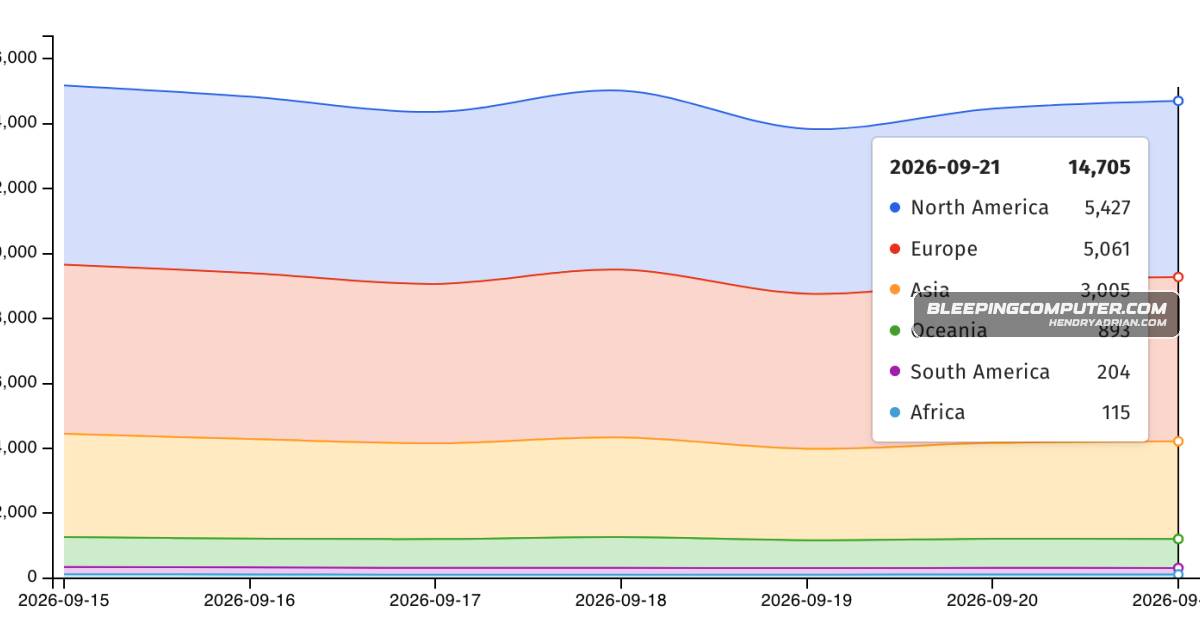
- Shadowserver tracks more than 14,700 IP addresses with BIG-IP APM fingerprints, but the article says the number already patched or operating as honeypots is unknown.
Article Details
- Vulnerability Types
- Remote code execution
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Apply an iRule, available from F5 Support, to the affected BIG-IP APM virtual server if security updates cannot be installed immediately.