cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2502 articles

Threat Research · hunt.io

Exposed Servers Reveal Scanning and BlueShell Tools Targeting Asian Organizations

Hunt researchers found exposed servers containing SQLMap and Nmap scans, reconnaissance tools, scripts, and files linked to the BlueShell backdoor, with activity targeting government and institutional organizations in Taiwan and elsewhere in Asia.
Jun 18, 2024
Threat Research · group-ib.com

Cron Android Banking Gang Infected Over One Million Devices Before Arrests

Group-IB details how the Cron group used Android banking Trojans to steal more than $800,000, infect over one million devices, and target customers of 50 Russian banks before law enforcement arrested its members.

Jun 13, 2024
Threat Research · hunt.io

Researchers Find Customized Certificates on Gh0st and Pantegana RAT Infrastructure

Hunt IO identified Gh0st and Pantegana RAT infrastructure, including Pantegana-like certificates with altered fields that may evade scanners relying on default certificate details.

Jun 12, 2024
Threat Research · wiz.io

DERO Cryptojacking Campaign Adapts to Evade Kubernetes Defenses

Wiz details an active DERO cryptojacking campaign abusing exposed Kubernetes APIs with overly permissive anonymous access. Attackers deployed disguised, packed miners with embedded wallet and pool data; the report provides technical findings, IOCs and mitigation advice.

Jun 7, 2024
Threat Research · hunt.io

TLS Certificates Reveal LightSpy and WyrmSpy Infrastructure Patterns

Hunt IO analyzes LightSpy and WyrmSpy infrastructure, showing how TLS certificate patterns, ports, hosting, and server details can help researchers identify and track related servers.

Jun 6, 2024
Threat Research · hunt.io

Researchers Find PlugX Builder, Controller and Possible Victim Data on Exposed Server

Hunt researchers found an exposed server containing a PlugX builder and controller, Korplug samples, and files that may contain data from infected hosts. A VBA script downloaded PlugX files from a Nepalese government website.

Jun 5, 2024
Threat Research · hunt.io

Researchers Map SolarMarker Infrastructure and Find Shared SSH Keys Across 100+ Servers

Hunt researchers identified 20 suspected SolarMarker servers and found a shared SSH key on more than 100 servers. Their analysis also surfaced hosting patterns, other services, and domains suspected of impersonating financial providers.

May 30, 2024
Threat Research · threatfabric.com

LightSpy macOS Spyware Used WebKit Exploits and 10 Data-Stealing Plugins

ThreatFabric details LightSpy’s macOS infection chain, two WebKit exploits, and 10 plugins for collecting data including files, Keychain contents, browser history, audio, and screen recordings. Researchers found a misconfigured operator panel but no confirmed real-world

May 29, 2024
Threat Research · hunt.io

Internet Scans Find 34 Yakit Instances Alongside Cobalt Strike and Other Red-Team Tools

Hunt IO identified 34 internet-facing Yakit instances and found some infrastructure also hosted ARL, Cobalt Strike, Cobalt Strike Cat, or SuperShell. The article cautions that Yakit use alone does not indicate malicious activity.

May 28, 2024
Threat Research · wiz.io

Wiz Researchers Detail Cross-Tenant Vulnerability in Replicate AI Platform

Wiz researchers used a malicious Cog container and TCP injection into an authenticated Redis connection to access and alter other customers’ prompts and outputs. Replicate fixed the issue after disclosure in January 2024; no customer data was compromised.

May 23, 2024
Threat Research · huntress.com

Huntress Details HTML-Smuggling Phishing Technique That Could Bypass MFA

Huntress analyzed a phishing campaign using HTML smuggling to render a proxied Outlook login iframe; researchers say stolen session tokens could enable MFA bypass. The mechanism was investigated, but victim impact and tooling were not confirmed.

May 23, 2024
Threat Research · hunt.io

Researchers Find Malware-Hosting Infrastructure by Revisiting Past Threat Reports

An investigation used IPs from historical threat reports to find open directories and malware-hosting infrastructure, including files associated with Empire, Meterpreter, PurpleFox, GhostRAT, and AsyncRAT.

May 21, 2024
Threat Research · hunt.io

Hunt Finds More Than 400 Exposed Viper Servers and Maps Related C2 Tools

Hunt tracked over 400 internet-exposed Viper login pages and found many hosted in China on Tencent infrastructure. Its scanning also linked Viper deployments with Cobalt Strike, Sliver, and Yakit.

May 8, 2024
Threat Research · huntress.com

Huntress Details Multi-Endpoint Activity Before INC Ransomware Deployment

Huntress analysts traced a recurring pattern before INC ransomware deployment, including attempts to disable security tools and prepare data for collection. Hunting for the pattern helped identify other potentially affected endpoints and alert customers.

May 1, 2024
Threat Research · huntress.com

Huntress Uncovers LightSpy macOS Variant and Details Its Multi-Stage Implant

Huntress analyzed a LightSpy variant targeting macOS, detailing its dropper, implant, plugins, and command-and-control behavior. The researchers caution that the sample alone does not establish an active campaign.

Apr 25, 2024
Threat Research · threatfabric.com

Brokewell Android Malware Steals Banking Data and Enables Remote Device Control

ThreatFabric describes Brokewell, Android malware distributed through a fake browser update that steals credentials, cookies and device data, and enables remote control. Researchers link its developer to a publicly available loader bypassing Android 13+ restrictions.

Apr 25, 2024
Threat Research · blog.talosintelligence.com

Cisco Details ArcaneDoor Espionage Campaign Targeting Perimeter Devices

Cisco Talos details ArcaneDoor, a state-sponsored espionage campaign targeting network perimeter devices, including Cisco ASA appliances. Attackers used Line Dancer and Line Runner backdoors; Cisco advises patching affected devices and provides detection guidance.

Apr 24, 2024
Threat Research · blog.talosintelligence.com

Suspected CoralRaider Campaign Delivers Three Infostealers via PowerShell

Cisco Talos details an ongoing campaign, attributed to CoralRaider with moderate confidence, that uses malicious Windows shortcuts, PowerShell and CDN-hosted files to deliver CryptBot, LummaC2 or Rhadamanthys.

Apr 23, 2024
Threat Research · hunt.io

Researchers Analyze SparkRAT C2 Infrastructure and Malware Delivery

Hunt researchers analyze SparkRAT’s authentication, C2 behavior, and suspected infrastructure, and use sandbox findings to examine an SFX archive that deploys the RAT.

Apr 23, 2024
Threat Research · blog.talosintelligence.com

OfflRouter Malware Has Infected Ukrainian Documents Since 2015, Exposing Confidential Files

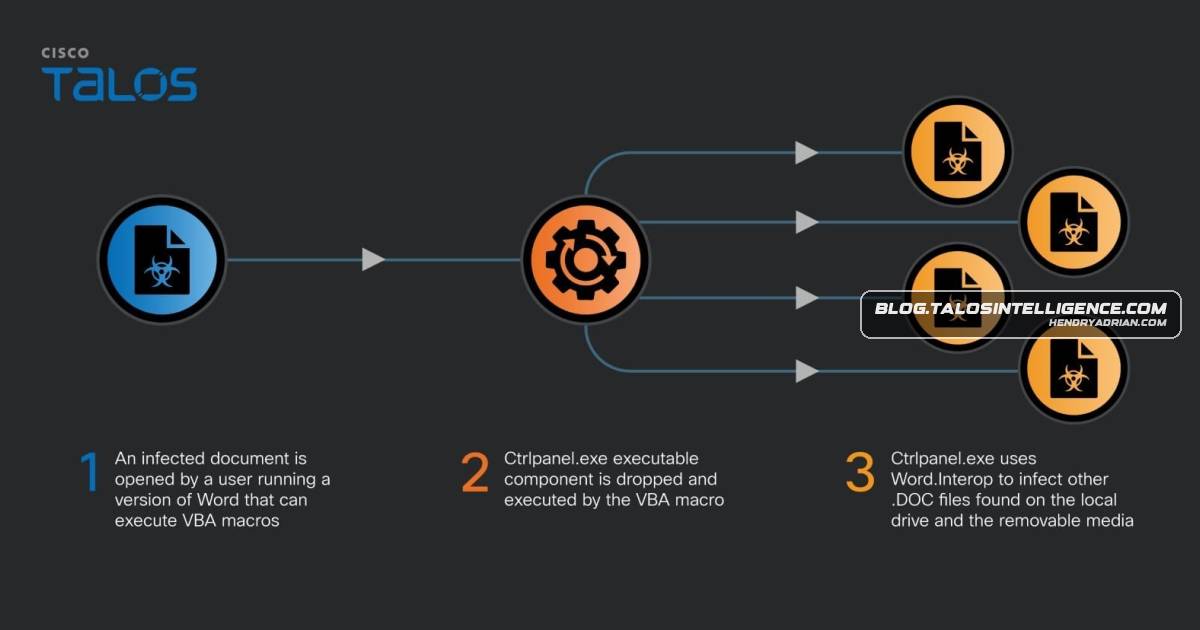
Cisco Talos found more than 100 Ukrainian documents infected by OfflRouter, a multi-module VBA and .NET virus active since 2015. The malware spreads through Word documents and removable drives, and infected documents have been uploaded to public repositories such as the

Apr 17, 2024
Threat Research · hunt.io

Open Directory Exposes SuperShell Payloads and a Cobalt Strike Beacon

An investigation of an exposed server uncovered two SuperShell payloads and a Linux Cobalt Strike beacon, along with associated command-and-control infrastructure and an ARL service.

Apr 16, 2024
Threat Research · blog.talosintelligence.com

Starry Addax Uses FlexStarling Android Malware to Target Human Rights Activists in North Africa

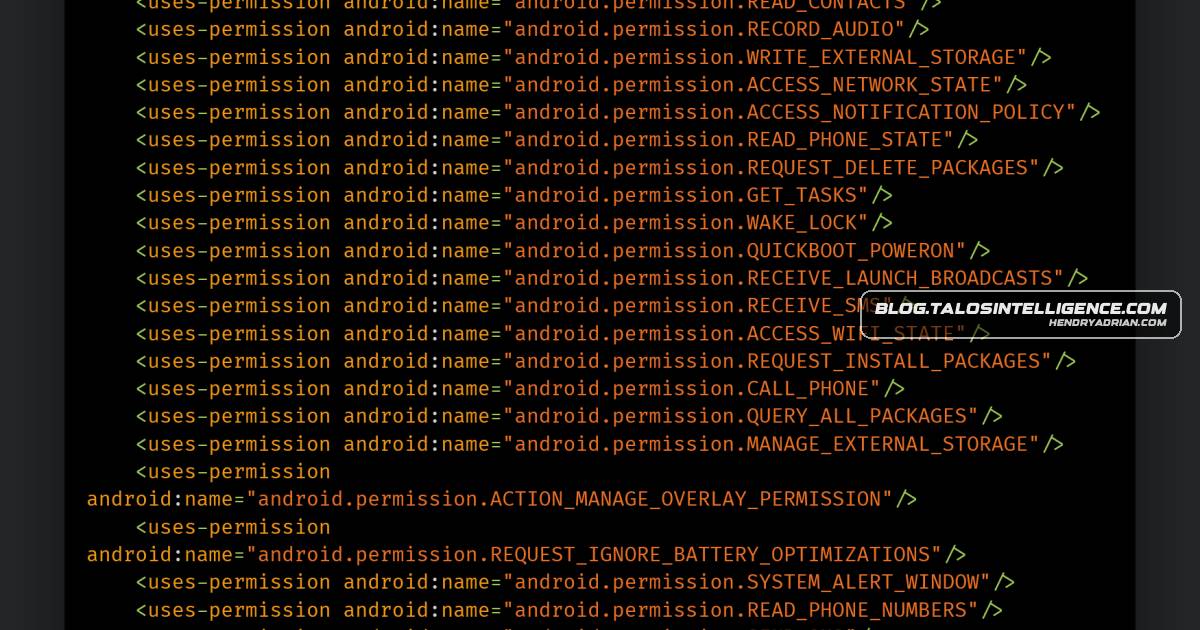
Cisco Talos details Starry Addax phishing campaigns targeting human rights activists linked to the Sahrawi cause with Android malware that can steal data and deploy components, and Windows credential-harvesting pages.

Apr 9, 2024
Threat Research · hunt.io

BlueShell Backdoor Remains in Use, With Attackers Modifying Its Capabilities

Researchers describe BlueShell’s continued use, tracked C2 servers, and a customized Linux ELF sample with added file-server and reverse-shell features. The backdoor has been reported in attacks targeting organizations in South Korea and Thailand.

Apr 9, 2024
Threat Research · wiz.io

Wiz researchers demonstrate cross-tenant attack paths in Hugging Face AI services

Wiz researchers report using a malicious pickle-based model and container-build weaknesses to demonstrate code execution and cross-tenant risks in Hugging Face services. Hugging Face collaborated on the findings and added security scanning.

Apr 4, 2024
PreviousPage 98 of 105 Next
© 2026 cyber.hendryadrian.com