cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2501 articles

Threat Research · wiz.io

AWS Console Sessions Can Obscure the Identity Behind CloudTrail Activity

Wiz describes how attackers with stolen AWS credentials can use assumed roles and console sessions to complicate CloudTrail identity tracing, and explains how SourceIdentity or matching log fields can restore traceability.
Aug 22, 2024
Threat Research · team-cymru.com

Team Cymru Maps Potential FIN7 Infrastructure Across Two Hosting Clusters

Team Cymru, Silent Push and Stark identified 25 Stark-assigned IPs potentially linked to FIN7 activity and two clusters communicating with those hosts. Stark suspended the reported services; the activity attribution remains an assessment.

Aug 13, 2024
Threat Research · hunt.io

Researchers Detail EvilGophish Phishing Infrastructure, Evasion Tactics, and Detection Clues

Hunt researchers describe EvilGophish’s phishing infrastructure and evasion tactics, including Turnstile pages and redirect rules, and explain how login-page text and URL patterns can reveal servers and associated domains.

Aug 13, 2024
Threat Research · wiz.io

Wiz Traces AWS Credential-Phishing Campaign Through Redirects and Related Domains

Wiz investigated an AWS credential-phishing email, traced its redirect chain to a fake sign-in page, and identified related domains through historical DNS and lookalike searches. The attacker’s intent and infrastructure links remain partly unconfirmed.

Aug 8, 2024
Threat Research · team-cymru.com

Team Cymru Tracks Quad7’s 7777 and 63256 Router Botnets

Team Cymru used port banners and NetFlow to identify 12,783 hosts potentially linked to Quad7’s 7777 and 63256 botnets, map seven management IPs, and connect activity to router types and proxied brute-force attacks.

Aug 8, 2024
Threat Research · hunt.io

Open Directory Exposes Government Credentials and Possible Phishing Targets

Hunt researchers found an exposed server containing pentesting tools, test results, credentials attributed to Egyptian government entities, and email lists or spoofing domains related to government organizations in five other countries. The server’s origin and intent is

Aug 7, 2024
Threat Research · darktrace.com

Safelink Smuggling Reuses Rewritten Links to Evade Email Security

Darktrace describes Safelink Smuggling, in which attackers get malicious links rewritten by email security services and reuse them in phishing or supply-chain attacks. It reports more than 300,000 suspicious cases over three months.

Aug 2, 2024
Threat Research · hunt.io

Mac Malware Impersonates The Unarchiver to Steal User Data

Researchers analyzed a malicious macOS disk image distributed through a spoofed Unarchiver site. Its Swift binary downloads scripts that collect user data and send it to an attacker-controlled server.

Jul 30, 2024
Threat Research · wiz.io

SeleniumGreed Campaign Exploits Exposed Selenium Grid to Deploy XMRig Miners

Wiz researchers detail an active campaign abusing exposed, unauthenticated Selenium Grid services to run remote commands and deploy XMRig miners, and recommend restricting access, enabling authentication, and monitoring workloads.

Jul 25, 2024
Threat Research · huntress.com

Fake MicroDicom Site Distributed Installer With Persistent SSH Backdoor

Huntress found a fake MicroDicom site distributing an oversized installer that bundled OpenSSH and installed a persistent service and SSH tunnel. The activity affected endpoints at two medical organizations; no data theft is reported.

Jul 23, 2024
Threat Research · hunt.io

Researchers Identify Suspected Oyster Backdoor Infrastructure Using JARM and HTML Hashes

Hunt.io used a JARM fingerprint and HTML response hash to identify four suspected Oyster backdoor domains hosted on OVH, then corroborated findings with VirusTotal and CleanUp.dll connections.

Jul 23, 2024
Threat Research · wiz.io

Wiz Researchers Detail SAP AI Core Vulnerability Chain That Exposed Customer Secrets

Wiz researchers say vulnerabilities in SAP AI Core let them bypass network restrictions, access internal services and customer cloud credentials, and take over the Kubernetes cluster. SAP fixed the issues; Wiz says no customer data was compromised.

Jul 17, 2024
Threat Research · huntress.com

Fake Browser Updates Deploy AsyncRAT and Malicious BOINC Clients

Huntress traced fake-browser-update infections to fileless AsyncRAT and BOINC clients repurposed as C2. Two malicious BOINC servers had about 10,000 connected clients, but researchers observed no tasks issued or further payloads.

Jul 17, 2024
Threat Research · hunt.io

SEO-Poisoned Software Sites Spread Poseidon, Gh0stRAT and Other Malware

Hunt researchers found fake Signal, TradingView, AICoin, and Sleipnir download sites distributing malware, including Poseidon and a Gh0stRAT variant, through poisoned search results and typosquatted domains.

Jul 16, 2024
Threat Research · hunt.io

Researchers Identify Five Servers Potentially Linked to SpiceRAT

Hunt.io researchers matched a distinctive HTML response to five IP addresses potentially linked to SpiceRAT, examined associated domains, and reported that only one was still active at the time of publication.

Jul 11, 2024
Threat Research · darktrace.com

Darktrace Details Network Activity in Qilin Ransomware Cases

Darktrace analyzed three probable Qilin ransomware cases from 2022–2024, detailing intrusion activity, malware, and data exfiltration across customer networks, including one case with more than 783 GB transferred.

Jul 4, 2024
Threat Research · hunt.io

ProxyLogon and ProxyShell Exploited to Steal Government Emails Across Four Countries

Hunt researchers found scripts exploiting ProxyLogon and ProxyShell to target government mail systems in Afghanistan, Laos, Georgia, and Argentina. An exposed server held thousands of files, including stolen emails and targeting scripts.

Jul 2, 2024
Threat Research · group-ib.com

TipTop Android Malware Group Infected 800,000 Phones Before Members Were Arrested

Group-IB says the TipTop group used fake Android apps and banking Trojans from 2015 to 2019 to steal from Russian bank customers. A coordinated operation led to arrests and prosecutions of group members.

Jun 28, 2024
Threat Research · hunt.io

Researchers Trace Geacon_Pro Infrastructure and Linux and Windows Payloads

Hunt researchers analyzed suspected Geacon_Pro servers, exposed directories, deployment scripts, and Linux and Windows payloads, including a webshell. They caution that certificate matches alone cannot confirm malicious use.

Jun 27, 2024
Threat Research · hunt.io

XenoRAT Disguised as Roblox Tools Spreads Through .gg Domains and GitHub

Hunt researchers found XenoRAT and other malware distributed through .gg command-and-control domains and a GitHub account posing as a Roblox scripting-tool source, with a video urging users to disable Windows Defender.

Jun 25, 2024
Threat Research · blog.talosintelligence.com

SneakyChef Uses SpiceRAT in Phishing Campaign Targeting Government Agencies

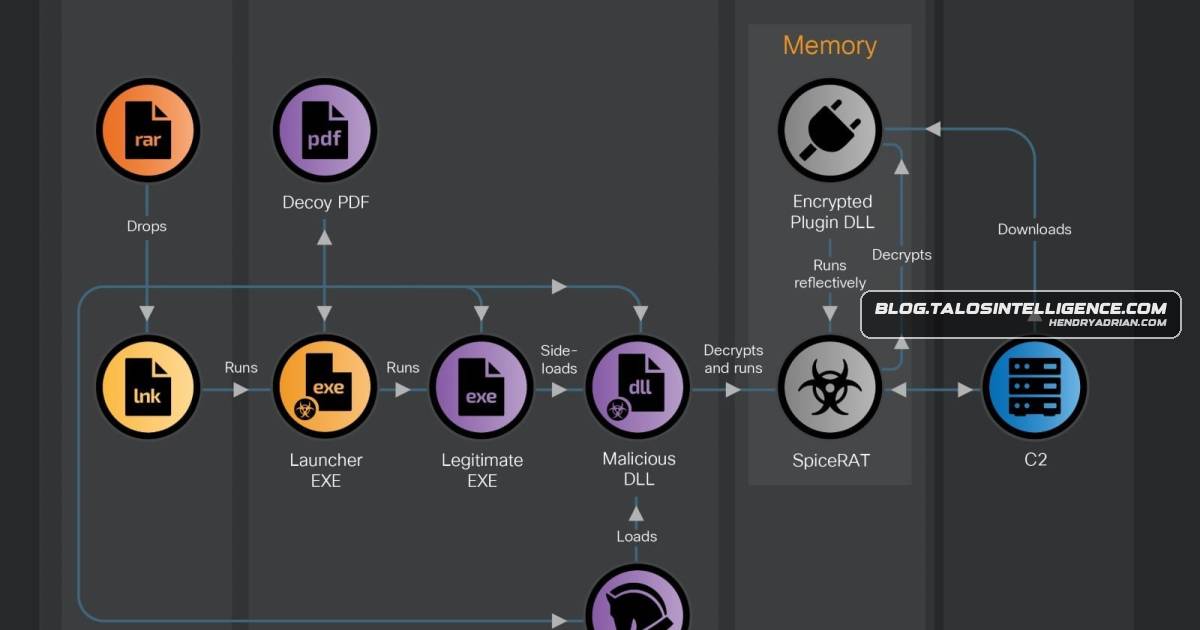
Cisco Talos details SneakyChef phishing campaigns delivering SpiceRAT and SugarGh0st to government agencies in EMEA and Asia, describing two infection chains, malware capabilities, C2 communications, and indicators of compromise.

Jun 21, 2024
Threat Research · blog.talosintelligence.com

SneakyChef Uses SFX RARs to Deliver SugarGh0st RAT in Government-Targeting Campaign

Talos reports that SneakyChef expanded SugarGh0st RAT operations across EMEA and Asia, using government-themed lures and a new SFX RAR infection chain that drops malware and establishes logon persistence.

Jun 21, 2024
Threat Research · hunt.io

SpyNote Android Spyware Disguised as Translate, Temp Mail and Banking Apps

Researchers found more than 40 SpyNote APKs in open directories, including samples disguised as Google Translate, Temp Mail and a German bank app. The samples collected sensitive data and contacted identified command-and-control infrastructure.

Jun 20, 2024
Threat Research · hunt.io

Exposed Servers Reveal Scanning and BlueShell Tools Targeting Asian Organizations

Hunt researchers found exposed servers containing SQLMap and Nmap scans, reconnaissance tools, scripts, and files linked to the BlueShell backdoor, with activity targeting government and institutional organizations in Taiwan and elsewhere in Asia.

Jun 18, 2024
PreviousPage 97 of 105 Next
© 2026 cyber.hendryadrian.com