Suspected CoralRaider Campaign Delivers Three Infostealers via PowerShell
Summary
Cisco Talos details an ongoing campaign, attributed to CoralRaider with moderate confidence, that uses malicious Windows shortcuts, PowerShell and CDN-hosted files to deliver CryptBot, LummaC2 or Rhadamanthys.
Key points
- Talos observed the campaign from at least February 2024 and assessed with moderate confidence that it is operated by CoralRaider, based on overlaps with the actor’s Rotbot campaign.
- The attack begins with a ZIP-distributed malicious Windows shortcut, likely delivered through phishing or drive-by downloads, that launches a CDN-hosted HTA file.
- Obfuscated JavaScript and PowerShell decrypt and run a loader, which uses FoDHelper and registry changes to bypass UAC and add ProgramData to Windows Defender exclusions.
- The loader downloads and runs one of three information stealers: CryptBot, LummaC2 or Rhadamanthys.
- The malware targets credentials and other sensitive information, including browser data, cryptocurrency wallets and financial information; described variants also target password-manager databases, authenticator information and Discord credentials.
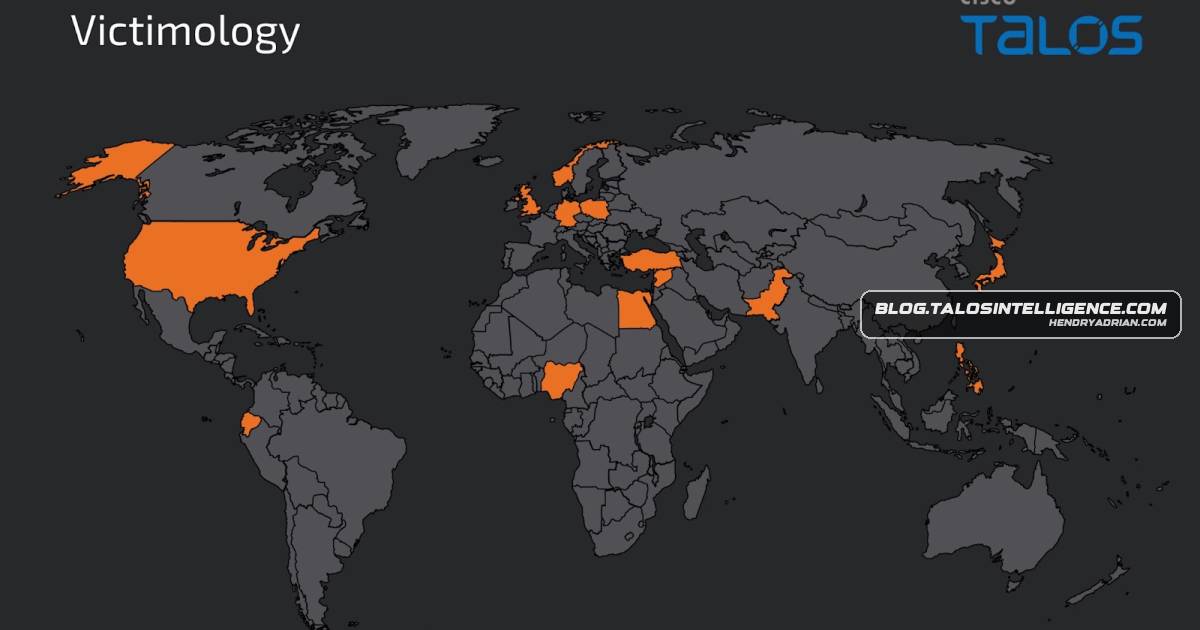
- Talos telemetry indicated victims across multiple countries and business sectors, including users in Japanese computer-service call centers and Syrian civil-defense organizations.
Article Details
- Attack Vectors
- A victim opens a malicious Windows Shortcut file inside a ZIP file downloaded through a drive-by download; Talos says the ZIP may be delivered through phishing links.
- The shortcut runs PowerShell to download and execute a malicious HTA file hosted on CDN cache URLs.
- The HTA runs embedded JavaScript that decodes and executes a PowerShell decryptor, which decrypts and runs a PowerShell loader.
- The loader uses FoDHelper.exe and registry ProgID/CurVer configuration to bypass UAC, adds ProgramData to Windows Defender exclusions, and downloads and runs an information stealer.
- The campaign delivers Cryptbot, LummaC2, or Rhadamanthys. The Rhadamanthys loader injects the malware into a selected process.
- Defensive Notes
- Talos recommends Cisco Secure Endpoint, Secure Web Appliance, Secure Email, Secure Firewall, Secure Malware Analytics, Umbrella, and Cisco Duo for relevant prevention, detection, blocking, or account protection.
- Talos reports Snort SID 63218–63225 and 300867–300870 for this threat.
- Talos lists ClamAV detections including Lnk.Downloader.CoralRaider-10027128-0, Txt.Tool.CoralRaider-10027140-0, Html.Downloader.CoralRaider-10027220-0, Win.Infostealer.Lumma-10027222-0, Win.Infostealer.Rhadamanthys-10027293-0, Win.Infostealer.Rhadamanthys-10027294-0, and Win.Infostealer.Cryptbot-10027295-0 through Win.Infostealer.Cryptbot-10027303-0 and Win.Infostealer.Cryptbot-10027305-0.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | claimconcessionrebe[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | culturesketchfinanciall[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | gemcreedarticulateod[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | liabilityarrangemenyit[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | modestessayevenmilwek[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | peasanthovecapspll[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | secretionsuitcasenioise[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | sofahuntingslidedine[.]shop | LummaC2 C2 domain the malware attempts to contact. |
| DOMAIN | triangleseasonbenchwj[.]shop | LummaC2 C2 domain the malware attempts to contact. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe HTA is heavily obfuscated, and the PowerShell scripts and LummaC2 variant use obfuscation.T1055 · Process InjectionThe Rhadamanthys loader allocates memory and injects the malware into a selected process.T1059.001 · PowerShellPowerShell commands and scripts execute the HTA, decryptor, loader, and payload-related actions.T1105 · Ingress Tool TransferPowerShell downloads the HTA and later downloads the information-stealer payload from CDN cache URLs.T1112 · Modify RegistryThe loader creates and configures registry keys for the FoDHelper UAC-bypass technique, then deletes the configured keys.T1140 · Deobfuscate/Decode Files or InformationJavaScript decodes an embedded function, and the PowerShell decryptor decrypts the next-stage loader.T1204.002 · Malicious FileThe infection chain begins when a victim opens a malicious Windows Shortcut file contained in a downloaded ZIP.T1218.005 · MshtaThe shortcut invokes mshta.exe to execute the remotely hosted malicious HTA.T1548.002 · Bypass User Account ControlThe loader uses FoDHelper.exe and registry ProgID/CurVer configuration to execute a batch script in an elevated context and bypass UAC.T1562.001 · Disable or Modify ToolsA batch script adds C:\ProgramData to the Windows Defender exclusion list.T1566.001 · Spearphishing AttachmentTalos assesses that malicious links may be delivered to victims through phishing emails.
People
Threat Actors
Malware
CryptBotCisco Talos discovered a new ongoing campaign since at least February 2024, operated by a threat actor distributing three famous infostealer malware, including Cryptbot, LummaC2 and Rhadamanthys.LummaC2Cisco Talos discovered a new ongoing campaign since at least February 2024, operated by a threat actor distributing three famous infostealer malware, including Cryptbot, LummaC2 and Rhadamanthys.RhadamanthysCisco Talos discovered a new ongoing campaign since at least February 2024, operated by a threat actor distributing three famous infostealer malware, including Cryptbot, LummaC2 and Rhadamanthys.
Vendors
Products
Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.Cisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.Cisco Secure Web ApplianceCisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.ClamAVClamAV detections are also available for this threat:Microsoft Windowsand procedures (TTPs) of CoralRaider’s Rotbot campaign, including the initial attack vector of the Windows Shortcut file, intermediate PowerShell decryptor and payload download scripts, the FoDHelper techniqueSnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org. Snort SID for this threat is 63218 - 63225 and 300867 - 300870.UmbrellaUmbrella, Cisco's secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.Windows Defenderwhich includes the PowerShell command to add the folder “ProgramData” of the victim machine to the Windows Defender exclusion list.
Tools
FoDHelper.exeThe dropped bath script is executed through a living-off-the-land binary (LoLBin) “FoDHelper.exe” and a Programmatic Identifiers (ProgIDs) registry key to bypass the User Access Controls (UAC) in the victim’s machine.mshta.exeto read the registry contents of the application classes registry key and gets the executable name “mshta.exe.” Using mshta.exe, the PowerShell instance executes the remotely hosted malicious HTA file on thePowerShellTalos also discovered a new PowerShell command-line argument embedded in the LNK file to bypass anti-virus products and download the final payload into the victims’ host.
Countries
EcuadorThe campaign affects victims across multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data andEgyptaffects victims across multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINTGermanyThe campaign affects victims across multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data andJapanthe U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINT information. Our telemetry also disclosed thatNigeriaThe campaign affects victims across multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data andNorwayincluding the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINT information. Our telemetry also disclosedPakistanThe campaign affects victims across multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data andPhilippinescountries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINT information. Our telemetry alsoPolandacross multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINT information. OurSyriathe U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINT information. Our telemetry also disclosed that someTurkeyNigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINT information. Our telemetry also disclosed that some affected usersU.K.victims across multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and OSINTU.S.The campaign affects victims across multiple countries, including the U.S., Nigeria, Pakistan, Ecuador, Germany, Egypt, the U.K., Poland, the Philippines, Norway, Japan, Syria and Turkey, based on our telemetry data and
Industries
civil defensedisclosed that some affected users were from Japan’s computer service call center organizations and civil defense service organizations in Syria. The affected users were downloading files masquerading as movie filescomputer service call centerand OSINT information. Our telemetry also disclosed that some affected users were from Japan’s computer service call center organizations and civil defense service organizations in Syria. The affected users were