cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2502 articles

Threat Research · blog.talosintelligence.com

CoralRaider Uses RotBot and XClient to Steal Credentials and Social Media Data

Cisco Talos details CoralRaider, a financially motivated group assessed to be based in Vietnam, using malicious Windows shortcuts, RotBot and XClient to steal credentials, financial information and social media data across several Asian countries.
Apr 4, 2024
Threat Research · wiz.io

XZ Utils Backdoor in Versions 5.6.0 and 5.6.1 Could Enable SSH-Based RCE

Researchers describe how a backdoor in XZ Utils 5.6.0 and 5.6.1 can enable remote code execution through SSH under specific conditions, and share findings on its hooks, log concealment, affected distributions and remediation.

Mar 29, 2024
Threat Research · huntress.com

Huntress Traces MSSQL-Based Attempts to Install ScreenConnect

Huntress traced automated-looking commands from MSSQL processes on two endpoints to attempted ScreenConnect installations. Investigators found no evidence the installers succeeded.

Mar 28, 2024
Threat Research · hunt.io

Open Directory Hosted Coin-Mining Malware and a Possible Mozi-Linked Payload

An investigation found suspicious files in open directories, including Windows screen savers that dropped payloads, modified firewall rules, and ran XMRig to mine Monero. BitTorrent-related DNS requests suggested possible Mozi-like activity.

Mar 28, 2024
Threat Research · hunt.io

Exposed Directory Reveals Red-Team Tools, Kerberoasted Hashes and Cobalt Strike Profile

Researchers found an exposed directory containing red-team tools, Kerberoasted hashes, and Cobalt Strike files. Certificate details were linked to a Cobalt Strike instance, but no beacon was associated with the port at the time of writing.

Mar 21, 2024
Threat Research · huntress.com

Huntress Details Two-Day MSSQL Attempt to Deploy a Web Shell

Huntress reconstructed two days of attempts to use MSSQL access to deploy a PHP reverse shell on a Windows server. Windows Defender detected and quarantined the files, and no functioning shell was observed.

Mar 20, 2024
Threat Research · hunt.io

W3LL Phishing Campaign Impersonates Adobe to Steal Outlook Credentials

Researchers found a W3LL phishing campaign using a fake Adobe Shared File page to steal Outlook credentials. The kit uses adversary-in-the-middle techniques to capture session cookies and bypass MFA.

Mar 19, 2024
Threat Research · blog.talosintelligence.com

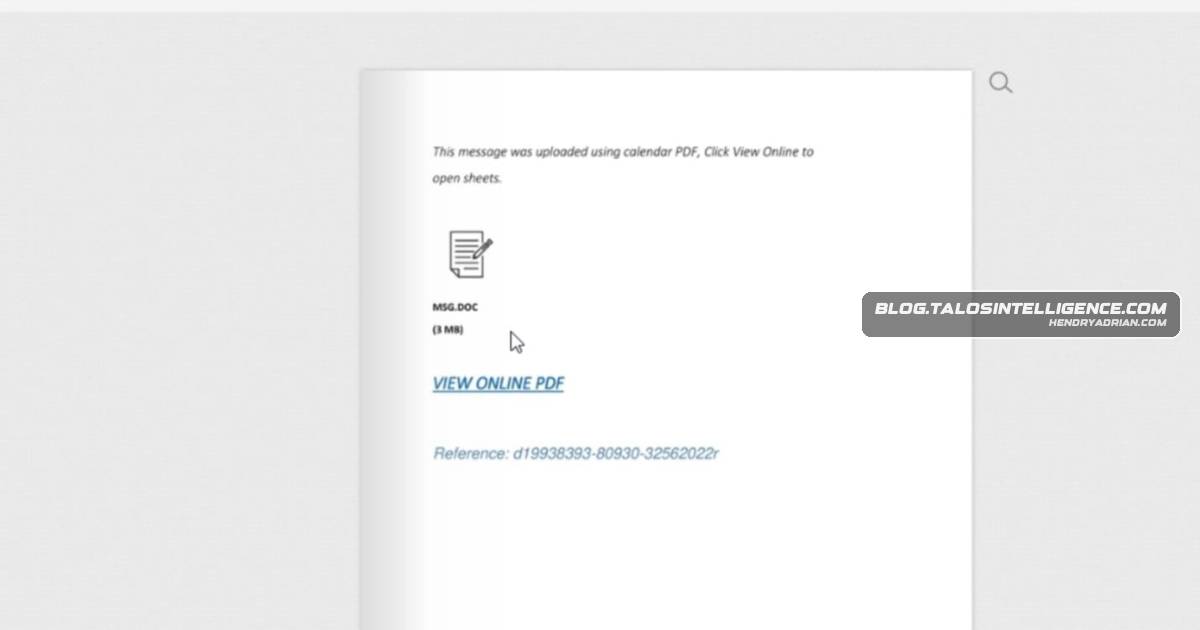
Threat Actors Abuse Document-Publishing Sites to Steal Credentials and Session Tokens

Talos observed phishing campaigns abusing legitimate document-publishing sites to host lures that redirect victims to credential- and session-token-harvesting pages, often impersonating Microsoft 365. The article details attack patterns, case studies, and defensive меры

Mar 13, 2024
Threat Research · huntress.com

Huntress Details Attempted Data Exfiltration Using Restic Backup Utility

Huntress traced an actor’s access to two Windows servers using compromised credentials and attempts to exfiltrate file shares with restic and cloud storage. The investigation found no clear evidence the second server’s data was successfully backed up.

Mar 13, 2024
Threat Research · team-cymru.com

Analysis Details Coper/Octo Android Malware-as-a-Service Operation

Team Cymru's analysis describes Coper/Octo, an Exobot-derived Android malware-as-a-service, detailing its credential-theft injects, keylogging, SMS interception, VNC control, encrypted command-and-control, and geographic and device filters.

Mar 6, 2024
Threat Research · blog.talosintelligence.com

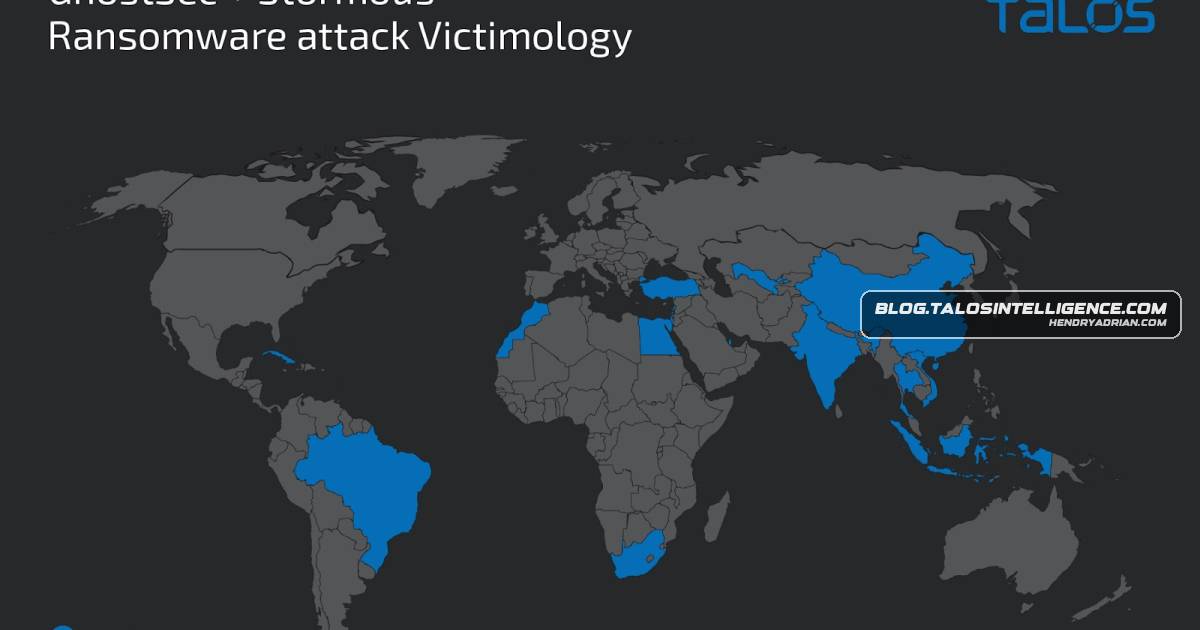
GhostSec and Stormous Expand Ransomware Operations With GhostLocker 2.0

Cisco Talos details GhostSec and Stormous’s joint ransomware operations, GhostLocker 2.0’s behavior, and two tools linked to attacks on websites: a site-scanning utility and a WordPress hacking tool.

Mar 5, 2024
Threat Research · hunt.io

Open Directory Reveals Phishing Campaign Targeting Google and Naver Credentials

Hunt analyzed an open directory hosting Google and Naver phishing pages, a modified Xeno-RAT sample, and victim data. Infrastructure and tactics show overlaps with Kimsuky, though attribution remains uncertain.

Mar 5, 2024
Threat Research · huntress.com

Huntress Traces SocGholish Infection from a Compromised WordPress Site

Huntress traced a SocGholish download through a compromised WordPress blog by reviewing Chrome history and analyzing an obfuscated script, identifying more than 100 potentially compromised domains.

Mar 1, 2024
Threat Research · huntress.com

Huntress Traces MSSQL Attack That Installed AnyDesk and Created a Local Account

Huntress traced an automated MSSQL attack that extracted and ran staged files, created a local account, and installed AnyDesk. Analysts isolated the endpoint before ransomware deployment.

Feb 29, 2024
Threat Research · huntress.com

Huntress Traces BlackCat Ransomware Activity to a Likely Compromised ScreenConnect Instance

Huntress reconstructs a February 2024 ransomware deployment through a likely compromised ScreenConnect instance, detailing an attempted Defender bypass, recovery-disabling commands and PsExec propagation. Logs showed no similar compromise on other Huntress customer-host

Feb 28, 2024
Threat Research · hunt.io

Suspected Lazarus-Linked Phishing Campaign Targets Blockchain Entrepreneurs via Telegram

A phishing campaign impersonates investment partners on Telegram and tricks blockchain entrepreneurs into running a malicious AppleScript. Infrastructure similarities suggest a possible Lazarus Group link, but attribution is unconfirmed.

Feb 28, 2024
Threat Research · blog.talosintelligence.com

TimbreStealer Targets Mexican Users Through Tax-Themed Phishing

Talos describes a campaign active since at least November 2023 that uses tax- and invoice-themed phishing to deliver TimbreStealer to users in Mexico, detailing its obfuscation, anti-analysis, persistence and information-stealing capabilities.

Feb 27, 2024
Threat Research · huntress.com

Huntress Details Post-Exploitation Activity Following ScreenConnect Vulnerability Exploitation

Huntress describes SOC-observed attacks exploiting ScreenConnect vulnerabilities, including ransomware and cryptominer deployments, Cobalt Strike activity, additional remote access tools, and persistence across victim networks.

Feb 23, 2024
Threat Research · blog.talosintelligence.com

Turla’s TinyTurla-NG Campaign Used Chisel, Credential Theft Scripts and a Web Shell

Cisco Talos and CERT.NGO detail Turla’s TinyTurla-NG operations, including compromised WordPress C2 servers, file discovery and exfiltration, a modified Chisel implant, credential-harvesting scripts, and a tool for running commands with another process’s privileges.

Feb 22, 2024
Threat Research · huntress.com

Huntress Explains ScreenConnect Authentication Bypass and Path-Traversal Exploits

Huntress recreated ScreenConnect exploits for CVE-2024-1709 and CVE-2024-1708, explaining how the authentication bypass can enable administrator access and how path traversal can write files. ConnectWise patched on-premises versions in 23.9.8.

Feb 21, 2024
Threat Research · blog.talosintelligence.com

Astaroth, Mekotio and Ousaban Campaigns Abuse Google Cloud Run to Deliver Banking Trojans

Talos details high-volume campaigns using Google Cloud Run links and malicious MSIs to distribute Astaroth, Mekotio and Ousaban, primarily to victims in Latin America. The report describes their infection chains, malware behavior and indicators.

Feb 20, 2024
Threat Research · threatfabric.com

Anatsa Banking Trojan Resurges in Europe Using Staged Droppers and AccessibilityService Abuse

ThreatFabric reports five Anatsa campaign waves targeting European regions, with five Google Play droppers exceeding 100,000 installations. The droppers use staged downloads, abuse AccessibilityService and bypass Android 13 restrictions.

Feb 19, 2024
Threat Research · blog.talosintelligence.com

Turla Uses TinyTurla-NG Backdoor to Target Polish NGOs and Steal Password-Manager Key Material

Cisco Talos details Turla’s TinyTurla-NG backdoor campaign targeting Polish NGOs, using compromised WordPress sites for C2 and PowerShell scripts to collect and exfiltrate files, including password-manager key material.

Feb 15, 2024
Threat Research · huntress.com

Huntress Correlates Exchange Logs and Defender Alerts to Investigate Exploit Activity

Huntress analysts correlated Defender, PowerShell, Exchange, and web-server logs to investigate commands sent to an unpatched Exchange endpoint. The activity appeared consistent with a scan; Defender remediated the commands, and the customer was urged to update.

Feb 14, 2024
PreviousPage 99 of 105 Next
© 2026 cyber.hendryadrian.com