cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2501 articles

Threat Research · hunt.io

Researchers Link Naver Phishing Infrastructure and Apple Spoofing Domains to Suspected DPRK Activity

Researchers found an exposed server hosting incomplete Naver credential-phishing pages and a separate cluster of Apple-spoofing domains. Infrastructure and certificate patterns are consistent with DPRK-linked activity, but attribution is unconfirmed.
Oct 29, 2024
Threat Research · hunt.io

Rekoobe Backdoor Found on Open Servers Alongside TradingView Lookalike Domains

Researchers found two Rekoobe samples on open servers, traced related infrastructure through shared SSH keys, and identified inactive domains resembling TradingView. Their connection to a campaign targeting TradingView users remains unconfirmed.

Oct 24, 2024
Threat Research · blog.talosintelligence.com

Phishing Campaign Uses Gophish to Deliver PowerRAT and DCRAT

Cisco Talos details a campaign targeting Russian-speaking users with phishing emails sent through Gophish. Malicious Word documents deploy PowerRAT, while HTML lures lead to DCRAT infections.

Oct 22, 2024
Threat Research · hunt.io

Researchers Map Updated WarmCookie Infrastructure and Identify Possible DarkGate C2 Overlap

Hunt.io researchers linked six servers to updated WarmCookie activity using certificate and HTTP-response similarities. A shared SSH key exposed a wider set of servers, including one flagged as a possible DarkGate C2.

Oct 17, 2024
Threat Research · hunt.io

Certificate and Redirect Clues Reveal Earth Baxia and PlugX Infrastructure

Researchers identified two distinct malicious infrastructure clusters using unusual TLS certificates and HTTP redirects: one linked to Earth Baxia and another potentially connected to PlugX.

Oct 10, 2024
Threat Research · hunt.io

Exposed Criminal Server Hosted DDoS Tools, Spyware APKs and Phishing Pages

Researchers found an exposed server containing DDoS tools, SpyNote APKs disguised as popular apps, phishing pages targeting cryptocurrency and messaging services, and files displaying a mobile ransom demand.

Oct 8, 2024
Threat Research · blog.talosintelligence.com

Talos Details MedusaLocker Affiliate Using BabyLockerKZ Since 2022

Talos links a financially motivated actor active since at least 2022 to BabyLockerKZ, a MedusaLocker variant, and details its credential-theft and lateral-movement tools, targeting patterns, and detection indicators.

Oct 3, 2024
Threat Research · hunt.io

Malicious Python Scripts Abuse BoxedApp SDK to Hide and Run a DLL in Memory

Hunt researchers analyzed Python scripts that use the BoxedApp SDK to load a DLL from a password-protected archive in memory and relaunch a loader if it stops. The final payload could not be identified.

Oct 1, 2024
Threat Research · blog.talosintelligence.com

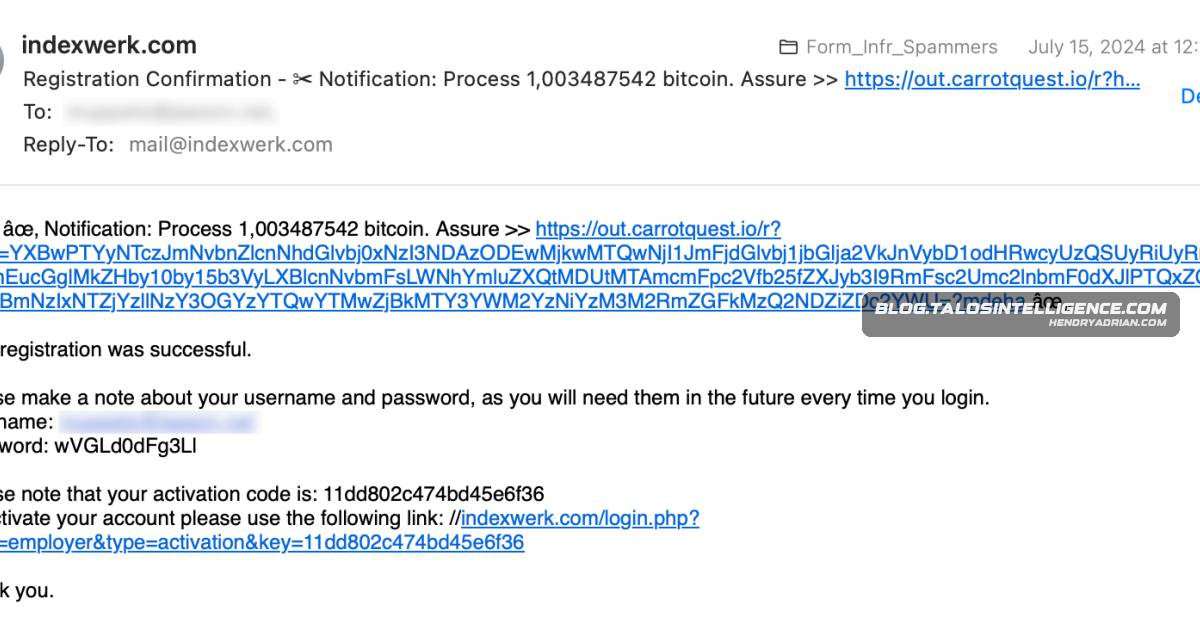
Talos Details How Spammers Abuse Web Forms and Stolen SMTP Credentials

Talos describes how spammers exploit legitimate web forms and Google apps to send unsolicited email, and use breached credentials to access outbound SMTP servers. It details tools and test-email patterns, plus defensive measures.

Sep 26, 2024
Threat Research · threatfabric.com

Octo2 Banking Trojan Targets European Users with Improved Remote Access and Evasion

ThreatFabric reports Octo2 campaigns in Italy, Poland, Moldova, and Hungary. The Android banking trojan uses Zombinder for installation and adds more stable remote access, advanced obfuscation, and a date-based DGA for C2 domains.

Sep 24, 2024
Threat Research · hunt.io

Open Directory Reveals Sliver C2 Malware Chain Resembling Stargazer Goblin Tactics

Researchers analyzed an exposed directory containing a disguised shortcut, obfuscated scripts, and malware payloads including Sliver C2. The tactics resemble Stargazer Goblin activity, but the researchers say attribution is unconfirmed.
Sep 24, 2024
Threat Research · huntress.com

Huntress Details ReadText34 Ransomware Attack and Its Use of a Vulnerable Driver

Huntress investigators traced a ReadText34 ransomware attack involving Administrator access, RDP, a vulnerable driver that crashed security software, persistence attempts, recovery inhibition and file encryption. Limited endpoint coverage left possible data theft unassس

Sep 22, 2024
Threat Research · huntress.com

Huntress Details Activity Observed Before Akira Ransomware Deployments

Huntress analysts describe activity seen before Akira ransomware deployments, including new accounts, RDP access, hidden accounts, Cloudflared tunnels, and ransomware execution. They recommend asset inventory, attack-surface reduction, and monitoring.

Sep 20, 2024
Threat Research · huntress.com

Attackers Brute-Force Exposed FOUNDATION Accounting Servers Using Default Credentials

Huntress found attackers brute-forcing publicly exposed FOUNDATION Accounting MSSQL servers, with unchanged default credentials enabling access and xp_cmdshell command execution. It confirmed 33 exposed hosts in its sample and advised rotating credentials and limiting.

Sep 17, 2024
Threat Research · blog.talosintelligence.com

DragonRank Compromises IIS Servers to Deploy PlugX and BadIIS for SEO Fraud

Talos reports that DragonRank compromised more than 35 IIS servers across multiple countries, using web shells, credential-harvesting tools, PlugX and BadIIS to maintain access and manipulate search results toward scam sites.

Sep 10, 2024
Threat Research · hunt.io

Malicious Chrome Extensions Use Scheduled Tasks and Decoy Documents to Target Networks

Researchers traced a malicious Chrome-extension operation from an open directory to Windows scheduled tasks and registry changes that bypass installation controls. A decoy Cobalt Strike guide uses a shortcut and PowerShell to download the malware; the extension includes

Sep 10, 2024
Threat Research · wiz.io

Responders Traced a Hybrid Cloud Attack from AWS to a Phishing-Infected Home Computer

A case study details how investigators traced repeated AWS compromises to a phishing-infected home computer, using cloud and on-premises logs, forensics, and threat intelligence. The extent of earlier data access remains unknown.

Sep 4, 2024
Threat Research · wiz.io

Phishing-Led Hybrid Cloud Attack Persisted for More Than 17 Months

A reconstructed attack began with phishing, compromised an employee’s home device and Citrix session, then used a jump server to steal data from AWS. Attackers maintained access and re-entered for more than 17 months.

Sep 4, 2024
Threat Research · blog.talosintelligence.com

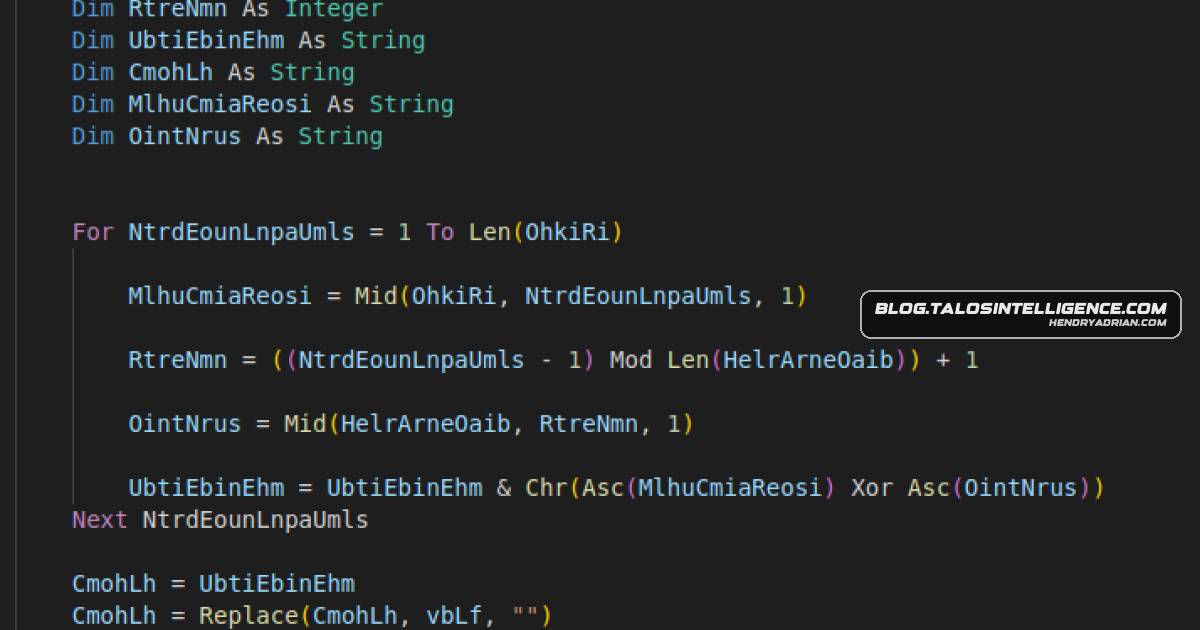
MacroPack-Generated Office Documents Deliver Havoc, Brute Ratel and PhantomCore Payloads

Cisco Talos analyzed MacroPack-generated Office documents that use obfuscated VBA and varied lures to deliver Havoc, Brute Ratel and PhantomCore payloads. Talos could not attribute the activity to a single actor and says some samples may be red-team exercises.

Sep 3, 2024
Threat Research · hunt.io

ToneShell Malware Targets IISS Defence Summit Attendees in Suspected Espionage Campaign

Researchers analyzed an IISS summit-themed lure that drops ToneShell-related malware, establishes persistence, and communicates with suspected Mustang Panda infrastructure. The campaign’s specific objectives were not confirmed.

Sep 3, 2024
Threat Research · team-cymru.com

Team Cymru Finds DDoS-Like Traffic Spike Targeting Venezuela’s Electoral Council

Team Cymru's NetFlow analysis found a 34-minute traffic spike targeting a CNE-linked IP during Venezuela's 2024 election, consistent with a possible DDoS attempt. The source and impact remain unclear; the data did not support claims of North Macedonian origin.

Aug 29, 2024
Threat Research · hunt.io

Latrodectus Malware Impersonates AhnLab Software and Uses Identified C2 Infrastructure

Researchers analyzed a Latrodectus DLL posing as AhnLab software and traced associated command-and-control servers and domains using certificate and infrastructure pivots. The malware can establish persistence and deploy additional payloads, including Brute Ratel C4.

Aug 29, 2024
Threat Research · huntress.com

Huntress Uncovers Long-Running Intrusion Targeting Vietnamese Human Rights Nonprofit

Huntress investigated an intrusion at a nonprofit supporting Vietnamese human rights, suspected to span at least four years. Malware analysis revealed layered persistence, PNG-hidden payloads, and overlaps with APT32/OceanLotus.

Aug 28, 2024
Threat Research · threatfabric.com

Rocinante Android Banker Malware Targets Brazilian Banks with Keylogging and Remote Control

ThreatFabric researchers describe Rocinante, an Android banking trojan targeting Brazilian institutions. Distributed through phishing sites, it uses Accessibility Services for keylogging and remote actions, while phishing screens steal financial data.

Aug 28, 2024
PreviousPage 96 of 105 Next
© 2026 cyber.hendryadrian.com