Attackers Brute-Force Exposed FOUNDATION Accounting Servers Using Default Credentials
Summary
Huntress found attackers brute-forcing publicly exposed FOUNDATION Accounting MSSQL servers, with unchanged default credentials enabling access and xp_cmdshell command execution. It confirmed 33 exposed hosts in its sample and advised rotating credentials and limiting.
Key points
- Huntress observed attackers targeting FOUNDATION Accounting Software installations used by construction-industry businesses.
- The software’s mobile-app connectivity may expose TCP port 4243, which provides direct access to its MSSQL instance.
- Huntress found high-privilege sa and dba accounts left with default credentials on multiple systems.
- On one host, investigators observed about 35,000 MSSQL login attempts before a successful authentication and xp_cmdshell being enabled.
- Huntress confirmed 33 publicly exposed hosts with unchanged default credentials in its sample of roughly 500 FOUNDATION systems.
- Huntress advises rotating database credentials, avoiding public internet exposure where possible, and disabling xp_cmdshell where appropriate.
- Huntress said it isolated machines with detected suspicious activity and notified affected customers and partners.
Article Details
- Attack Vectors
- Attackers brute-forced publicly exposed FOUNDATION-associated Microsoft SQL Server instances and gained access using unchanged default credentials for high-privilege accounts.
- The FOUNDATION mobile app connectivity may lead administrators to expose TCP port 4243 publicly, providing direct access to MSSQL.
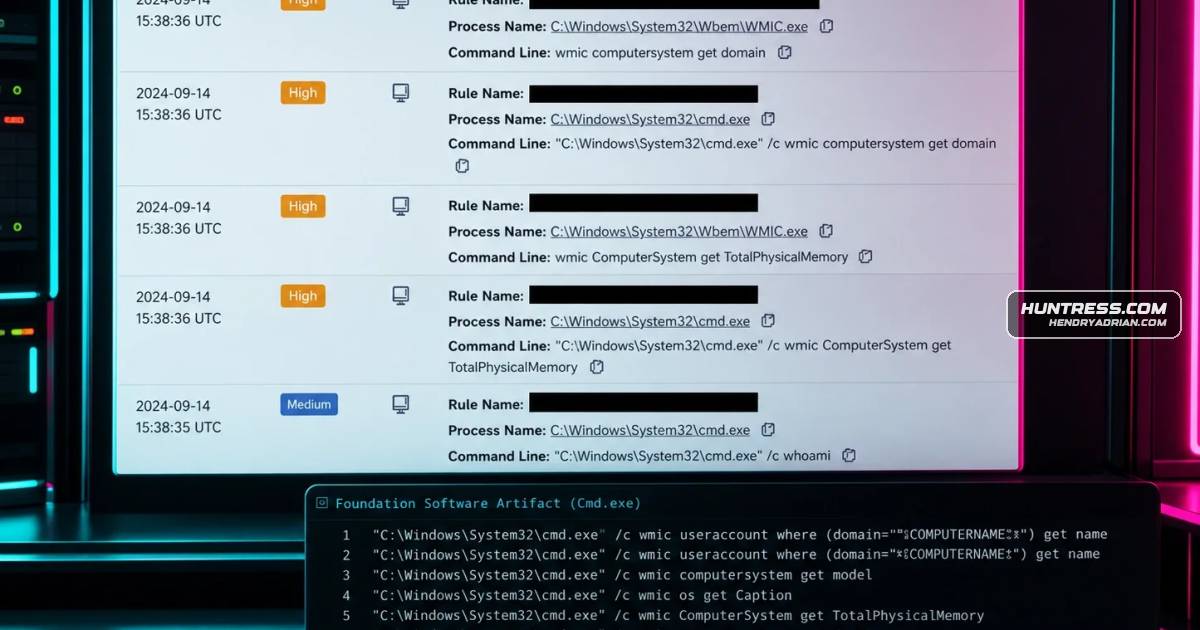
- After authentication, attackers enabled MSSQL xp_cmdshell and used it to run operating-system commands.
- Defensive Notes
- Rotate credentials for accounts connected to the FOUNDATION database, including dba and sa.
- Where possible, stop exposing the FOUNDATION application to the public Internet.
- Disable xp_cmdshell where appropriate.
- Huntress says it isolated machines with detected suspicious activity and notified affected customers and partners.
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryHuntress observed commands enumerating domain information and machine details.T1059.003 · Windows Command ShellCommands spawned from sqlservr.exe through cmd.exe after access was obtained.T1078 · Valid AccountsAttackers gained access using unchanged default credentials for privileged database accounts.T1082 · System Information DiscoveryHuntress observed host-enumeration commands during the intrusion.T1110 · Brute ForceAttackers made approximately 35,000 brute-force login attempts against an MSSQL server before a successful authentication.T1505.001 · SQL Stored ProceduresAttackers enabled MSSQL xp_cmdshell, an extended stored procedure used to execute operating-system commands.
People
Alden SchmidtCredited for contributions to the investigation and writeup.Craig SweeneyCredited for contributions to the investigation and writeup.Dr. AghaCredited for contributions to the investigation and writeup.Jamie LevyCredited for contributions to the investigation and writeup.John HammondCredited for contributions to the investigation and writeup.Michael TiggesCredited for contributions to the investigation and writeup.Tanner FilipCredited for contributions to the investigation and writeup.
Vendors
Products
FOUNDATION Accounting SoftwareHomeBlogCracks in the Foundation: Intrusions of FOUNDATION Accounting SoftwareMicrosoft SQL ServerThe FOUNDATION software includes a Microsoft SQL Server (MSSQL) instance to handle its database operations. While it is common to keep a database server internal and behind a firewall or VPN, the FOUNDATION software