Talos Details How Spammers Abuse Web Forms and Stolen SMTP Credentials
Summary
Talos describes how spammers exploit legitimate web forms and Google apps to send unsolicited email, and use breached credentials to access outbound SMTP servers. It details tools and test-email patterns, plus defensive measures.
Key points
- Attackers abuse account-registration, event-signup, and contact forms with weak input validation to send spam through legitimate organizations’ email infrastructure.
- Spammers also misuse Google apps, including Forms, Calendar, and Groups; setting up some of these attacks can require significant manual work.
- Credential stuffing lets attackers test breached username-password pairs against IMAP and outbound SMTP servers, using compromised accounts to send spam or access victims’ email.
- Talos identifies tools used for SMTP credential testing, including MadCat and MailRip, and lists common test-email subject lines.
- Talos says it diverts identified test messages in spam traps to make attackers believe an SMTP account works, prompting spam activity that can damage the sending IPs’ reputation.
- Recommended protections include unique passwords, a dedicated password manager, and caution around unsolicited messages sent through legitimate forms.
Article Details
- Attack Vectors
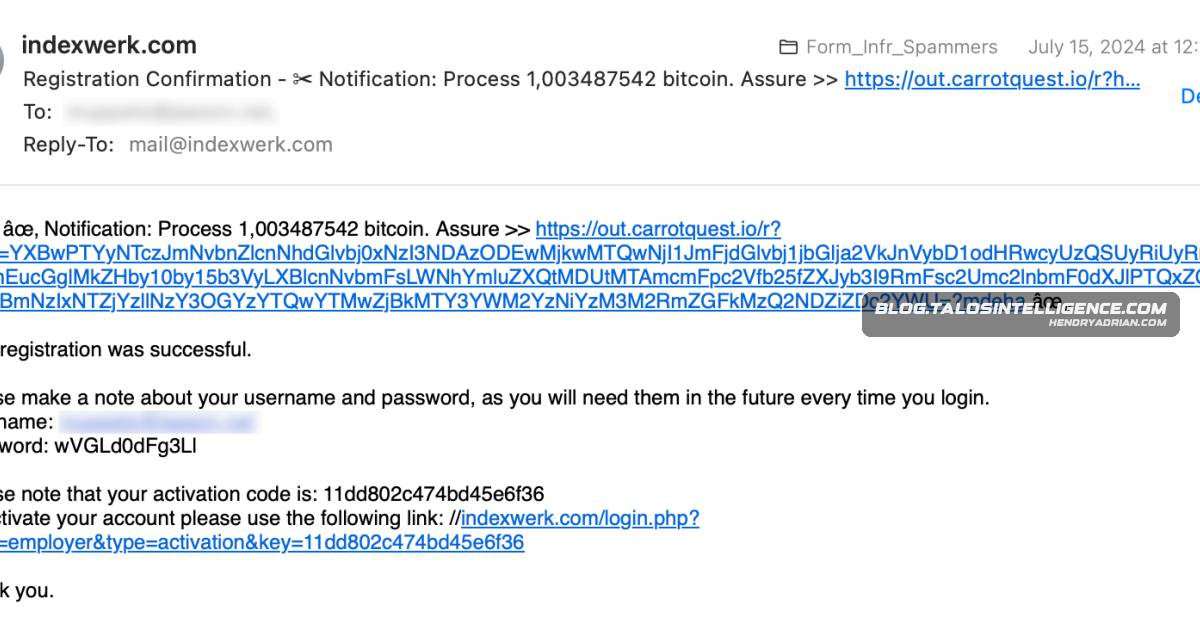
- Abuse of web forms that send confirmation or response emails: attackers submit unvalidated text and links in name or response fields so the resulting email delivers spam to a victim.
- Abuse of Google applications, including Quizzes, Drawings, Sheets, Forms, Calendar, and Groups, to send unsolicited messages through their legitimate email infrastructure.
- Credential stuffing against POP/IMAP and outbound SMTP accounts using credentials obtained from data breaches; successful SMTP access is used to send spam through the victim's mail server.
- Use of tools such as MadCat and MailRip to test username/password combinations on IMAP and outbound SMTP servers.
- Defensive Notes
- Use unique passwords for each website and a dedicated password manager; avoid storing credentials in a browser.
- Educate users to scrutinize unsolicited email, including messages sent through legitimate web forms, because suspicious extra content may reveal abuse.
- Talos describes routing identified credential-stuffing test messages from spam traps to make attackers believe an outbound account works; subsequent spam can cause connecting IP addresses to be flagged.
MITRE ATT&CK
T1110.004 · Credential StuffingAttackers reuse credentials obtained from data breaches to test access to victims' POP/IMAP and outbound SMTP accounts.T1566.002 · Spearphishing LinkSpam sent through abused web forms or compromised outbound mail accounts can deliver phishing and other attacks by email.
People
Vendors
Products
1Passworda password manager. It is best to use a dedicated password manger such as KeePass, LastPass or 1Password. Google CalendarGoogle Drawingsabusing Google Quizzes. But that is not the only Google software that spammers have been abusing. Google Drawings, Sheets, Forms, Calendar and Groups all contain similar vulnerabilities that allow spammers to sendGoogle formsGoogle GroupsGoogle QuizzesTalos previously reported on spammers abusing Google Quizzes. But that is not the only Google software that spammers have been abusing. Google Drawings, Sheets, Forms, Calendar and Groups all contain similarGoogle SheetsKeePassfor storing your passwords: a password manager. It is best to use a dedicated password manger such as KeePass, LastPass or 1Password. LastPassyour passwords: a password manager. It is best to use a dedicated password manger such as KeePass, LastPass or 1Password.
Tools
Laravel Monster ToolSubject: !XProad mx.example.com|2525|nywepaq@example.com|f29r21caT4. (from Laravel Monster Tool) MadCatalso open-source tools used for these sorts of activities. Among the tools Talos sees most frequently are MadCat and MailRip, both of which are available to download and run on GitHub. MailRiptools used for these sorts of activities. Among the tools Talos sees most frequently are MadCat and MailRip, both of which are available to download and run on GitHub.