cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2501 articles

Threat Research · wiz.io

Wiz Details Evolving Diicot Malware Campaign Targeting Linux Systems

Wiz researchers attribute an evolving Linux malware campaign to Diicot. The malware brute-forces weak SSH credentials, spreads in cloud environments, and establishes persistence; researchers suspect it mines cryptocurrency on non-cloud systems.
Dec 17, 2024
Threat Research · wiz.io

JINX-2401 Tried to Hijack AWS Bedrock Models Using Compromised IAM Keys

Wiz Research traced JINX-2401 activity across AWS environments, where compromised IAM keys were used to create users and Bedrock policies. Service Control Policies blocked the observed model-access attempts; Wiz recommends restricting Bedrock access and monitoring Cloud

Dec 15, 2024
Threat Research · aquasec.com

Researchers Find 336,000 Internet-Exposed Prometheus Servers and Exporters

Aqua Security researchers found about 336,000 internet-exposed Prometheus servers and exporters, which could leak sensitive data, enable denial-of-service attacks through pprof endpoints, or expose users to malicious exporters via RepoJacking.

Dec 12, 2024
Threat Research · hunt.io

Researchers Identify Fresh Infrastructure Linked to the Oyster Backdoor

Hunt IO identified three IPs and associated domains linked to Oyster backdoor activity, using TLS and web-page fingerprints to track infrastructure. Shared SSH keys connected one IP to 20 others, though the links do not prove malicious intent.

Dec 12, 2024
Threat Research · huntress.com

Huntress Analyzes Malichus Malware Linked to Cleo Software Exploitation

Huntress analyzes Malichus, malware delivered through exploitation of a Cleo software vulnerability, detailing its staged loaders, Java backdoor, custom C2 protocol, command execution, configuration access, and file exfiltration capabilities.

Dec 11, 2024
Threat Research · hunt.io

Researchers Track Suspected Kimsuky Infrastructure Using “Million OK!!!!” Response and Naver Branding

Hunt researchers linked newly observed domains and servers returning “Million OK!!!!” and displaying Naver branding to suspected Kimsuky infrastructure, identifying recurring domains, certificates, hosting, and server traits.

Dec 10, 2024
Threat Research · wiz.io

Ultralytics PyPI Releases Compromised Through GitHub Actions Workflow Attack

A crafted pull-request branch name reportedly exploited an Ultralytics GitHub Actions workflow, leading to PyPI releases 8.3.41 and 8.3.42 containing XMRig cryptomining code. The versions were removed; users are advised to uninstall and restore affected systems.

Dec 9, 2024
Threat Research · hunt.io

MoqHao Campaign Uses Apple iCloud and VK to Target Apple IDs and Android Devices

Researchers traced a Japanese delivery-themed smishing campaign to MoqHao. It served localized Apple ID phishing pages to iOS users and a malicious Android APK, using Apple iCloud, VK, and dynamic DNS infrastructure.

Dec 5, 2024
Threat Research · hunt.io

Rare Cobalt Strike Watermark Links Seven Servers to Suspicious Infrastructure

Researchers linked seven Cobalt Strike 4.10 team servers through a rare watermark and shared configuration, finding brand-impersonating domains and extracted beacon samples. They also observed a separate, unexplained cluster using watermark 1.

Dec 3, 2024
Threat Research · hunt.io

Open Directories Reveal XWorm Disguised as Legitimate Software

Hunt researchers found XWorm samples in exposed directories disguised as familiar software. Examples included a batch script that appeared to disable Windows Defender and a campaign using fake gift-card shortcuts to deliver malware that exfiltrated data to Telegram.

Nov 28, 2024
Threat Research · aquasec.com

Matrix DDoS Campaign Targets IoT Devices and Enterprise Servers to Build a Botnet

Aqua researchers detail Matrix’s campaign, which uses weak credentials, exposed services and known vulnerabilities to compromise IoT devices and servers, expand a DDoS botnet, and sell attack services through Telegram.

Nov 26, 2024
Threat Research · huntress.com

Huntress Links Two RDP-Brute-Force Intrusions to Renamed MeshAgent Persistence

Huntress traced two intrusions to RDP brute force, documenting PsExec-based lateral movement, a renamed MeshAgent, WDigest credential exposure and a retroactive hunt linking the same tradecraft across environments.

Nov 25, 2024
Threat Research · hunt.io

Certificate and Domain Patterns Reveal More Infrastructure Linked to Suspected DarkPeony Campaign

Hunt IO correlates SSL/TLS certificates, domains, and servers with suspected DarkPeony infrastructure, linking one domain to a PlugX-related malicious file and sharing a query to help defenders hunt for similar infrastructure.

Nov 21, 2024
Threat Research · threatfabric.com

Ghost Tap Uses NFC Relays to Scale Fraudulent Cash-Outs

ThreatFabric describes Ghost Tap, a cash-out tactic relaying NFC traffic from a device with a stolen card linked to a mobile payment service to a mule at a retailer, and outlines fraud indicators for financial institutions.

Nov 20, 2024
Threat Research · hunt.io

XenoRAT Delivered Through Excel XLL With ConfuserEx Obfuscation

Researchers analyzed a XenoRAT dropper delivered as an Excel XLL, protected with ConfuserEx and Excel-DNA. The chain used a decoy PDF and led to a XenoRAT payload communicating with a hardcoded C2 server.

Nov 19, 2024
Threat Research · bitdefender.com

Malicious Facebook Ads Promote a Fake Bitwarden Extension to Steal User and Business Data

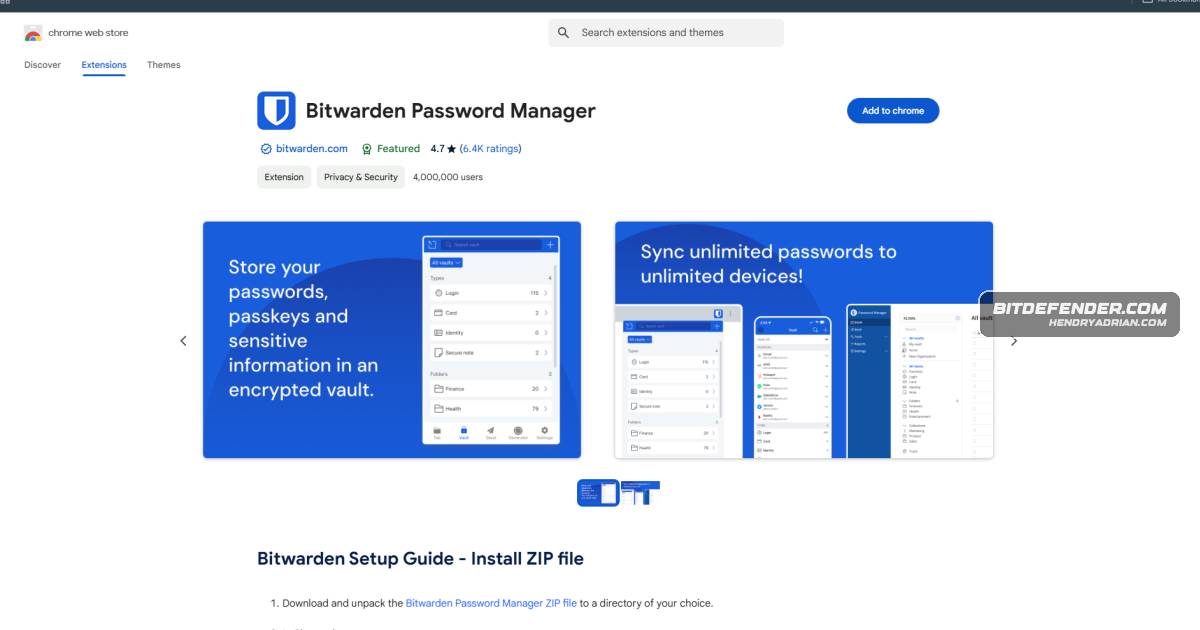
Bitdefender researchers describe Facebook ads promoting a fake Bitwarden update that leads users to sideload a malicious Chrome extension. It harvests Facebook cookies and account data, including business and billing information, and sends it to an attacker-controlled C

Nov 18, 2024
Threat Research · hunt.io

Researchers Link Sliver C2 Infrastructure to Possible Y Combinator Targeting

Hunt IO linked two Sliver C2 servers and Ligolo-ng tunneling infrastructure through shared TLS certificates and port configurations, and found a spoofed Y Combinator-like domain and a Sliver implant. The intended target remains uncertain.

Nov 12, 2024
Threat Research · wiz.io

Wiz Details Methods for Finding 0ktapus Phishing Domains

Wiz outlines ways to pivot across phishing pages, network fingerprints and registration data to find 0ktapus-linked domains, identifying multiple DOM templates and new domains while cautioning that shared kits complicate attribution.

Nov 7, 2024
Threat Research · blog.talosintelligence.com

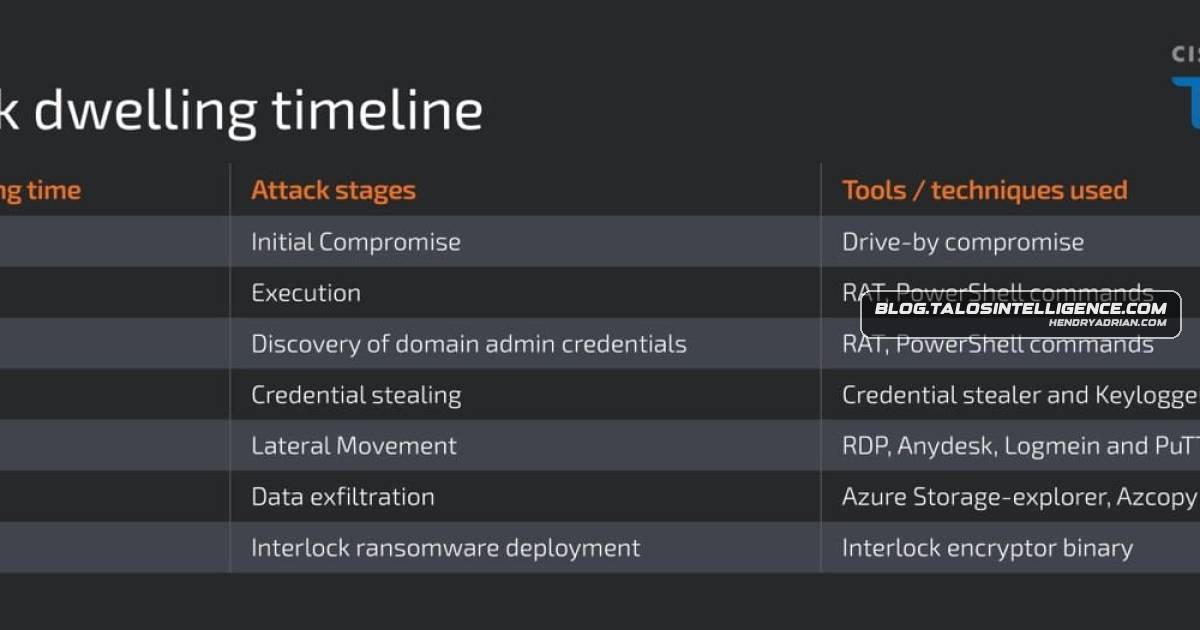
Talos Details Interlock Ransomware’s Attack Chain and Links to Rhysida

Talos describes Interlock ransomware attacks involving a fake Chrome updater, credential theft, lateral movement and data exfiltration. The group encrypts Windows and Linux systems; Talos sees low-confidence overlaps with Rhysida.

Nov 7, 2024
Threat Research · hunt.io

Researchers Trace 60,000-Plus Phishing Links Abusing Cloudflare Services

Hunt researchers found more than 60,000 phishing links, many targeting Microsoft SharePoint and Office 365 credentials. The pages used a shared Font Awesome kit and Cloudflare Workers or IPFS gateways to host credential-harvesting content.

Nov 7, 2024
Threat Research · hunt.io

RunningRAT Analysis Finds Crypto-Mining Tools on Associated C2 Server

Researchers analyzed RunningRAT samples and infrastructure, finding XMRig deployment scripts and tools on an associated C2 server. The RAT communicates with the server, while a separate executable showed possible credential-stealing functionality.

Nov 5, 2024
Threat Research · blog.talosintelligence.com

Phishing Campaign Targets Taiwan Facebook Business Accounts With LummaC2 and Rhadamanthys

Cisco Talos describes a campaign targeting Facebook business and advertising account users in Taiwan with copyright-themed phishing emails that deliver LummaC2 or Rhadamanthys information stealers through evasive loaders.

Oct 31, 2024
Threat Research · hunt.io

Open Directory Exposes Cobalt Strike, Phishing and Browser Credential Tools

Researchers found an open directory containing Cobalt Strike 4.2, exploit payloads, Goblin phishing-tool configuration, and browser password-stealing utilities. The intended targets and malicious use of the tools remain unconfirmed.

Oct 31, 2024
Threat Research · threatfabric.com

LightSpy iOS Spyware Uses Public Exploits and Adds Destructive Plugins

ThreatFabric analyzed LightSpy for iOS, finding public exploits, 17–28 plugins and destructive features that can impair or prevent booting. Researchers identified five C2 servers and logs indicating eight infected iOS devices.

Oct 29, 2024
PreviousPage 95 of 105 Next
© 2026 cyber.hendryadrian.com