cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2500 articles

Threat Research · huntress.com

Huntress Research Finds Rogue OAuth Apps Across Azure Tenants

Huntress surveyed more than 8,000 Azure tenants, finding Traitorware in about 10% and identifying over 500 Stealthware apps across partner tenants. It released Cazadora, an open-source script to audit tenant applications.
Feb 10, 2025
Threat Research · blog.talosintelligence.com

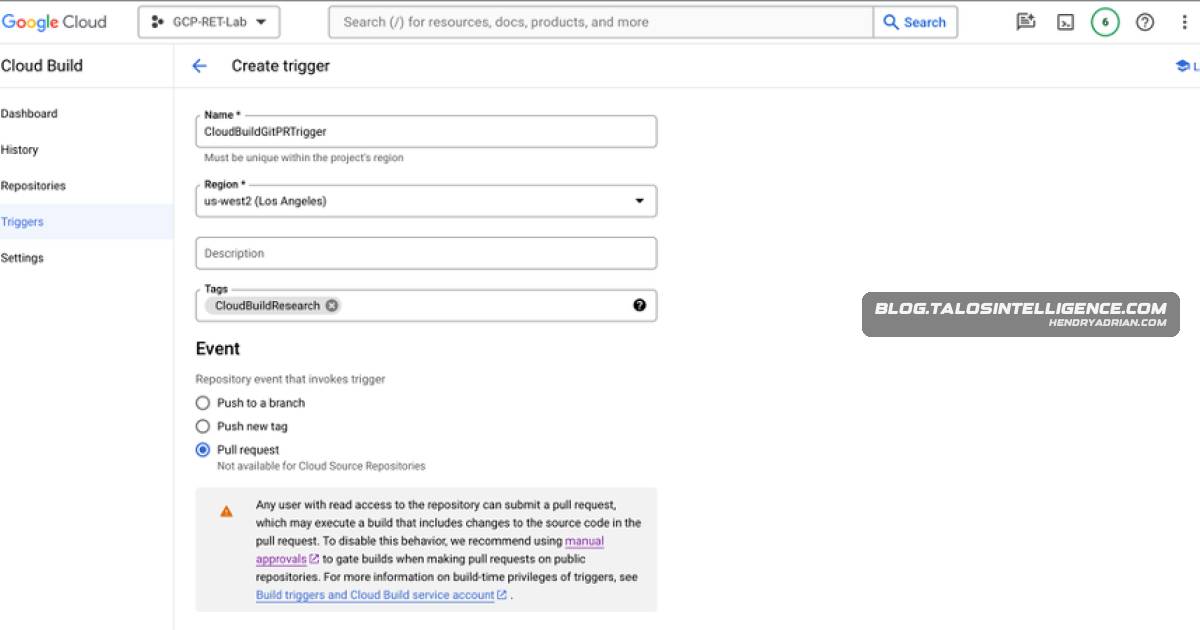
Talos Shows How Cloud Build Jobs Could Be Abused to Destroy Google Cloud Storage Data

Talos research demonstrates how an attacker able to trigger Cloud Build jobs could use the build service account’s permissions to delete or encrypt Cloud Storage data, and identifies audit events and safeguards for defenders.

Feb 6, 2025
Threat Research · huntress.com

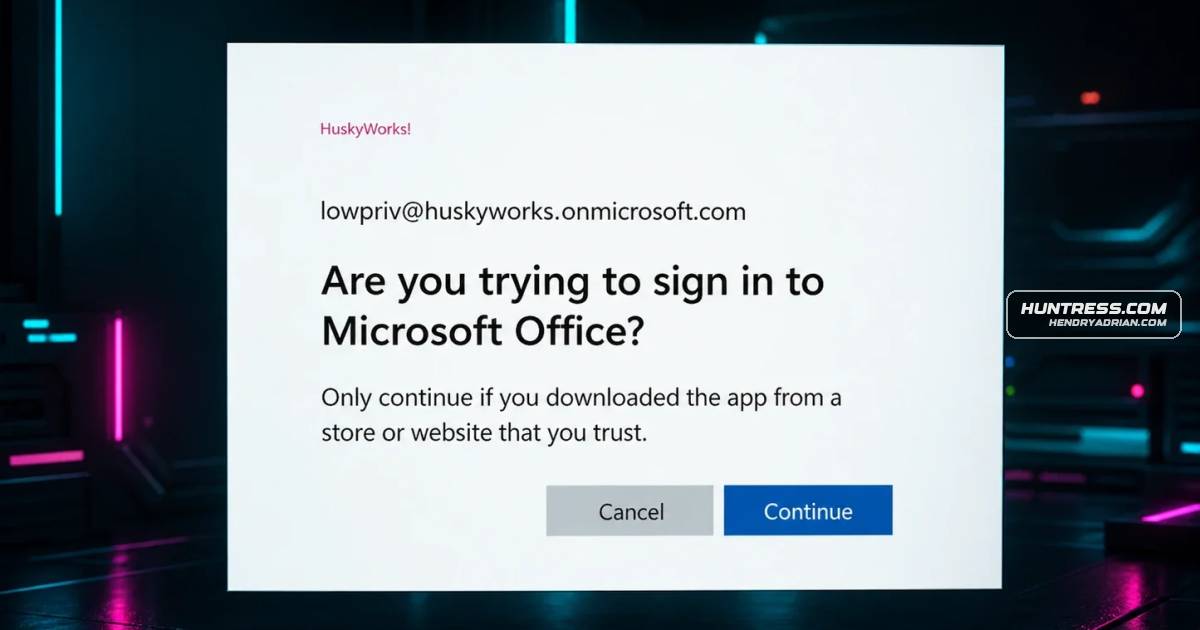
OAuth Device-Code Phishing Has Broader Impact in Azure Than Google Cloud

A technical comparison finds Azure’s device-code flow can let attackers obtain broadly scoped tokens after phishing a user, while Google Cloud restricts available scopes, limiting the attack’s potential. The author notes undocumented options may exist.

Feb 6, 2025
Threat Research · darktrace.com

Darktrace Details RansomHub Tactics and Activity in Customer Networks

Darktrace describes RansomHub’s growing use and reports observed activity including network scanning, credential attempts, lateral movement via remote-management tools, data exfiltration, and file encryption.

Feb 6, 2025
Threat Research · hunt.io

Open Directories Expose SmokeLoader Campaign Using Ukrainian Banking and Auto Lures

Researchers found SmokeLoader samples and fake invoice and bank-statement PDFs in two open directories, revealing staging infrastructure and technical details of a campaign targeting Ukrainian organizations.

Feb 6, 2025
Threat Research · bitdefender.com

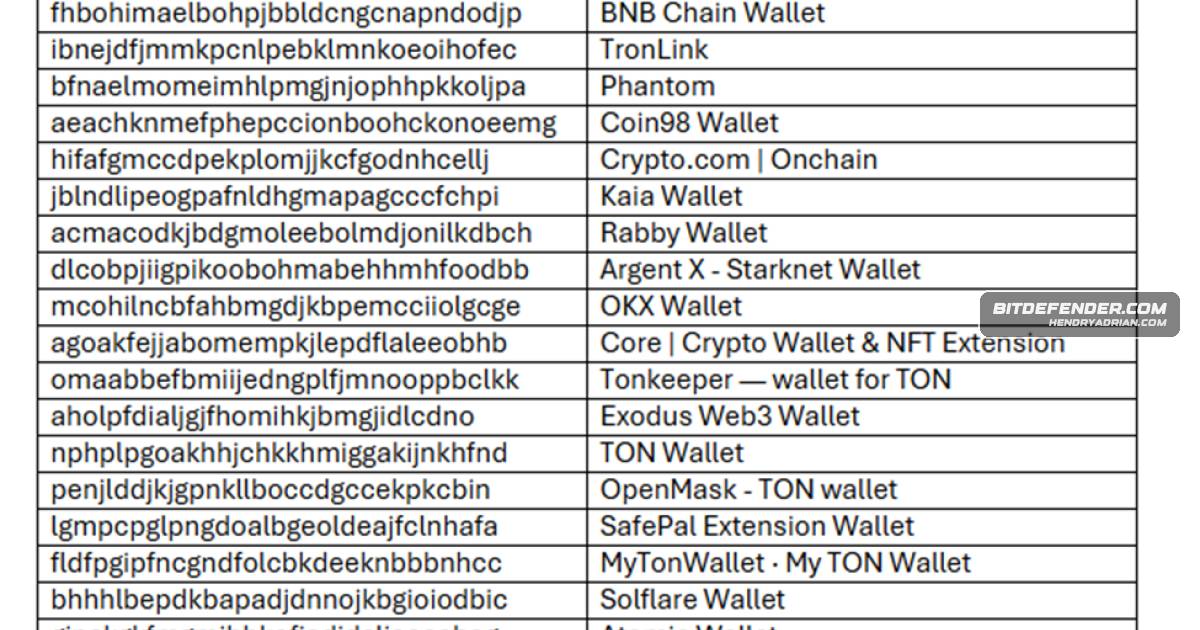
Lazarus-Linked Recruiting Scam Uses Cross-Platform Malware to Steal Data

Bitdefender details a suspected Lazarus campaign using fake LinkedIn job offers and malicious code repositories to deploy cross-platform malware that steals credentials, files, and cryptocurrency data.

Feb 5, 2025
Threat Research · hunt.io

GreenSpot-Linked Phishing Infrastructure Spoofs 163.com to Steal Credentials

Hunt.io researchers linked suspected GreenSpot infrastructure to spoofed 163.com login and attachment-download pages. Some pages captured submitted credentials; the researchers found no evidence of credential exfiltration from one separate login-page cluster.

Feb 4, 2025
Threat Research · aquasec.com

Research Shows How Misconfigured Kubernetes Policies Can Allow Unapproved Container Images

Aqua researchers found that prefix-based OPA Gatekeeper and Kyverno policies can be bypassed when repository constraints omit trailing slashes, potentially allowing unapproved container images. They describe a revised Gatekeeper policy and scanning recommendations.

Feb 3, 2025
Threat Research · team-cymru.com

Telemetry Investigation Links SmartApeSG to Active NetSupport RAT Servers

Team Cymru used internet telemetry to trace SmartApeSG management hosts to active NetSupport RAT servers and observe a connection to a Quasar RAT C2. The relationship between some infrastructure and threat actor activity remains uncertain.

Feb 3, 2025
Threat Research · blog.talosintelligence.com

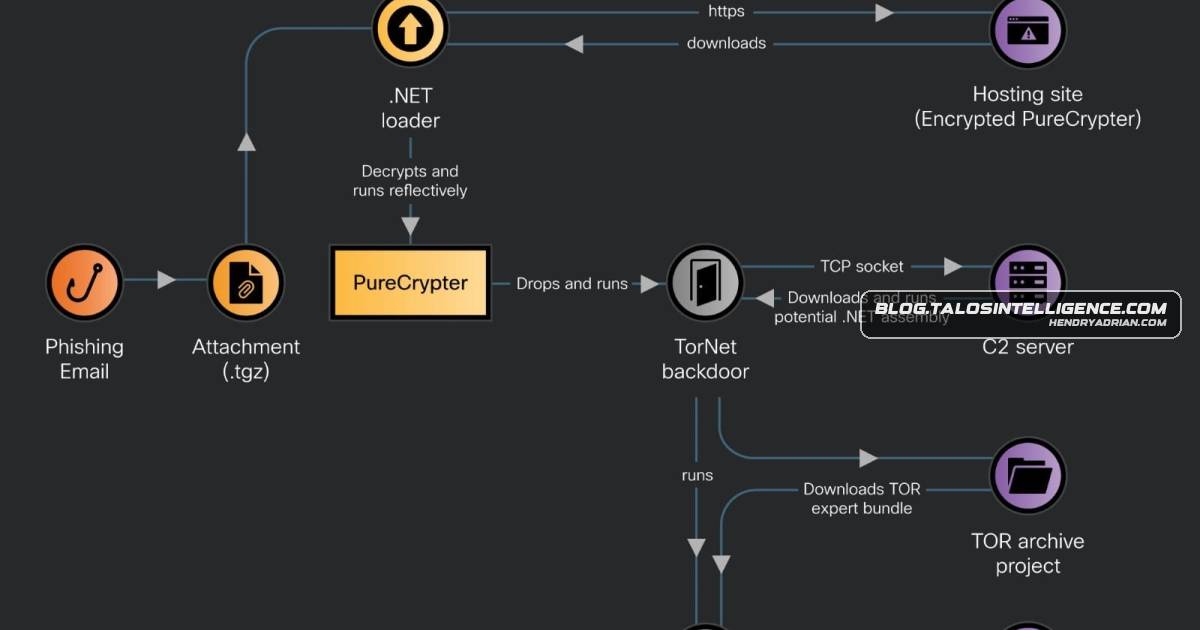
TorNet Backdoor Uses Tor for Stealthy Command-and-Control in Phishing Campaign

Cisco Talos analyzed a campaign targeting users mainly in Poland and Germany. Phishing attachments deliver PureCrypter, which can install the TorNet backdoor for persistent access, Tor-routed command-and-control, and execution of remote .NET assemblies.

Jan 28, 2025
Threat Research · hunt.io

Researchers Identify SparkRAT Infrastructure and macOS Activity in Suspected DPRK Campaign

Researchers found three additional servers linked to suspected SparkRAT activity, including macOS implants delivered through exposed directories. They describe C2 detection fingerprints, persistence behavior, infrastructure, and related indicators.

Jan 28, 2025
Threat Research · blog.talosintelligence.com

Talos Reports Phishing Emails Using Hidden Text to Evade Detection

Talos observed increased use of hidden text salting in email threats during the second half of 2024. Attackers hide characters or content in HTML to confuse parsers, language detection, spam filters, and security engines.

Jan 24, 2025
Threat Research · hunt.io

TLS Certificate and JA4X Clues Link New Servers to Suspected GhostWolf Infrastructure

Hunt researchers identified six active servers matching TLS certificate and JA4X indicators associated with suspected GhostWolf infrastructure, but say attribution to RedGolf/APT41 remains uncertain. A wolfSSL change also makes one certificate field unreliable for dete

Jan 23, 2025
Threat Research · hunt.io

Malicious VS Code Extension Impersonating Zoom Targets Chrome Cookies

Researchers found a VS Code extension posing as Zoom that added code to access Chrome cookies in version 0.2.2. It also contained hardcoded secrets for more than 20 services; the researchers reported it to Microsoft.

Jan 21, 2025
Threat Research · wiz.io

Wiz Uses Behavioral Cloud IOCs to Track Credential-Abusing Actors

Wiz describes using honeypot data and cloud API patterns to identify credential abuse and link incidents to an actor it calls “Bapak.” In observed cases, the actor lacked permission to create the attempted ECS cluster.

Jan 15, 2025
Threat Research · darktrace.com

Darktrace Details ShadowSyndicate’s RansomHub Attacks on Customers

Darktrace identified four RansomHub incidents attributed to ShadowSyndicate across customer networks, involving reconnaissance, data exfiltration, lateral movement and, in three cases, encryption.

Jan 14, 2025
Threat Research · hunt.io

JustJoin-Themed Landing Page Resurfaces on Infrastructure Linked to TA444/BlueNoroff

Hunt researchers found a JustJoin-themed landing page on infrastructure linked to previously reported TA444/BlueNoroff activity. Related servers shared an SSH fingerprint, suggesting coordinated infrastructure management.

Jan 14, 2025
Threat Research · hunt.io

TLS Certificate Analysis Links Cyberhaven Extension Attack to Long-Running Infrastructure

Researchers traced TLS certificate overlaps from the Cyberhaven Chrome extension compromise to 19 servers and domains with activity dating to early 2024. The infrastructure suggests a longer-running campaign, but links to Savvy Seahorse remain unconfirmed.

Jan 9, 2025
Threat Research · hunt.io

Golang Cobalt Strike Beacon Uses VS Code Tunnels for Command and Control

Researchers traced a Golang Cobalt Strike beacon to a server using VS Code dev tunnels for command and control. The investigation details beacon behavior and indicators, while noting that no specific target has been identified.

Jan 7, 2025
Threat Research · wiz.io

Wiz Details Nuclei Signature-Verification Bypass That Could Enable Malicious Template Execution

Wiz disclosed CVE-2024-43405, a Nuclei signature-verification bypass caused by mismatched Go regex and YAML newline handling. Crafted templates could execute unverified code; Nuclei 3.3.2 fixes it.

Jan 3, 2025
Threat Research · darktrace.com

Mamba 2FA Uses AiTM Phishing to Bypass MFA and Hijack Microsoft 365 Accounts

The article analyzes Mamba 2FA’s AiTM phishing tactics and describes Darktrace detections of compromised Microsoft 365 accounts, including unusual logins, mailbox-rule changes, and attempts to register authenticator apps.

Dec 31, 2024
Threat Research · team-cymru.com

Jingle Shells: How Virtual Offices Can Give Malicious Hosting a Facade of Legitimacy

Team Cymru links a Metasploit C2 IP and seven high-risk ASes to UK-registered hosting firms using virtual offices and overseas infrastructure, finding opaque records and leased IPv4 may enable abuse; it recommends stronger vetting and monitoring.

Dec 20, 2024
Threat Research · blog.talosintelligence.com

How Threat Actors Exploit Vulnerable Windows Drivers in BYOVD Attacks

Cisco Talos analyzes how attackers abuse vulnerable Windows drivers to escalate privileges, load unsigned kernel code, and disable security tools, documenting ransomware use and explaining Windows mitigations and defensive measures.

Dec 19, 2024
Threat Research · wiz.io

Wiz Details Evolving Diicot Malware Campaign Targeting Linux Systems

Wiz researchers attribute an evolving Linux malware campaign to Diicot. The malware brute-forces weak SSH credentials, spreads in cloud environments, and establishes persistence; researchers suspect it mines cryptocurrency on non-cloud systems.

Dec 17, 2024
PreviousPage 94 of 105 Next
© 2026 cyber.hendryadrian.com