cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2486 articles

Threat Research · socket.dev

Socket Tracks 73 Open VSX Extensions Linked to GlassWorm, Including Six Activated to Deliver Malware

Socket reports 73 Open VSX extensions linked to GlassWorm, with at least six activated to deliver malware. The investigation describes cloned listings, dependency-based delivery, native binaries, and obfuscated JavaScript loaders.
Apr 25, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details Shai-Hulud npm Worm’s Credential Theft and Self-Propagation

Unit 42 analyzes a malicious @bitwarden/cli package attributed to a TeamPCP campaign. Its payload harvests developer and cloud credentials, exfiltrates them through C2 and GitHub, and backdoors npm packages to spread.

Apr 25, 2026
Threat Research · thehackernews.com

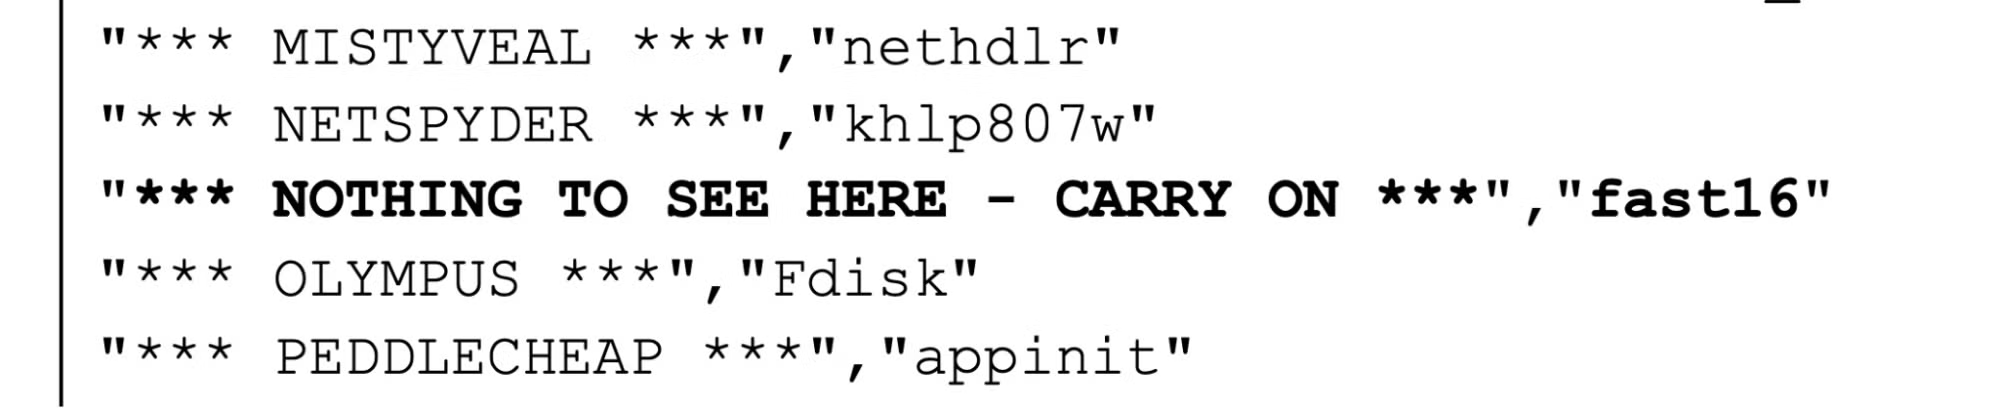
SentinelOne Uncovers 2005 Lua Malware Framework Targeting Engineering Software

SentinelOne researchers describe fast16, a Lua-based Windows framework dating to 2005. Its kernel driver could alter engineering and simulation software calculations; the investigation details its components and propagation, and places it before Stuxnet.

Apr 25, 2026
Threat Research · security.com

Harvester Expands GoGra Backdoor to Linux, Using Outlook for C2

Researchers linked Harvester’s Linux GoGra backdoor to its Windows variant through shared code and typos. It uses Microsoft Graph and Outlook for C2; researchers reported no observed victims in this activity.

Apr 25, 2026
Threat Research · securityweek.com

ESET Details GopherWhisper APT’s Backdoors in Attacks on Mongolian Government

ESET attributes a toolset of backdoors and injectors to China-linked GopherWhisper, which infected about 12 systems at a Mongolian government institution and likely targeted dozens more. Its tools use legitimate services for command and control and data exfiltration.

Apr 25, 2026
Threat Research · cyble.com

Operation TrustTrap Uses 16,800 Domains to Spoof Government Portals

Cyble researchers report 16,800+ spoofed domains impersonating government services to harvest credentials and payment-card data. The campaign uses deceptive subdomains and hyphens; one infrastructure cluster was assessed as consistent with APT36.

Apr 25, 2026
Threat Research · stepsecurity.io

GitHub Actions Injection Pushes Malicious elementary-data Releases to PyPI and GHCR

A GitHub Actions script-injection flaw let an attacker forge a release of elementary-data 0.23.3, published to PyPI and GHCR with a credential-stealing .pth payload. The team removed the artifacts and released clean 0.23.4.

Apr 25, 2026
Threat Research · bleepingcomputer.com

Firestarter Malware Persists on Cisco Firewalls Despite Patches and Reboots

U.S. and U.K. agencies report that UAT-4356-attributed Firestarter persists on Cisco ASA/FTD firewalls through reboots and updates, using LINA hooks and crafted WebVPN requests. They link access to CVE-2025-20333 and/or CVE-2025-20362 and advise reimaging.

Apr 24, 2026
Threat Research · cyfirma.com

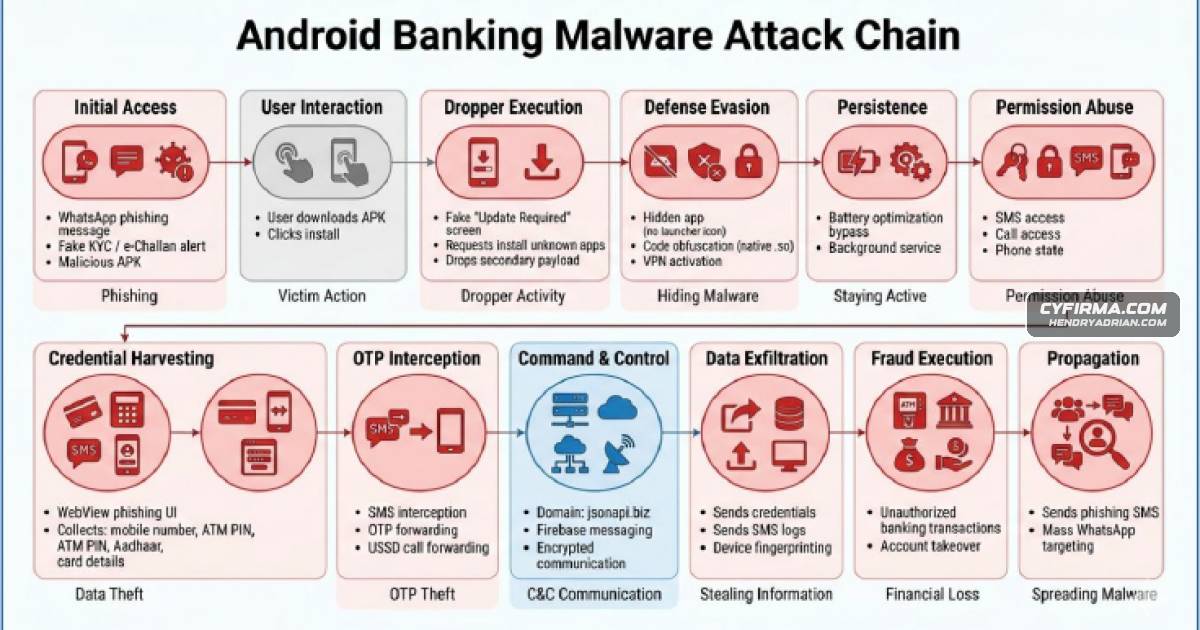
KYCShadow Android Malware Uses Fake KYC Workflows to Steal Credentials and OTPs

Cyfirma analyzes KYCShadow, an Android malware campaign distributed via WhatsApp. Its hidden payload uses fake KYC screens, SMS and call control, and a VPN; the report links its infrastructure to earlier e-Challan fraud with moderate-to-high confidence.

Apr 24, 2026
Threat Research · securityweek.com

Researchers Detail Pre-Stuxnet Fast16 Malware Built for Strategic Sabotage

SentinelLabs analyzed Fast16, a Lua-based malware referenced in the ShadowBrokers leak and reportedly used in 2005. Its driver could patch precision-calculation software; researchers say evidence suggests US development, while specific targets remain unconfirmed.

Apr 24, 2026
Threat Research · sentinelone.com

SentinelLABS Links ShadowBrokers’ fast16 Reference to a 2005 Precision-Sabotage Framework

SentinelLABS analyzed fast16, a 2005 Lua-based framework whose boot-start driver patched executable code in memory, apparently targeting high-precision engineering software. Researchers linked its name to ShadowBrokers’ Territorial Dispute signatures; exact targets are未

Apr 24, 2026
Threat Research · darkreading.com

Research Details Tropic Trooper’s Router DNS Hijacking and Expanded Targeting

Researchers report Tropic Trooper campaigns used compromised home routers to hijack DNS and deliver trojanized updates, while targeting individuals in Japan, Taiwan, and South Korea with new malware, phishing decoys, and other lures.

Apr 24, 2026
Threat Research · thehackernews.com

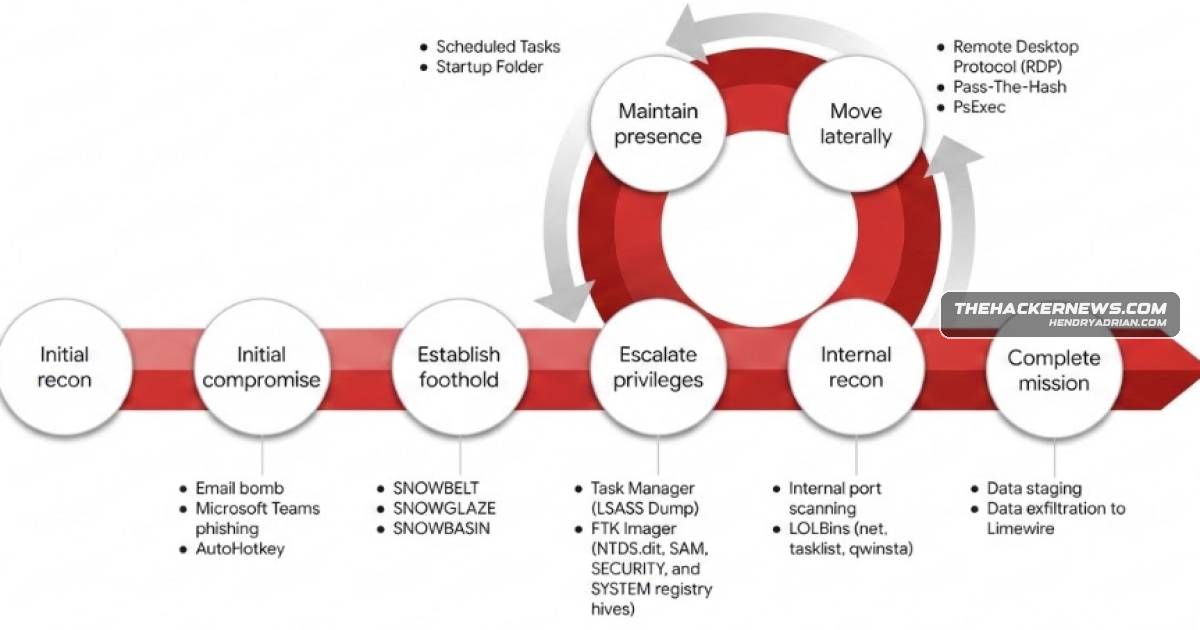
UNC6692 Uses Teams Help Desk Impersonation to Deploy SNOW Malware

Mandiant reports that UNC6692 uses email bombing and Microsoft Teams help-desk impersonation to deliver a modular SNOW toolkit, steal credentials, move laterally, and collect and exfiltrate data.

Apr 24, 2026
Threat Research · cyberscoop.com

Firestarter Backdoor Persisted on Cisco Firewalls Despite Patches, Agencies Warn

U.S. and U.K. agencies identified Firestarter, a backdoor that can persist on Cisco firewalls after patches and standard reboots. CISA found it on a federal device and ordered agencies to audit appliances and submit memory snapshots.

Apr 23, 2026
Threat Research · rhisac.org

RH-ISAC Details CL-CRI-1116 Vishing and SaaS Extortion Campaign

RH-ISAC describes CL-CRI-1116 targeting retail and hospitality with vishing and SSO phishing to steal credentials, abuse SaaS access to locate and exfiltrate sensitive files, and extort victims; it recommends caller-verification policies, training and technical controls

Apr 23, 2026
Threat Research · cloud.google.com

Google Details UNC6692’s SNOW Malware and Teams-Based Intrusion

Google Threat Intelligence Group details UNC6692’s Teams-based social engineering and its modular SNOW malware suite, tracing credential theft, persistence, lateral movement, and exfiltration through a victim environment.

Apr 23, 2026
Threat Research · circleid.com

Researchers Map DNS and WHOIS Infrastructure Linked to ForceMemo

An analysis of 20 network IoCs tied to ForceMemo used DNS and WHOIS data to identify look-alike registrations, linked domains and additional IPs; the researchers caution that some flagged entities may prove harmless.

Apr 23, 2026
Threat Research · security.com

Symantec Details Trigona Affiliates’ Custom Data Exfiltration Tool

Symantec reports that Trigona affiliates used a custom uploader in March 2026, with parallel transfers, connection rotation and file filtering, after disabling defenses; intrusions also involved AnyDesk and credential-theft tools.

Apr 23, 2026
Threat Research · levelblue.com

StepDrainer and EtherRAT Illustrate Convergence of Crypto Drainers and Traditional Malware

LevelBlue analyzes StepDrainer and EtherRAT, detailing how wallet-phishing drainers and a trojanized Windows installer combine crypto-focused operations with traditional malware techniques, including obfuscated payload delivery, on-chain configuration, and persistence.

Apr 23, 2026
Threat Research · blog.talosintelligence.com

UAT-4356 Uses FIRESTARTER Backdoor to Target Cisco Firepower Devices

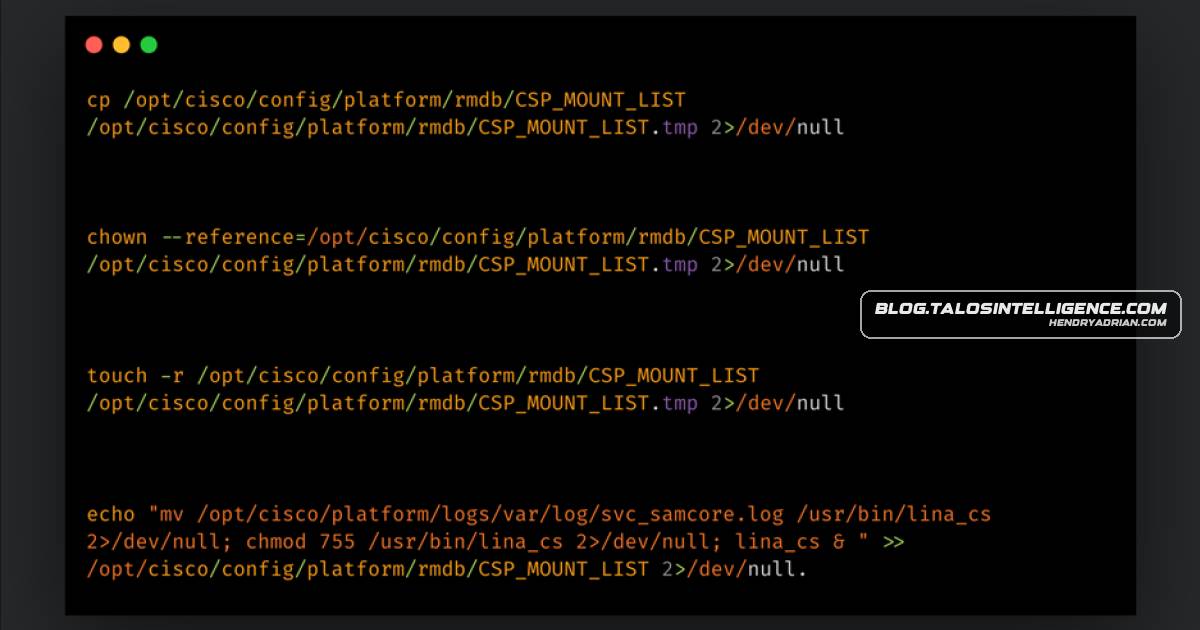
Cisco Talos reports that UAT-4356 exploited two vulnerabilities to access Cisco Firepower devices and deploy FIRESTARTER, a backdoor that enables remote code execution in the LINA process.

Apr 23, 2026
Threat Research · infoblox.com

Fake CAPTCHAs Funnel Users Into International SMS Revenue-Share Fraud

Researchers detail a campaign active since at least 2020 that uses fake CAPTCHAs and traffic-distribution systems to trick users into sending large batches of international SMS messages, generating revenue for the operators and unexpected charges for victims.

Apr 23, 2026
Threat Research · rapid7.com

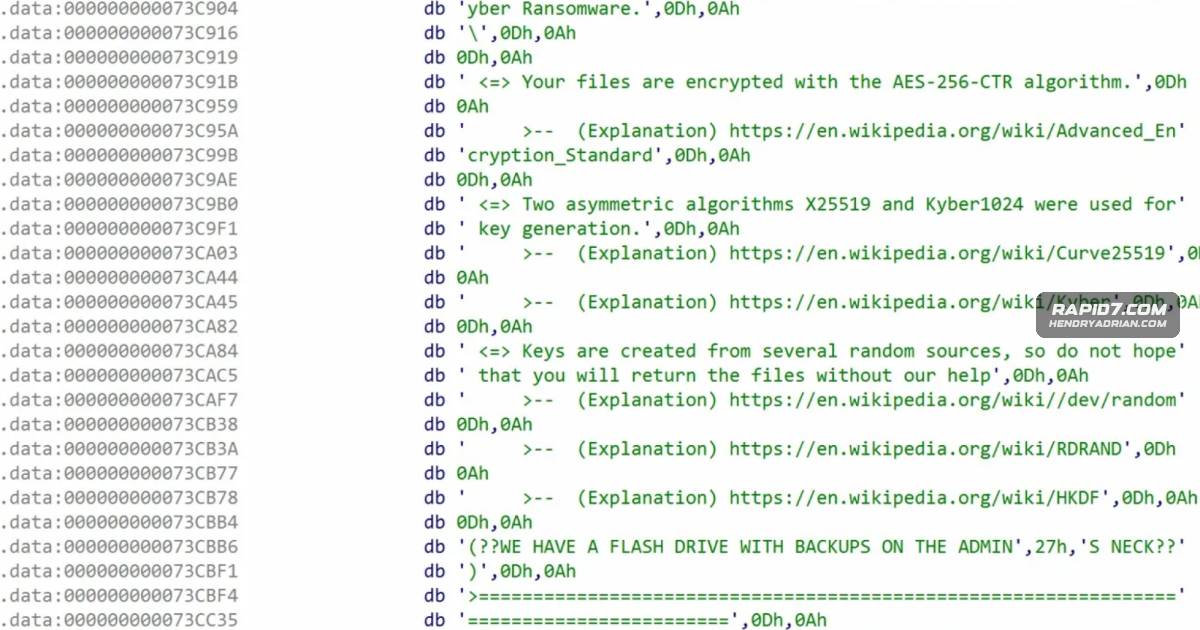
Rapid7 Analyzes Kyber Ransomware’s Windows and ESXi Variants

Rapid7 analyzed Windows and ESXi Kyber ransomware samples recovered during a March 2026 response, finding distinct encryption implementations, shared campaign infrastructure, ESXi VM and datastore targeting, and Windows anti-recovery capabilities.

Apr 23, 2026
Threat Research · sentinelone.com

Researchers Find Hardcoded Credentials in Cheap Smart Cameras

A LABScon 2025 investigation found Eken- and Tuck-branded cameras and doorbells share Allwinner hardware, hardcoded root credentials, and superficial firmware fixes. Researchers say traffic routes through China and Hong Kong and warn that opaque suppliers and remote re-

Apr 23, 2026
Threat Research · helpnetsecurity.com

ESET Details GopherWhisper APT’s Slack, Discord and Outlook C2

ESET researchers linked China-aligned GopherWhisper to an intrusion at a Mongolian government entity, documenting backdoors using Slack, Discord and Outlook drafts for C2, file exfiltration via file[.]io, and recovered operator messages supporting the investigation.

Apr 23, 2026
PreviousPage 67 of 104 Next
© 2026 cyber.hendryadrian.com