
Trickmo.C Android Banker Uses TON for Covert Command-and-Control
Summary
ThreatFabric reports that Trickmo.C, delivered through fake TikTok and streaming apps, targets banking and crypto-wallet users in France, Italy, and Austria. It uses TON .ADNL addresses for C2 and adds networking and tunneling commands.
Key points
- ThreatFabric says it has observed the Trickmo.C variant since January and that it targets users in France, Italy, and Austria.
- The malware is disguised as TikTok or streaming apps and targets banking credentials and cryptocurrency wallets.
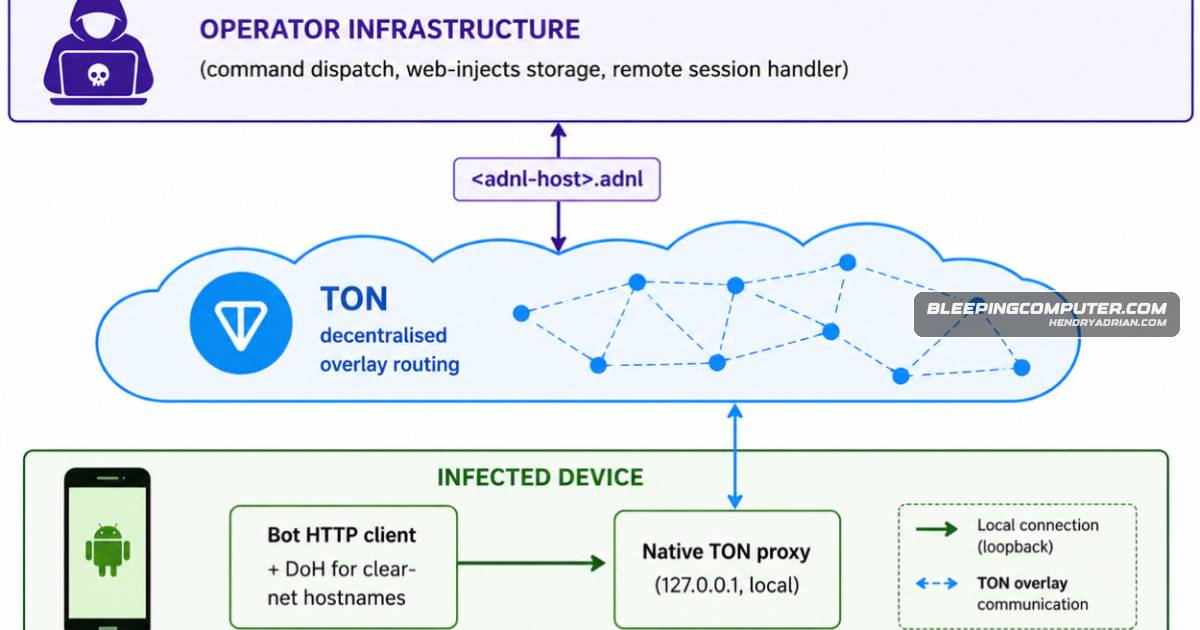
- Its operator communications use .ADNL identities over TON, routed through a local proxy on infected devices, obscuring the underlying server infrastructure.
- TrickMo uses a host APK for loading and persistence, then downloads a runtime APK module for its offensive functions.
- Reported capabilities include phishing overlays, keylogging, screen recording, SMS interception, OTP notification suppression, and clipboard modification.
- New commands include network diagnostics, SSH tunneling, port forwarding, and authenticated SOCKS5 proxy support.
- ThreatFabric found the Pine hooking framework present but inactive, and reported no active NFC functionality despite declared NFC permissions.
Article Details
- Attack Vectors
- Trickmo.C is delivered disguised as fake TikTok and streaming apps.
- The malware uses phishing overlays to target banking credentials.
- Its host APK acts as a loader and persistence layer, then downloads a runtime APK module with offensive functionality.
- The variant communicates with its operator using TON .ADNL addresses routed through an embedded local TON proxy on infected devices.
- Reported capabilities include keylogging, screen recording and streaming, SMS interception, OTP notification suppression, clipboard modification, notification filtering, and screenshot capture.
- New commands provide networking functions and SSH tunneling, port forwarding, and authenticated SOCKS5 proxy support.
- Defensive Notes
- Download software only from Google Play and use apps from reputable publishers.
- Limit the number of installed apps and keep Play Protect active.
MITRE ATT&CK
Malware
Products
AndroidA new TrickMo Android banking malware variant, tracked as Trickmo.C, is being spread through fake TikTok and streaming apps to target banking and crypto wallet users in France, Italy, and Austria.The Open Network (TON)The latest version uses TON-based communications with .ADNL addresses to obscure its command-and-control infrastructure and adds new networking and remote-access commands.TikTokA new TrickMo Android banking malware variant, tracked as Trickmo.C, is being spread through fake TikTok and streaming apps to target banking and crypto wallet users in France, Italy, and Austria.
Tools
Countries
AustriaA new TrickMo Android banking malware variant, tracked as Trickmo.C, is being spread through fake TikTok and streaming apps to target banking and crypto wallet users in France, Italy, and Austria.FranceA new TrickMo Android banking malware variant, tracked as Trickmo.C, is being spread through fake TikTok and streaming apps to target banking and crypto wallet users in France, Italy, and Austria.ItalyA new TrickMo Android banking malware variant, tracked as Trickmo.C, is being spread through fake TikTok and streaming apps to target banking and crypto wallet users in France, Italy, and Austria.
Industries
BankingA new TrickMo Android banking malware variant, tracked as Trickmo.C, is being spread through fake TikTok and streaming apps to target banking and crypto wallet users in France, Italy, and Austria.CryptocurrencyIn a report today, ThreatFabric says that the malware is disguised as TikTok or streaming apps and targets banking and cryptocurrency wallets of users in France, Italy, and Austria.