CloudSEK Details IPL Ticket Scams and Streaming Sites Delivering macOS Infostealer
Summary
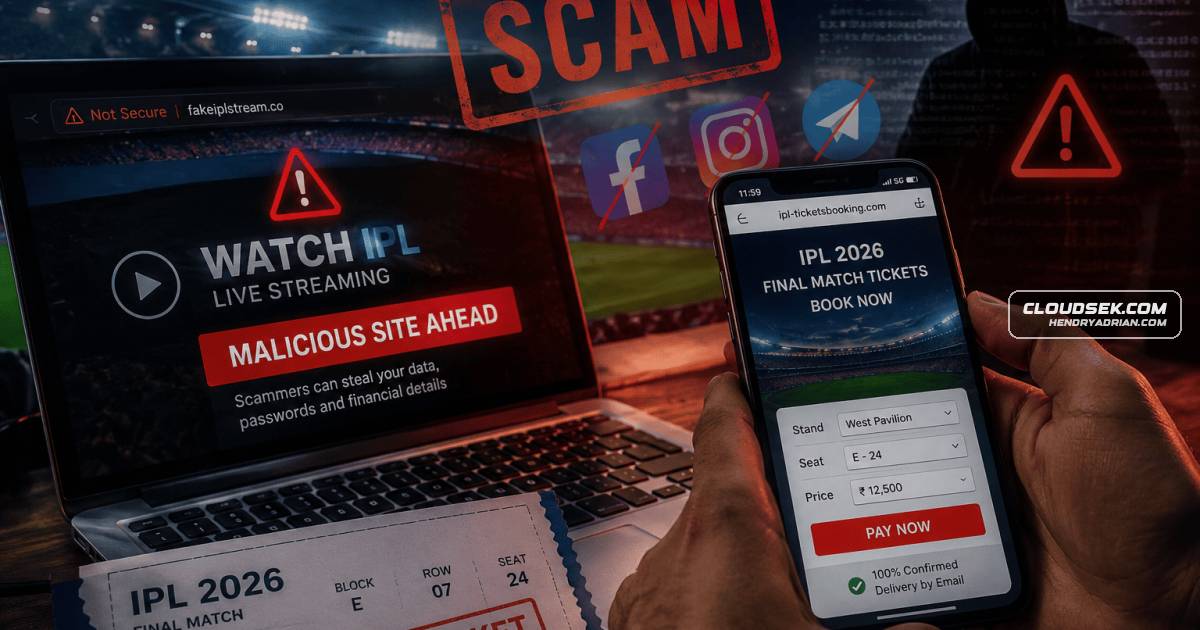
CloudSEK identified more than 600 fake IPL ticket domains and 400-plus streaming sites. Some streaming redirects deliver SHub Stealer, which targets macOS credentials, browser data, crypto wallets and other files, and establishes persistence.
Key points
- Researchers found more than 600 fraudulent ticket domains impersonating platforms such as BookMyShow and District, and more than 400 sites claiming to offer free IPL streams.
- Fake ticket sites collect names, phone numbers, email addresses and payments, then issue fabricated PDF tickets; one exposed admin panel included booking management and victim data.
- Scammers promote ticket offers through social media, ads and search results, using imitation branding and urgency tactics.
- Unofficial streaming sites use intrusive ads and redirect chains; researchers say OS-aware routing can send Mac users to ClickFix pages that prompt them to run Terminal commands.
- The resulting macOS malware, SHub Stealer, targets passwords, browser data, messaging sessions, documents and cryptocurrency wallet data.
- SHub Stealer can tamper with wallet applications to capture seed phrases and install a LaunchAgent for persistence and command execution.
- CloudSEK advises buying tickets through official platforms, avoiding unofficial streams and links, checking URLs, and keeping devices and browsers updated.
Article Details
- Attack Vectors
- Fake ticket-booking domains impersonate legitimate platforms and collect personal and payment details before issuing fabricated tickets.
- Fraudulent ticket offers are promoted through social media posts, reels, groups, and paid ads.
- Unofficial streaming sites are promoted through search results and community posts, then use deceptive overlays, pop-unders, and redirects to route visitors toward malware.
- A ClickFix-style lure directs macOS users to paste a command into Terminal, which retrieves and executes a loader and the SHub Stealer payload.
- The SHub Stealer collects credentials, browser data, wallet information, messaging sessions, and files; it can also modify wallet applications and maintain persistence through a LaunchAgent.
- Defensive Notes
- Buy tickets only through official platforms and avoid links from social media, ads, or unknown websites.
- Avoid unofficial free-streaming sites and links shared through Reddit, Telegram, or Facebook.
- Check URLs carefully for misspellings, unusual domain extensions, extra hyphens, and inserted characters.
- Do not paste commands into Terminal or install software in response to streaming-site prompts.
- Keep devices and browsers updated, limit app permissions, and enable two-factor authentication on email, financial accounts, and crypto wallets.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | book-ipl-ticket-2026[.]online | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | book-iplticket[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | book-my-ticket[.]store | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | book-myshow[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site impersonating a ticketing brand. |
| DOMAIN | book-your-ticket[.]online | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | bookm-show[.]shop | Domain identified by CloudSEK as a fake IPL ticket-selling site impersonating a ticketing brand. |
| DOMAIN | bookmy-show[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site impersonating a ticketing brand. |
| DOMAIN | bookmyiplticket[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | bookmyshow-ipl-ticket[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site impersonating a ticketing brand. |
| DOMAIN | bookmyshowticket[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site impersonating a ticketing brand. |
| DOMAIN | bookmyticket[.]sbs | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | go[.]webcric[.]com | Domain cited as an unofficial streaming option; the article describes such streaming sites as using suspicious redirects and serving as malware-delivery channels. |
| DOMAIN | ipl-ticket-booking[.]online | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | ipl-tickets-booking[.]live | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | ipl2026-ticket[.]online | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | iplticket[.]online | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | iplticket[.]store | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | pavillion-tickets[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | pavilliontickets[.]com | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | stadium-seat-booking[.]online | Domain identified by CloudSEK as a fake IPL ticket-selling site. |
| DOMAIN | thebookmyshow[.]in | Domain identified by CloudSEK as a fake IPL ticket-selling site impersonating a ticketing brand. |
MITRE ATT&CK
T1005 · Data from Local SystemSHub Stealer collects browser files, wallet data, documents, images, and other local files.T1027.013 · Encrypted/Encoded FileThe second-stage loader is described as Base64-encoded and Gzip-compressed.T1036.005 · Match Legitimate Resource Name or LocationThe malware creates a fake Google Update application to make its persistence component appear legitimate.T1041 · Exfiltration Over C2 ChannelThe malware uploads stolen archives and telemetry to its C2.T1056.003 · Web Portal CaptureFake ticket-booking pages collected victims’ names, phone numbers, email addresses, and payment details through web forms.T1059.002 · AppleScriptThe final SHub Stealer payload is a malicious AppleScript executed in the background.T1059.004 · Unix ShellA shell loader was piped to zsh for execution, and the article describes shell-script payload activity.T1082 · System Information DiscoveryThe loader and stealer collect system details including hostname and macOS version.T1105 · Ingress Tool TransferThe loader retrieves a second-stage script and downloads the SHub Stealer payload from C2.T1204.004 · Malicious Copy and PasteClickFix-style pages instructed macOS users to paste a provided command into Terminal.T1543.001 · Launch AgentSHub Stealer establishes persistence by installing a LaunchAgent that runs periodically.T1554 · Compromise Host Software BinaryThe malware replaces wallet applications’ app.asar files with modified versions designed to exfiltrate seed phrases.T1555.001 · KeychainSHub Stealer exfiltrates the victim’s Keychain directory.T1555.003 · Credentials from Web BrowsersSHub Stealer attempts to obtain the Chrome master password and collects browser credential data.T1560.001 · Archive via UtilityThe malware packages stolen data into a zip archive before uploading it.T1566.002 · Spearphishing LinkTicket and streaming links were promoted through social media posts, reels, groups, and ads to lure victims to fraudulent sites.T1583.001 · DomainsOperators registered newly created domains used for fake IPL ticket-booking sites.T1585.003 · Cloud AccountsAccounts used solely to propagate unofficial streaming links are described as part of the distribution campaign.T1608.006 · SEO PoisoningFake ticket and streaming sites were optimized for high-intent search terms to appear in search results.
Malware
Products
BookMyShowticketing platforms by lifting logos, color schemes, and UI layouts directly from trusted brands like BookMyShow and District, creating an experience familiar enough to disarm suspicion.Districtby lifting logos, color schemes, and UI layouts directly from trusted brands like BookMyShow and District, creating an experience familiar enough to disarm suspicion.macOSDuring our testing, we identified that Mac users get routed toward macOS-targeted malware.
Countries
Indiamass attention, emotional investment, and financial activity makes it one of the most exploited events in India's cybercrime calendar.RussiaIf a Russian keyboard is detected, the script sends a "cis_blocked" telemetry event to the command-and-control server and terminates immediately to avoid infecting users in Russia or CIS countries.