
Microsoft Details Kazuar’s Modular Peer-to-Peer Espionage Botnet
Summary
Microsoft researchers say a recent Kazuar variant uses kernel, bridge, and worker modules in a leader-based P2P botnet. It collects data and uses configurable defense bypasses, with non-leader systems staying silent to reduce visibility.
Key points
- Microsoft researchers analyzed a Kazuar variant attributed in the article to Secret Blizzard, an actor associated with Turla.
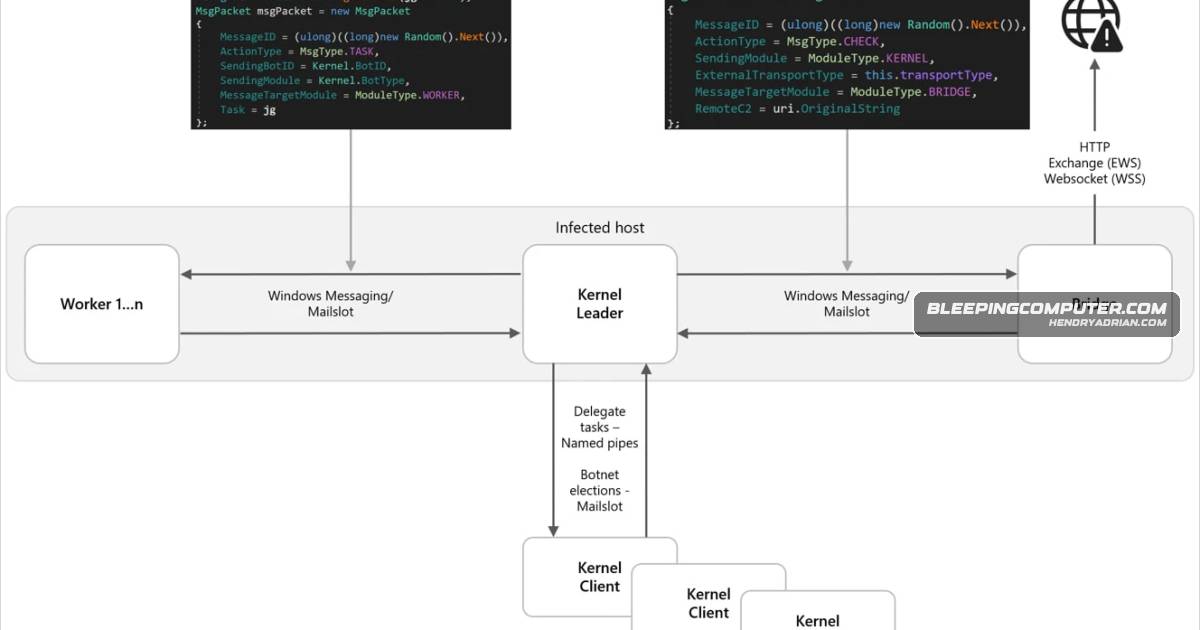
- Kazuar uses kernel, bridge, and worker modules to coordinate tasks, relay communications, and conduct espionage.
- An elected leader communicates with the command-and-control server and relays tasks; other infected systems can remain silent.
- Internal communications use Windows Messaging, Mailslots, and named pipes; messages are AES-encrypted and serialized with Protobuf.
- The worker module can capture keystrokes and screenshots, collect filesystem and email data, and conduct system and network reconnaissance.
- Microsoft says Kazuar supports 150 configuration options, including AMSI, ETW, and WLDP bypasses.
- Microsoft recommends behavioral detection because the malware’s modularity and configurability can make it evasive.
Article Details
- Attack Vectors
- Kazuar operates as a modular peer-to-peer botnet with Kernel, Bridge, and Worker modules.
- One infected Kernel module is elected to communicate with the C2 server and relay tasks internally; non-leader systems remain silent toward the C2.
- The Bridge module relays external traffic using HTTP, WebSockets, or Exchange Web Services.
- Internal module communications use Windows Messaging, Mailslots, and named pipes, with AES-encrypted, Protocol Buffers-serialized messages.
- The Worker module conducts espionage activities including keylogging, screenshot capture, filesystem data collection, reconnaissance, and email/MAPI collection.
- Collected data is encrypted, staged locally, and later exfiltrated through the Bridge module.
- Kazuar supports AMSI, ETW, and WLDP bypasses and process injection.
- Defensive Notes
- Microsoft recommends prioritizing behavioral detection over static signatures because Kazuar is modular, configurable, and designed for stealth.
- The article reports that non-leader infected systems do not communicate directly with the C2, reducing external traffic and visibility.
MITRE ATT&CK
T1005 · Data from Local SystemKazuar collects data from infected systems' filesystems and steals recent files.T1041 · Exfiltration Over C2 ChannelKazuar exfiltrates collected data through the Bridge module, which relays traffic to the C2 infrastructure.T1055 · Process InjectionThe article says Kazuar supports process injection.T1056.001 · KeyloggingKazuar's Worker module performs keylogging.T1071.001 · Web ProtocolsKazuar's Bridge module communicates with remote C2 infrastructure using HTTP and WebSockets.T1074.001 · Local Data StagingKazuar encrypts collected data and stages it locally before later exfiltration.T1113 · Screen CaptureKazuar's Worker module captures screenshots.T1114.001 · Local Email CollectionKazuar collects email/MAPI data, including Outlook downloads.T1562.001 · Disable or Modify ToolsKazuar offers AMSI, ETW, and WLDP bypass options.
Threat Actors
Malware
Vendors
Countries
Industries
DefenseRussian intelligence service (FSB) and is known for targeting government and diplomatic organizations, defense-related entities, and critical systems across Europe, Asia, and Ukraine.GovernmentBear, has been associated with the Russian intelligence service (FSB) and is known for targeting government and diplomatic organizations, defense-related entities, and critical systems across Europe, Asia, and