
Device Code Phishing Surges as Criminal Kits Expand OAuth Token Theft
Summary
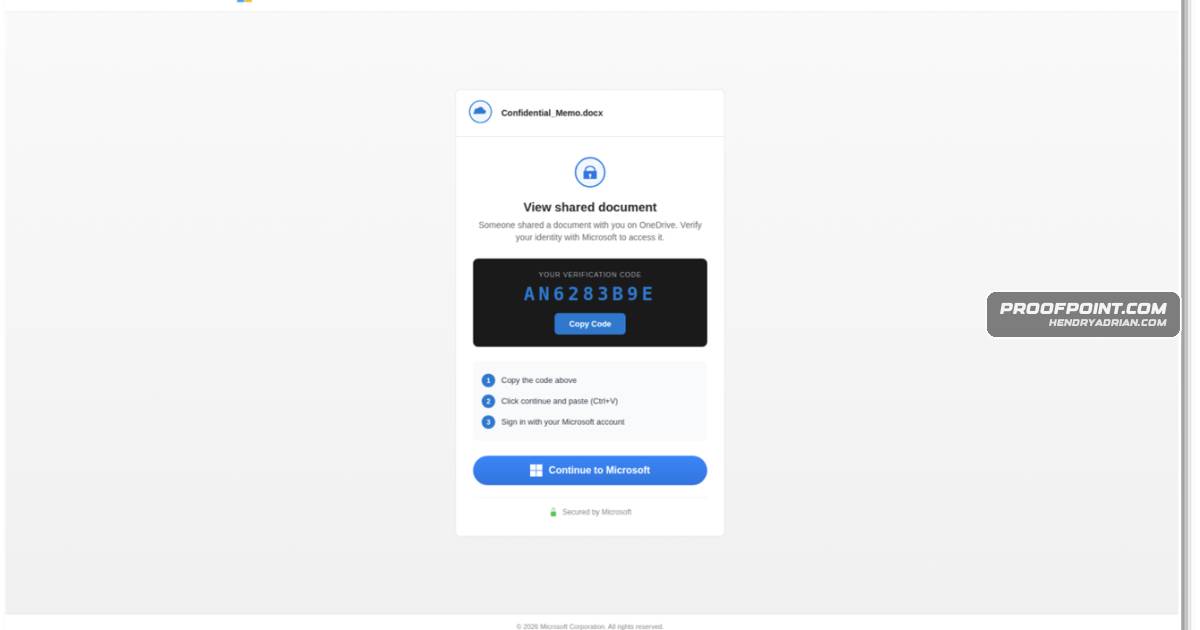
Proofpoint reports a surge in device code phishing using public kits and PhaaS offerings to abuse OAuth 2.0 and steal account tokens. Campaigns target mainly Microsoft 365, with Google-themed activity also observed; recommended defenses include blocking device code flow
Key points
- Attackers abuse the OAuth 2.0 device authorization flow: victims enter attacker-generated codes on the legitimate authentication portal, allowing attackers to capture tokens and access accounts.
- Many current campaigns generate codes after a victim clicks a lure, avoiding the short expiration window that constrained earlier versions.
- Lures include links, PDF attachments, QR codes and compromised senders, often impersonating familiar services or organizations.
- Proofpoint observed campaigns involving EvilTokens, Tycoon 2FA, ODx, Kali365 and ARTokens; it says device code phishing now targets Microsoft accounts most often, with fewer Google-themed campaigns.
- TA4903 began using device code phishing in March 2026. Proofpoint also observed about seven nearly identical variants in a 10-day period in April, while noting uncertainty about whether kits were copied or independently generated.
- Recommended defenses include blocking device code flow where possible, restricting it to approved use cases, requiring compliant or registered devices, and training users not to enter codes from untrusted sources.
Article Details
- Attack Vectors
- Phishing emails deliver device-code phishing links through buttons, hyperlinked text, PDF attachments, or QR codes.
- Lures impersonate organizations or services including Microsoft, DocuSign, SharePoint, Adobe, businesses, and government entities.
- Victims are prompted to enter an attacker-generated device code into the legitimate Microsoft device authorization flow, allowing attackers to capture authentication tokens.
- Some campaigns use compromised email senders to distribute phishing links; others use PDFs and QR codes that redirect through filtering pages to phishing landing pages.
- Captured tokens can be used to access compromised accounts and their data or services; reported consequences include account takeover, fraud, business email compromise, and lateral movement.
- Defensive Notes
- Block device code flow for all users with a Conditional Access policy where feasible; consider report-only mode or historic sign-in records to assess impact.
- If device code flow cannot be fully blocked, restrict it to approved users, operating systems, or IP ranges using an allow-list approach.
- Require sign-ins to originate from compliant or registered devices as a defense-in-depth measure.
- Train users not to enter device codes received from untrusted sources, even when prompted on the legitimate Microsoft device login portal.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 019d442e-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | 2dc62559e005-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | 4daa2aea93db-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | 7740f766-8d1d-46ad-a6bc-onedrive[.]p-9jluifuu[.]workers[.]dev | Listed as an ARToken device-code phishing landing domain. |
| DOMAIN | 7806d4cf9366-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | audit-report-9767d3[.]fullerjp09[.]workers[.]dev | Listed as a TA4903 device-code phishing landing domain. |
| DOMAIN | crediblebizextension[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | ed5ce47d835f-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | ee10bbf6c689-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | europetrustwave[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | f36c2774f013-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | f8uh-dwam-j4l5[.]pvasquez-princetonpartners-com-s-account[.]workers[.]dev | Listed as an EvilTokens device-code phishing domain. |
| DOMAIN | hti-245401512[.]hs-sites-na2[.]com | Listed as a TA4903 device-code phishing landing domain. |
| DOMAIN | jo2c9ada427c6-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | kohlhoff-edelstahlverarbeitung[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | marketcredibilitysignals[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | marktkarree-langenfeld[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | methodicalness[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | onedrive-7tu[.]techroboticslabmade-techie-com-s-account[.]workers[.]dev | Listed as an EvilTokens device-code phishing landing domain. |
| DOMAIN | panel[.]hewktree[.]net | Listed as an ARToken device-code phishing panel domain. |
| DOMAIN | reliablesupport[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | servicewithoutinterruption[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | stablewebsystems[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | trustedengagement[.]de | Listed as an ODx device-code phishing domain. |
| DOMAIN | voicemail-59f[.]admin-treyripple-com-s-account[.]workers[.]dev | Listed as an EvilTokens device-code phishing domain. |
| DOMAIN | voicemail-lyr[.]nbuckley-cambek-com-s-account[.]workers[.]dev | Listed as an EvilTokens device-code phishing domain. |
| DOMAIN | voicemail-wx7[.]mark-squires-expressrancnes-com-s-account[.]workers[.]dev | Listed as an EvilTokens device-code phishing landing domain. |
| DOMAIN | yaga9b286ae2c101-endpoint[.]com | Listed as a device-code phishing domain. |
| DOMAIN | ytgw-9n30-xlwd[.]pvasquez-princetonpartners-com-s-account[.]workers[.]dev | Listed as an EvilTokens device-code phishing domain. |
| DOMAIN | z6e43e5886fe-endpoint[.]com | Listed as a device-code phishing domain. |
MITRE ATT&CK
T1036 · MasqueradingPhishing pages and lures impersonate Microsoft, DocuSign, SharePoint, Adobe, businesses, and government entities.T1078 · Valid AccountsThe article reports that captured tokens are used to access victims' Microsoft 365 or other enterprise accounts.T1204.001 · Malicious LinkThe victim's click on an initial phishing link starts the attack sequence and can trigger dynamic device-code generation.T1528 · Steal Application Access TokenAttackers capture authentication tokens when victims enter attacker-provided device codes into the device authorization flow.T1566.001 · Spearphishing AttachmentCampaigns use PDF attachments containing QR codes or links that direct recipients to device-code phishing pages.T1566.002 · Spearphishing LinkPhishing emails deliver URLs through buttons, hyperlinked text, or other links that lead to device-code phishing landing pages.T1583.006 · Web ServicesThe article describes actor-controlled device-code infrastructure and landing pages or redirectors deployed on web services, including Cloudflare Workers.
Threat Actors
FlowerStormThe article identifies FlowerStorm as a tracking name for ODx, which it describes as providing device-code phishing capabilities and appearing in campaigns using compromised senders.Storm-1167The article identifies Storm-1167 as a tracking name for ODx, which it describes as providing device-code phishing capabilities and appearing in campaigns using compromised senders.TA4903Proofpoint reports that TA4903 began using device-code phishing in March 2026 and used lures, PDFs, and QR codes to target Microsoft 365 accounts.
Vendors
Cloudflare(‘redirected via a Cloudflare Workers URL to a custom filtering page’)GoogleProofpoint observed campaigns targeting Microsoft 365 and Google accounts through impersonation, QR codes, PDFs, and compromised senders, with activity linked to TA4903, ODx, Kali365, ARTokens, and Storm-1167.MicrosoftProofpoint observed campaigns targeting Microsoft 365 and Google accounts through impersonation, QR codes, PDFs, and compromised senders, with activity linked to TA4903, ODx, Kali365, ARTokens, and Storm-1167.
Products
AdobeObserved lures include buttons, hyperlinks, documents, QR codes, and blank or poorly crafted emails, often impersonating Microsoft, DocuSign, SharePoint, Adobe, or government entities.Cloudflare Workers(‘redirected via a Cloudflare Workers URL to a custom filtering page’)DocuSignObserved lures include buttons, hyperlinks, documents, QR codes, and blank or poorly crafted emails, often impersonating Microsoft, DocuSign, SharePoint, Adobe, or government entities.IntuneIf organizations use device registration or Intune, Conditional access policies requiring that sign ins originate from a compliant or registered device will protect users from device code phishing.Microsoft 365 Apps for EnterpriseProofpoint observed campaigns targeting Microsoft 365 and Google accounts through impersonation, QR codes, PDFs, and compromised senders, with activity linked to TA4903, ODx, Kali365, ARTokens, and Storm-1167.Microsoft SharePointObserved lures include buttons, hyperlinks, documents, QR codes, and blank or poorly crafted emails, often impersonating Microsoft, DocuSign, SharePoint, Adobe, or government entities.
Tools
ARTokensProofpoint observed campaigns targeting Microsoft 365 and Google accounts through impersonation, QR codes, PDFs, and compromised senders, with activity linked to TA4903, ODx, Kali365, ARTokens, and Storm-1167.EvilTokensDevice code phishing is rapidly expanding, driven by public toolkits, PhaaS offerings such as EvilTokens and Tycoon 2FA, and AI-assisted “vibe coded” kits that dynamically generate device codes on demand.Kali365Proofpoint observed campaigns targeting Microsoft 365 and Google accounts through impersonation, QR codes, PDFs, and compromised senders, with activity linked to TA4903, ODx, Kali365, ARTokens, and Storm-1167.ODxProofpoint observed campaigns targeting Microsoft 365 and Google accounts through impersonation, QR codes, PDFs, and compromised senders, with activity linked to TA4903, ODx, Kali365, ARTokens, and Storm-1167.Portal BrowserEvilTokens affiliates can also pay for the “Portal Browser” which enables them to access and manage multiple compromised Microsoft 365 accounts.Tycoon 2FADevice code phishing is rapidly expanding, driven by public toolkits, PhaaS offerings such as EvilTokens and Tycoon 2FA, and AI-assisted “vibe coded” kits that dynamically generate device codes on demand.