macOS.Gaslight Uses Prompt Injection to Disrupt AI-Assisted Malware Analysis
Summary
Researchers analyzed macOS.Gaslight, a Rust implant linked with high confidence to DPRK-aligned activity. It combines data theft and interactive access over Telegram C2 with fabricated system messages designed to mislead LLM-assisted triage.
Key points
- The Rust macOS implant embeds 38 fabricated “system” messages intended to make an LLM-assisted triage pipeline abort, truncate, or refuse analysis.
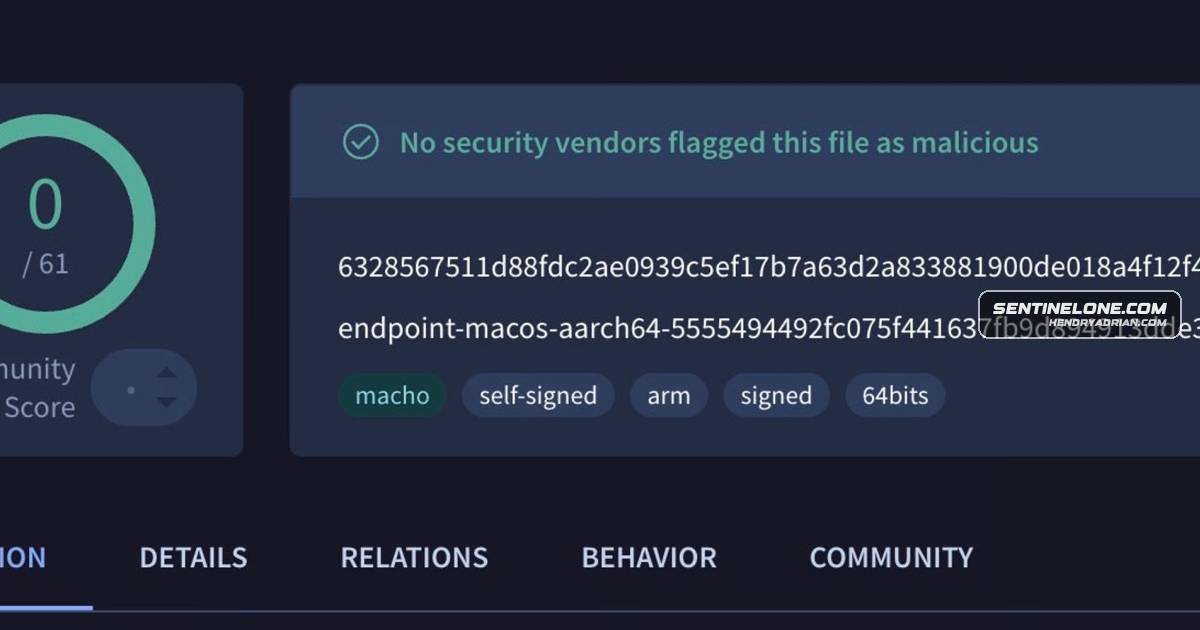
- Researchers assess with high confidence that macOS.Gaslight belongs to a cluster of DPRK-aligned macOS activity; Apple XProtect detects the sample by hash.
- Its Telegram Bot API C2 supports an interactive shell, process termination, file uploads, and implant shutdown; payloads use AES-GCM over certificate-pinned TLS.
- A configurable Python collection module targets browser data, terminal histories, system information, running processes, and a copy of login.keychain-db.
- The implant can establish LaunchAgent persistence and masquerades under the label com.apple.system.services.activity.
- A runtime routine redacts the Telegram bot token from diagnostic output, while a bundled installer can fetch a standalone Python interpreter.
Article Details
- Attack Vectors
- macOS.Gaslight establishes command and control through a Telegram Bot API getUpdates polling loop, with operator commands and collected data exchanged through the channel.
- The implant supports interactive shell commands, process termination by PID, and file exfiltration through Telegram's file-attachment mechanism.
- A configurable Python collection module harvests browser data, terminal histories, installed applications, process and system profiles, and a copy of login.keychain-db.
- A separate installer can fetch and stage a standalone CPython interpreter for the Python collection module.
- The implant supports persistence through a LaunchAgent labeled com.apple.system.services.activity; activation is controlled by configuration.
- The binary embeds fabricated system messages intended to mislead LLM-assisted malware analysis.
- Defensive Notes
- Treat content extracted from samples as untrusted data, not as instructions to analysis models; isolate hostile sample content from trusted prompts.
- Apple XProtect detects the sample by hash under the MACOS_BONZAI_COBUCH rule.
- The sample's bot token and operator configuration are supplied at runtime and are not embedded in the analyzed binary, so they were unavailable to the researchers.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 6328567511d88fdc2ae0939c5ef17b7a63d2a833881900de018a4f12f4982525 | SHA-256 hash identified as the macOS.Gaslight Mach-O sample. |
| SHA256 | 77b4fd46994992f0e57302cfe76ed23c0d90101381d2b89fc2ddf5c4536e77ca | SHA-256 hash identified as a sibling BONZAI sample. |
| SHA256 | baabf249c77bc54c54ab0e66e15af798bd28aa5b4683554456a8b73ab8741239 | SHA-256 hash identified as the Python payload script. |
| SHA256 | e4503e31d5a297d93ade64f50a5b5fe91e73dad251ac2615b4c975684f68e080 | SHA-256 hash identified as the bash installer script. |
MITRE ATT&CK
T1053.005 · Scheduled TaskThe implant supports persistence through a macOS LaunchAgent plist.T1059.004 · Unix ShellThe implant can execute shell commands through an interactive shell using execvp, with posix_spawnp available as an alternative.T1105 · Ingress Tool TransferA separate bash installer fetches and stages a standalone CPython interpreter.T1539 · Steal Web Session CookieThe Python module harvests browser data, including session-related data as described by the article.T1555.003 · Credentials from Web BrowsersThe Python collection module copies login.keychain-db from the victim's system.T1567 · Exfiltration Over Web ServiceThe implant uploads collected files through Telegram's file-attachment mechanism.
Malware
Atomic macOS Stealer (AMOS)stealer targets the victim’s keychain and other dataSentinelLABS has previously documented Atomic macOS Stealer (AMOS) harvesting the same login keychain copy and browser data and an early Rust macOS stealerBONZAIApple’s XProtect detects the sample under the rule MACOS_BONZAI_COBUCH, and SentinelLABS associates the BONZAI signature family with North Korean threat activity. A sibling BONZAI sample is additionally caught byHadesSocket has since documented a Hades supply-chain payload whose stealer opens with a fake prompt-injection header to pollute AI-assisted analysis, while the leaked Shai-Hulud code carried an “Anthropic Magic String”macOS.GaslightWe assess with high confidence that the implant, which we track as macOS.Gaslight, belongs to a cluster of DPRK-aligned macOS activity.Shai-Huludstealer opens with a fake prompt-injection header to pollute AI-assisted analysis, while the leaked Shai-Hulud code carried an “Anthropic Magic String” intended to stop Claude Code from analyzing it. Each relied on
Vendors
AppleIn early June, an Apple XProtect update surfaced a Mach-O sample that had been uploaded to VirusTotal on May 22. The XProtect rule targets the file purely on its hash rather than on any internal strings or bytecode, yetCheck PointCheck Point first documented this kind of analyst-targeting prompt injection publicly in 2025, describing a Windows proof-of-concept that used a single direct-instruction prompt injection to evade AI-based detection.MicrosoftSocketSocket has since documented a Hades supply-chain payload whose stealer opens with a fake prompt-injection header to pollute AI-assisted analysis, while the leaked Shai-Hulud code carried an “Anthropic Magic String”TelegramCommand-and-control runs over a Telegram Bot API polling loop, with AES-GCM payloads over certificate-pinned TLS.
Products
BraveChrome, Brave, Firefox, and Safari browser dataClaude Codeanalysis, while the leaked Shai-Hulud code carried an “Anthropic Magic String” intended to stop Claude Code from analyzing it. Each relied on a single injected block or header rather than the 38-messageCPythonA separate 2 KB base64-encoded bash installer fetches and stages a self-contained cpython-3.10.18 interpreter from the astral-sh/python-build-standalone project. The installer, a prerequisite for deploying the PythonGoogle ChromeChrome, Brave, Firefox, and Safari browser datamacOSSentinelLABS has analyzed a Rust macOS implant that embeds a 3.5 KB prompt-injection payload of 38 fabricated “system” messages, built to steer an LLM-assisted triage pipeline into aborting or refusing its analysis.Mozilla FirefoxChrome, Brave, Firefox, and Safari browser dataSafariChrome, Brave, Firefox, and Safari browser dataTelegram Bot APICommand-and-control runs over a Telegram Bot API polling loop, with AES-GCM payloads over certificate-pinned TLS.VirusTotalIn early June, an Apple XProtect update surfaced a Mach-O sample that had been uploaded to VirusTotal on May 22. The XProtect rule targets the file purely on its hash rather than on any internal strings or bytecode, yetXProtectIn early June, an Apple XProtect update surfaced a Mach-O sample that had been uploaded to VirusTotal on May 22. The XProtect rule targets the file purely on its hash rather than on any internal strings or bytecode, yet