
DNS Investigation Examines Shadow-Earth-053 Infrastructure
Summary
A DNS/WHOIS investigation of the China-aligned Shadow-Earth-053 campaigns examined 31 core indicators and related infrastructure, alongside reported Exchange and IIS exploitation, GODZILLA persistence, and ShadowPad DLL sideloading.
Key points
- Researchers characterize Shadow-Earth-053 as China-aligned campaigns targeting government entities and critical infrastructure in parts of Asia and a NATO member state.
- The article reports exploitation of N-day flaws in internet-facing Microsoft Exchange and IIS servers, deployment of GODZILLA for persistence, and ShadowPad staging through DLL sideloading.
- The investigation expanded an earlier set of 26 network indicators to 31 core IoCs: 16 subdomains, 10 domains and five IP addresses.
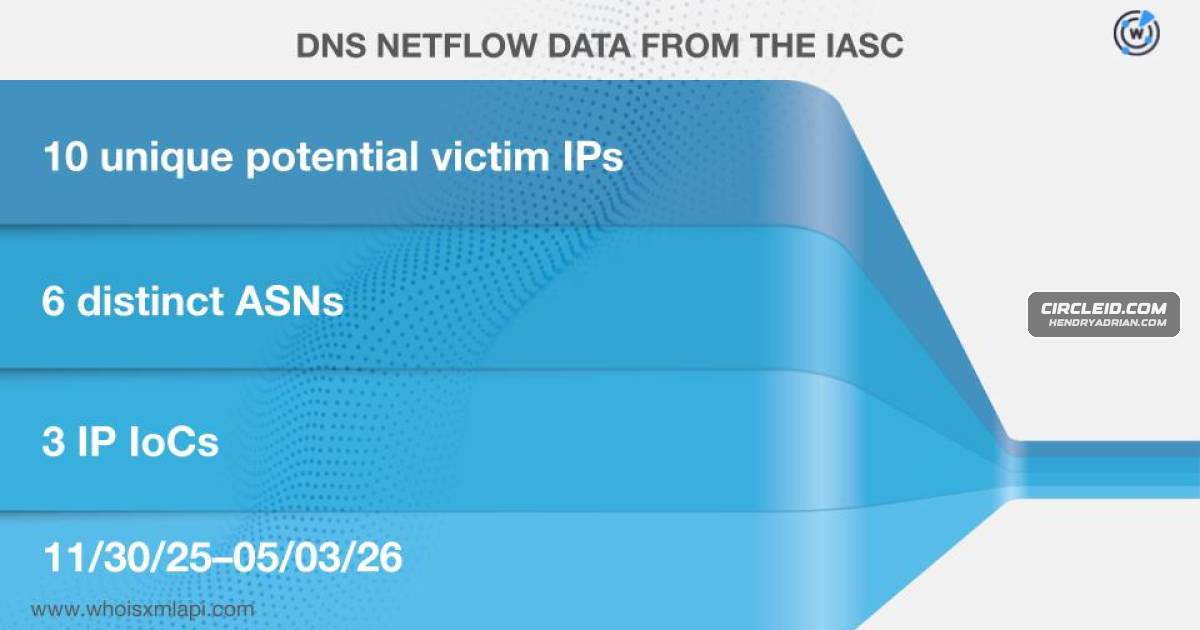
- Traffic data showed 865 client IP addresses communicating with three domain IoCs through 3,476 DNS queries between March 6 and May 4, 2026.
- WHOIS analysis linked public historical registration email addresses to 835 additional domains; DNS research also identified additional IP and domain artifacts.
- The researchers caution that some entities labeled malicious could later be found harmless and recommend further investigation to corroborate findings.
Article Details
- Attack Vectors
- The operators exploited N-day vulnerabilities in internet-facing Microsoft Exchange and IIS servers to gain initial access.
- ShadowPad implants were staged through DLL sideloading of legitimate signed executables.
- GODZILLA was deployed to maintain persistent access on compromised servers.
- The researchers describe a possible chain involving rogue DNS resolution, router compromise, traffic interception, and credential harvesting.
- Defensive Notes
- The article recommends supplementary investigation to corroborate entities identified as threats, noting that some may later prove harmless or require further context.
- The investigation used DNS-resolution and WHOIS-history data to connect campaign IoCs with related infrastructure.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | dnserver[.]life | Listed as a campaign domain IoC with historical domain-to-IP resolutions. |
| DOMAIN | dnsmaps[.]com | Listed among campaign domain IoCs that continued to resolve to IP addresses in 2026. |
| DOMAIN | group-ib[.]icu | Listed among campaign domain IoCs that continued to resolve to IP addresses in 2026. |
| DOMAIN | kaspersky[.]icu | Campaign domain IoC serving as the parent zone for subdomains described as operator-controlled infrastructure impersonating Kaspersky. |
| DOMAIN | microsi0ft[.]com | Listed among campaign domain IoCs that continued to resolve to IP addresses in 2026. |
| DOMAIN | microsofttrends[.]com | Listed as a campaign domain IoC; the article reports historical DNS resolutions and continued resolution in 2026. |
| DOMAIN | office365-update[.]com | Campaign domain IoC recorded on the First Watch Malicious Domains Data Feed; the article says it was likely registered with malicious intent. |
| DOMAIN | zimbra-beta[.]info | Campaign domain IoC recorded on the First Watch Malicious Domains Data Feed; the article says it was likely registered with malicious intent. |
| DOMAIN | zimbra[.]life | Listed among campaign domain IoCs that continued to resolve to IP addresses in 2026. |
| HOSTNAME | cert[.]kaspersky[.]icu | Campaign subdomain IoC impersonating Kaspersky; the article says it may target industrial and security professionals. |
| HOSTNAME | erp[.]kaspersky[.]icu | Campaign subdomain IoC described as able to serve fake enterprise-portal login pages for credential theft. |
| HOSTNAME | news[.]kaspersky[.]icu | Campaign subdomain IoC described as a potential distributor of fake threat reports or malware disguised as software updates. |
| HOSTNAME | ns1[.]kaspersky[.]icu | Campaign subdomain IoC; the article describes it as an NS record providing DNS control under the impersonating Kaspersky zone. |
| HOSTNAME | ns2[.]kaspersky[.]icu | Campaign subdomain IoC described as paired with ns1[.]kaspersky[.]icu in an operator-controlled DNS zone. |
| IPV4 | 194[.]38[.]11[.]3 | One of the campaign's IP IoCs; the article reports 757 historical IP-to-domain resolutions. |
MITRE ATT&CK
T1190 · Exploit Public-Facing ApplicationThe operators exploited N-day flaws in internet-facing Microsoft Exchange and IIS servers to gain initial access.T1505.003 · Web ShellThe article identifies GODZILLA as a web shell used to maintain access on compromised servers.T1574.002 · DLL Side-LoadingThe article says ShadowPad implants were staged by DLL sideloading through legitimate signed executables.
Threat Actors
Malware
GodzillaThe attackers used GODZILLA for persistence and ShadowPad via DLL sideloading, while researchers uncovered 31 core IoCs and many related domains, IPs, and email-linked artifacts.ShadowPadThe attackers used GODZILLA for persistence and ShadowPad via DLL sideloading, while researchers uncovered 31 core IoCs and many related domains, IPs, and email-linked artifacts.
Vendors
Products
IISShadow-Earth-053 is a China-aligned campaign set that targeted government entities and critical infrastructure across Asia and a NATO member state by exploiting Microsoft Exchange and IIS N-day flaws.Microsoft ExchangeShadow-Earth-053 is a China-aligned campaign set that targeted government entities and critical infrastructure across Asia and a NATO member state by exploiting Microsoft Exchange and IIS N-day flaws.
Tools
Bulk IP Geolocation LookupWe then queried the IP IoCs on Bulk IP Geolocation Lookup and discovered that:DNS Chronicle APIWe then queried the domain IoCs on DNS Chronicle API and discovered that nine recorded 1,297 historical domain-to-IP resolutions over time.DNS Lookup APINext, we queried the domain IoCs on DNS Lookup API, which led to the discovery of nine unique additional IP addresses.First Watch Malicious Domains Data FeedIn addition, we discovered that two domain IoCs—zimbra-beta[.]info and office365-update[.]com—were recorded on the First Watch Malicious Domains Data Feed.Reverse WHOIS APIWe then queried the public email addresses on Reverse WHOIS API and found out that they were used to register 835 unique email-connected domains after the domain IoCs were filtered out.WHOIS APINext, we queried the domain IoCs on WHOIS API and found out that:WHOIS History APIWe began by querying the 10 domain IoCs on WHOIS History API and discovered that eight had 32 email addresses in their historical WHOIS records.WhoisXML API MCP ServerAccording to the WhoisXML API MCP Server, none of the domains were legitimate and all were currently active.
Industries
Critical infrastructureShadow-Earth-053 is a China-aligned campaign set that targeted government entities and critical infrastructure across Asia and a NATO member state by exploiting Microsoft Exchange and IIS N-day flaws.GovernmentShadow-Earth-053 is a China-aligned campaign set that targeted government entities and critical infrastructure across Asia and a NATO member state by exploiting Microsoft Exchange and IIS N-day flaws.