
SentinelLABS Details Suspected China- and India-Nexus Espionage Against Pakistani Police
Summary
SentinelLABS tracked suspected China- and India-nexus intrusions against Pakistani law enforcement from 2024 to 2026, identifying Balochistan Police as the main target and a compromised complaint portal hosting malware implants.
Key points
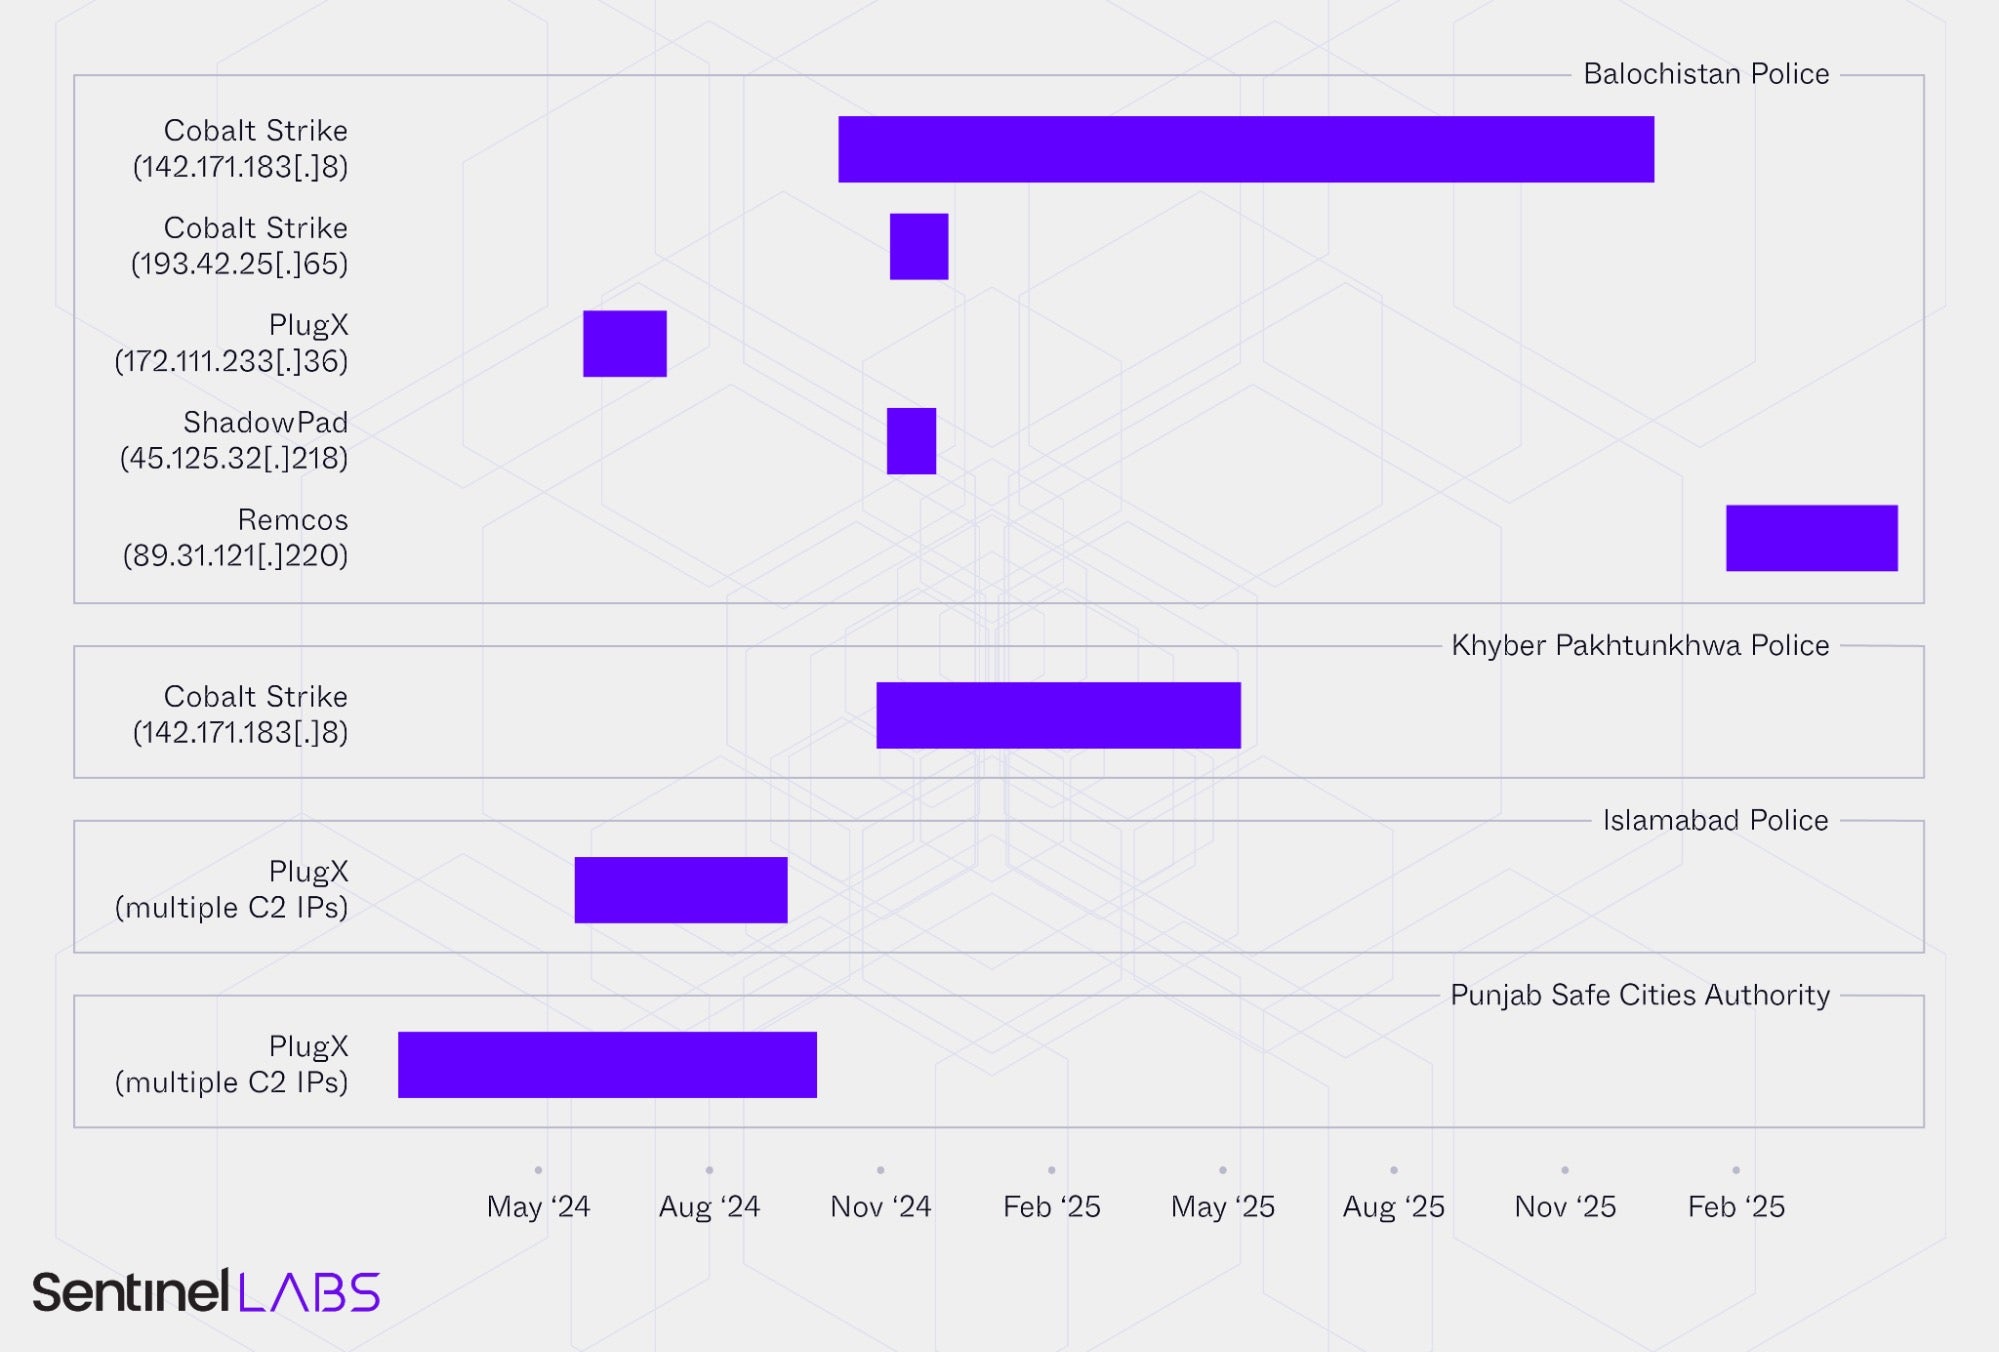
- SentinelLABS observed intrusions against several Pakistani law enforcement organizations from February 2024 to April 2026, with the highest concentration at Balochistan Police.
- Researchers grouped command-and-control activity into PlugX, ShadowPad, Cobalt Strike, and Remcos clusters; they assessed the activity as involving suspected China- and India-nexus actors, with varying attribution confidence.
- The Remcos cluster was associated with suspected India-nexus activity tracked as TAG-179. A related lure used a decoy document about repatriation coordination among police, government, and intelligence organizations.
- Affected Balochistan Police assets included network appliances and servers hosting applications for personnel, criminal, biometric, vehicle, hotel, tenant, and citizen-complaint records. Access to the underlying data stores was described as a possibility, not confirmed.
- Researchers found two cms_plugin.exe variants hosted on the compromised Complaint Management System: a Rust stager that downloaded another payload and a .NET executable that masqueraded as 360Safe.exe and loaded an AsyncRAT client.
- A fake portal-update message and the implants’ placement suggested targeting of staff and citizens using the CMS. Successful execution could provide access to users’ devices and, for police staff, a potential foothold into internal networks.
Article Details
- Attack Vectors
- A suspected China-nexus actor compromised the Balochistan Police Complaint Management System (CMS) and placed two variants of cms_plugin.exe in the portal's client scripts directory.
- The Rust cms_plugin.exe stager downloaded a next-stage payload from 193.42.25[.]65 and executed it.
- The .NET cms_plugin.exe masqueraded as 360Safe.exe and reflectively loaded an assembly implementing an AsyncRAT client configured to use 41.216.188[.]140.
- The implants displayed “Update Complete! Please refresh the page” to imitate a CMS update and were aimed at users of the portal, including police staff and citizens.
- TAG-179-associated lure files included a decoy document posing as an operational plan for repatriating undocumented foreigners and coordinating police activity.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 142[.]171[.]183[.]8 | Cobalt Strike C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]111[.]233[.]105 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]111[.]233[.]12 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]111[.]233[.]26 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]111[.]233[.]36 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]111[.]233[.]96 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]94[.]9[.]19 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]94[.]9[.]43 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 172[.]94[.]9[.]49 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 193[.]42[.]25[.]65 | Cobalt Strike C2 server and next-stage payload source used by the CMS implant stager. |
| IPV4 | 41[.]216[.]188[.]140 | C2 server configured in the AsyncRAT client embedded in the CMS implant. |
| IPV4 | 45[.]125[.]32[.]218 | ShadowPad C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 45[.]74[.]6[.]17 | PlugX C2 server communicating with Pakistani law enforcement infrastructure. |
| IPV4 | 89[.]31[.]121[.]220 | Remcos C2 server attributed by the researchers to suspected India-nexus activity tracked as TAG-179. |
| SHA1 | 000fad96a85dd6933c22d3dbec9aed47b7f1f066 | Hash of a TAG-179 backdoor launcher. |
| SHA1 | 08570471f39bb6725f07b8cddbea99ed48c22686 | Hash of a TAG-179 backdoor launcher. |
| SHA1 | 23f4766c011d193f076dfc735dc460e2a41ead79 | Hash of a TAG-179 backdoor launcher. |
| SHA1 | 23f6781919a50b118d8d4e6a7e9ae63b71ecc885 | Hash of a cms_plugin.exe implant sample. |
| SHA1 | 4039454c9189e64285e93fc075a30b93f814b5b5 | Hash of a cms_plugin.exe implant sample. |
| SHA1 | 47f8cb0c2dcf62702f58cfc1603d6325755f6820 | Hash of a TAG-179 backdoor launcher. |
| SHA1 | 539bd79fbb684edea94eb37518134b97e94b9dd8 | Hash of a TAG-179 lure file. |
| SHA1 | 58cb2d95063b9df807b7aa8dc106b74ce988a491 | Hash of a cms_plugin.exe implant sample. |
| SHA1 | 5d60ff36ff519c2e13e7f66cfa0bb46be79592a7 | Hash of a TAG-179 backdoor. |
| SHA1 | 63b88d00331de88af696dfb7a896935d830e485f | Hash of a TAG-179 backdoor. |
| SHA1 | 6fe2e74d009abbd56de01fd7404a1245e9b47c79 | Hash of a TAG-179 lure file. |
| SHA1 | 71757adba833b46f961e840d0f055bcce0b529c4 | Hash of a TAG-179 lure file. |
| SHA1 | 8c329db96e093fa25268e078405a33c518dbb5c9 | Hash of a TAG-179 backdoor. |
| SHA1 | c6c197e61079a0a33108c2c87b5e3c7056a138ec | Hash of a TAG-179 lure file. |
| SHA1 | d66ab0cd2e44dc8389c111b7ed34c7bcb0b35311 | Hash of a TAG-179 backdoor. |
| URL | hxxps[:]//cms[.]balochistanpolice[.]gov[.]pk/client%20scripts/cms_plugin.exe | Specific CMS-hosted URL identified as the location of malicious implant files. |
MITRE ATT&CK
T1036.005 · Match Legitimate Resource Name or LocationThe .NET cms_plugin.exe masqueraded as 360Safe.exe, a component of 360 Safe Guard.T1105 · Ingress Tool TransferThe Rust cms_plugin.exe stager downloaded a next-stage payload from 193.42.25[.]65 and executed it.T1204.002 · Malicious FileThe implants were placed on the CMS portal and disguised as an update to induce portal users to run the executable.
Threat Actors
BitterQihoo 360 tracking name for a threat actor whose infrastructure, tooling, and TTPs overlap to varying degrees with TAG-179 activity. The article explicitly gives Bitter as an alternate name for APT-C-08.Mysterious ElephantKaspersky tracking name for a threat actor whose infrastructure, tooling, and TTPs overlap to varying degrees with TAG-179 activity; the article does not identify them as the same actor.TAG-179Recorded Future tracks this suspected India-nexus actor, which the researchers associate with the Remcos C2 server 89.31.121[.]220 and with lure files and backdoor components relevant to Pakistani law enforcement.
Malware
AsyncRATThe activity involved PlugX, ShadowPad, Cobalt Strike, Remcos, AsyncRAT, TAG-179, and compromised infrastructure tied to sensitive police, citizen, and biometric records.PlugXThe activity involved PlugX, ShadowPad, Cobalt Strike, Remcos, AsyncRAT, TAG-179, and compromised infrastructure tied to sensitive police, citizen, and biometric records.RemcosThe activity involved PlugX, ShadowPad, Cobalt Strike, Remcos, AsyncRAT, TAG-179, and compromised infrastructure tied to sensitive police, citizen, and biometric records.ShadowPadThe activity involved PlugX, ShadowPad, Cobalt Strike, Remcos, AsyncRAT, TAG-179, and compromised infrastructure tied to sensitive police, citizen, and biometric records.
Vendors
Products
360 Safe GuardThe .NET executable masquerades as 360Safe.exe, a component of the endpoint security software 360 Safe Guard from the Chinese vendor Qihoo 360.Complaint Management SystemThey affected network appliances and web servers hosting several of its web applications, one of which, the Complaint Management System (CMS), drew particular attention.FortiMaila Fortinet FortiMail appliance that had served as Balochistan Police’s primary inbound email gateway.
Tools
Countries
ChinaSentinelLABS tracked China- and India-nexus intrusions against Pakistani law enforcement from February 2024 to April 2026, with Balochistan Police emerging as the main target and the CMS portal being turned into anIndiaSentinelLABS tracked China- and India-nexus intrusions against Pakistani law enforcement from February 2024 to April 2026, with Balochistan Police emerging as the main target and the CMS portal being turned into anPakistanactors converged on Balochistan Police over this period, bringing both a partner and an adversary of Pakistan to the same police force in a province shaped by a separatist insurgency and the regional tensions it
Industries
GovernmentWhat draws them is a particular kind of institution: one that holds the government’s internal security picture, what it knows about the threats inside its borders, and how it acts against them.Law enforcementSentinelLABS tracked China- and India-nexus intrusions against Pakistani law enforcement from February 2024 to April 2026, with Balochistan Police emerging as the main target and the CMS portal being turned into an