
DNS Analysis Maps Infrastructure Used in MSHTA-Delivered CountLoader Campaigns
Summary
A DNS investigation of MSHTA-related IoCs linked infrastructure to CountLoader campaigns deploying LummaStealer and Amatera. It identified typosquatting clusters, historical resolutions and additional domains, while describing some victim connections as potential.
Key points
- Bitdefender described attackers abusing Microsoft’s legacy MSHTA tool to deliver CountLoader, which deployed LummaStealer and Amatera.
- The investigation analyzed 120 network IoCs: 81 domains, 11 subdomains and 28 IP addresses.
- Network traffic showed 17 client IP addresses communicating with 28 domain IoCs through 2,652 DNS queries between March 22 and May 20, 2026.
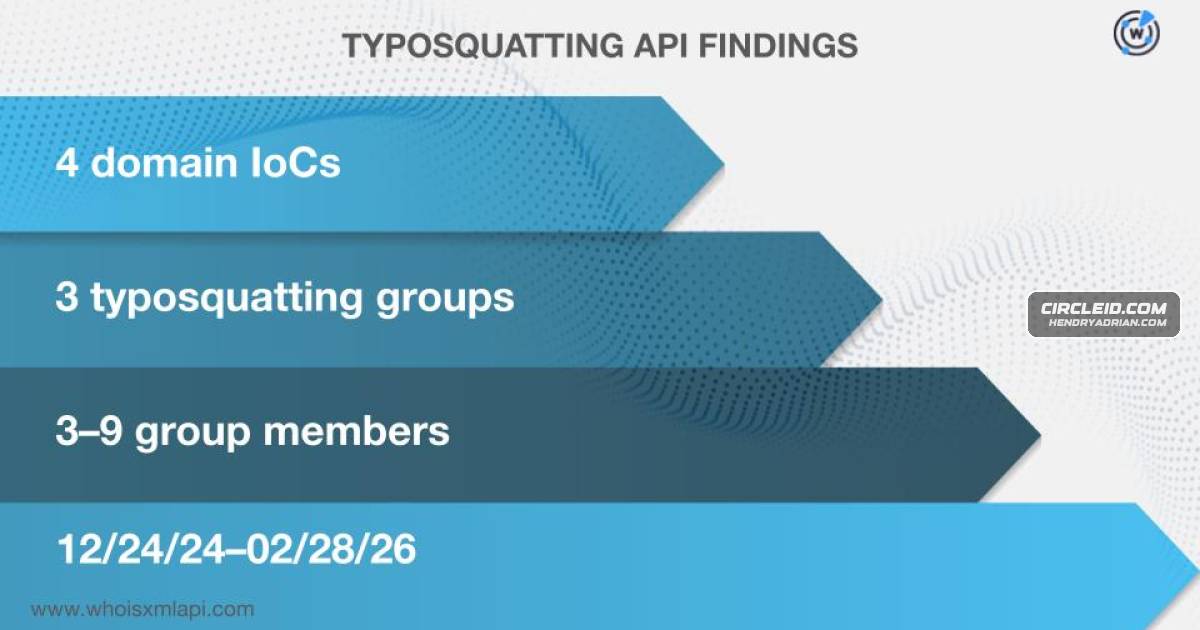
- Four domain IoCs appeared in three typosquatting groups; 20 domains were assessed as likely registered with malicious intent.
- Researchers found 618 IP addresses that could belong to victims communicating with 25 IP IoCs; the article does not establish that these systems were compromised.
- Of 2,260 email-connected domains identified, 56 were reported as already confirmed malicious by a threat-intelligence query. The article cautions that some threat classifications may require further investigation.
Article Details
- Attack Vectors
- Attackers abused Microsoft’s legacy MSHTA tool to deliver the HTA-based loader CountLoader.
- CountLoader was used to deploy LummaStealer and Amatera onto victims’ systems.
- The research linked the ClickFix attack to domain, subdomain, and IP infrastructure, including typosquatting domains.
- Defensive Notes
- The article recommends supplementary investigation to corroborate entities identified as threats, since their status may change or later prove harmless.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | health-smooth-eu3[.]com | Listed as a domain IoC and among examples likely registered with malicious intent. |
| DOMAIN | holiday-updateservice[.]com | Listed as a domain IoC and among examples likely registered with malicious intent. |
| DOMAIN | ms-team-ping6[.]com | Listed as a domain IoC and among examples likely registered with malicious intent; it also appeared in historical domain-to-IP resolutions. |
| DOMAIN | propofgustestyle[.]info | Listed as a domain IoC and among examples likely registered with malicious intent. |
| DOMAIN | qlkwr[.]com | Listed as a domain IoC and among examples likely registered with malicious intent. |
| DOMAIN | simplerwebs[.]space | Domain IoC included in a typosquatting group with similarly named domains. |
| DOMAIN | simplerwebs[.]world | Domain IoC included in a typosquatting group with similarly named domains. |
| HOSTNAME | asd[.]s7610rir[.]pw | Subdomain IoC; the article says the random-string .pw domains fit a malware-distribution or phishing pattern. |
| HOSTNAME | asq[.]d6shiiwz[.]pw | Subdomain IoC; the article says the random-string .pw domains fit a malware-distribution or phishing pattern. |
| HOSTNAME | check[.]qlkwr[.]com | Subdomain IoC that shares an IP address with d1[.]pool4883[.]pw. |
| HOSTNAME | d1[.]pool4883[.]pw | Subdomain IoC that shares an IP address with check[.]qlkwr[.]com; the article notes the shared resolution could indicate proxy or C&C infrastructure. |
| HOSTNAME | us1[.]pool4883[.]pw | Listed as a subdomain IoC associated with the attack infrastructure. |
| IPV4 | 103[.]115[.]17[.]90 | Listed as an IP IoC; the article reports historical IP-to-domain resolutions for it. |
| IPV4 | 107[.]175[.]187[.]11 | Listed as an IP IoC with historical IP-to-domain resolutions. |
| IPV4 | 87[.]96[.]21[.]84 | Listed as an IP IoC; the article reports historical IP-to-domain resolutions for it. |
MITRE ATT&CK
T1036 · MasqueradingThe article describes typosquatting domains and domains crafted to resemble legitimate names.T1105 · Ingress Tool TransferCountLoader deployed LummaStealer and Amatera onto victims’ systems.T1218.005 · MshtaAttackers abused the legacy MSHTA tool as a delivery mechanism for CountLoader.T1583.001 · DomainsThe investigation identified domains likely registered with malicious intent to support the attack infrastructure.
Malware
Amatera StealerBitdefender detailed how attackers abused Microsoft’s legacy MSHTA tool to deliver CountLoader, which deployed LummaStealer and Amatera in multiple campaigns.CountLoaderBitdefender detailed how attackers abused Microsoft’s legacy MSHTA tool to deliver CountLoader, which deployed LummaStealer and Amatera in multiple campaigns.LummaStealerBitdefender detailed how attackers abused Microsoft’s legacy MSHTA tool to deliver CountLoader, which deployed LummaStealer and Amatera in multiple campaigns.