
Malicious @injectivelabs/sdk-ts Release Stole Wallet Seed Phrases and Private Keys
Summary
Version 1.20.21 of the Injective TypeScript SDK contained code that exfiltrated wallet seed phrases and some private keys through an HTTP header. It was available for about 49 minutes before being removed and replaced with version 1.20.23.
Key points
- The compromised npm release was @injectivelabs/sdk-ts version 1.20.21, published on July 8, 2026.
- Malicious code hooked the SDK’s mnemonic and private-key loading functions, capturing full seed phrases and private keys passed as strings.
- The code base64-encoded captured data and sent it in the X-Request-Id header to testnet.archival.chain.grpc-web.injective[.]network.
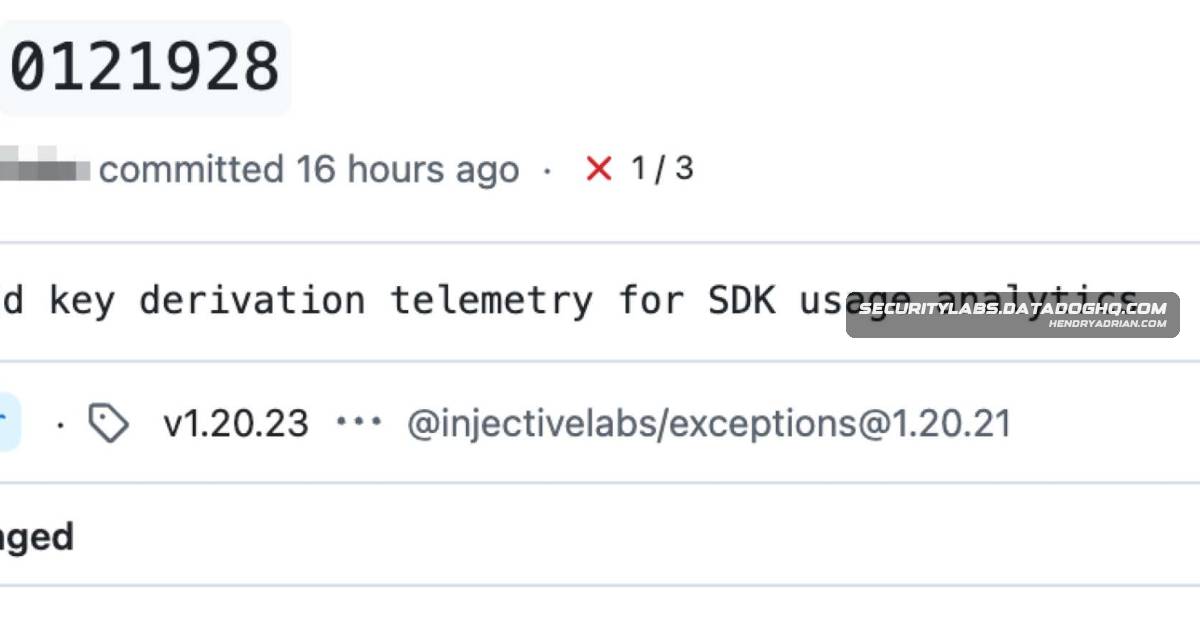
- The malicious changes were introduced through GitHub commits that researchers assessed were made by an attacker, based partly on unusual commit behavior and timezone metadata.
- Version 1.20.21 was available for about 49 minutes; the code was reverted and malware-free version 1.20.23 was published.
- Organizations can check whether version 1.20.21 was installed and hunt network and DNS logs for the exfiltration domain.
- The article reports that the exfiltration endpoint still appeared to accept requests when tested.
Article Details
- Attack Vectors
- A malicious commit introduced obfuscated code into @injectivelabs/sdk-ts version 1.20.21, published through npm.
- Hooks in PrivateKey.fromMnemonic() and PrivateKey.fromHex() captured mnemonic phrases and, when provided as a string, private keys during wallet loading.
- Captured data was base64-encoded and sent to a remote endpoint in the X-Request-Id HTTP header.
- Defensive Notes
- Use the Library Inventory query library_name:(@injectivelabs/sdk-ts) library_version:(1.20.21) to identify systems where the compromised version was installed.
- Hunt in logs for DNS queries, network destinations, or HTTP URLs involving testnet.archival.chain.grpc-web.injective.network.
- Version 1.20.23 was reported as malware-free; the malicious changes were reverted.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | testnet[.]archival[.]chain[.]grpc-web[.]injective[.]network | Article-identified attacker-used exfiltration domain for captured secrets. |
| URL | hxxps[:]//testnet[.]archival[.]chain[.]grpc-web[.]injective[.]network | Article-identified exfiltration endpoint receiving captured secrets in the X-Request-Id header. |