
SourTrade Malvertising Builds Session-Specific Windows Executables in Browsers
Summary
Confiant says SourTrade uses cloaked ads and browser workers to assemble session-specific Windows executables from a Bun runtime and attacker-controlled material. The final files’ payload capabilities are not established.
Key points
- Confiant says SourTrade has operated since late 2024, impersonating TradingView, Solana, and Luno to target traders and crypto investors in 12 countries.
- Landing pages fingerprint visitors and show suspected researchers and bots an empty page while presenting selected targets with imitations of the impersonated services.
- A page-scoped ServiceWorker and an embedded SharedWorker request configuration containing a template, session-specific values, and a secondary runtime URL.
- The browser retrieves a clean Bun runtime from purelogicbox[.]org in a published sample, then combines it with attacker-controlled executable material and pseudorandom bytes to build a Windows executable.
- Changing session-specific seeds and sizes produces different file hashes, reducing the usefulness of simple hash-based detection; the article notes that executable structures and bytecode still cross the network.
- The documented chain does not use a browser vulnerability or remove Mark of the Web. Confiant did not establish whether the download starts automatically or requires a click.
- Confiant did not demonstrate that the analyzed samples carry JSCEAL or WeevilProxy, and the article says their payload capabilities cannot be assigned to the current files.
Article Details
- Attack Vectors
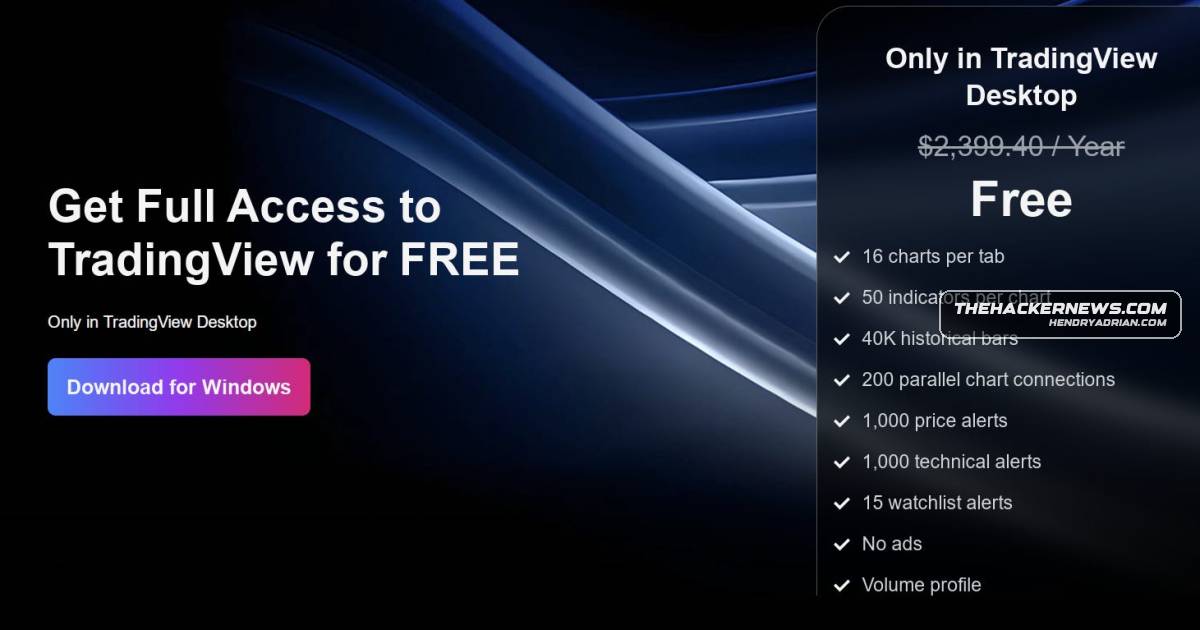
- Malvertising directs selected targets to cloaked landing pages impersonating TradingView, Solana, and Luno.
- The landing page uses fingerprinting to show suspected researchers and bots an empty page while presenting selected visitors with the impersonated service.
- Page scripts use a ServiceWorker and an embedded SharedWorker to retrieve configuration and assemble a Windows executable in the browser from a clean Bun runtime and attacker-controlled material.
- Defensive Notes
- Install trading and wallet software only from the vendor’s own site, not from an advertisement.
- Examine the complete chain, including the ad referral, cloaked landing page, /config request, secondary-domain runtime fetch, and ServiceWorker download; do not treat one network or file artifact as decisive.
- Per-session builds reduce the value of simple hash-based detection, but the attacker-controlled PE material and bytecode still cross the network.
- The article reports no software patch to apply and does not establish that the file downloads automatically or executes in the browser.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | purelogicbox[.]org | Secondary domain used in the published SourTrade sample response to deliver the Bun runtime. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe configuration supplies Base64-encoded PE structures and bytecode, and per-session values alter the assembled file.T1036 · MasqueradingLanding pages impersonate TradingView, Solana, and Luno to appear convincing to selected targets.T1059.007 · JavaScriptEmbedded page JavaScript and worker code assemble the executable in the browser.
People
Products
BunSourTrade is a malvertising campaign that uses cloaked landing pages and per-session file assembly to make victims’ browsers build a Windows executable from components delivered through a legitimate Bun runtime.LunoConfiant says the operation has targeted TradingView, Solana, and Luno users since late 2024 across 12 countries, with the final file varying by session to evade hash-based detection.SolanaConfiant says the operation has targeted TradingView, Solana, and Luno users since late 2024 across 12 countries, with the final file varying by session to evade hash-based detection.TradingViewConfiant says the operation has targeted TradingView, Solana, and Luno users since late 2024 across 12 countries, with the final file varying by session to evade hash-based detection.