
Hunt.io Reports Unattended Hermes AI Agent Used in Thai Finance Ministry Intrusion
Summary
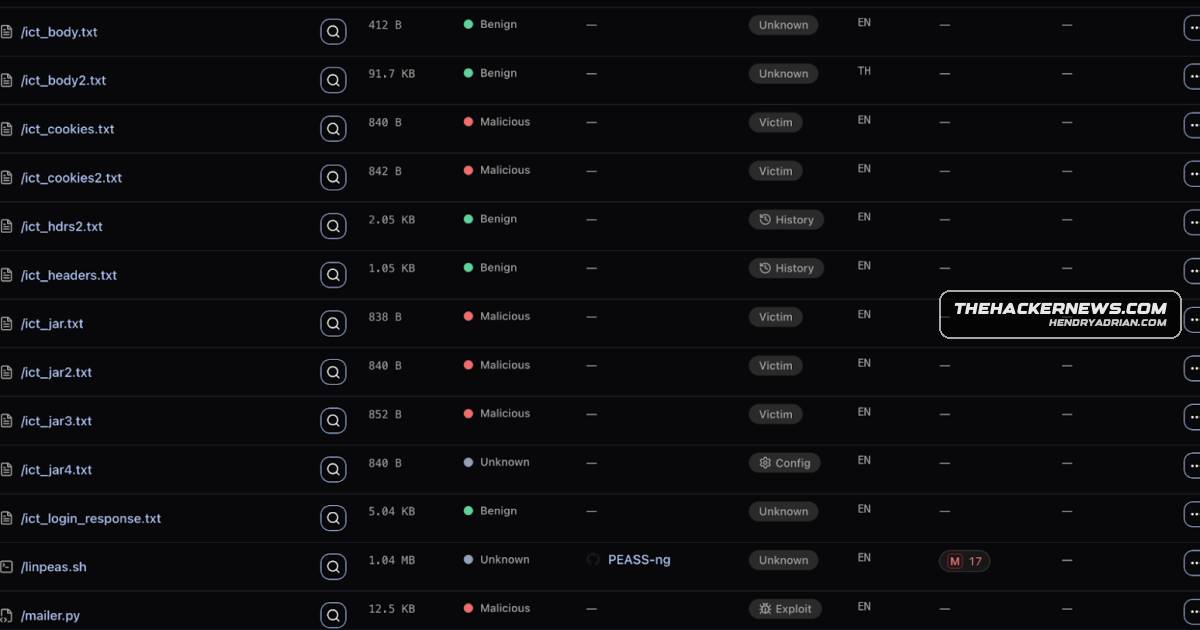
Hunt.io and Bob Diachenko report that an operator already inside Thailand’s Finance Ministry network used Hermes in YOLO mode for scans and file crawls. Exposed logs revealed attack tooling, but no evidence showed data leaving the network.
Key points
- Hunt.io and Bob Diachenko found agent logs and 585 files containing 470 MB of attack tooling on an exposed web server; they are the only public source cited for the ministry-specific findings.
- Logs show Hermes running host scans, LinPEAS checks, elevated-permission searches, and a recursive crawl of a personnel-record directory dating to 2012.
- The directory contained office documents, performance evaluations, and personnel records; the logs do not show those files leaving the network.
- Recovered scripts targeted HiveServer2, whose default NONE authentication accepts any password, and used HiveCmd.jar to run operating-system commands through database queries.
- Artifacts included a hidden web shell, custom scripts, and a Go implant called Hades; no recovered evidence shows Hades reached a ministry machine.
- The operator’s initial access method is unknown. The recovered material does not establish that any of four scanned 2026 kernel flaws ran or that data was exfiltrated.
- The article recommends checking HiveServer2 authentication, restricting user-defined function installation, and monitoring web-server connections to internal Hadoop ports.
Article Details
- Attack Vectors
- The operator had already accessed the ministry network before starting Hermes; the initial access method is unknown.
- A hidden web shell was found on a ministry web server.
- A custom script connected to the internal HiveServer2 service, which was configured to accept any password by default, and installed HiveCmd.jar as a user-defined function to run operating-system commands.
- The operator tested default credentials against an internal GlassFish console, but successful deployment was not confirmed.
- Hermes was run in YOLO mode to conduct host checks, privilege-escalation checks, filesystem searches, and a recursive web-root crawl without approval for each command.
- A customized LinPEAS script checked for four Linux kernel vulnerabilities, but the article says there is no evidence that the flaws ran or affected a ministry kernel.
- Defensive Notes
- Check whether HiveServer2 authentication is set to NONE and restrict who can install user-defined functions.
- Alert when a web server process connects to internal Hadoop ports such as 10000 or 50070.
- Search web roots recursively for hidden PHP files with leading-dot names that imitate system caches.
- Patch against CVE-2026-31431, CVE-2026-43284, CVE-2026-43500, and CVE-2026-43503; update sudo to 1.9.5p2 or later, patch polkit for CVE-2021-4034, and address any remaining IIS 6.0 WebDAV exposure.
- Treat Hermes YOLO mode as unsafe outside trusted, sandboxed environments; it disables human approval for commands, although a separate blocklist remains.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 103[.]97[.]0[.]57 | IP address from which the operator's SSH session to the staging server originated, according to the article. |
MITRE ATT&CK
T1046 · Network Service DiscoveryThe operator used host scanning, including a kernel vulnerability scan against a ministry host.T1059.004 · Unix ShellHiveCmd.jar was installed as a Hive user-defined function to run operating-system commands through database queries.T1083 · File and Directory DiscoveryHermes listed the filesystem and recursively crawled the Office of the Permanent Secretary web root, including personnel records.T1210 · Exploitation of Remote ServicesA custom script connected to internal HiveServer2, whose default NONE authentication accepts any password, and installed a function capable of running commands as the Hive service account.T1505.003 · Web ShellA hidden web shell was found on a ministry web server.T1552.001 · Credentials In FilesA mail-testing script contained hardcoded stolen mailbox passwords.
CVE
CVE-2021-4034Patch kernels against all four 2026 flaws above, plus sudo to 1.9.5p2 or later, polkit for CVE-2021-4034, and any remaining IIS 6.0 WebDAV.CVE-2026-31431A customized linpeas.sh checked for four 2026 Linux kernel flaws across three families: Copy Fail (CVE-2026-31431), Dirty Frag (CVE-2026-43284 and CVE-2026-43500), and DirtyClone (CVE-2026-43503).CVE-2026-43284A customized linpeas.sh checked for four 2026 Linux kernel flaws across three families: Copy Fail (CVE-2026-31431), Dirty Frag (CVE-2026-43284 and CVE-2026-43500), and DirtyClone (CVE-2026-43503).CVE-2026-43500A customized linpeas.sh checked for four 2026 Linux kernel flaws across three families: Copy Fail (CVE-2026-31431), Dirty Frag (CVE-2026-43284 and CVE-2026-43500), and DirtyClone (CVE-2026-43503).CVE-2026-43503A customized linpeas.sh checked for four 2026 Linux kernel flaws across three families: Copy Fail (CVE-2026-31431), Dirty Frag (CVE-2026-43284 and CVE-2026-43500), and DirtyClone (CVE-2026-43503).
People
Malware
Vendors
Products
Apache HadoopRecovered artifacts included a hidden web shell, custom Hadoop scripts, and Hades implants.GlassFishSeparate scripts tested default credentials against an internal GlassFish console, with neither deployment confirmed, alongside exploit code for three older flaws in polkit, sudo, and IIS 6.0.HermesAn operator used the Hermes AI assistant in YOLO mode to autonomously probe Thailand’s Ministry of Finance network, including host scans, privilege-escalation checks, and directory crawls of internal personnel records.HiveServer2The operation relied on default HiveServer2 authentication and other known weaknesses.
Tools
hive_rce_py2.pyA script called hive_rce_py2.py connects to HiveServer2, the SQL front end to that cluster, on an internal machine at port 10000, and sends a password.HiveCmd.jar#Hermes #Huntio #BobDiachenko #ThailandMinistryofFinance #Hades #HiveCmd.jarLinPEASLinPEAS, a standard script that hunts for privilege escalation paths on Linux.VShellThe same server previously hosted a ShadowPad controller and now runs a VShell command-and-control listener.
Countries
Hong KongThe operator’s own SSH session into the staging server came from 103.97.0[.]57 in Hong Kong.ThailandAn operator used the Hermes AI assistant in YOLO mode to autonomously probe Thailand’s Ministry of Finance network, including host scans, privilege-escalation checks, and directory crawls of internal personnel records.