
Unit 42 Details Zimbra Zero-Click Espionage Campaign Linked to Russian Actors
Summary
Unit 42 reports that CL-STA-1114 uses CVE-2025-66376 to target Zimbra webmail with HTML-delivered JavaScript that exfiltrates credentials, 2FA scratch codes, session data and email history.
Key points
- Unit 42 tracks the activity as CL-STA-1114 and links it to overlapping activity attributed by other vendors to Void Blizzard and LAUNDRY BEAR.
- The campaign targeted Zimbra webmail at government, defense, transportation and financial organizations across NATO member states, Ukraine, CIS countries and Africa.
- The campaign targeting Zimbra began in July 2025; Unit 42 says the activity cluster has been active since at least 2024.
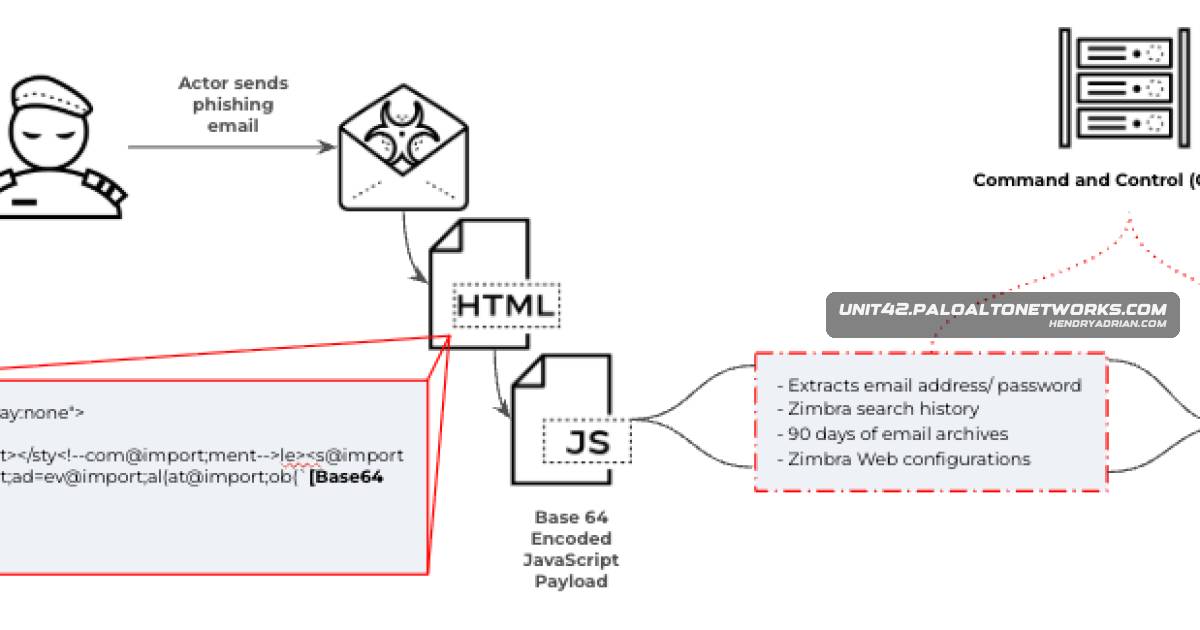
- HTML attachments or embedded HTML use obfuscated Base64-encoded scripts that decode into JavaScript and inject into the victim’s browser without requiring interaction, according to the report.
- The payload exfiltrates CSRF tokens, email credentials, 2FA scratch codes, system details, and the victim’s last 90 days of email and search history.
- Unit 42 observed at least nine C2 IP addresses and nine domains, with servers active for an average of 35.4 days; it says attackers continue targeting unpatched Zimbra Collaboration Suite instances using CVE-2025-66376.
- The report recommends patching vulnerable systems and using the listed indicators to investigate and strengthen defenses.
Article Details
- Attack Vectors
- Phishing emails with HTML attachments or embedded HTML deliver an obfuscated, Base64-encoded script.
- The emails exploit CVE-2025-66376 in Zimbra Collaboration Suite to inject JavaScript into a victim’s browser without recipient interaction.
- The JavaScript exfiltrates Zimbra credentials, 2FA scratch codes, CSRF tokens, system details, and the victim’s last 90 days of email and search history to a hard-coded C2 server.
- Defensive Notes
- Patch vulnerable Zimbra Collaboration Suite instances.
- Use the listed C2 IP addresses and domains to investigate and strengthen defenses against CL-STA-1114 activity.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | analyticemailmeter[.]com | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | emailanalytics[.]com[.]ua | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | istc-cloud[.]com | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | mailnalysis[.]com | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | synacorzimbra[.]nl | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | zimbra-metadata[.]com | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | zimbrasoft[.]com[.]ua | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | zimbrastat[.]com | C2 domain used in CL-STA-1114 activity. |
| DOMAIN | zmailanalytics[.]com | C2 domain used in CL-STA-1114 activity. |
| IPV4 | 104[.]248[.]134[.]194 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 185[.]86[.]79[.]95 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 193[.]238[.]152[.]66 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 194[.]156[.]103[.]193 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 216[.]252[.]238[.]104 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 216[.]252[.]238[.]18 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 216[.]252[.]238[.]64 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 37[.]120[.]247[.]228 | C2 infrastructure used in CL-STA-1114 activity. |
| IPV4 | 64[.]226[.]124[.]190 | C2 infrastructure used in CL-STA-1114 activity. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe phishing HTML uses an obfuscated section and Base64-encoded script to conceal malicious content.T1041 · Exfiltration Over C2 ChannelThe injected JavaScript sends stolen Zimbra data to a hard-coded C2 server.T1059.007 · JavaScriptThe decoded Base64 script executes as a JavaScript payload in the victim’s browser.T1190 · Exploit Public-Facing ApplicationThe campaign exploits CVE-2025-66376 in Zimbra Collaboration Suite to inject code through the webmail platform.T1566.001 · Spearphishing AttachmentPhishing emails delivered HTML attachments used to initiate the attack.
CVE
Threat Actors
CL-STA-1114Unit 42 tracks this activity cluster, which it reports has targeted Zimbra webmail users since July 2025.Laundry BearUnit 42 links CL-STA-1114 to overlapping activity from LAUNDRY BEAR; the article describes the campaign as linked, not as definitively attributed to this actor.TA488Unit 42 links CL-STA-1114 to overlapping activity from Void Blizzard; the article describes the campaign as linked, not as definitively attributed to this actor.
Products
Zimbracyberespionage campaign linked to the Russian threat actors Void Blizzard and LAUNDRY BEAR that targets Zimbra webmail in government, defense, transportation, and financial organizations across multiple regions.Zimbra Collaboration SuiteThe attackers used zero-click phishing emails exploiting CVE-2025-66376 in Zimbra Collaboration Suite to inject JavaScript that steals credentials, 2FA scratch codes, session data, and email/search history from
Industries
Defenseto the Russian threat actors Void Blizzard and LAUNDRY BEAR that targets Zimbra webmail in government, defense, transportation, and financial organizations across multiple regions.Governmentlinked to the Russian threat actors Void Blizzard and LAUNDRY BEAR that targets Zimbra webmail in government, defense, transportation, and financial organizations across multiple regions.Transportationthreat actors Void Blizzard and LAUNDRY BEAR that targets Zimbra webmail in government, defense, transportation, and financial organizations across multiple regions.