cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2384 articles

Threat Research · bleepingcomputer.com

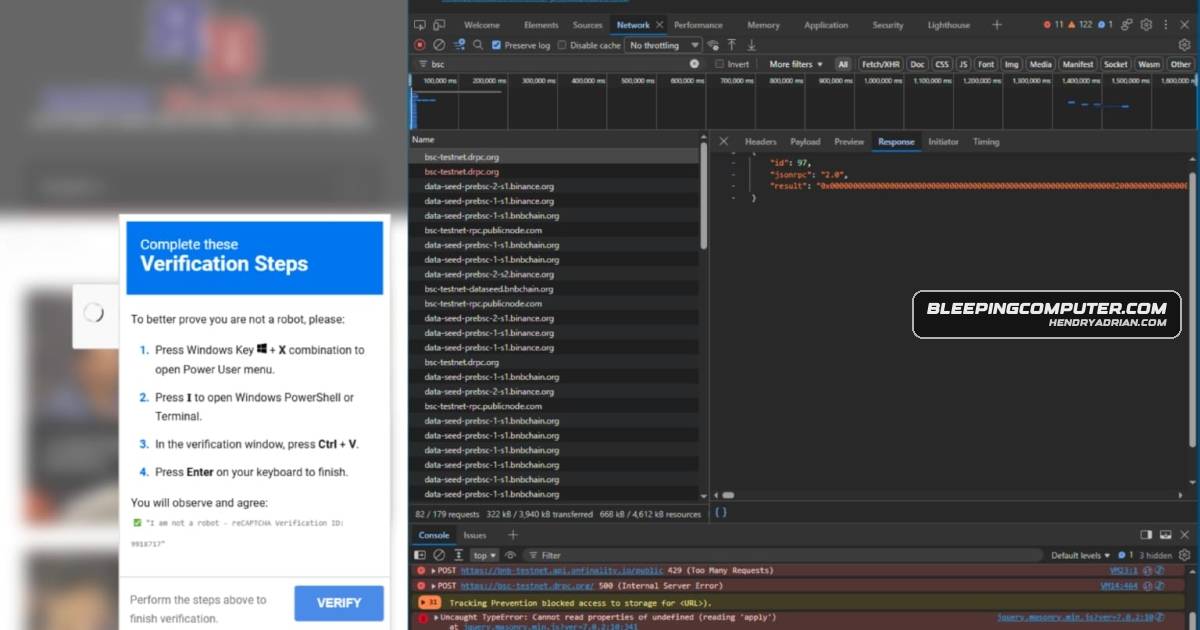
5,400+ Compromised Websites Deliver ClickFix Payloads Stored on BNB Smart Chain

Researchers identified more than 5,400 compromised WordPress and PrestaShop sites serving ClickFix lures with payloads stored in BNB Smart Chain smart contracts. A newer variant uses a WebRTC stager to receive and execute code.

Sep 5, 2026
Threat Research · thehackernews.com

Attackers Exploit PaperCut Flaws to Steal Credentials at Education Organizations

Arctic Wolf reports attackers exploiting PaperCut flaws CVE-2026-81578 and CVE-2026-82078 at U.S. and European education organizations to steal credentials, create privileged accounts, and deliver Meterpreter payloads.

Sep 5, 2026
Threat Research · censys.com

Censys Tracks NPS Proxy Use and Its Role in Intrusions

Censys finds about 17,500 NPS servers, mostly in China and Hong Kong. The dual-use tunneling tool has also been deployed alongside other remote access tools in intrusions, so NPS alone is not conclusive evidence of compromise.

Sep 4, 2026
Threat Research · rapid7.com

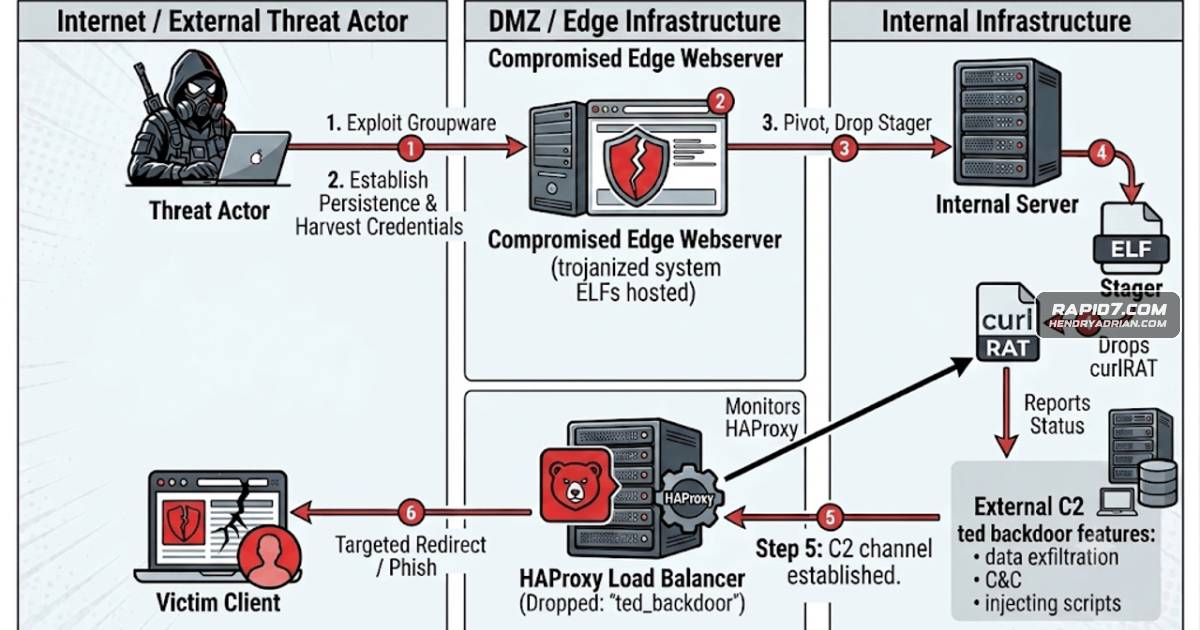
DPRK-Linked Toolkit Uses HAProxy Backdoor and CurlRAT to Target South Korean Organizations

Rapid7 details a Linux espionage toolkit targeting South Korean media and automotive organizations. Its HAProxy backdoor and CurlRAT components enable command execution, credential and session theft, traffic manipulation, and persistence; DPRK attribution is assessed at

Sep 4, 2026
Threat Research · securelist.com

Toy Ghouls Deploy Custom Backdoors Using HiveMQ and Element for C2

Kaspersky details two custom Toy Ghouls backdoors targeting Russian organizations. Delivered via WinRM, they establish persistence on Windows and use HiveMQ or Element for command-and-control.

Sep 4, 2026
Threat Research · thehackernews.com

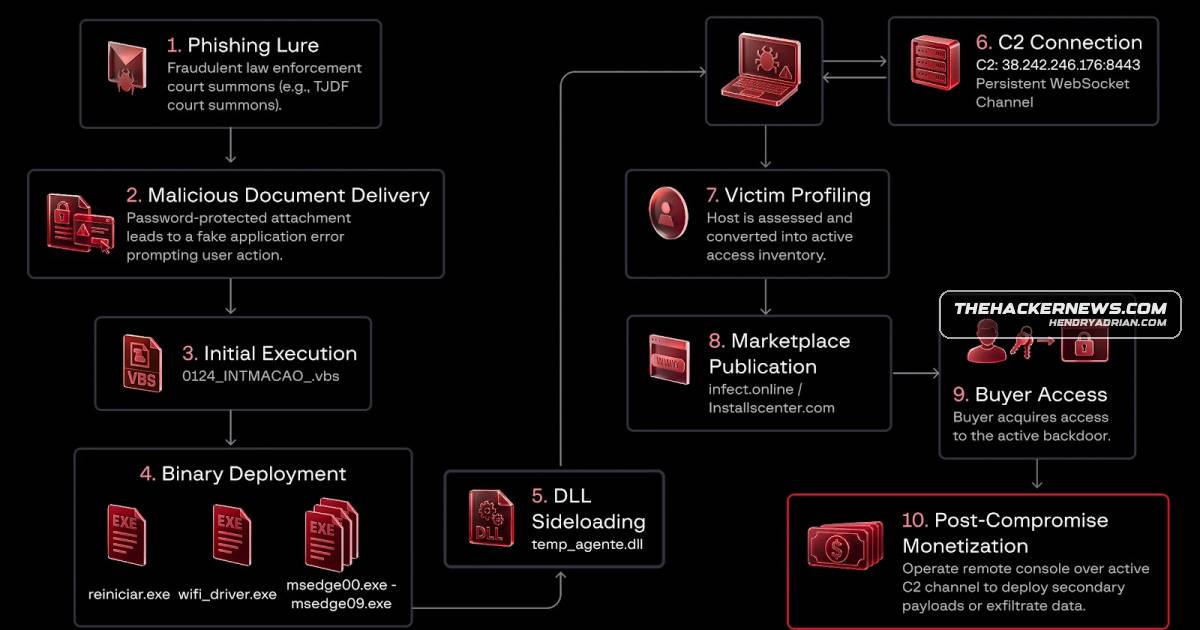
BraZetsu Malware Turns Compromised Windows Hosts Into Marketplace Inventory

Group-IB describes BraZetsu, a Python-based Windows framework that helps Exilware sell access to compromised hosts. It gathers system, browser, and financial data to prioritize targets; delivery remains unclear.

Sep 4, 2026
Threat Research · netskope.com

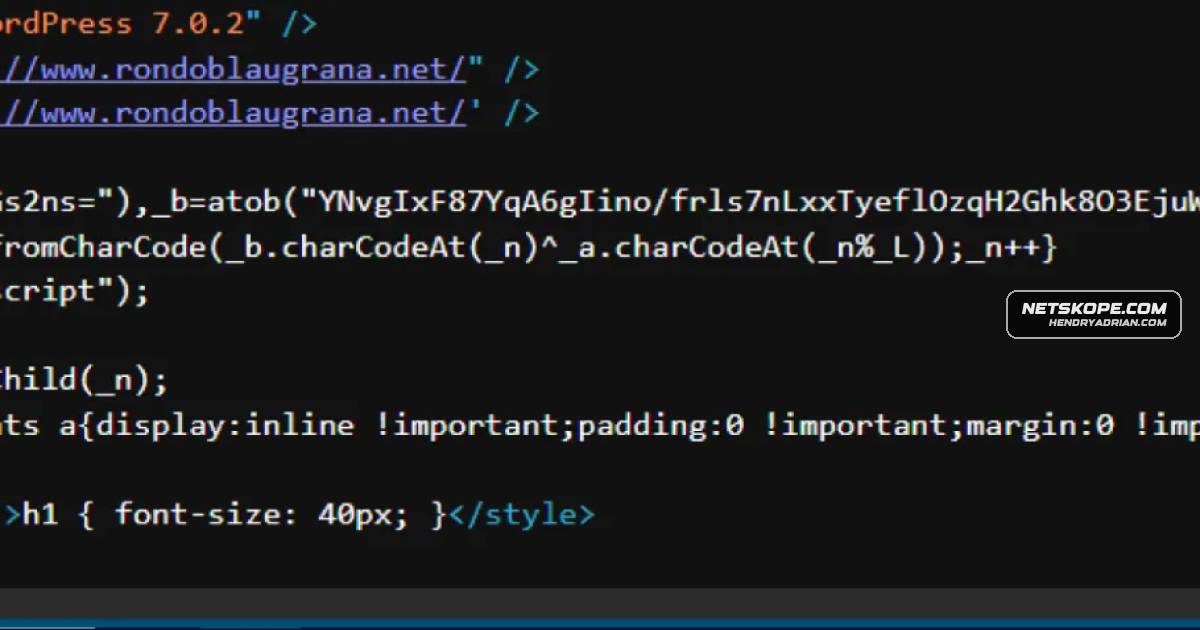
EtherHiding Campaign Uses BNB Smart Chain and Covert WebRTC Channels

Netskope reports more than 5,400 compromised sites using BNB Smart Chain testnet contracts to deliver ClickFix lures or a covert WebRTC command channel; the initial compromise method is unknown.

Sep 3, 2026
Threat Research · arcticwolf.com

Arctic Wolf Details PREY-0058 Vishing Campaign Targeting Microsoft 365 and SaaS Data

Arctic Wolf describes PREY-0058, a vishing and AiTM campaign that bypasses MFA to access Microsoft 365 and SaaS data, then extorts victims without encrypting files. It details the intrusion sequence and defensive measures.

Sep 3, 2026
Threat Research · netspi.com

NetSPI Details Azure Privilege-Escalation Risks and a Fixed Built-In Role

NetSPI explains how Azure RBAC permissions and ABAC conditions can create privilege-escalation paths, and reports that Microsoft removed role-assignment permissions from the Anyscale Platform Administrator built-in role.

Sep 3, 2026
Threat Research · feeds.fortinet.com

Attackers Hijack AWS Bedrock Access Using Stolen IAM Credentials

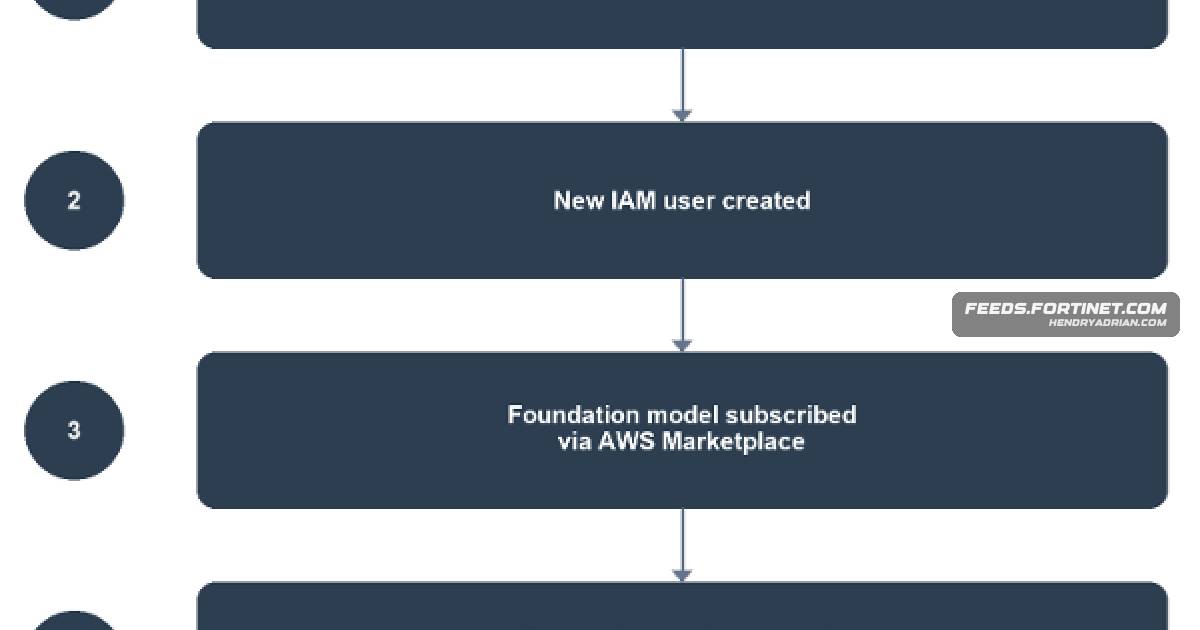
Fortinet reports an AWS compromise in which a leaked, long-lived administrator IAM key was used to create an identity, subscribe to foundation models through Marketplace, and invoke them, charging inference costs to the victim. The article outlines logging and identity-

Sep 3, 2026
Threat Research · unit42.paloaltonetworks.com

AI-Assisted Campaigns Target Transportation and Financial Organizations in Latin America

Unit 42 analyzed two campaigns targeting organizations in Mexico, Ecuador and Brazil, finding phishing, custom tools and evidence of LLM use. Exposed staging infrastructure revealed scripts and operational details.

Sep 3, 2026
Threat Research · reliaquest.com

Empty SMTP Sender Can Bypass Microsoft 365 RejectDirectSend Control

ReliaQuest found that an unauthenticated email with an empty SMTP envelope sender can bypass Microsoft 365’s RejectDirectSend control while displaying an internal-looking From address. IP-restricted inbound connectors blocked the attempts in testing.

Sep 3, 2026
Threat Research · aikido.dev

MECCHA CHAMELEON Maps Enabled a Delayed RCE Through Arbitrary File Writes

Researchers demonstrated that a crafted MECCHA CHAMELEON map could exploit an exposed recording function to write a payload to the Windows Startup folder, enabling delayed RCE. The game fixed the issue in version 4.0.0.

Sep 3, 2026
Threat Research · jamf.com

Trojanized macOS Installers Deliver OtterCookie Malware in Contagious Interview Campaign

Jamf analyzed 14 unsigned macOS installers linked to Contagious Interview. The installers fetch staged scripts and OtterCookie, which can enable remote access, steal credentials, scan files, and capture clipboard contents.

Sep 3, 2026
Threat Research · iru.com

Rust Supply-Chain Attack Delivers macOS Rustbot RAT to Steal Credentials

Malicious Rust crates available for about two hours delivered Rustbot when affected projects were compiled. The macOS RAT collects credentials and other data, installs persistence, and communicates with attacker-controlled C2 servers.

Sep 3, 2026
Threat Research · hunt.io

Chinese-Speaking Operator Used AI Agents to Target Government and Education Systems Across Asia

Hunt.io links five exposed workspaces to a Chinese-speaking operator using AI agents and conventional exploits. The campaign compromised government and education systems, stealing credentials and records and deploying webshells and SecBox implants.

Sep 3, 2026
Threat Research · security.com

Attackers Revive Node.js Abuse to Run Malware and Maintain Persistence

Symantec reports that multiple threat actors have used the legitimate Node.js runtime in attacks since February 2026, including intrusions involving PowerShell, ransomware-linked malware and an implant that contacted Ethereum gateways.

Sep 3, 2026
Threat Research · netskope.com

Python NodeStealer Adds Spyware Features and Expands Facebook Data Theft

Netskope found a Python NodeStealer variant with keylogging, clipboard and screenshot capture, expanded Facebook Graph API collection, and separate Telegram bots for stolen browser credentials and Facebook data. AI assistance is suspected, not confirmed.

Sep 2, 2026
Threat Research · blog.barracuda.com

Kali365 Phishing Kit Abuses Microsoft 365 Authentication to Hijack Sessions

Barracuda researchers describe how the Kali365 phishing kit uses device-code authentication and adversary-in-the-middle attacks to obtain Microsoft 365 sessions or tokens, even when victims complete genuine sign-in and MFA.

Sep 2, 2026
Threat Research · asec.ahnlab.com

LegionLoader Campaign Uses Fake Cloudflare CAPTCHA Pages to Deliver PowerShell Commands

ASEC describes LegionLoader campaigns using malicious links and spear-phishing emails to direct users to fake Cloudflare CAPTCHA pages, where copied PowerShell commands download and execute the malware.

Sep 2, 2026
Threat Research · asec.ahnlab.com

Analysis Details How Syslogk Rootkit Hides Processes, Network Connections, Files, and Its Kernel Module

AhnLab analyzes how the Syslogk Linux rootkit uses kernel hooks to hide processes, TCP sockets, files, and its module, and reports that V3 Net for Linux Server detected and remediated it.

Sep 2, 2026
Threat Research · asec.ahnlab.com

Attackers Use Radmin and UltraVNC to Control Korean Systems and Turn Them Into Proxy and VPN Servers

AhnLab describes attacks on Korean users that install Radmin and UltraVNC for remote control, then add proxy tools or SoftEther VPN to repurpose infected systems. The initial intrusion method and attacker identity remain unknown.

Sep 2, 2026
Threat Research · research.checkpoint.com

Gambling Goblin Uses Compromised Brazilian Government Sites for SEO Phishing Campaign

Check Point Research details a campaign linked to Chinese-speaking actor Gambling Goblin that abuses compromised Brazilian sites to proxy phishing pages and manipulate search rankings, using Apache modules and a broad Linux malware toolkit.

Sep 2, 2026
Threat Research · crowdstrike.com

CrowdStrike-Led Operation Disrupts Sality P2P Botnet After Two Decades

CrowdStrike and international partners disrupted the Sality P2P botnet, which had infected more than 15,000 machines. Peer-list manipulation and sinkholing cut off tasking; existing infections remain active and require remediation.

Sep 2, 2026
PreviousPage 27 of 100 Next
© 2026 cyber.hendryadrian.com