
5,400+ Compromised Websites Deliver ClickFix Payloads Stored on BNB Smart Chain
Summary
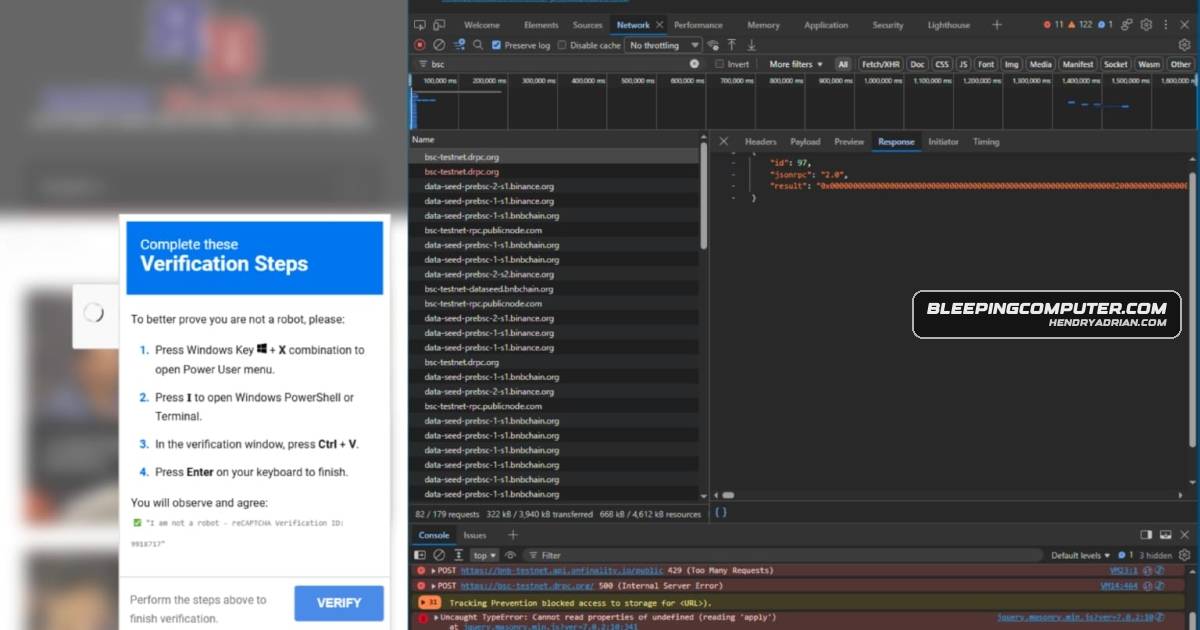
Researchers identified more than 5,400 compromised WordPress and PrestaShop sites serving ClickFix lures with payloads stored in BNB Smart Chain smart contracts. A newer variant uses a WebRTC stager to receive and execute code.
Key points
- Researchers identified more than 5,400 compromised websites, mostly built on WordPress and PrestaShop; how the sites were initially compromised remains unknown.
- Injected scripts retrieve next-stage payloads from BNB Smart Chain Testnet smart contracts using EtherHiding.
- A fake CAPTCHA instructs visitors to open the Windows Run dialog and paste a PowerShell command that downloads and executes the payload.
- A newer variant replaces the ClickFix payload with a WebRTC data-channel stager that receives JavaScript from a hardcoded C2 address.
- The stager buffers received code and executes it dynamically in browser memory rather than saving it to disk.
- Researchers observed more than 300 infected sites being used daily; nearly 400 contacted BSC Testnet RPC endpoints daily in August, with a peak of 536.
- Netskope recommends blocking the BSC Testnet RPC endpoint pool and monitoring for non-web UDP traffic associated with WebRTC.
Article Details
- Attack Vectors
- Attackers injected scripts into more than 5,400 compromised WordPress and PrestaShop websites; the initial compromise method is unknown.
- Injected scripts retrieved payloads from smart contracts on BNB Smart Chain Testnet using EtherHiding.
- Visitors were shown a fake CAPTCHA instructing them to paste a PowerShell command into the Windows Run dialog, which downloaded and executed a payload.
- A later variant used a WebRTC data-channel stager to receive JavaScript from a hardcoded C2 address and execute it dynamically in browser memory.
- Defensive Notes
- Researchers recommend blocking the pool of BSC Testnet RPC endpoints referenced in their guidance.
- Monitor for non-web UDP traffic associated with WebRTC.
MITRE ATT&CK
T1059.001 · PowerShellThe fake CAPTCHA instructs visitors to paste a PowerShell command into the Windows Run dialog.T1059.007 · JavaScriptThe WebRTC stager receives JavaScript code from a hardcoded C2 address and executes it dynamically in the browser.T1105 · Ingress Tool TransferThe ClickFix flow downloads the final payload after the visitor runs the supplied PowerShell command.T1189 · Drive-by CompromiseCompromised WordPress and PrestaShop websites deliver the campaign's lure and payload to visitors.T1584.004 · ServerThe operation uses compromised websites as infrastructure to deliver its payloads.
Products
BNB Smart ChainA large criminal campaign is using more than 5,400 compromised WordPress and PrestaShop websites to deliver ClickFix payloads stored in smart contracts on the BNB Smart Chain via EtherHiding.PrestaShopA large criminal campaign is using more than 5,400 compromised WordPress and PrestaShop websites to deliver ClickFix payloads stored in smart contracts on the BNB Smart Chain via EtherHiding.WordPressA large criminal campaign is using more than 5,400 compromised WordPress and PrestaShop websites to deliver ClickFix payloads stored in smart contracts on the BNB Smart Chain via EtherHiding.