DPRK-Linked Toolkit Uses HAProxy Backdoor and CurlRAT to Target South Korean Organizations
Summary
Rapid7 details a Linux espionage toolkit targeting South Korean media and automotive organizations. Its HAProxy backdoor and CurlRAT components enable command execution, credential and session theft, traffic manipulation, and persistence; DPRK attribution is assessed at
Key points
- Rapid7 found the toolkit targeting South Korean media and automotive sectors, likely for long-term espionage; attribution to DPRK-linked actors is assessed with medium confidence.
- The toolkit includes a custom HAProxy 2.8.12 backdoor, CurlRAT, a stager, an SSH keylogger, and trojanized system binaries such as crond, agetty, atd, and polkitd.
- The HAProxy implant intercepts HTTP traffic, captures selected requests and session cookies, and can inject malicious scripts into responses to targeted users.
- CurlRAT supports remote command execution, file transfers, reverse and interactive shells, system profiling, and C2 polling; the SSH keylogger captures plaintext passwords.
- The stager replaces legitimate system daemons, timestomps binaries, and selectively removes log entries to conceal installation.
- Rapid7 could not confirm the initial access method or establish a definitive campaign timeline; exploitation of exposed Groupware portals is a scenario, not a confirmed entry point.
- Rapid7 recommends stronger integrity checks and independent network correlation for edge systems handling user traffic, rather than relying solely on those systems’ logs.
Article Details
- Attack Vectors
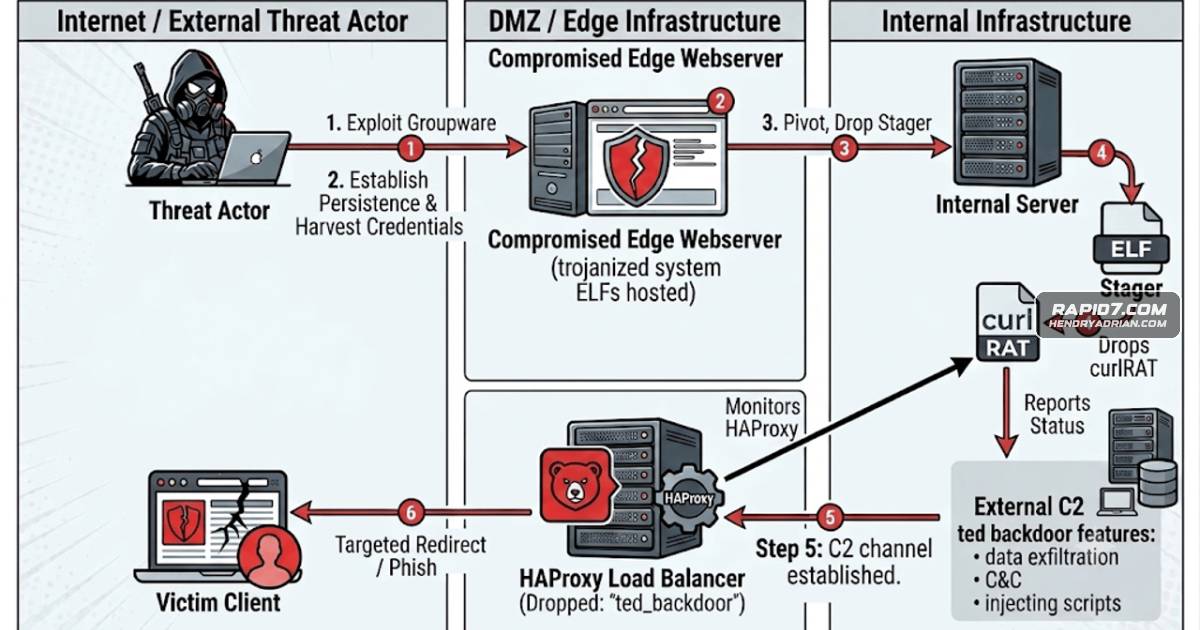
- Initial access is unconfirmed. The article presents exploitation of a vulnerability in an externally accessible Groupware login portal as an assumed scenario, and describes exposed mail-server services as another plausible surface.
- After obtaining an edge-host foothold, the attacker can use the host for credential harvesting and staging trojanized system binaries, then pivot inward and deploy a stager to internal servers.
- The stager deploys CurlRAT when it detects HAProxy or cron; ted backdoor is installed in the HAProxy load balancer.
- The compromised HAProxy can intercept selected HTTP traffic, capture session-related data, and inject or replace webpage content for selected clients.
- Defensive Notes
- Apply strict security standards to edge components that manage user traffic, SSL, or runtime modules, as well as to application servers.
- Do not rely solely on the edge component's own logs; use independent network correlation, memory behavioral analysis, and binary integrity checks.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | img[.]darklights[.]store | CurlRAT secondary C2/configuration host used after recorded network failures. |
| DOMAIN | img[.]monderhouse[.]space | CurlRAT C2 domain used as a fallback when configuration validation fails. |
| DOMAIN | img[.]responsive[.]pstatic[.]autos | Domain listed among the campaign's C2 indicators and described as mimicking Naver's static-content domain. |
| DOMAIN | img[.]smartnords[.]site | Domain listed in the article's C2 infrastructure indicators. |
| DOMAIN | img[.]socialteams[.]store | Domain contacted by a trojanized agetty instance for CurlRAT activity. |
| DOMAIN | img[.]worksongo[.]store | Domain contacted by a trojanized polkitd instance for CurlRAT activity. |
| SHA256 | 009a1e2d7a582a24e50cf2ffc2a005482c8e38f22bf5ed416053855f8d054e1e | Hash listed as a CurlRAT malware artifact. |
| SHA256 | 09739441ed4599bac2f8159028f772f71e4b25c8badfff95574e56d7384f3dbe | Hash of a CurlRAT stager variant identified in the article. |
| SHA256 | 12810854c8b2c391b23e2e18b013e873d0369b0637aa3cf993136c07188ba3b8 | Hash listed as a CurlRAT malware artifact. |
| SHA256 | 2f02b09d61d432134e994ad671258f523bbf289ae6091fd4eae192c60bd51b6f | Hash of a trojanized agetty binary listed as a CurlRAT-related artifact. |
| SHA256 | 4bb923eb040aa13ca8fd409c31ee4729c60ddff32e350efe1c5a4a9168a065f5 | Hash of the SSH keylogger identified in the article. |
| SHA256 | 5db1b6d52faf60b4f32d6fd0c7c938e4d05d29a14c32ded4a9668357c08b6a91 | Hash of the CurlRAT stager identified in the article. |
| SHA256 | 6cf1b5e92a9c0756f597a5ddefb38eba32961c52efac7ab2a0aa52c639a8fc53 | Hash listed as a CurlRAT malware artifact. |
| SHA256 | 7007a78d50a993cb174c685eba96eb442c9507e38fd9d8e5dffc712f613ec110 | Hash listed as a CurlRAT malware artifact. |
| SHA256 | 72e70936f0dbe459142a1d867617c35f8d0cce5d18c6a49e1090a2a5adc8e558 | Hash of a recompiled HAProxy build containing the ted backdoor plugin. |
| SHA256 | 83f7d565b0465546027052b597af46eae3a199e7a91fcc2ab936341147349130 | Hash listed as a CurlRAT malware artifact. |
| SHA256 | 8f30b57928934ae67478d0e690c91d046e35a638da098d02922a4a88a0fdb66c | Hash of an earlier CurlRAT version listed as an artifact. |
| SHA256 | 94630b96f628c96a6bff7904b40ffc9ad67c86f8a4ff6080c3b524831c93f402 | Hash listed as a ted backdoor artifact. |
| SHA256 | a1d8af3a6acb731f07f72040eccb3450c1c83d40e29f736c2a63d35388660be4 | Hash of a trojanized polkitd binary listed as a CurlRAT-related artifact. |
| SHA256 | a8bfab4de81a1acb04aacdf757346946b0f5e30f0c9f402004016d0e425119c7 | Hash listed for a ted backdoor sample containing CurlRAT configuration. |
| SHA256 | d53c760c23b4405eb04ad0f20ead375440344b3bdf1fb7854ed12e40d155eabe | Hash of a trojanized cronie binary listed as a CurlRAT-related artifact. |
| SHA256 | ed72f4cd8d467b5c5d95ae6aeca4aaeea14d79565d379c1ca5871a714727be16 | Hash listed as a CurlRAT malware artifact. |
| SHA256 | fea1bc36632c71e5a839803469ef60ac47595d36b2c50934ac109ade6df06e61 | Hash of a CurlRAT stager variant identified in the article. |
| SHA256 | feeea9d0bf6ae7396d28271baa51ae50df5169ce5d32a516865856f91abc50b3 | Hash of the CurlRAT sample analyzed in the article. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe toolkit encrypts configuration and payload data with XOR and substitution ciphers and uses Base64 encoding for C2 data.T1036.005 · Match Legitimate Resource Name or LocationThe toolkit uses trojanized crond, polkitd, agetty, and atd binaries, and CentOS CurlRAT functions are named with atd_ prefixes.T1041 · Exfiltration Over C2 ChannelCurlRAT returns command output over its C2 channel, and the toolkit sends captured credentials and session data to operator infrastructure.T1057 · Process DiscoveryThe CurlRAT watchdog monitors HAProxy process status by reading its PID and checking process information.T1059.004 · Unix Shellted backdoor and CurlRAT execute commands through popen; CurlRAT also provides reverse-shell and PTY-shell handlers.T1070.002 · Clear Linux or Mac System LogsThe stager selectively removes matching keywords from shell history and Linux system logs.T1070.006 · TimestompThe stager gives the trojanized crond binary the creation timestamp of /usr/bin/ssh.T1071.001 · Web ProtocolsCurlRAT communicates with C2 over HTTP or HTTPS; ted backdoor carries its C2 traffic through HTTP responses on the HAProxy connection.T1082 · System Information DiscoveryThe stager profiles hostname, OS distribution and version, kernel details, and CPU architecture; CurlRAT also sends system information in a beacon.T1102 · Web ServiceThe article describes CurlRAT using web-hosted C2/configuration domains, including fallback and secondary hosts.T1106 · Native APIThe article identifies pthread-based shell threads and HAProxy allocation and task-scheduling calls used by the implant.T1119 · Automated Collectionted backdoor automatically logs HTTP request records that match its configured filters.T1132.001 · Standard EncodingCurlRAT encodes C2 payloads with Base64 after XOR processing.T1185 · Browser Session Hijackingted backdoor replaces or appends payload content to selected HTTP responses delivered through HAProxy.T1190 · Exploit Public-Facing ApplicationThe article describes exploitation of an exposed Groupware login portal as an assumed, unconfirmed initial-access scenario.T1480 · Execution GuardrailsDeployment and execution are gated on checks including HAProxy or cron presence, victim-token validation, and ted backdoor targeting rules.T1497.001 · System ChecksThe CurlRAT watchdog checks for /usr/lib/libvirtlog.so.0 and aborts when the check does not indicate a virtualized environment.T1539 · Steal Web Session Cookieted backdoor captures selected HTTP traffic, including session-related request data and cookies.T1543 · Create or Modify System ProcessThe stager overwrites the legitimate crond binary with a trojanized version and restarts the service.T1548 · Abuse Elevation Control MechanismCurlRAT's reverse-shell handler calls setuid(0) and setreuid(0, 0); the stager also checks for root privileges before dropping a payload.T1556.003 · Pluggable Authentication ModulesThe SSH keylogger intercepts plaintext passwords through userauth_passwd() and saves them to an encrypted log.T1560 · Archive Collected DataThe SSH keylogger encrypts captured credentials before writing them to a log; CurlRAT applies XOR and Base64 processing to outbound data.T1562.006 · Indicator Blockingted backdoor alters HAProxy connection and traffic counters to conceal intercepted C2 requests.T1568 · Dynamic ResolutionCurlRAT derives a victim identifier from a cron version string, hostname, IP address, and hardware/OS UUID, then uses it in C2 requests.T1572 · Protocol Tunnelingted backdoor uses named pipes and the HAProxy HTTP connection to dispatch shell activity and return output.T1574.006 · Dynamic Linker HijackingThe ted plugin is integrated as an HAProxy filter loaded when the HAProxy process starts.
Threat Actors
APT37The article says the C2 list is associated with APT37 by ThreatFox and maltrail, and assesses the campaign's attribution to DPRK APTs with medium confidence.KimsukyMentioned as a group whose documented tradecraft is consistent with the plausible exposed mail-server initial-access scenario; the article does not confirm Kimsuky conducted this campaign.Lazarus GroupThe article compares the campaign with Operation SyncHole and describes overlapping South Korea targeting and tradecraft; it does not definitively attribute this toolkit to Lazarus Group.
Malware
CurlRATinternal servers. The stager checks for the presence of either crond or HAProxy, and only then deploys CurlRAT retrieving it either from its data section or the edge webserver. ted backdoorand media industries with minimal detection. The campaign made use of a HAProxy instance named “ted backdoor”, alongside trojanized versions of crond, agetty, atd, sshd, and polkitd. This previously undocumented
Products
HAProxyacross South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “ted backdoor”, alongside trojanized versions of crond, agetty, atd, sshd, and polkitd.LinuxA new Linux toolkit, identified by Rapid7 Labs, has been targeting organizations across South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “ted
Countries
DPRKThe toolkit is attributed with medium confidence to DPRK APTs, given that the attacks Rapid7 observed were targeting South Korean media and automotive sectors, likely aiming at long-term espionage, the usage of simpleSouth KoreaA new Linux toolkit, identified by Rapid7 Labs, has been targeting organizations across South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “ted
Industries
AutomotiveA new Linux toolkit, identified by Rapid7 Labs, has been targeting organizations across South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “tedMediatoolkit, identified by Rapid7 Labs, has been targeting organizations across South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “ted backdoor”,