cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2385 articles

Threat Research · thehackernews.com

Breeze Comet Uses Custom Malware to Target Brazilian Payment Systems

GTIG and Mandiant describe Breeze Comet intrusions into Brazilian organizations, using phishing, RMM tools, vulnerable JBoss servers and custom malware to reach payment systems. The group has executed hundreds of fraudulent transactions; expansion abroad may be underway
Sep 2, 2026
Threat Research · malwareinfo.app

Fake GlobalProtect Installer Uses Myanmar Geofencing and Google Sheets C2

Researchers traced an unsigned, GlobalProtect-themed MSI through Myanmar geofencing and Google Sheets tasking to a follow-on payload. The evidence supports malware activity but does not establish attribution to SideWinder or another actor.

Sep 2, 2026
Threat Research · threatfabric.com

StreamRat Android Banking Trojan Uses Social Media Ads to Take Control of Devices

ThreatFabric details StreamRat, an Android banking trojan promoted through ads targeting Spanish-speaking users. Its dropper installs the malware, which abuses Accessibility Services and screen capture for remote control, credential theft, and data collection.

Sep 2, 2026
Threat Research · huntress.com

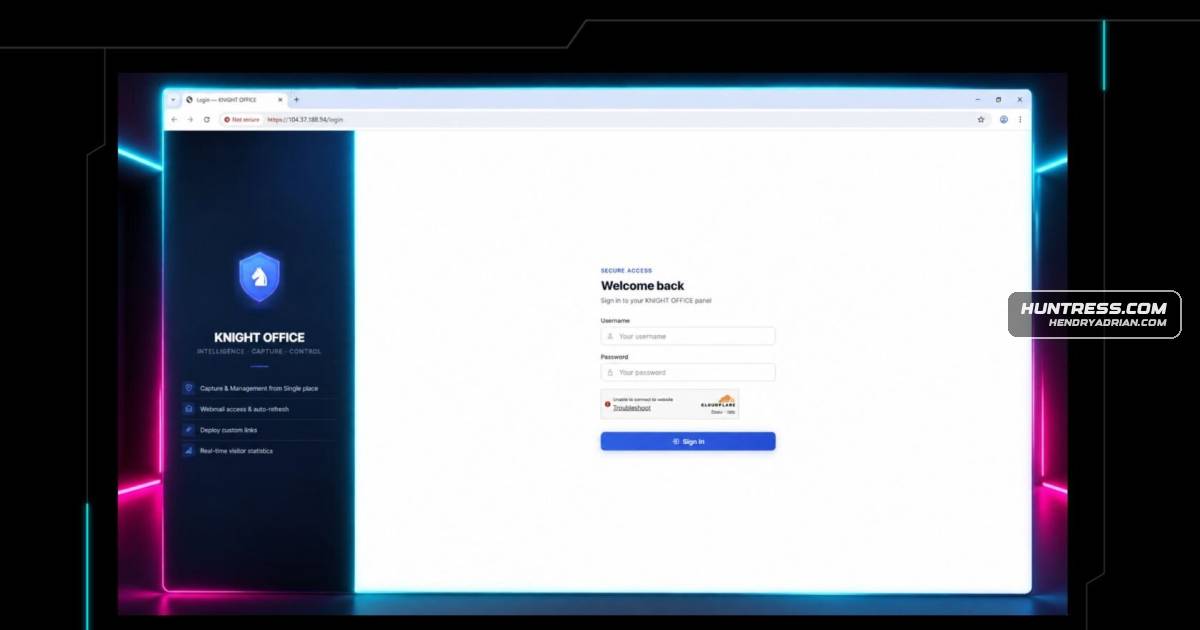
Knight Office AiTM Kit Steals Microsoft 365 Session Tokens and Establishes Persistent Access

Huntress traced a Microsoft 365 AiTM phishing attack to the Knight Office kit, which captured session tokens and enabled unauthorized device registration and Windows Hello credentials. Telemetry linked at least nine token-replay attacks to the kit.

Sep 2, 2026
Threat Research · malwarebytes.com

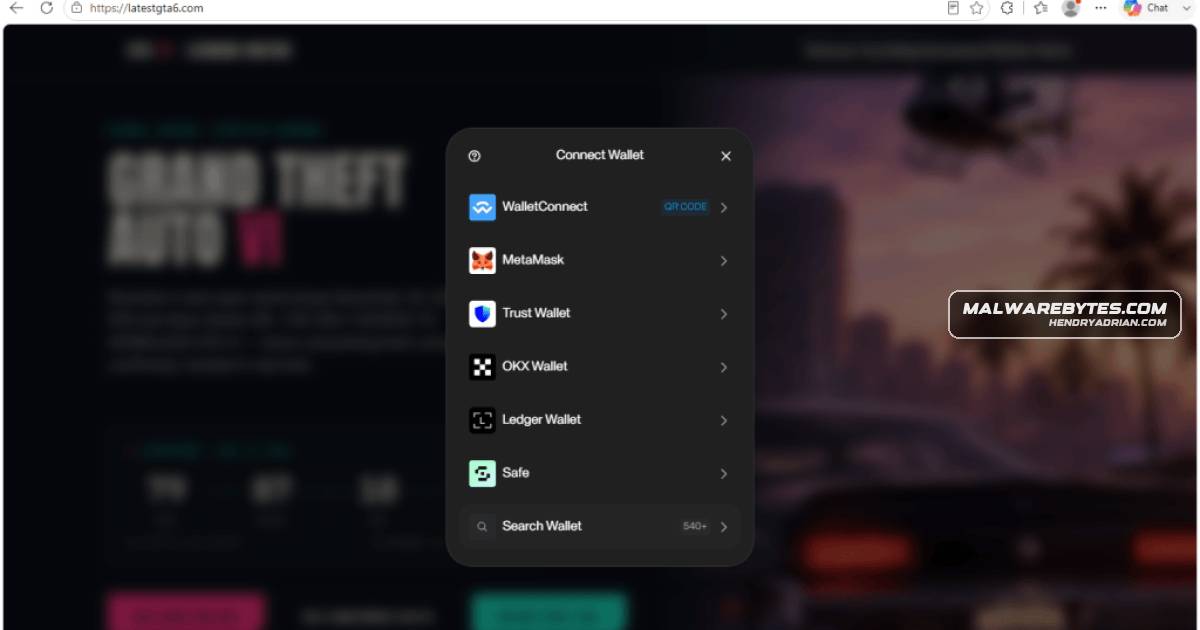
Fake GTA 6 Leak Site Uses Code to Drain Cryptocurrency Wallets

Malwarebytes analyzed a fake GTA 6 leaked-copy site that profiles connected wallets and can seek transfers or token and NFT approvals across seven blockchains. The article explains the code and advises users to reject suspicious wallet requests.

Sep 1, 2026
Threat Research · cisecurity.org

PowerShell RAT Campaign Uses Phishing and Dual RMM Tools to Target U.S. SLTT Networks

CIS reports an active phishing campaign targeting U.S. state, local, tribal, and territorial networks with a PowerShell WebSocket RAT and ScreenConnect and Pulseway RMM tools for persistent access.

Sep 1, 2026
Threat Research · asec.ahnlab.com

AhnLab Links Seafood-Themed Malicious LNK Attack to Kimsuky

AhnLab analyzes a malicious LNK disguised as a seafood purchase request that displays a decoy HWP document, runs scripts on a 14-minute schedule, sends system data through Backblaze B2, and retrieves follow-up commands.

Sep 1, 2026
Threat Research · asec.ahnlab.com

MoiClient Backdoor Uses UAC Bypass and Vulnerable Driver to Deploy Browser Stealer

AhnLab details MoiClient, a backdoor delivered in an invoice-themed VHDX that uses DLL side-loading, an RPC-based UAC bypass, and a vulnerable driver to disable security tools, persist, and deploy a browser-information stealer.

Sep 1, 2026
Threat Research · securityweek.com

Forescout Uses Claude to Port WAGO PLC Exploit, Bricking Device in C2 Test

Forescout researchers used Claude Code to port a CVE-2021-31886-based RCE exploit from a WAGO 750-852 to a 750-831, requiring extensive oversight and over $500 for the final RCE stage; a C2 follow-up permanently bricked the PLC.

Sep 1, 2026
Threat Research · securelist.com

Mirage Kitten Deploys Node.js and JavaScript RATs Through Fake Job Challenges

Kaspersky details Mirage Kitten’s use of NodeRabbit and PollCat, cross-platform RATs delivered in trojanized coding challenges to targets in the Middle East and Africa.

Sep 1, 2026
Threat Research · huntress.com

Compromised Atera RMM Used to Target Three MSP Customers

Huntress traced malicious activity at three MSP customers to a compromised Atera RMM instance. The actor created local administrator accounts and installed Cloudflared tunnels; Huntress isolated affected endpoints before the attacks progressed further.

Sep 1, 2026
Threat Research · huntress.com

Tampered Exodus Installer Hides Modular RAT with Remote Access and Credential-Theft Features

Huntress details a campaign using fake documents and software updates to install a trojanized Exodus wallet that loads a modular RAT, enabling hidden remote access, browser credential theft, and SOCKS proxying.

Sep 1, 2026
Threat Research · cloud.google.com

BREEZE COMET Uses Custom Malware to Target Brazil’s Financial Systems

Mandiant details BREEZE COMET’s intrusions into Brazilian financial and related organizations, including custom malware, compromised websites, credential theft, and fraudulent transfers, and provides indicators and defensive recommendations.

Sep 1, 2026
Threat Research · sophos.com

Sophos Details GOLD SHERWOOD’s The Gentlemen Ransomware Playbook

Sophos researchers analyzed 15 incidents linked to The Gentlemen ransomware operation, detailing how affiliates gain access, escalate privileges, evade defenses, exfiltrate data and deploy ransomware—sometimes within 24 hours of observed post-compromise activity.

Sep 1, 2026
Threat Research · thehackernews.com

Kaspersky Details ValleyRAT Campaign Using Signed QN Wallpaper Adware

Kaspersky says Silver Fox likely distributed ValleyRAT through signed QN Wallpaper adware, using DLL sideloading to run the backdoor in a trusted process. Its analysis was based on one submitted installer and gave no victim count for this route.

Aug 31, 2026
Threat Research · bleepingcomputer.com

Microsoft Details TerminalFix ClickFix Attacks Using Reverse Tunnels

Microsoft details TerminalFix, a ClickFix campaign using fake Cloudflare CAPTCHA prompts to run PowerShell, deploy in-memory payloads, persist, conduct reconnaissance and provide a Python reverse tunnel. Microsoft saw no hands-on activity.

Aug 31, 2026
Threat Research · securonix.com

Clop Campaign Exploits PTC Windchill Flaw to Steal Data and Credentials

A detailed analysis links Clop’s Windchill data-theft campaign to CVE-2026-12569, describing custom JSP implants that can steal files and decrypt stored credentials, along with indicators, scoping advice, and defensive measures.

Aug 31, 2026
Threat Research · threatlabs.netskope.com

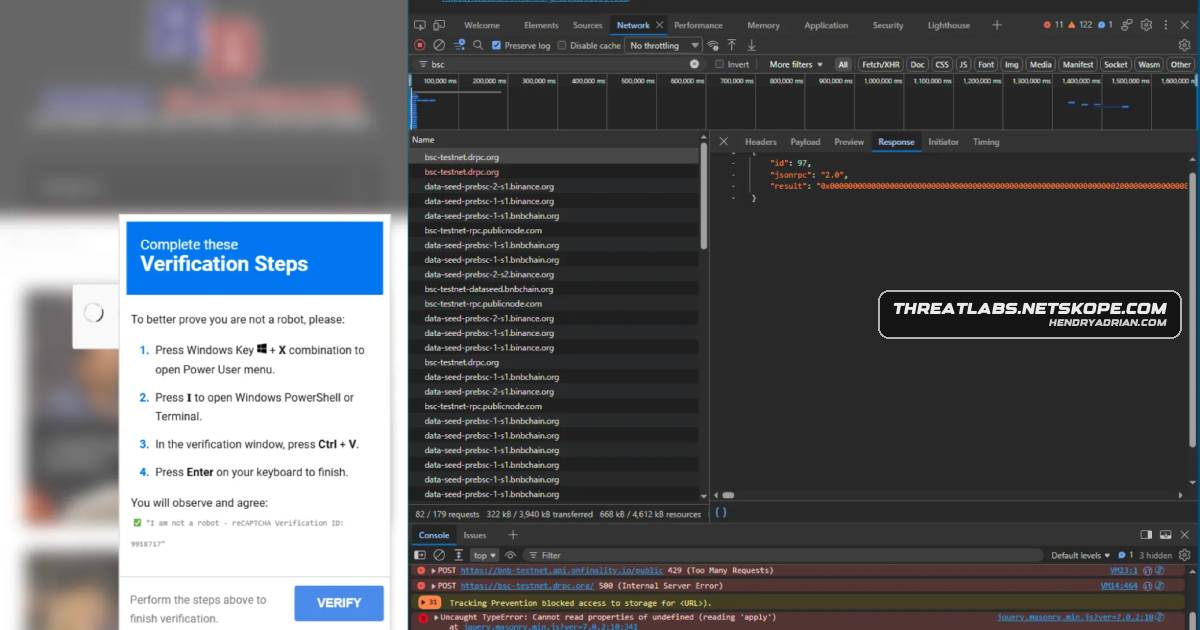
EtherHiding Campaign Targets 5,400+ Compromised Sites with WebRTC-Based C2

Netskope reports an EtherHiding campaign using BSC testnet contracts to deliver malware through more than 5,400 compromised sites. A newer variant forges a WebRTC answer to open a covert C2 channel without signaling traffic.

Aug 31, 2026
Threat Research · bleepingcomputer.com

Fire Ant Uses Compromised Cisco Routers to Spy on High-Value Networks

Sygnia reports that Fire Ant compromised Cisco routers and related systems to capture network traffic and reach connected high-value environments, using hidden GRE tunnels, custom malware and a disguised backdoor called BridgeAgent.

Aug 31, 2026
Threat Research · helpnetsecurity.com

GreyNoise Finds AI Crawler Impersonation Used to Scan for Exposed Credentials

GreyNoise identified 824 IPs spoofing AI-crawler identities to scan for exposed credentials and configuration files. None matched published vendor ranges; it could not confirm that any files were accessed or secrets stolen.

Aug 31, 2026
Threat Research · socket.dev

13 Malicious Packagist Themes Deliver iOS Spyware and Steal Crypto Wallet Seeds

Socket found 13 trojanized Composer themes that inject gambling redirects and, on vulnerable iPhones, a WebKit-to-kernel exploit chain delivering spyware that steals device data and cryptocurrency wallet seeds.

Aug 31, 2026
Threat Research · research.checkpoint.com

Researchers Reveal JSCeal Stealer Capabilities Using Static V8 Bytecode Deobfuscation

Check Point researchers developed a static pipeline to deobfuscate JSCeal’s compiled V8 bytecode, revealing credential theft, keylogging, surveillance, and HTTPS interception. They also document newer payload encryption, V8 version changes, and macOS targeting.

Aug 31, 2026
Threat Research · unit42.paloaltonetworks.com

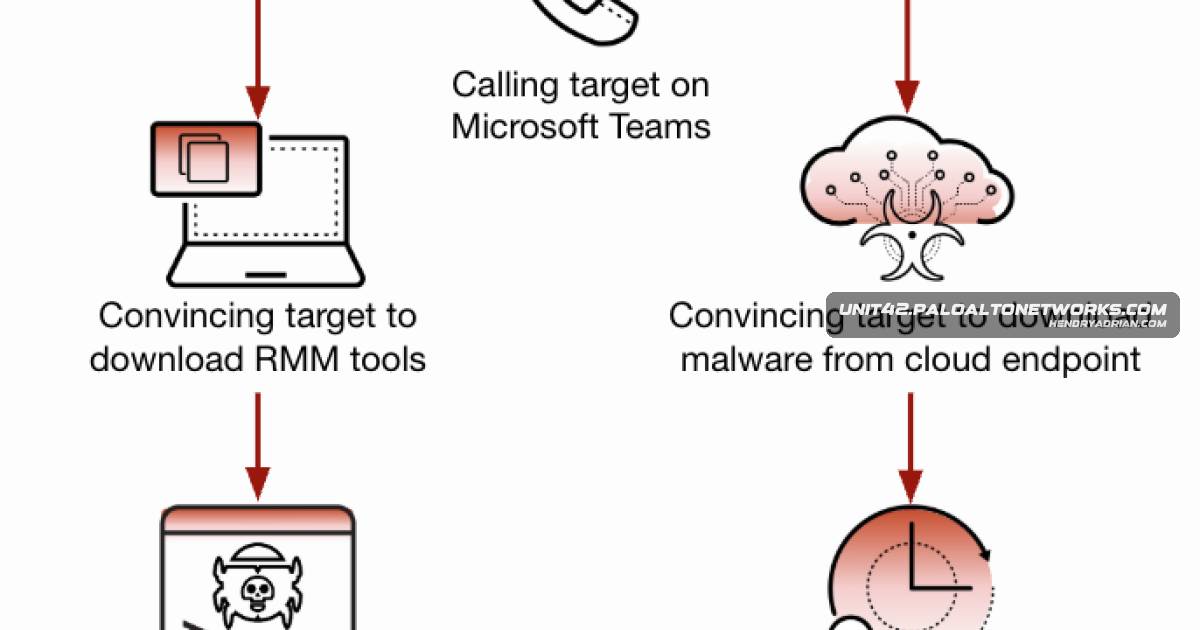
Spring Ring Campaigns Use Microsoft Teams Vishing to Deliver Malware and Attempt NTLM Relay

Unit 42 reports that Spring Ring operators used Microsoft Teams help-desk impersonation and voice phishing to target over 150 employees at 10+ companies, delivering malware and attempting an NTLM relay attack; defenses blocked the observed activity.

Aug 31, 2026
Threat Research · securelist.com

ValleyRAT Backdoor Disguised as Adware Uses DLL Sideloading to Spy on Victims

Researchers found installers posing as adware that deploy the ValleyRAT backdoor through DLL sideloading, disable Windows Defender, and collect keystrokes, clipboard data, screenshots, and system information.

Aug 31, 2026
PreviousPage 28 of 100 Next
© 2026 cyber.hendryadrian.com