
BraZetsu Malware Turns Compromised Windows Hosts Into Marketplace Inventory
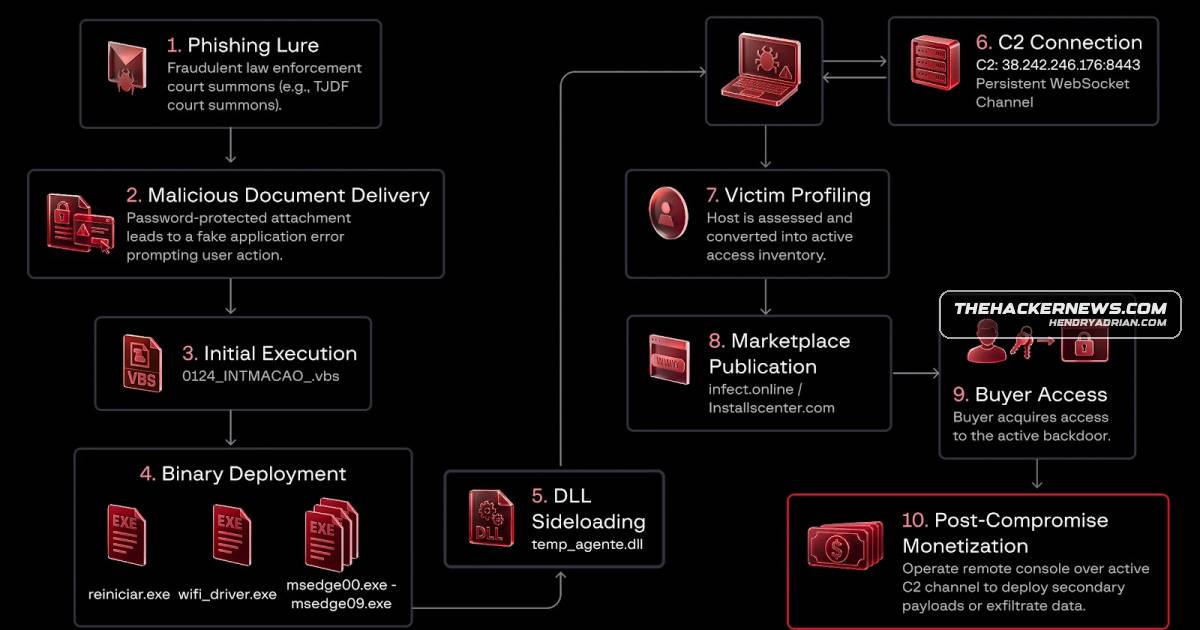
Summary
Group-IB describes BraZetsu, a Python-based Windows framework that helps Exilware sell access to compromised hosts. It gathers system, browser, and financial data to prioritize targets; delivery remains unclear.
Key points
- BraZetsu is a modular Python framework that scans Windows hosts and gathers system data, browser histories, certificates, screenshots, and Brazilian CNAB financial files.
- Group-IB says Exilware uses the Infected Marketplace to sell access to compromised systems, where buyers can remotely run additional payloads.
- The malware uses generative AI to assess and prioritize compromised hosts; researchers say five versions have been observed, with later versions focusing on Brazilian corporate targets.
- Researchers found code and infrastructure overlaps with CNABHunter and AgenteV2; Group-IB assesses that AgenteV2 and BraZetsu are the same initial-access framework.
- The delivery method is unknown. A loader disguised as Microsoft Edge and files from caixaentradas1inboxshop[.]site provide clues, while social engineering is considered likely.
- BraZetsu communicates with the marketplace over WebSocket and retrieves command-and-control information from a Pastebin URL.
Article Details
- Attack Vectors
- BraZetsu is described as a Python-based Windows framework used to establish initial access and catalog compromised systems for resale through the Infected Marketplace.
- The delivery method for BraZetsu remains unclear; researchers consider social engineering the most likely route. A loader masquerading as Microsoft Edge was downloaded from a distribution domain, and associated VBS files downloaded the next stage.
- BraZetsu retrieves C2 information from a Pastebin URL and uses WebSocket communication to maintain contact with the Infected Marketplace.
- The framework conducts host and network reconnaissance, collects browser histories, certificates, screenshots, system data, and CNAB financial files, and supports remote shell command execution and deployment of additional modules.
- Marketplace buyers can remotely execute their own malicious payloads or tools on purchased compromised systems.
- CNABHunter scans directories for CNAB files, exfiltrates payment metadata, polls a remote server for commands, and can replace legitimate payment details with attacker-controlled banking details, PIX keys, or barcodes.
- Defensive Notes
- Monitor for suspicious loaders masquerading as Microsoft Edge, VBS scripts downloading subsequent stages, and unexpected downloads from the reported distribution domain.
- Hunt for BraZetsu-like collection and reconnaissance activity, including browser-history and screenshot collection, searches for CNAB files, environment-variable and process enumeration, and remote shell execution.
- Monitor endpoints and network traffic for persistent WebSocket communications associated with the Infected Marketplace and for malware retrieving C2 configuration from Pastebin.
- Protect corporate financial workflows by monitoring for unauthorized access to or modification of CNAB files and payment details.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | caixaentradas1inboxshop[.]site | Distribution domain used to deliver a loader masquerading as Microsoft Edge and associated VBS files for the BraZetsu attack. |
| DOMAIN | infect[.]online | Domain identified in the article as the Infected Marketplace used by Exilware to monetize access to compromised hosts. |
| IPV4 | 38[.]242[.]246[.]176 | IP address identified in artifacts matching Exilware's naming convention and previously tied to the AgenteV2 backdoor. |
MITRE ATT&CK
T1005 · Data from Local SystemBraZetsu collects browser histories, certificates, screenshots, system data, and financial files from compromised hosts.T1010 · Application Window DiscoveryBraZetsu obtains the active application window title and checks it for banking-related keywords.T1016 · System Network Configuration DiscoveryBraZetsu maps network infrastructure and enumerates network ports.T1036.005 · Match Legitimate Resource Name or LocationThe BraZetsu loader masquerades as Microsoft Edge.T1057 · Process DiscoveryBraZetsu enumerates running processes.T1059.005 · Visual BasicVBS files associated with the distribution domain download the next attack stage; the article also describes a VBS script executing the final payload in the Ousaban delivery chain.T1071.001 · Web ProtocolsBraZetsu uses WebSocket communications to maintain persistent contact with the Infected Marketplace.T1082 · System Information DiscoveryBraZetsu profiles system hardware and software environment to assess compromised machines.T1083 · File and Directory DiscoveryBraZetsu locates CNAB files, recently opened files, and common ERP installation directories.T1105 · Ingress Tool TransferThe BraZetsu framework supports deployment of additional worker modules, and marketplace buyers can deploy secondary payloads to purchased hosts.T1113 · Screen CaptureBraZetsu captures screenshots, and AgenteV2 streams a victim's screen to the attacker in real time.T1217 · Browser Information DiscoveryBraZetsu collects browser histories from Chrome, Edge, Brave, Vivaldi, and Opera.
People
@johnk3rResearcher who publicly disclosed CNABHunter one day before BraZetsu was discovered in the wild, according to the article.Julio Guapo MenezesGroup-IB malware analyst who commented on BraZetsu's role in supporting initial access brokers.Miguel SalazarGroup-IB malware analyst who commented on BraZetsu's role in supporting initial access brokers.Serhii MelnykSecurity researcher who reported findings from a machine apparently used by a Blind Eagle operator.
Threat Actors
Blind EagleSpanish-speaking hacking group described as targeting government agencies, financial institutions, and corporate entities in Latin America.Dark CaracalCyber espionage group attributed in the article to an intrusion affecting a communications organization in Venezuela.ExilwareTracked threat actors who use BraZetsu and the Infected Marketplace to commercialize access to compromised systems.
Malware
agenteV2The malware targets Iberian and Latin American organizations, uses AI-assisted triage and stealthy reconnaissance, and overlaps in function and infrastructure with CNABHunter and AgenteV2.AsioGatethe threat actor used invoice-themed lures containing SVG attachments to distribute a backdoor called AsioGate, a successor to Poco RAT, via a Delphi loader in attacks targeting users and entities in Chile andBandookThe incident, which took place in June 2026, resulted in the deployment of a previously undocumented Go-based modular framework codenamed GoCaracal and an updated version of Bandook.BraZetsuResearchers uncovered BraZetsu, a Python-based Windows malware framework used by Exilware to turn compromised systems into tradable access points on the Infected Marketplace.CNABHunterThe malware targets Iberian and Latin American organizations, uses AI-assisted triage and stealthy reconnaissance, and overlaps in function and infrastructure with CNABHunter and AgenteV2.GoCaracalThe incident, which took place in June 2026, resulted in the deployment of a previously undocumented Go-based modular framework codenamed GoCaracal and an updated version of Bandook.OusabanInterestingly, the same domain has been used to deliver the Ousaban banking trojan.Poco RATinvoice-themed lures containing SVG attachments to distribute a backdoor called AsioGate, a successor to Poco RAT, via a Delphi loader in attacks targeting users and entities in Chile and Brazil.
Products
BraveCollects digital certificates, browser histories from Google Chrome, Microsoft Edge, Brave, Vivaldi, and Opera, and financial files while tracking user behavior through screen capturesGoogle ChromeCollects digital certificates, browser histories from Google Chrome, Microsoft Edge, Brave, Vivaldi, and Opera, and financial files while tracking user behavior through screen capturesMicrosoft EdgeCollects digital certificates, browser histories from Google Chrome, Microsoft Edge, Brave, Vivaldi, and Opera, and financial files while tracking user behavior through screen capturesOperaCollects digital certificates, browser histories from Google Chrome, Microsoft Edge, Brave, Vivaldi, and Opera, and financial files while tracking user behavior through screen capturesVivaldiCollects digital certificates, browser histories from Google Chrome, Microsoft Edge, Brave, Vivaldi, and Opera, and financial files while tracking user behavior through screen captures
Tools
BraZetsuResearchers uncovered BraZetsu, a Python-based Windows malware framework used by Exilware to turn compromised systems into tradable access points on the Infected Marketplace.CNABHunterThe malware targets Iberian and Latin American organizations, uses AI-assisted triage and stealthy reconnaissance, and overlaps in function and infrastructure with CNABHunter and AgenteV2.
Countries
BrazilBraZetsu is a portmanteau of “Brazil” and “Zetsu,” a fictional character from the Japanese Manga series Naruto who is known to operate as a threat from the shadows.Chilecalled AsioGate, a successor to Poco RAT, via a Delphi loader in attacks targeting users and entities in Chile and Brazil.ColombiaBlind Eagle is a Spanish-speaking hacking group active since at least 2018, primarily targeting government agencies, financial institutions, and corporate entities in Latin America, particularly in Colombia and Ecuador.EcuadorBlind Eagle is a Spanish-speaking hacking group active since at least 2018, primarily targeting government agencies, financial institutions, and corporate entities in Latin America, particularly in Colombia and Ecuador.Portugal“If they are in Spain or Portugal, the webpage downloads a VBS file to kickstart the next part of the attack.Spain“If they are in Spain or Portugal, the webpage downloads a VBS file to kickstart the next part of the attack.VenezuelaIn recent weeks, Dark Caracal, a cyber espionage group with ties to Lebanon’s General Directorate of General Security, has been attributed to a targeted intrusion affecting a communications organization in Venezuela.
Industries
CommunicationsIn recent weeks, Dark Caracal, a cyber espionage group with ties to Lebanon’s General Directorate of General Security, has been attributed to a targeted intrusion affecting a communications organization in Venezuela.corporateThe Singapore-headquartered company said BraZetsu is primarily scoped to target Iberian and Latin American targets in e-commerce, corporate, financial, industrial, law enforcement, and other environments.E-commerceThe malware targets Iberian and Latin American sectors, including e-commerce, finance, industry, and law enforcement.financialThe Singapore-headquartered company said BraZetsu is primarily scoped to target Iberian and Latin American targets in e-commerce, corporate, financial, industrial, law enforcement, and other environments.IndustrialThe Singapore-headquartered company said BraZetsu is primarily scoped to target Iberian and Latin American targets in e-commerce, corporate, financial, industrial, law enforcement, and other environments.Law enforcementThe malware targets Iberian and Latin American sectors, including e-commerce, finance, industry, and law enforcement.