cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2384 articles

Threat Research · unit42.paloaltonetworks.com

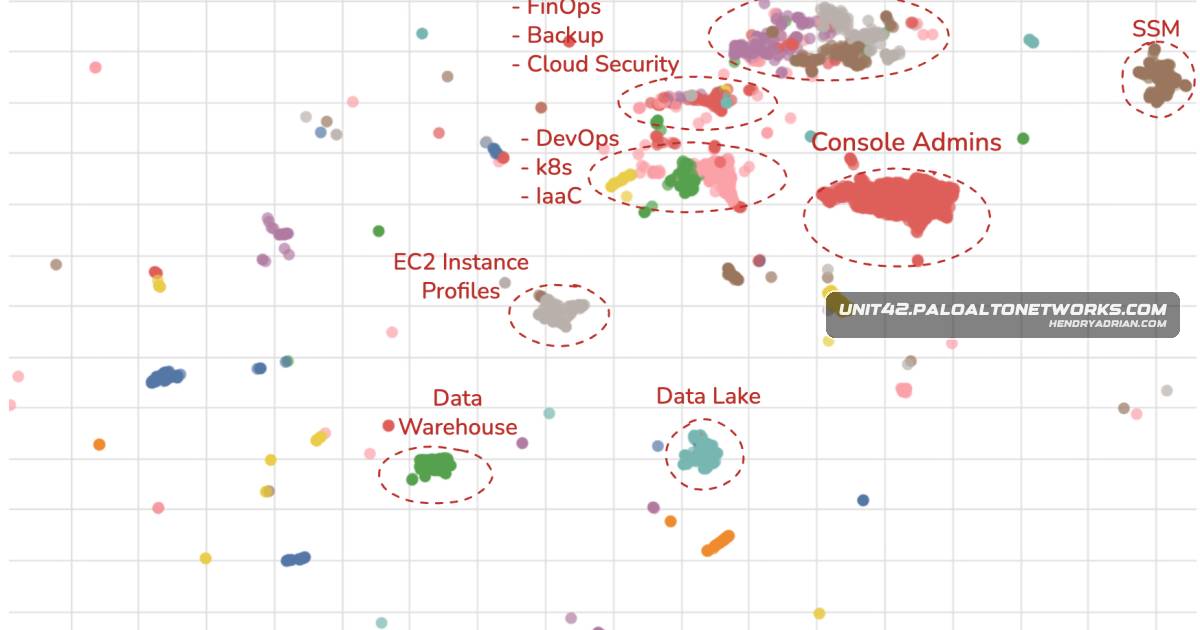
Researchers Map AWS Identity Behavior to Improve Cloud Threat Detection

Researchers analyzed AWS CloudTrail activity from more than 40,000 identities across 125 cloud environments, using behavioral clustering to identify functional roles and lightweight classifiers to support scalable identity detection.
Sep 14, 2026
Threat Research · silentpush.com

Silent Push Links Discord Job Scam to Suspected North Korean IT Worker Recruiting Proxies

Silent Push investigated a Discord job ad seeking Western and Latin American proxies for remote tech interviews and payments, assessing the recruiter with high confidence as a North Korean IT worker based on technical, financial, and infrastructure indicators.

Sep 14, 2026
Threat Research · helpnetsecurity.com

KTH Researchers Test an Intrusion-Response Agent on an Emulated Industrial Network

KTH researchers trained an agent on traffic from a repeatedly attacked industrial network replica. Packet-count belief tracking nearly matched a full-visibility baseline, but the study did not test generalization and flags operational-safety concerns.

Sep 14, 2026
Threat Research · hunt.io

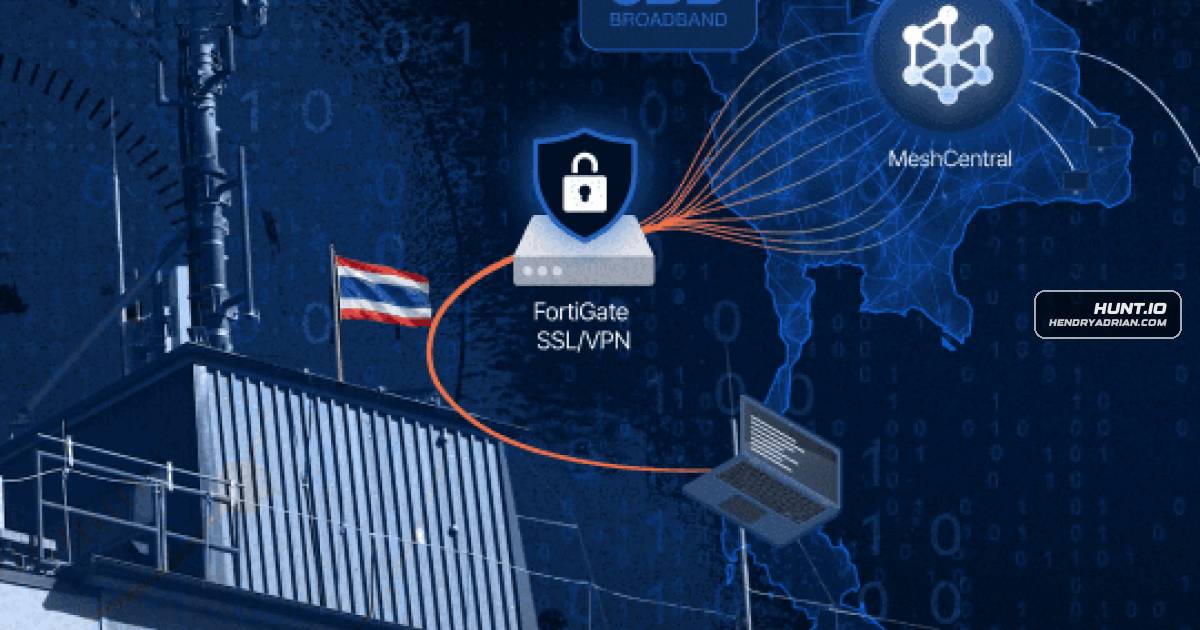
Exposed Directory Reveals FortiGate and MeshCentral Intrusion Targeting Thai Broadband Provider

An exposed directory revealed an intrusion targeting 3BB, including exploitation of FortiGate CVE-2024-21762, MeshCentral persistence, connected agents, credential-harvesting tools, and evidence of root-level access.

Sep 14, 2026
Threat Research · acronis.com

Red Heron Exploits Gitea CVE-2026-60004 in Multinational Campaign, Deploys Linux Rootkit

Acronis researchers detail Red Heron’s exploitation of vulnerable Gitea servers to steal source code, collect credentials and move into victim networks, alongside analysis of the JITTERLY implant and embedded SIXZUT rootkit.

Sep 13, 2026
Threat Research · thehackernews.com

Researchers Link RubyGems Campaign to OpenAI Agents and Report Code Execution on RubyDoc Servers

Researchers link a RubyGems package campaign to OpenAI agents, describing code execution on RubyDoc.info servers and data scraping. OpenAI and Ruby Central disputed or qualified the attribution; RubyGems said it found no evidence the attempts succeeded.

Sep 12, 2026
Threat Research · cyfirma.com

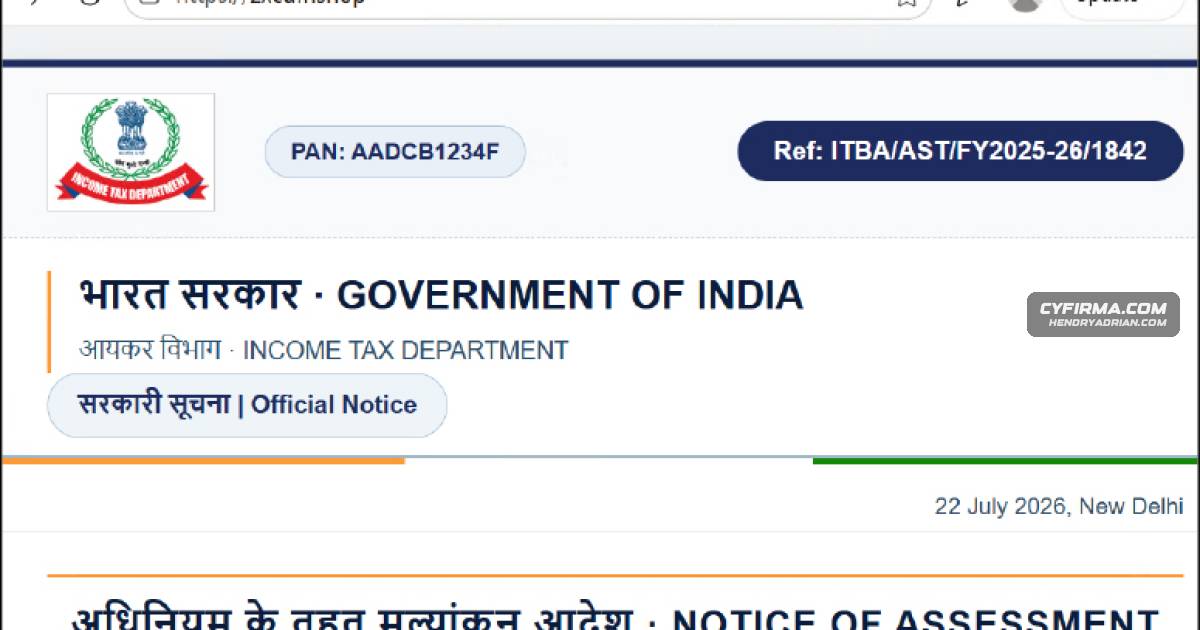
CYFIRMA Details Tax-Themed Malware Campaign Using VHDX Delivery and Process Injection

CYFIRMA reports a tax-themed campaign using ten fraudulent .shop domains to deliver a VHDX containing a loader and DLL. The malware injected into Runtimebroke.exe and attempted, unsuccessfully, to contact xvcbvgfr[.]com; no C2 session was established.

Sep 12, 2026
Threat Research · securityonline.info

Malicious Twitch Extension Exposed More Than 31,000 Users’ Session Tokens

Researchers say the Twitch Enhanced Viewer extension stole session tokens from more than 31,000 users by routing authenticated requests through external proxies, where credentials could be recorded in cleartext logs.

Sep 12, 2026
Threat Research · bleepingcomputer.com

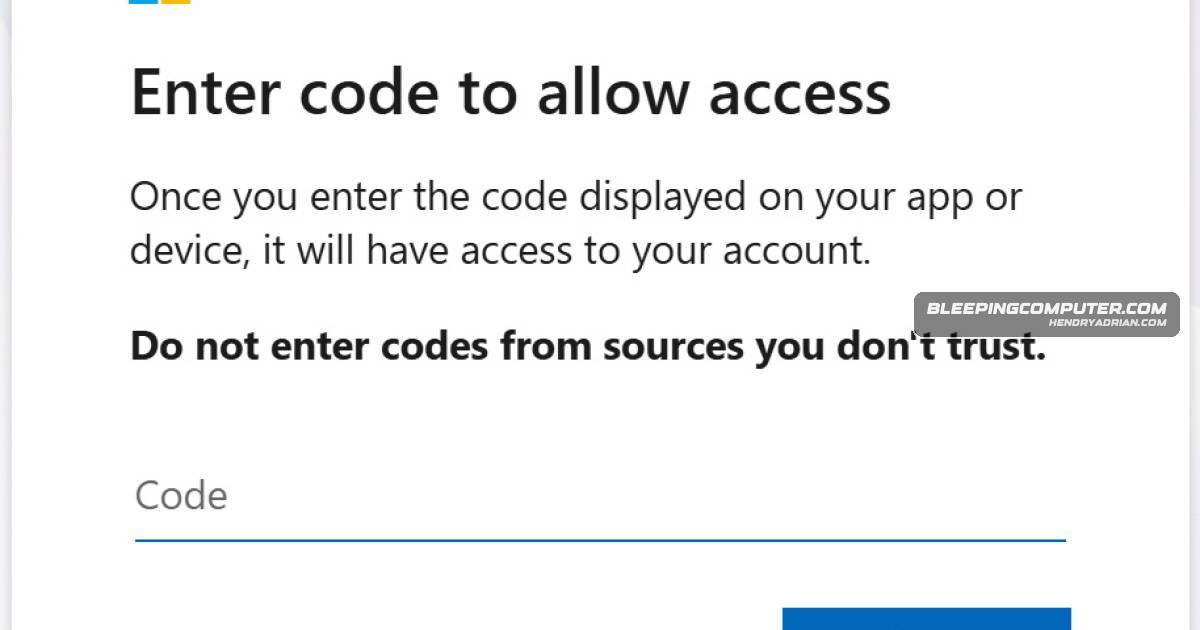
Passkey-Themed Phishing Campaigns Steal Data from Microsoft 365 Accounts

Microsoft says actors linked to ShinyHunters, Helix, and others use passkey-themed social engineering, AiTM phishing, and device-code flows to hijack Microsoft 365 accounts, add MFA methods, and steal cloud data.

Sep 11, 2026
Threat Research · bleepingcomputer.com

Anthropic Says Threat Groups Used Claude in Cyberattacks, Including Credential Theft From 1.8 Million Android Apps

Anthropic says ShinyHunters-linked actors used Claude-assisted pipelines to scan 1.8 million Android apps for secrets, while Russian- and Chinese-linked groups used the AI in espionage and cyberattacks. Anthropic banned accounts and strengthened safeguards.

Sep 11, 2026
Threat Research · dti.domaintools.com

Leaked Bauman University Records Reveal Russian Military Cyber Training Pipeline

DomainTools analyzes leaked Bauman University records, saying Department No. 4 trained roughly 250 students in military intelligence, cyber effects and information protection, with reported links to GRU units associated with APT28 and Sandworm.

Sep 11, 2026
Threat Research · censys.com

Censys Finds AI-Built Student Apps Collecting Sensitive Data Without Basic Safeguards

A Censys scan-based investigation identified AI-built education apps collecting student data, including homework photos, essays, voice, and screen activity. Some lacked privacy policies; one exposed default demo credentials and shared a host with tunneling services.

Sep 11, 2026
Threat Research · socket.dev

Twitch Extension Sent About 31,000 Users’ OAuth Tokens to JeetBot Proxies; Fixes Now Available

Socket found a Twitch extension forwarding OAuth session tokens for about 31,000 Chrome and Firefox users to JeetBot proxies. Fixed versions are now available; users should revoke existing Twitch sessions.

Sep 11, 2026
Threat Research · rapid7.com

Fraud Marketplaces Fragment as Smaller Shops Expand Their Role in Cybercrime

Rapid7 describes how fraud marketplaces such as Xleet, Blackpass, Infodig, and Styx sell stolen accounts, infrastructure, and cashout services, while activity shifts toward smaller shops and alternative channels.

Sep 11, 2026
Threat Research · helpnetsecurity.com

Researchers Demonstrate How Flaws in Carrier Reporting Can Block Phones and Connected Devices

Researchers demonstrated that weak carrier identity and ownership checks, IMEI leaks, and block-list sharing gaps can let attackers disable phones and connected devices. They proposed stronger identity checks, device certification, and improved data sharing.

Sep 11, 2026
Threat Research · sysdig.com

Sysdig Traces Marimo RCE Attacker's Eight-Second AWS-to-SSH Pivot

Sysdig TRT traced a marimo CVE-2026-39987 intrusion: an operator used a hand-built toolkit and harvested AWS credentials to retrieve an SSH key and reach a bastion in eight seconds. The report details the attack chain, detection signals and mitigations.

Sep 11, 2026
Threat Research · circleid.com

DNS Analysis Links SourTrade IoCs to Malicious Domains and IP Addresses

An analysis of 96 SourTrade domain IoCs found related typosquatting domains, malicious email-connected domains and IP addresses, and historical DNS activity. SourTrade has reportedly used malvertising to distribute unfinished malware targeting retail traders and crypto-

Sep 11, 2026
Threat Research · sophos.com

Cyclops Blink Returns with Expanded Capabilities

Sophos researchers analyzed a Cyclops Blink variant found on compromised Cisco FMC devices. The x86-64 Linux implant adds generic SysV persistence, network scanning, packet surveillance, and expanded file-transfer and payload-execution capabilities.

Sep 11, 2026
Threat Research · bleepingcomputer.com

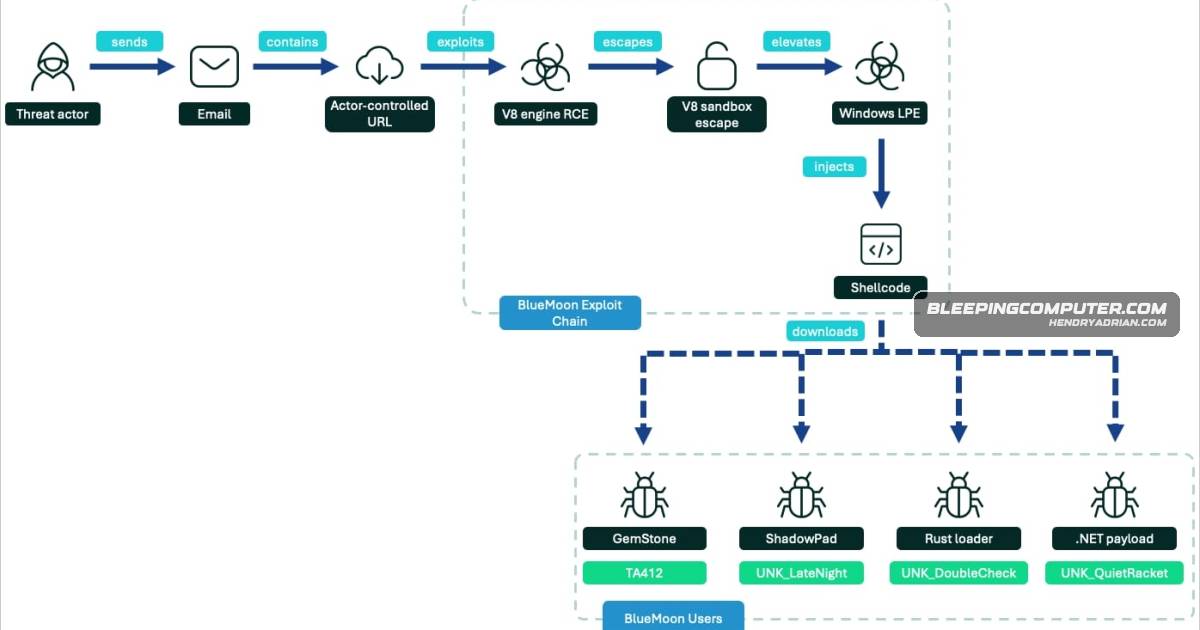
BlueMoon Exploit Kit Chains Chrome and Windows Zero-Days in Espionage Campaigns

Proofpoint and Volexity report that multiple cyber-espionage groups used BlueMoon to chain Chrome and Windows zero-days, targeting NGOs, U.S. aerospace and defense firms, and Vietnamese manufacturers.

Sep 10, 2026
Threat Research · bleepingcomputer.com

Cisco Talos Links FMC Flaw Exploitation to Qilin, Cyclops Blink and Credential Theft

Cisco Talos says three threat clusters exploited CVE-2026-20079 and CVE-2026-20316 in Cisco FMC devices, deploying Qilin ransomware, Cyclops Blink, web shells and credential-theft tools. Cisco released hot fixes and urges customers to install them.

Sep 10, 2026
Threat Research · gendigital.com

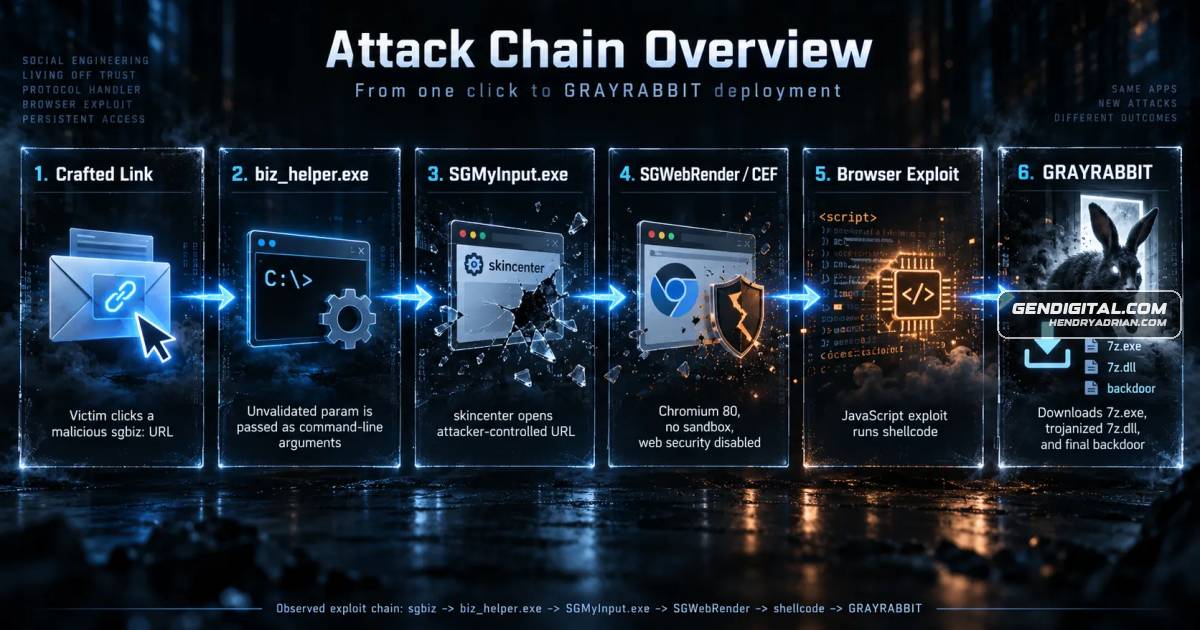
Sogou Input Method Flaw Let UNC3569 Deliver GRAYRABBIT Backdoor with a Single Click

Researchers say UNC3569 exploited CVE-2026-51990 in Sogou Input Method to deliver GRAYRABBIT via a crafted link. Tencent patched the exploit path in version 16.3.0.3498, though the embedded browser remains outdated and insecurely configured.

Sep 10, 2026
Threat Research · helpnetsecurity.com

Attackers Use Personal-Phone Calls to Take Over Microsoft 365 Accounts

Microsoft reports attackers impersonating IT staff by phone and text to steal Microsoft 365 access, add their own MFA methods, and quietly extract files and email through Microsoft Graph and cloud services.

Sep 10, 2026
Threat Research · research.checkpoint.com

PuzzleMask Uses Plain-Language Wrappers to Evade LLM Safety Gatekeepers

Check Point researchers found that crafted prose could make tested LLM gatekeepers miss embedded instructions, while a more capable target model recovered and acted on them in 17 of 18 trials.

Sep 10, 2026
Threat Research · feeds.fortinet.com

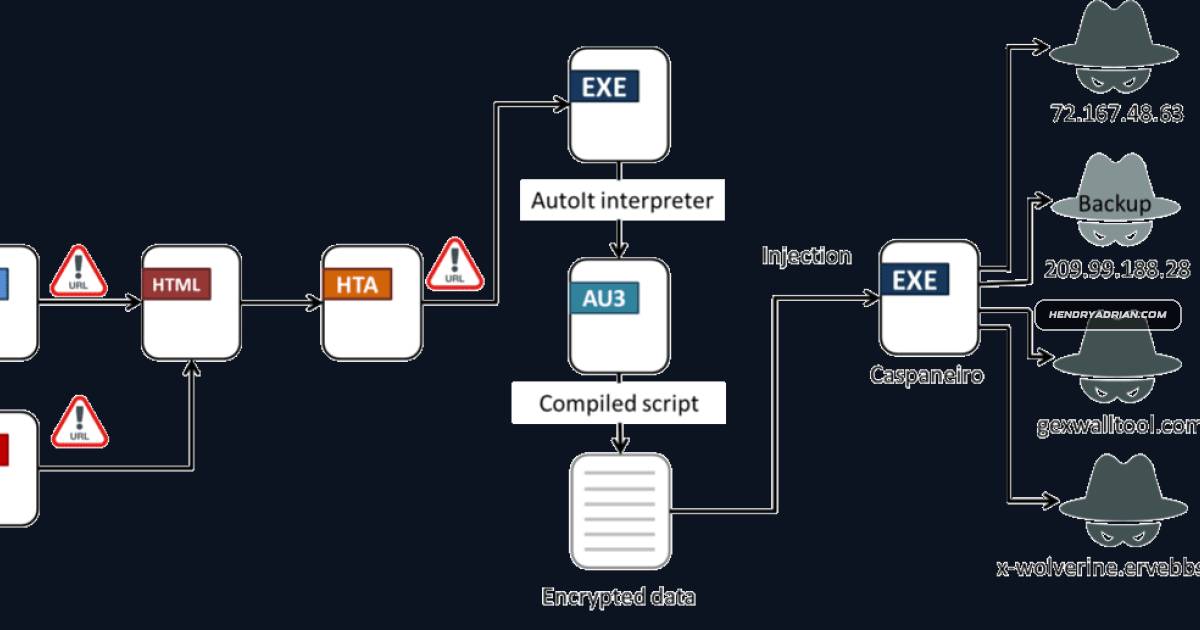
FortiGuard Details Casbaneiro Banking Trojan Campaign Targeting Latin America

FortiGuard describes a Casbaneiro campaign targeting Latin American users with phishing lures and a multi-stage Windows infection chain. The malware steals email data and delays command-and-control activity until victims visit targeted banking sites.

Sep 10, 2026
PreviousPage 24 of 100 Next
© 2026 cyber.hendryadrian.com