BlueMoon Exploit Kit Chains Chrome and Windows Zero-Days in Espionage Campaigns
Summary
Proofpoint and Volexity report that multiple cyber-espionage groups used BlueMoon to chain Chrome and Windows zero-days, targeting NGOs, U.S. aerospace and defense firms, and Vietnamese manufacturers.
Key points
- BlueMoon is described as a modular exploit kit used in distinct cyber-espionage operations.
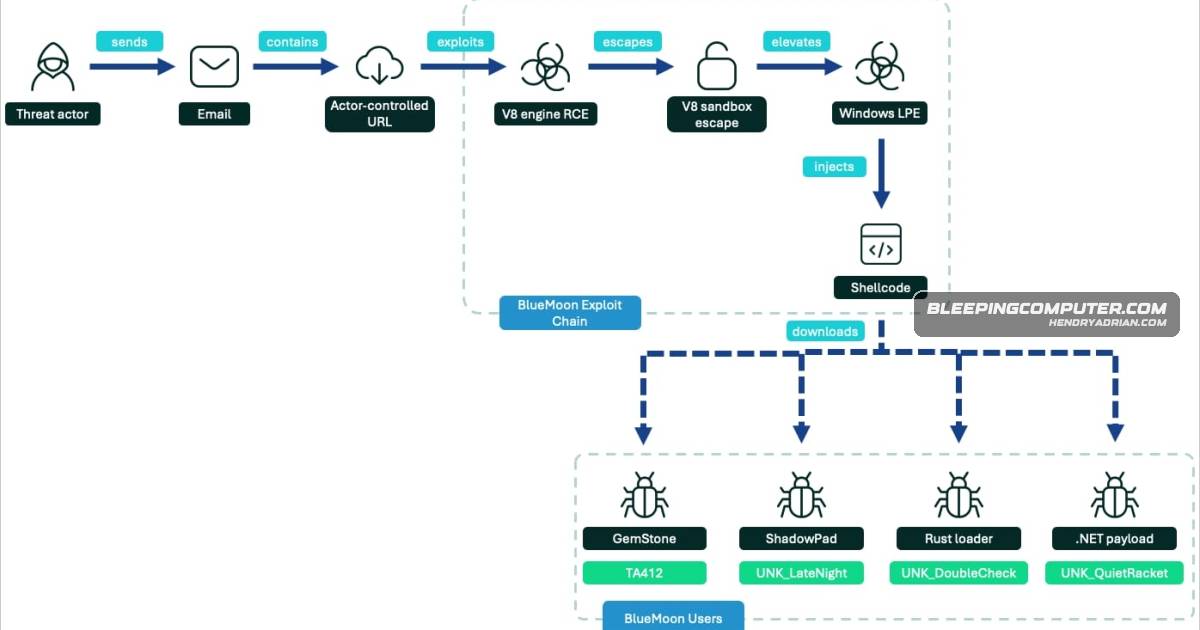
- It chains two Chromium flaws for remote code execution and sandbox escape with a Windows ALPC flaw for local privilege escalation: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880.
- The kit fingerprints systems, elevates the Chrome renderer, injects into Chrome’s parent process, and runs an operator-selected command; its default command downloads and runs an executable.
- Proofpoint observed JungleBamboo using BlueMoon in spearphishing operations starting August 28; Volexity reported similar UTA0560 activity targeting NGO customers on September 1.
- Other reported clusters targeted U.S. aerospace and defense firms and Vietnamese manufacturers. The final payload in the latter activity was not retrieved for analysis.
- Proofpoint suspects the Windows privilege-escalation exploit may have been used since 2025, based in part on a 2025 DLL compilation timestamp; this is not presented as confirmed.
Article Details
- Attack Vectors
- BlueMoon was used in spearphishing operations attributed to JungleBamboo, beginning August 28.
- Volexity observed UTA0560 using donation lures to target NGO customers on September 1.
- BlueMoon chained Chrome V8 vulnerabilities for code execution and sandbox escape with a Windows ALPC vulnerability for local privilege escalation.
- After fingerprinting the system and elevating the Chrome renderer, BlueMoon injected into Chrome's parent process to run an operator-selected command. Its default command used curl to download and run an executable from %TEMP%.
- Defensive Notes
- The article advises defenders to use the indicators of compromise shared in the Proofpoint and Volexity reports to block the activity early.
MITRE ATT&CK
T1055 · Process InjectionAfter elevating the Chrome renderer, BlueMoon injected into Chrome's parent process to run an operator-selected command.T1068 · Exploitation for Privilege EscalationBlueMoon exploited a Windows ALPC flaw to elevate privileges locally.T1105 · Ingress Tool TransferBlueMoon's default final command used curl to download an executable, typically a malware loader, to %TEMP%.T1203 · Exploitation for Client ExecutionBlueMoon exploited Chrome V8 flaws to achieve remote code execution in the browser.T1566 · PhishingProofpoint observed BlueMoon in spearphishing operations attributed to JungleBamboo; Volexity reported donation lures in UTA0560 campaigns.
CVE
CVE-2026-85046CVE-2026-85046: a type-confusion flaw in Chrome’s V8 JavaScript engine that provides arbitrary memory access inside the V8 sandboxCVE-2026-85880CVE-2026-85880: a heap-based buffer overflow in Windows ALPC that allows local privilege escalationCVE-2026-87491CVE-2026-87491: a V8 sandbox escape that corrupts WebAssembly metadata to run embedded shellcode
Threat Actors
APT31The article identifies APT31 as an alias of JungleBamboo.JungleBambooProofpoint attributed BlueMoon spearphishing operations to this actor; the article identifies it as a Chinese state-sponsored actor.TA412The article identifies Tide Castle as an alias of JungleBamboo.UNK_DoubleCheckA BlueMoon-associated activity cluster reported to target Vietnamese manufacturing firms with an in-memory Rust loader.UNK_LateNightA BlueMoon-associated activity cluster reported to deploy ShadowPad against U.S. aerospace and defense-industrial-base companies.UTA0560Volexity tracked this actor in BlueMoon activity targeting NGO customers with donation lures.Violet TyphoonThe article identifies Violet Typhoon as an alias of JungleBamboo.
Malware
GemStonefor targeting NGOs in the US, mining companies, and individual high-value targets, using the Longtale/GemStone credential stealer extension disguised as Google Gemini.GRIMWEDGEis UTA0560, which targeted NGOs using donation lures and triggered an infection chain that delivered Grimwedge, an in-memory JScript backdoor for reconnaissance, file and process management, command execution, andLONGTALEis known for targeting NGOs in the US, mining companies, and individual high-value targets, using the Longtale/GemStone credential stealer extension disguised as Google Gemini.ShadowPadThe third cluster is tracked as UNK_LateNight, known for deploying the ShadowPad backdoor on systems belonging to U.S.
Vendors
GoogleMultiple cyber-espionage groups used the BlueMoon exploit kit to chain zero-day flaws in Microsoft Windows and Google Chrome for remote code execution, sandbox escape, and privilege escalation.MicrosoftMultiple cyber-espionage groups used the BlueMoon exploit kit to chain zero-day flaws in Microsoft Windows and Google Chrome for remote code execution, sandbox escape, and privilege escalation.
Products
Google ChromeMultiple cyber-espionage groups used the BlueMoon exploit kit to chain zero-day flaws in Microsoft Windows and Google Chrome for remote code execution, sandbox escape, and privilege escalation.Microsoft WindowsMultiple cyber-espionage groups used the BlueMoon exploit kit to chain zero-day flaws in Microsoft Windows and Google Chrome for remote code execution, sandbox escape, and privilege escalation.V8CVE-2026-85046: a type-confusion flaw in Chrome’s V8 JavaScript engine that provides arbitrary memory access inside the V8 sandbox
Tools
BlueMoonMultiple cyber-espionage groups used the BlueMoon exploit kit to chain zero-day flaws in Microsoft Windows and Google Chrome for remote code execution, sandbox escape, and privilege escalation.curlThe default final command uses curl to save an executable, typically a malware loader, under %TEMP% and run it.
Countries
Industries
Aerospace and defenseaerospace and defense firms, and Vietnamese manufacturers.ManufacturingA fourth group, tracked as UNK_DoubleCheck, targeted Vietnamese manufacturing firms with an in-memory Rust loader, though the final payload couldn’t be retrieved for analysis.Miningthe first Chinese state-sponsored actor observed using BlueMoon, is known for targeting NGOs in the US, mining companies, and individual high-value targets, using the Longtale/GemStone credential stealer extensionNon-governmental organizationsin campaigns from another actor it tracks as UTA0560 that targeted “customers at multiple non-governmental organizations (NGOs).”