
CYFIRMA Details Tax-Themed Malware Campaign Using VHDX Delivery and Process Injection
Summary
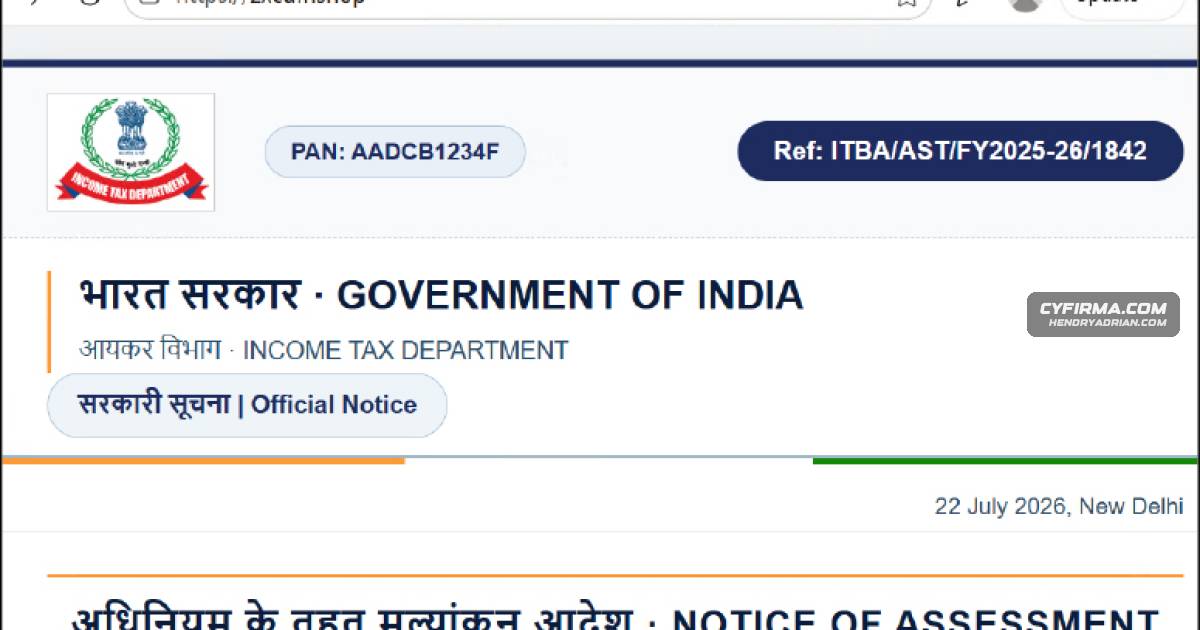
CYFIRMA reports a tax-themed campaign using ten fraudulent .shop domains to deliver a VHDX containing a loader and DLL. The malware injected into Runtimebroke.exe and attempted, unsuccessfully, to contact xvcbvgfr[.]com; no C2 session was established.
Key points
- A fake Indian Income Tax Department assessment notice lured users to download a VHDX file presented as a tax utility.
- The VHDX contained an executable loader that loaded the tedutil.dll payload from its resource section.
- The malware injected into Runtimebroke.exe and was assessed to have persistence, system discovery, and remote command execution capabilities.
- The malware attempted to connect to xvcbvgfr[.]com, resolving to 103.97.128.245, but the connection handshake did not complete and no C2 session was observed.
- Tracking recorded 1,013 visit events and 48 download events; these were not confirmed unique victims.
- CYFIRMA described the campaign as unattributed and said observed similarities to China-associated activity were insufficient to establish a link.
Article Details
- Attack Vectors
- A fake Indian Income Tax Department assessment notice directs victims to fraudulent .shop portals and prompts them to download a malicious VHDX disk image.
- Mounting the VHDX exposes a loader executable that extracts and loads tedutil.dll from its resource section.
- The malware injects into Runtimebroke.exe and attempted outbound communication over TCP/443 to xvcbvgfr[.]com; the connection handshake did not complete.
- Defensive Notes
- Block the listed fraudulent tax-themed domains and monitor the associated IP addresses and suspected C2 domain.
- Restrict mounting and execution of untrusted VHDX files; inspect disk images and files downloaded from suspicious domains.
- Monitor for the campaign’s named VHDX, executable, and DLL artifacts, as well as process injection and unusual outbound connections from RuntimeBroker.exe.
- Use URL filtering, reputation-based blocking, sandboxing, and application allowlisting; alert on unsigned or untrusted binaries executed from mounted images or user-writable locations.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | bmnjhy[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| DOMAIN | bvnbhy[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| DOMAIN | cbvfrd[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| DOMAIN | mkjiun[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| DOMAIN | nmhjnu[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| DOMAIN | sfbnhy[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| DOMAIN | ssefcv[.]shop | Fraudulent tax-themed portal used in the campaign to distribute the malicious payload. |
| DOMAIN | xvbndr[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| DOMAIN | xvcbvgfr[.]com | Suspected C2 endpoint contacted by the malware; only a TCP SYN was observed and no successful C2 session was established. |
| DOMAIN | zasxcd[.]shop | Fraudulent tax-themed portal used to host the fake assessment page and distribute the malicious VHDX. |
| DOMAIN | zxcdfr[.]shop | Fraudulent tax-themed campaign domain listed for blocking. |
| IPV4 | 103[.]59[.]103[.]170 | IP associated in the report with the fraudulent campaign domains. |
| IPV4 | 103[.]97[.]128[.]245 | Resolved address for the malware’s suspected C2 domain; the attempted connection did not complete. |
| MD5 | 2462c9ca59a40ce04e3f072a95e104f0 | MD5 hash of the malicious VHDX disk image delivered by the fraudulent portal. |
| MD5 | 69c5a70b15c886a7f9ab5449be286779 | MD5 hash of tedutil.dll, the payload loaded by the campaign’s executable loader. |
| MD5 | e347d86749a1f9e61c6e3b330c681b50 | MD5 hash of the loader executable contained in the malicious VHDX. |
| SHA256 | 518ee4c9ae0321bd4fe8616e4f195f0079c6503109d2710e80e09d1a0f1dc98f | SHA-256 sample hash identified for an artifact associated with the malware campaign. |
| SHA256 | 71d15f3c13f5b11866cf65d9cf014236a47d221155ae992d9992abccedb66cf2 | SHA-256 sample hash identified for an artifact associated with the malware campaign. |
| SHA256 | f4ae0f7c0c663e41dab28b2992f1afa9b97fe13a52f2d1fa26156554a23b99a7 | SHA-256 sample hash identified for an artifact associated with the malware campaign. |
MITRE ATT&CK
T1036 · MasqueradingThe fake tax portal and tax-utility filenames impersonate legitimate government communications and software.T1036.005 · Match Legitimate Resource Name or LocationThe embedded executable uses the original filename topoedit.exe and Topology Editor metadata to appear legitimate.T1055 · Process InjectionThe malware injects into Runtimebroke.exe to execute within another process.T1071.001 · Web ProtocolsThe malware attempted web-based communication over TCP/443 to xvcbvgfr[.]com, but the connection handshake did not complete.T1082 · System Information DiscoveryThe report attributes system-discovery capabilities to the payload.T1204.002 · Malicious FileThe lure prompts victims to download and mount a malicious VHDX, relying on user interaction to initiate execution.