cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2384 articles

Threat Research · helpnetsecurity.com

Fake GTA 6 Installer Deploys RATs, an Infostealer, and Destructive Ransomware

Huntress analyzed a fake GTA 6 ISO that installs NJRAT, DCRAT, Mercurial Grabber, and Chaos ransomware used as a wiper. Researchers say updated Windows Defender should detect it.
Sep 10, 2026
Threat Research · unit42.paloaltonetworks.com

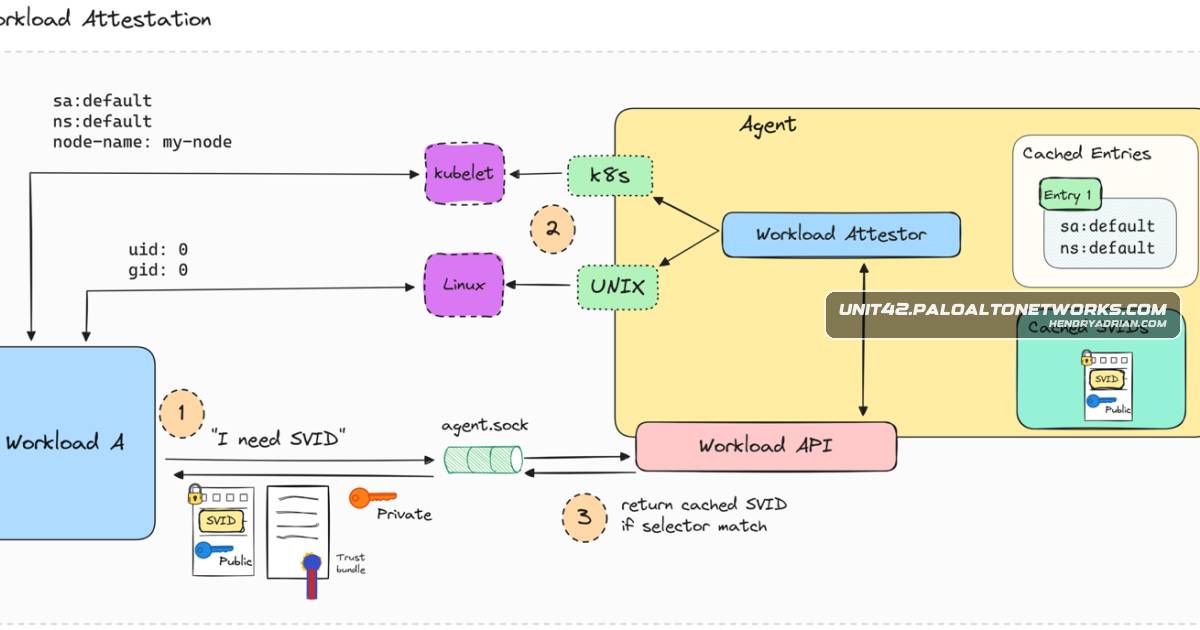
Researchers Show How Root Access on Kubernetes Nodes Can Expose SPIFFE/SPIRE Workload Identities

Unit 42 demonstrated that an attacker with root access to a Kubernetes node can spoof cgroup data to trick SPIRE into issuing co-located workloads’ identities. Its Spooffe tool automates identity enumeration; Unit 42 reports no in-the-wild exploitation.

Sep 10, 2026
Threat Research · thehackernews.com

BlueMoon Exploit Kit Chains Chrome and Windows Flaws Across Espionage Campaigns

Proofpoint reports that BlueMoon chains Chrome and Windows flaws in espionage campaigns linked to APT31 and other clusters. Attacks install varied payloads and persistence; patching Chrome does not remove existing implants.

Sep 10, 2026
Threat Research · cyberscoop.com

China-aligned Groups Use BlueMoon Chain of Three Zero-Days in Espionage Campaigns

Proofpoint reports at least four China-aligned groups used the BlueMoon chain of three unpatched browser and Windows flaws for espionage since late August, targeting organizations in the U.S. and Southeast Asia.

Sep 10, 2026
Threat Research · malwareinfo.app

Analysis Links Pension-Themed Spear-Phishing Implant to Regional Campaign, but SideWinder Attribution Remains Unproven

A password-protected pension-themed Word attachment concealed DellHeuristics.exe, whose lab activity used GitHub APIs. Its embedded IP matched an earlier regional phishing IOC, but a SideWinder link remains unproven.

Sep 10, 2026
Threat Research · huntress.com

AD RMS Root-Key Extraction Can Permanently Expose Protected Documents

The article details how an AD RMS Service Group member can extract a software-held SLC private key, decrypt documents protected by the deployment offline, and forge trusted identities. It explains detection gaps and limits of remediation.

Sep 10, 2026
Threat Research · zscaler.com

Zscaler Details SloppyRAT, a New Malware Linked to Ransomware Attacks

Zscaler ThreatLabz analyzed SloppyRAT, a malware family found in June 2026 that is likely used in ransomware-related attacks. It details the ClickFix delivery chain, malware capabilities, C2 communications, and detection guidance.

Sep 10, 2026
Threat Research · hunt.io

Hunt.io Links UK Council Attack to SonicWall SMA1000 Exploitation Campaign

Hunt.io reports a campaign exploiting CVE-2026-15409 in SonicWall SMA1000 appliances to steal LDAP credentials and Active Directory secrets. It assesses with moderate confidence that the activity is linked to a cyberattack on a UK council.

Sep 10, 2026
Threat Research · cofense.com

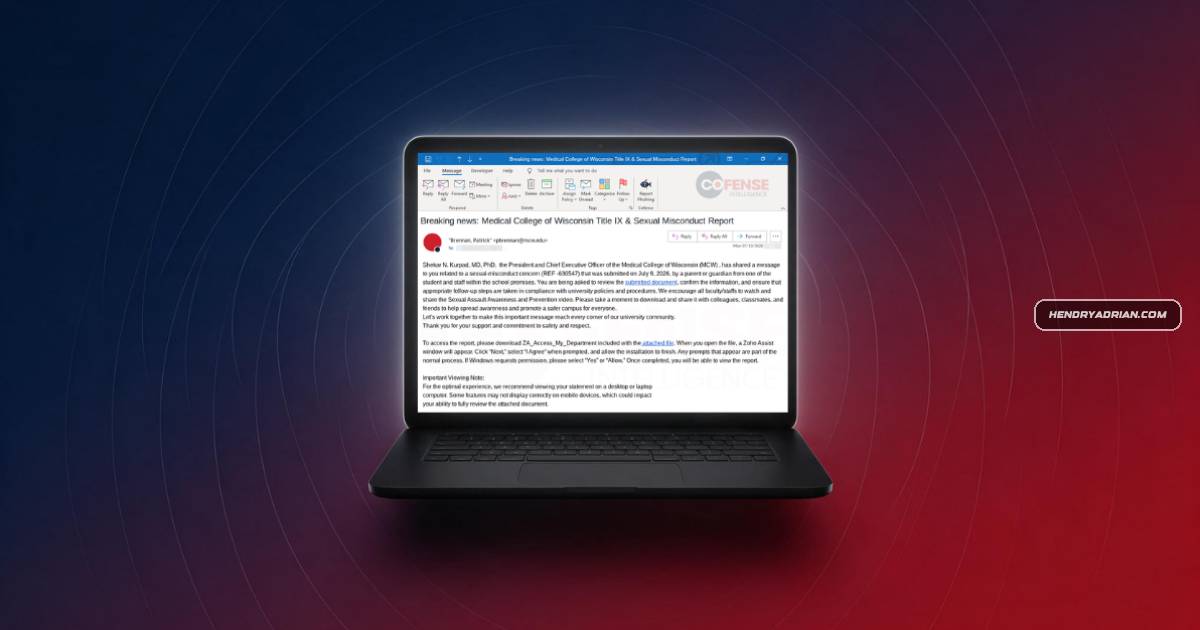
Phishing Campaign Uses Fabricated Misconduct Claims to Deliver Zoho Assist RAT

Cofense describes a phishing campaign impersonating university leaders with fabricated sexual misconduct claims. Links route victims through Google Drive to a malicious Zoho Assist download; healthcare-affiliated universities appear to be the main targets.

Sep 10, 2026
Threat Research · socket.dev

Malicious Chrome and Firefox Extensions Steal Crypto Traders’ Session and Wallet Data

Socket traced malicious browser extensions targeting Axiom Trade and Padre users. The extensions harvest authenticated session and wallet-related data and send it to attacker-controlled infrastructure.

Sep 9, 2026
Threat Research · opensourcemalware.com

OpenSourceMalware Show #20: Mini Shai-Hulud Payload Resurfaces on npm

The episode discusses four npm packages containing a Mini Shai-Hulud payload that resurfaced after 111 days, plus supply-chain threats, PolinRider’s execution method, GitHub defenses and developer precautions.

Sep 9, 2026
Threat Research · volexity.com

Volexity Details Chinese Actors’ Chrome–Windows Exploit Chain Used in Two Espionage Campaigns

Volexity reports that UTA0560 and JungleBamboo used the same Chrome–Windows exploit chain in phishing campaigns, despite a gap between Chromium fixes and Chrome releases, to deploy distinct backdoors and credential-stealing malware.

Sep 9, 2026
Threat Research · wiz.io

Researchers Detail LiteLLM Authentication Bypass, Root-Level RCE and Cloud Credential Theft

Wiz researchers found LiteLLM authentication weaknesses and exploitable attack paths to MCP access, root-level code execution, and cloud credentials. Patches are available; the MCP bypass has been observed exploited and is listed in CISA’s KEV catalog.

Sep 9, 2026
Threat Research · zimperium.com

Zimperium Details Mantax Otax Android Spyware-Ransomware

Zimperium’s zLabs details Mantax Otax v2, an Android spyware-ransomware linked to Indonesian actors. It spreads through sideloaded APKs, steals credentials and surveillance data, and mainly encrypts files on Android 9 and earlier; Firebase supports C2 and extortion.

Sep 9, 2026
Threat Research · levelblue.com

Nightmare-Eclipse PoCs Abuse Security Software and Trusted Windows Components

LevelBlue analyzes four Nightmare-Eclipse PoCs targeting Kaspersky, Avast, NVIDIA, and CrowdStrike, detailing their techniques, impacts, detection opportunities, and remediation status.

Sep 9, 2026
Threat Research · helpnetsecurity.com

Sophos Finds F5 BIG-IP APM Rootkit That Hides Web Shell in Memory

Sophos analyzed a staged rootkit on compromised F5 BIG-IP APM devices that hides a web shell in memory by intercepting Apache and PHP operations. F5 linked related activity to exploitation of CVE-2025-53521.

Sep 9, 2026
Threat Research · unit42.paloaltonetworks.com

CL-CRI-1171 Uses YouTube and SEO Lures to Distribute Three Malware Families

Unit 42 traced a pay-per-install operation using gaming videos and SEO-poisoned downloads to spread OfferLoader and deliver Insomnia RAT, ARKTunnel and Docro Hijacker. Researchers identified over 10,000 loader samples.

Sep 9, 2026
Threat Research · blog.barracuda.com

Barracuda Details Phishing Campaign That Builds Pages Inside Victims’ Browsers

Barracuda researchers describe a phishing campaign that routes victims through Microsoft services, then builds the phishing page locally with a blob URL. Service workers, sandboxed iframes and backend controls manage the workflow.

Sep 9, 2026
Threat Research · thehackernews.com

Sophos Details F5 BIG-IP Malware That Injects a PHP Web Shell Into Memory

Sophos explains how c05d5254 modifies Apache and PHP loading to inject a web shell into memory on F5 BIG-IP APM appliances, evading disk scans. It recommends checking memory, files, logs and integrity reports even after patching.

Sep 9, 2026
Threat Research · proofpoint.com

Multiple State-Aligned Threat Actors Rapidly Adopt BlueMoon Chrome and Windows Exploit Chain

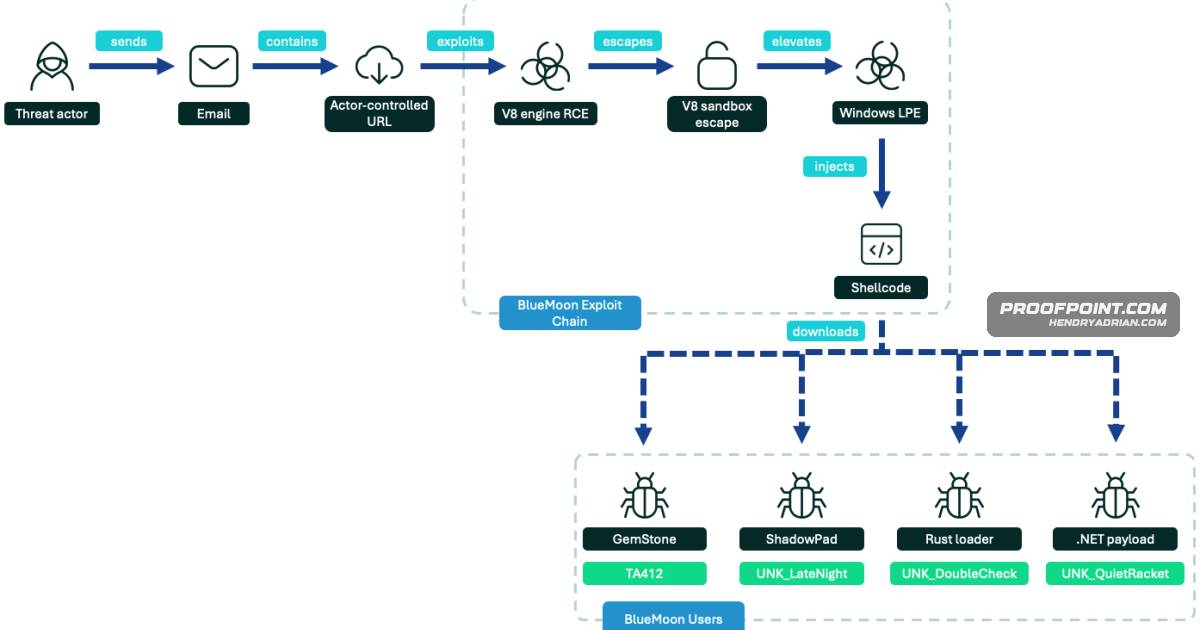
Proofpoint details BlueMoon, an exploit kit chaining Chrome and Windows vulnerabilities that multiple espionage-focused actors used in spearphishing campaigns. The report covers its exploit mechanics, payloads, targets, and detection opportunities.

Sep 9, 2026
Threat Research · seqrite.com

Analysis Details MacSync macOS Stealer’s ClickFix Delivery and Data-Theft Chain

Seqrite analyzes MacSync, a macOS MaaS stealer delivered through ClickFix lures and malvertising. The report details its native Mach-O stager, in-memory AppleScript payload, credential theft, persistence, and chunked exfiltration.

Sep 9, 2026
Threat Research · thehackernews.com

Hidden ChatGPT Prompt Could Use JFrog Artifactory to Exfiltrate Gmail and Chat Data

Check Point Research found that hidden ChatGPT instructions could use shared JFrog Artifactory metadata to relay connected Gmail data, chat history, and files between accounts. OpenAI took the internal service offline; no user update is required.

Sep 9, 2026
Threat Research · stealthmole-intelligence-hub.blogspot.com

StealthMole Traces Night Hunters’ Network and Retaliatory Operations

StealthMole traces The Night Hunters’ fragmented Telegram and social-media network, linking it to seven defacement alerts and actor-published claims of database, government and industrial-control access. The claims are not independently verified.

Sep 9, 2026
Threat Research · huntress.com

Huntress Details Worm-Like Campaign Spreading Malicious Scripts Through ScreenConnect

Huntress traced a campaign using rogue ScreenConnect clients to run staged VBScript and PowerShell payloads, persist on Windows hosts, and spread scripts to newly connected endpoints. ConnectWise fixed a related file-transfer vulnerability in ScreenConnect 26.6.5.

Sep 9, 2026
PreviousPage 25 of 100 Next
© 2026 cyber.hendryadrian.com