Fake Security Locker Uses Google Ads and Anti-Analysis Tricks to Drive Tech-Support Scams
Summary
Researchers analyzed a tech-support-scam kit delivered through Google Ads that uses anti-analysis checks and fake Windows or macOS alerts to pressure victims into calling scammers. It affected at least 619 organizations in two weeks.
Key points
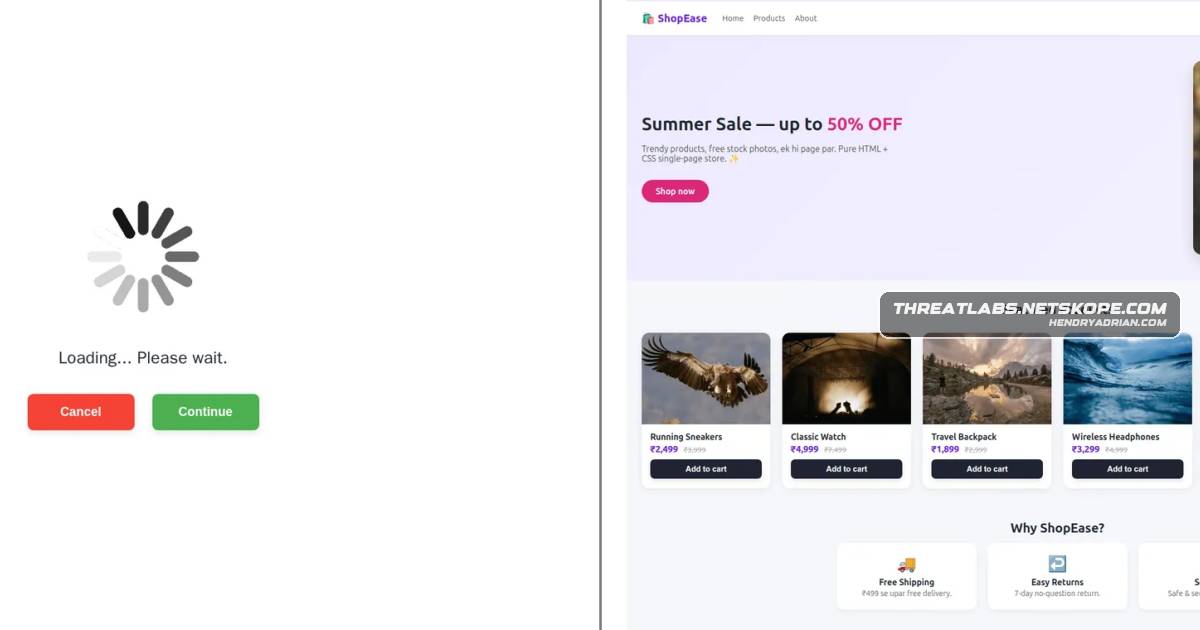
- The kit routes ad clickers through a loading page to a fake online store, then activates after detecting mouse movement to evade automated analysis.
- It decrypts a command-and-control address and an OS-specific payload in the browser; the fake locker is assembled in memory rather than downloaded as an inspectable file.
- The Windows and macOS versions impersonate trusted security alerts and claim the device is infected to pressure victims into calling a bogus support number.
- The page uses full-screen mode, hides the cursor, blocks common exit keys, and slows the browser to make the computer appear locked; operating-system controls remain usable.
- From August 31 to September 14, 2026, the campaign reached at least 619 organizations, using more than 250 Google Ads campaign IDs across at least 284 legitimate publisher sites.
- Do not call the displayed number. Exit full-screen mode by holding Escape, or force-close the browser through the operating system; Netskope says its detection identifies the kit.
Article Details
- Attack Vectors
- Victims arrive through paid Google Ads and are directed to a fake storefront page.
- After detecting a mouse movement, the kit decrypts a C2 address, retrieves an OS-specific encrypted payload, and assembles the fake security locker in browser memory.
- The locker uses a fake security alert and callback number to pressure victims into calling a bogus support line, potentially seeking payment, remote access, or personal and financial details.
- Defensive Notes
- Do not call the number shown in a fake security alert. Hold Escape to try to exit full-screen mode, then close the tab.
- If that does not work, force-close the browser using the operating system’s Task Manager on Windows or Force Quit on Mac, then reopen without restoring the previous session.
- Netskope Threat Protection detects the kit as Generic.Phishing Tech Support Scam Kit Detected.
MITRE ATT&CK
Products
Google AdsDelivery: paid Google ads at scaleMicrosoft Defender Security CenterOn Windows, it impersonates Windows Defender, with a fake “Microsoft Defender Security Center” scan claiming the machine is infected with malware, stacked system dialogs, and a callback number.Windows DefenderOn Windows, it impersonates Windows Defender, with a fake “Microsoft Defender Security Center” scan claiming the machine is infected with malware, stacked system dialogs, and a callback number.
Countries
Australiaad clicks, the United States accounts for roughly 62% of the affected organizations, Japan for 16%, and Australia for 14%, with the remainder scattered thinly across a long tail of other countries.Japanthe geography of the ad clicks, the United States accounts for roughly 62% of the affected organizations, Japan for 16%, and Australia for 14%, with the remainder scattered thinly across a long tail of other countries.United States14, 2026) the kit hit at least 619 organizations, and by the geography of the ad clicks, the United States accounts for roughly 62% of the affected organizations, Japan for 16%, and Australia for 14%, with the