Censys Finds 131 Internet-Exposed Mythic C2 Hosts, Including a Cluster Developing Custom Implants
Summary
Censys identified 131 internet-exposed Mythic hosts and analyzed their fingerprints and infrastructure. One cluster showed evidence of custom implant development and Discord-based C2; the article also outlines detection opportunities for defenders.
Key points
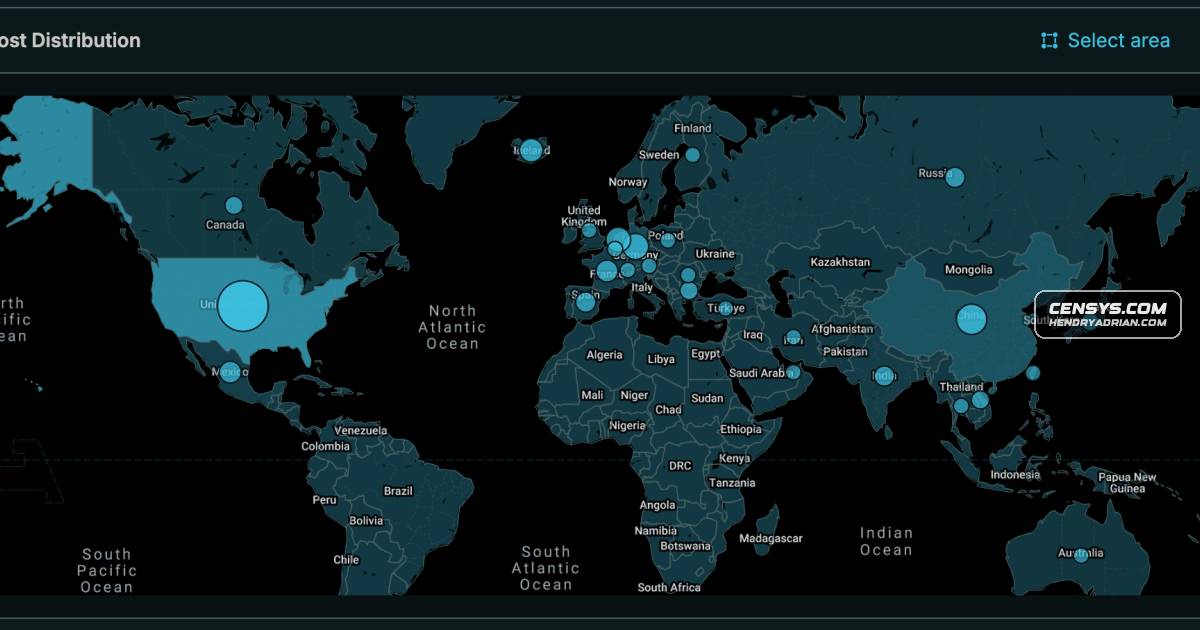
- As of September 11, 2026, Censys tracked 131 hosts exposing Mythic; 115 had default Mythic certificate subject organizations.
- Common fingerprints include a self-signed certificate identifying Mythic, the default internal certificate chain, and an HTTP 502 response on port 7443.
- Ten hosts also exposed another C2 framework, including Sliver or Adaptix C2; one multi-framework cluster appeared consistent with a lab or training fleet.
- A separate cluster used telemetry-update[.]services and exposed staged payload builds, Rust source for another implant family, and scripts indicating Discord-based C2 development.
- Censys recommends monitoring for Mythic certificate details, port 7443 connections, default internal certificate names, and unexpected Mythic Docker containers or agent behaviors.
Article Details
- Attack Vectors
- Mythic supports remote command execution and shell access through its agents.
- Mythic agents can use HTTP/HTTPS, WebSocket, TCP, SMB named pipes, and DNS transport profiles.
- The reported cluster used a Discord-based C2 transport with steganographic staging.
- The reported staging server exposed Windows PE builds of the nyx payload family, Rust source and archive files for fys2, and a /serve/ directory containing build outputs staged for victim download.
- Mythic supports SMB pipe-based agent pivoting and SOCKS proxy chaining.
- Defensive Notes
- Alert on TLS connections to servers whose certificate subject organization is O=Mythic or O=Mythic C2.
- Flag outbound connections to port 7443 on dedicated VPS or cloud IPs without a known legitimate service, particularly when the TLS certificate is self-signed.
- Monitor servers your organization communicates with for the default internal PKI names CN=operators and CN=multiplayer.
- Alert on unexpected Docker Compose deployments containing mythic_nginx, mythic_rabbitmq, or mythic_server container names.
- Look for unexpected scheduled tasks, launch agents, or systemd units that point to binaries in temporary or user directories.
- On Windows targets, monitor process injection and LSASS access from non-system processes.
- Cross-reference Censys results for Mythic hosts with egress telemetry to identify internal hosts communicating with suspected Mythic infrastructure.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | telemetry-update[.]services | Custom domain used by the reported Mythic-only cluster; the article says it was built to blend with Windows telemetry traffic. |
| IPV4 | 142[.]93[.]52[.]11 | Host in the reported Mythic-only cluster associated with the domain telemetry-update[.]services. |
| IPV4 | 170[.]64[.]183[.]242 | Host in the reported Mythic-only cluster associated with the domain telemetry-update[.]services. |
| IPV4 | 194[.]26[.]192[.]117 | Host in the reported Mythic-only cluster associated with the domain telemetry-update[.]services. |
| IPV4 | 65[.]87[.]7[.]11 | Publicly accessible staging server hosting payload builds and files staged for victim download. |
MITRE ATT&CK
T1055 · Process InjectionThe article advises monitoring for process injection and says Mythic's Apollo Windows agent uses standard injection techniques.T1056.001 · KeyloggingThe article lists agent-side keylogging as a Mythic capability.T1113 · Screen CaptureThe article lists agent-side screenshot capture as a Mythic capability.
Malware
fys2Eleven sequential Windows PE builds of a payload family named “nyx” (nyx-v5.exe through nyx-v15.exe) sit alongside Rust source for a second family, “fys2” (fys2_config.rs, fys2_src.tar.gz).nyxEleven sequential Windows PE builds of a payload family named “nyx” (nyx-v5.exe through nyx-v15.exe) sit alongside Rust source for a second family, “fys2” (fys2_config.rs, fys2_src.tar.gz).
Tools
Adaptix C2Ten of the 131 tracked hosts carry an additional C2 framework alongside Mythic: 6 also expose Sliver, 6 expose Adaptix C2, 1 exposes Havoc, and 1 exposes FRP (Fast Reverse Proxy).ApolloApollo, Mythic’s primary Windows agent, uses standard injection techniques.FRPTen of the 131 tracked hosts carry an additional C2 framework alongside Mythic: 6 also expose Sliver, 6 expose Adaptix C2, 1 exposes Havoc, and 1 exposes FRP (Fast Reverse Proxy).HavocTen of the 131 tracked hosts carry an additional C2 framework alongside Mythic: 6 also expose Sliver, 6 expose Adaptix C2, 1 exposes Havoc, and 1 exposes FRP (Fast Reverse Proxy).MythicMythic is an open-source collaborative C2 framework which is actively maintained on GitHub.SliverTen of the 131 tracked hosts carry an additional C2 framework alongside Mythic: 6 also expose Sliver, 6 expose Adaptix C2, 1 exposes Havoc, and 1 exposes FRP (Fast Reverse Proxy).
Countries
ChinaGeolocation: The United States accounts for 42 hosts (32%), followed by Hong Kong (11 hosts, 8%), China (10 hosts, 8%), Germany (7 hosts, 5%), Mauritius (7 hosts, 5%), the Netherlands and Singapore (6 each).GermanyGeolocation: The United States accounts for 42 hosts (32%), followed by Hong Kong (11 hosts, 8%), China (10 hosts, 8%), Germany (7 hosts, 5%), Mauritius (7 hosts, 5%), the Netherlands and Singapore (6 each).Hong KongGeolocation: The United States accounts for 42 hosts (32%), followed by Hong Kong (11 hosts, 8%), China (10 hosts, 8%), Germany (7 hosts, 5%), Mauritius (7 hosts, 5%), the Netherlands and Singapore (6 each).IcelandIceland’s 1984 ehf (AS 1984) hosts 5 servers.MauritiusMauritius Telecom (ASN 23889) accounts for 7 hosts across two adjacent cities: Beau Bassin-Rose Hill (3 hosts) and Quatre Bornes (4 hosts).NetherlandsGeolocation: The United States accounts for 42 hosts (32%), followed by Hong Kong (11 hosts, 8%), China (10 hosts, 8%), Germany (7 hosts, 5%), Mauritius (7 hosts, 5%), the Netherlands and Singapore (6 each).SingaporeGeolocation: The United States accounts for 42 hosts (32%), followed by Hong Kong (11 hosts, 8%), China (10 hosts, 8%), Germany (7 hosts, 5%), Mauritius (7 hosts, 5%), the Netherlands and Singapore (6 each).United StatesGeolocation: The United States accounts for 42 hosts (32%), followed by Hong Kong (11 hosts, 8%), China (10 hosts, 8%), Germany (7 hosts, 5%), Mauritius (7 hosts, 5%), the Netherlands and Singapore (6 each).