China-Linked Actors Use Chrome-Windows Exploit Chain to Deploy GRIMWEDGE and LONGTALE
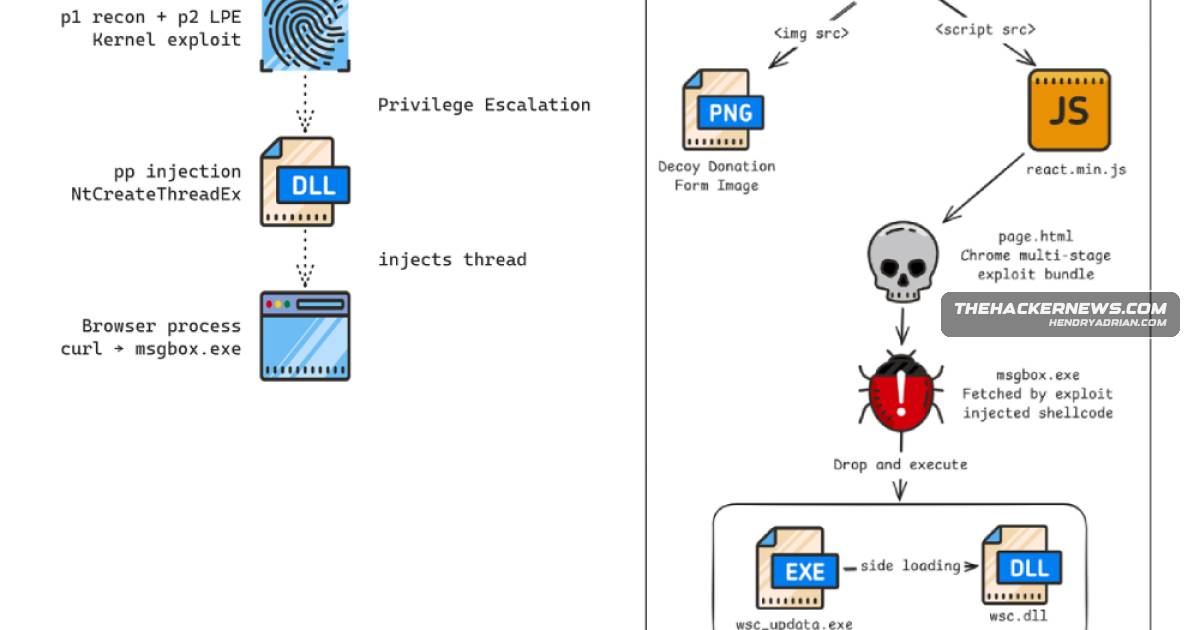
Summary
Volexity reports that UTA0560 used spear-phishing and a Chrome-Windows exploit chain to deliver GRIMWEDGE to NGOs, while JungleBamboo used the chain to deploy SUPERSTOMP and the LONGTALE credential-stealing extension.
Key points
- UTA0560 targeted NGOs with spear-phishing on September 1, 2026, directing recipients through a university website with a reflected XSS flaw to attacker-controlled infrastructure.
- The reported chain combined CVE-2026-85046 and CVE-2026-87491 in Chrome with CVE-2026-85880 in Windows to escape the browser sandbox and execute code.
- UTA0560 delivered GRIMWEDGE through a loader and DLL sideloading chain; the backdoor supports reconnaissance, file and process operations, command execution, and payload delivery.
- GRIMWEDGE communicated with ocr[.]opusaccel[.]top. Researchers said it lacked built-in persistence, lateral movement, and exfiltration beyond file-read and upload commands.
- Volexity also observed JungleBamboo, also known as APT31, using the chain to deploy SUPERSTOMP and LONGTALE, a Chrome extension with credential- and session-theft capabilities.
- The article reports a patch gap: fixes for the two Chrome flaws were in Chromium but not yet in a stable Chrome release, creating a window in which the flaws remained exploitable in Chrome.
Article Details
- Attack Vectors
- UTA0560 sent spear-phishing emails to NGO users with links to a university website vulnerable to reflected cross-site scripting; the page redirected recipients to attacker-controlled infrastructure hosting a Chrome-Windows exploit chain.
- The exploit chain used CVE-2026-85046 for arbitrary read/write in the V8 sandbox, CVE-2026-87491 to escape the browser sandbox, and CVE-2026-85880 to inject code into the Chrome process and achieve code execution.
- The chain delivered Base64-embedded shellcode and an executable loader that extracted a legitimate Windows binary and malicious wsc.dll, initiating a DLL sideloading chain.
- The loader and DLL fetched a hostname-named text file containing an MSI installer that executed an obfuscated JavaScript backdoor.
- JungleBamboo (APT31) used the same exploit chain to deploy SUPERSTOMP, which installed the LONGTALE credential-stealing Chrome extension from a remote server.
- Defensive Notes
- Apply the relevant Chrome and Windows security fixes; the article reports a gap between fixes entering the Chromium codebase and their inclusion in a stable Google Chrome release.
- Investigate spear-phishing links to sites vulnerable to reflected XSS, suspicious Chrome exploit-page activity, msgbox.exe, wsc.dll, unexpected MSI execution, and unauthorized Chrome extensions.
- Monitor for GRIMWEDGE C2 polling and command activity, including file reads and uploads, and for LONGTALE behavior such as keylogging, form capture, cookie and session theft, screenshots, and bulk data exfiltration.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ocr[.]opusaccel[.]top | C2 domain polled by the GRIMWEDGE backdoor for commands. |
MITRE ATT&CK
T1005 · Data from Local SystemGRIMWEDGE can read files on the compromised host.T1041 · Exfiltration Over C2 ChannelGRIMWEDGE supports uploading files to the C2 server; LONGTALE sends stolen information to its C2.T1055 · Process InjectionThe exploit chain used shellcode for browser-process injection.T1056.001 · KeyloggingLONGTALE captures keystrokes and form input.T1057 · Process DiscoveryGRIMWEDGE can enumerate running processes using its Tasklist command.T1059 · Command and Scripting InterpreterGRIMWEDGE's Run command executes commands in a hidden window.T1059.007 · JavaScriptGRIMWEDGE is an obfuscated JavaScript backdoor whose commands execute in memory through eval().T1083 · File and Directory DiscoveryGRIMWEDGE can retrieve directory listings and read files.T1113 · Screen CaptureLONGTALE captures screenshots by monitoring page content for C2-supplied keywords.T1189 · Drive-by CompromiseThe exploit chain was reached through a link to a university website with a reflected XSS flaw.T1203 · Exploitation for Client ExecutionThe actors exploited Chrome and Windows vulnerabilities to execute code on the victim systems.T1539 · Steal Web Session CookieLONGTALE steals browser cookies and session data.T1547 · Boot or Logon Autostart ExecutionNot selected: the researchers said GRIMWEDGE has no built-in persistence.T1566.001 · Spearphishing AttachmentUTA0560 used spear-phishing emails containing links to initiate the infection.T1574.002 · DLL Side-Loadingmsgbox.exe extracted a legitimate Windows binary and malicious wsc.dll to initiate DLL sideloading.
CVE
CVE-2026-85046The chain combined CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880 to run code in Chrome and Windows.CVE-2026-85880The chain combined CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880 to run code in Chrome and Windows.CVE-2026-87491The chain combined CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880 to run code in Chrome and Windows.
People
Threat Actors
APT31Alternate name given in the article for JungleBamboo, which used the exploit chain to deploy SUPERSTOMP and LONGTALE.JungleBambooThreat actor reported using the Chrome-Windows exploit chain to deploy SUPERSTOMP and LONGTALE; the article identifies APT31 as an alternate name.UTA0560Volexity-tracked threat cluster that targeted NGOs with spear-phishing and deployed GRIMWEDGE.
Malware
GRIMWEDGEA Chinese threat actor tracked as UTA0560 used spear-phishing and a Chrome-Windows exploit chain to deliver the GRIMWEDGE JavaScript backdoor to NGOs.LONGTALEAround the same time, JungleBamboo (APT31) used the same chain to deploy SUPERSTOMP and the LONGTALE credential-stealing Chrome extension.SUPERSTOMPAround the same time, JungleBamboo (APT31) used the same chain to deploy SUPERSTOMP and the LONGTALE credential-stealing Chrome extension.
Vendors
Products
Google ChromeA Chinese threat actor tracked as UTA0560 used spear-phishing and a Chrome-Windows exploit chain to deliver the GRIMWEDGE JavaScript backdoor to NGOs.Google GeminiIt masquerades as a Google Gemini Chrome extension (ID: ckiknalbeplpcpofpnabcnhjcegckfei) to evade detection, while supporting the following features –Microsoft WindowsA Chinese threat actor tracked as UTA0560 used spear-phishing and a Chrome-Windows exploit chain to deliver the GRIMWEDGE JavaScript backdoor to NGOs.