PoeLLM Botnet Hides C2 Address in GitHub Poem, Infecting More Than 3,400 Servers
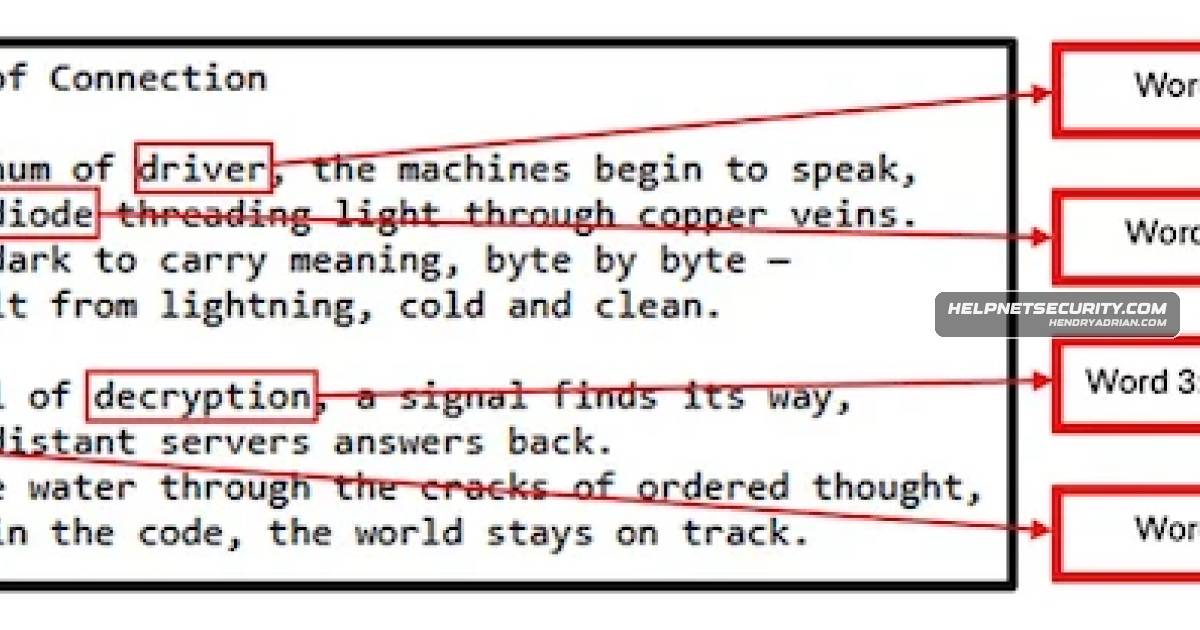
Summary
Black Lotus Labs says the PoeLLM campaign has compromised over 3,400 servers since April 2026, using a GitHub poem to encode C2 addresses and infected systems to mine cryptocurrency and scan for new targets.
Key points
- PoeLLM retrieves its C2 address by translating four words in a poem hosted on GitHub; edits to the poem redirect infected systems to new servers.
- The Canto Incognito campaign has compromised more than 3,400 servers since April 2026, mostly in the US and Western Europe.
- Victims include exposed LiteLLM, Ollama, Gotenberg, and Gitea services; the malware uses crafted requests to make vulnerable servers download its payload.
- The analyzed LiteLLM endpoint is associated with CVE-2026-42271, a command injection vulnerability.
- Infected systems run XMRig and Iron cryptocurrency miners connected to the Kryptex mining pool, and scan for and exploit additional targets.
- Bots have also begun targeting SSH ports and other login portals, which researchers say may indicate early testing of distributed brute-force attacks.
- Black Lotus Labs says it has blocked traffic to and from PoeLLM C2 servers and will continue monitoring.
Article Details
- Attack Vectors
- PoeLLM targets exposed, vulnerable LiteLLM, Ollama, Gotenberg, and Gitea services. An exploit server sends a crafted POST request instructing a vulnerable server to download a file from the C2 server.
- The analyzed sample references the LiteLLM endpoint /mcp-rest/test/connection, associated in the article with CVE-2026-42271.
- Infected systems use HTTP/S scanning and exploit deployment to find and compromise additional targets.
- Bots have recently targeted SSH ports and other login portals; researchers say this may indicate early-stage testing of distributed brute-force attacks.
- Defensive Notes
- Black Lotus Labs says it blocked traffic to and from PoeLLM C2 servers and is monitoring for new traffic.
- Researchers advise updating internet-facing AI and enterprise tools and incorporating AI tools into attack-surface management and patch and update cycles.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 5[.]78[.]73[.]122 | Dedicated server contacted by a compromised Ivanti Sentry victim and identified as a PoeLLM C2. |
| IPV4 | 92[.]119[.]165[.]74 | Earlier PoeLLM C2 address decoded from words in the GitHub poem. |
MITRE ATT&CK
T1110 · Brute ForceResearchers say bots may be testing distributed brute-force attacks against SSH ports and other login portals.T1496 · Resource HijackingPoeLLM uses infected servers to mine cryptocurrency.T1595 · Active ScanningInfected servers scan the internet for potential victims, including services on ports 3000 and 4000.
CVE
CVE-2026-10520The team first came across PoeLLM while looking into an Ivanti Sentry vulnerability (CVE-2026-10520).CVE-2026-42271In the sample Black Lotus Labs analyzed, the targeted LiteLLM endpoint (/mcp-rest/test/connection) is referenced in CVE-2026-42271, a command injection vulnerability in LiteLLM.