Signed Loader Unpacks Cobalt Strike Beacon That Masquerades as CrowdStrike Traffic
Summary
Analysis of a signed Windows loader found it unpacks a Cobalt Strike Beacon configured to imitate CrowdStrike traffic. The Beacon did not contact its server in the sandbox, and delivery method and operational context remain unknown.
Key points
- The 1.1 MB Windows executable was signed through Microsoft Trusted Signing with a certificate issued to an individual that was valid for three days; the certificate was reported to Microsoft.
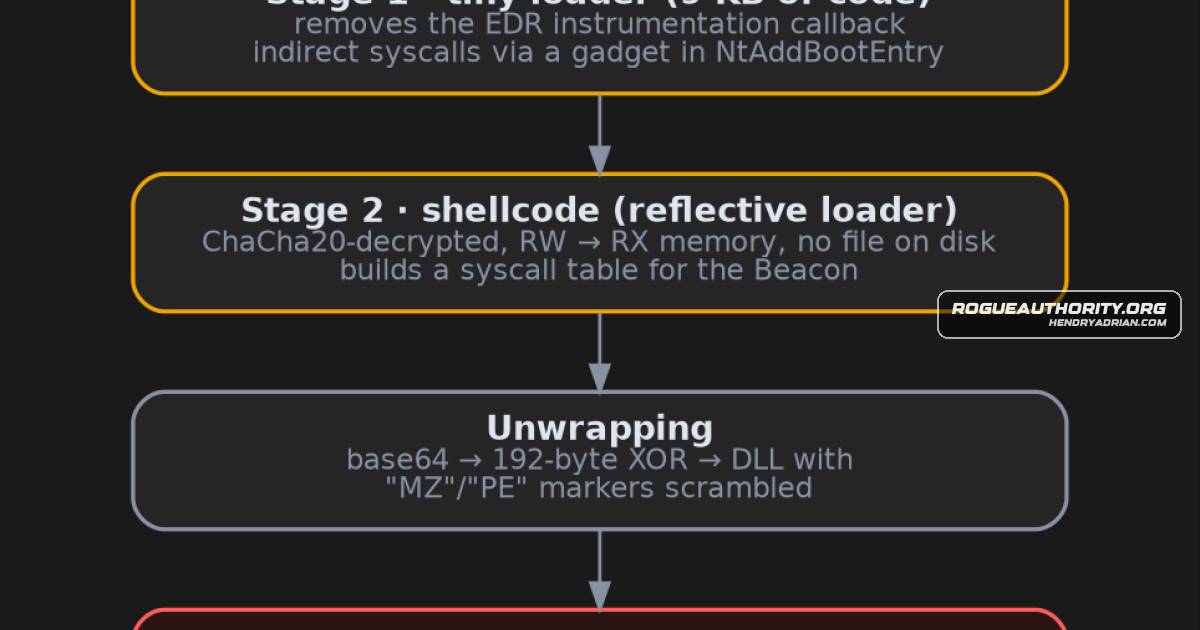
- A small loader decrypts shellcode, which reflectively loads a Cobalt Strike Beacon into memory.
- The loader uses timing delays, clears an instrumentation callback, and uses indirect system calls; the payload also scrambles PE header markers.
- The Beacon is configured to mimic CrowdStrike Falcon traffic, including its user agent, headers, cookie, and API-style paths, while targeting an Azure hostname: asiioasdjasiojasodijasa[.]eastus[.]cloudapp[.]azure[.]com.
- Sandbox analysis found the Beacon in memory, but it did not load required networking libraries or resolve its configured server; the authors did not determine why.
- The authors do not know how the file was delivered or whether it was used in an authorized exercise or an intrusion, and they did not contact the server.
- Defender suggestions include alerting on CrowdStrike-like headers sent to non-CrowdStrike destinations and monitoring unusual msiexec.exe -Embedding activity.
Article Details
- Attack Vectors
- A signed Windows loader decrypts shellcode, which reflectively loads a Cobalt Strike Beacon DLL in memory.
- The loader uses timing delays, clears an instrumentation callback, and uses indirect system calls to evade analysis and security monitoring.
- The Beacon is configured to disguise its C2 traffic as CrowdStrike Falcon activity, using CrowdStrike-style headers, a user agent, and API-like URIs.
- Defensive Notes
- Alert when the CrowdStrike user agent or X-CS-AGENTID header is sent to infrastructure other than CrowdStrike's real cloud.
- Monitor for msiexec.exe -Embedding launched by an unusual parent process.
- Block or monitor the reported certificate serial and malware hashes.
- Treat newly issued Microsoft Trusted Signing certificates issued to individuals with extra caution; a valid signature does not establish that a program is safe.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | asiioasdjasiojasodijasa[.]eastus[.]cloudapp[.]azure[.]com | Configured C2 hostname for the Beacon; the analysis says it did not resolve or connect to it, and its current status is unknown. |
| SHA256 | 2d2bcc28d4d6bdb4cdf160191b153d5f346cb6aa7ce0b8467c4166c5707dcdc7 | SHA-256 hash of the decrypted shellcode used by the loader. |
| SHA256 | 40ac4220748b54e62402fd428b76ce7467e3ee96af7375b13953ad188f42fc92 | SHA-256 hash of the signed loader identified in the analysis. |
| SHA256 | c040aff434f2201cac1c240f97315a09d32ce9e03bbb7b8f38b3c534f7455f35 | SHA-256 hash of the Cobalt Strike Beacon DLL with its headers restored. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe loader encrypts a large embedded blob, and the payload uses nested encoding and XOR wrapping with deliberately scrambled PE header markers.T1036 · MasqueradingThe Beacon's user agent, headers, cookie, URIs, and upload content are configured to imitate CrowdStrike Falcon traffic.T1055 · Process InjectionThe Beacon configuration specifies msiexec.exe -Embedding as the sacrificial process for post-exploitation jobs; the article does not say process injection was observed.T1105 · Ingress Tool TransferThe Beacon configuration includes uploads to its C2 using CrowdStrike-themed paths; the article notes that this traffic was configured but not observed.T1497.003 · Time Based ChecksThe loader runs a short busy loop measured with high-precision timers, which the article says can trip up emulators.T1562.001 · Disable or Modify ToolsThe loader clears its process's instrumentation callback, which the article describes as a way to interfere with security-product monitoring.T1620 · Reflective Code LoadingThe shellcode reflectively loads the Beacon DLL directly into memory without writing it to disk.
People
Malware
Vendors
Products
CrowdStrike FalconThe Beacon’s network traffic is designed to look like CrowdStrike Falcon talking to its cloud: a CrowdStrike user agent, CrowdStrike-style headers and /api/v2/crowdstrike/...Level RMMThe export name levelagent.exe might be aimed at users of the Level RMM product.Microsoft Trusted SigningThis file is signed through Microsoft Trusted Signing under the name of a private individual.
Tools
1768.pyTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.ANY.RUNTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.capaTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.capstone/objdumpTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.MalcatTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.pefileTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.pycryptodomeTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.PythonTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.speakeasyTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.Triage sandboxTools used: Malcat, capstone/objdump, Python (pefile, pycryptodome), capa, Didier Stevens’ 1768.py, speakeasy, the ANY.RUN sandbox and Triage sandbox.