Midnight Mimosa Malware Preinstalled on Android Phones Enables Ad Fraud and Proxy Botnets
Summary
Bitdefender researchers detail Midnight Mimosa, malware preinstalled on low-cost Android devices that silently deploys payloads for ad fraud and proxy botnets. They also found related apps on Google Play and observed the campaign on thousands of devices.
Key points
- A persistent, platform-signed system app is embedded in affected device firmware and cannot be removed through normal app controls.
- The enabler silently installs and removes payloads, grants permissions, loads remote code, and disables Google Play Protect during installs.
- Payloads generate hidden ad impressions and clicks; another component enrolls devices as residential-proxy relays that could support botnets.
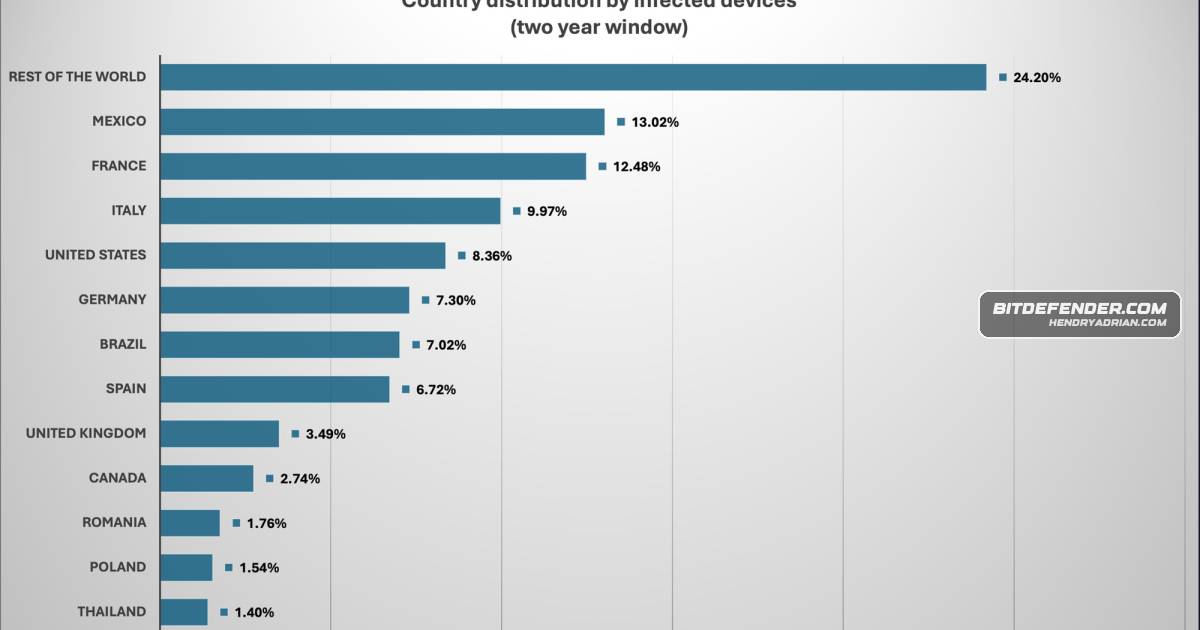
- Researchers observed the campaign on thousands of devices across more than 150 countries and found 13 related apps on Google Play.
- Package names and signing certificates vary; researchers recommend identifying the shared malware core rather than relying on package-name blocklists.
- Because the root component resides in the system partition, remediation may require firmware cleanup or disabling it through ADB; the researchers say most owners cannot remove it normally.
Article Details
- Attack Vectors
- A platform-signed system application ships preinstalled in affected Android firmware and can silently install or remove applications and grant permissions. The point of malware integration in the supply chain remains unknown.
- The native library decrypts an embedded framework, which retrieves remotely controlled DEX/JAR plugins containing installation, ad-fraud and proxyware functionality.
- Disguised cover applications generate hidden advertisements, synthetic clicks and fabricated conversion events through legitimate advertising SDKs.
- A bundled fake app-lock application enrolls devices as remotely controlled TCP relay nodes. No relay traffic was observed during the reported dynamic test.
- Thirteen genuine Google Play-distributed applications carry the same ad-fraud family markers and communicate with the same infrastructure.
- Plugins temporarily disable Google Play Store during payload installation. Some enabler samples also falsely record Google Play as their installer.
- Defensive Notes
- Detect shared native/framework markers and malicious infrastructure rather than relying only on rotating package names or signing certificates.
- Behavioral monitoring can identify repeated sensitive-access changes and silent installation or removal of unrelated applications.
- Do not trust the recorded installer field alone: the article recommends checking the Play-applied frosting signature block when evaluating claimed Google Play provenance.
- Normal uninstallation cannot remove the preinstalled system component. The article identifies firmware-level cleanup or disabling the component through ADB as remediation options, while noting their practical difficulty for typical owners.
- Accessibility, Notification Access and SMS permissions were available, but the researchers did not observe their use during analysis; capability should not be reported as demonstrated abuse.
- The article's erratum identifies 85.17.70.38 as a sinkhole, correcting its earlier classification as a live C2 server.
- Certificates bearing Shenzhen Zediel's name establish a technical signing relationship, not proof that the certificate owner authored, distributed or knew about the malware.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 0aa0cf0637d66c0d[.]com | Domain pool used to construct proxyware control hosts; the observed resolved IP was subsequently identified as a sinkhole. |
| DOMAIN | 442fe7151fb1e9b5[.]com | Domain pool used to construct rotating EnLoaderLib proxyware control hosts. |
| DOMAIN | 5[.]ahd187[.]com | Infrastructure listed for the Midnight Mimosa cluster in the operator-lineage table. |
| DOMAIN | aa86a52a98162b7d[.]com | Domain pool used to construct EnLoaderLib proxyware control hosts. |
| DOMAIN | api[.]weatherlive[.]world | Shared module-control C2 identified across enabler-family samples. |
| DOMAIN | cgb[.]jingongbuxiao[.]com | Historical Android.Phantom.5 and Android.Click.429.origin infrastructure listed in the lineage table. |
| DOMAIN | fyapi[.]freeflightbird[.]com | Infrastructure listed for the Android.Phantom.5 and Android.Click.429.origin lineage. |
| DOMAIN | newsadapi[.]zhuifengzhe[.]top | Infrastructure listed for the Android.Phantom.5 and Android.Click.429.origin lineage. |
| DOMAIN | oss[.]showtimetool[.]com | Payload module and asset distribution host; modules are served as PNG files. |
| DOMAIN | v46wd6uramzkmeeo[.]in | Domain pool used to construct EnLoaderLib proxyware control hosts. |
| DOMAIN | weatherlive[.]world | Infrastructure receiving fabricated ad interaction events. |
| DOMAIN | zhuifengzhe[.]top | Historical Android.Joker infrastructure listed in the lineage table. |
| HOSTNAME | oeawmfedpcleaih9[.]apple[.]0aa0cf0637d66c0d[.]com | Proxyware control hostname used during dynamic testing; its resolved IP was subsequently identified as a sinkhole. |
| HOSTNAME | oeawmfedpcleaih9[.]apple[.]442fe7151fb1e9b5[.]com | Rotating proxyware control hostname observed on a subsequent connection attempt. |
| IPV4 | 120[.]78[.]215[.]151 | Embedded-framework crash C2 at port 80, path /api/bugLog. |
| IPV4 | 39[.]96[.]8[.]180 | DX/S1 framework bug-report C2 at port 9008, path /ssc/rprt/bug. |
| MD5 | 0377ca97ac0ca35f9134052fede67a81 | Malware sample listed in the article's full sample set. |
| MD5 | 05ae89e761a890fa24f80f4be7263651 | Malware sample listed in the article's full sample set. |
| MD5 | 079298a7a506b376def4f4ff9a250672 | Malware sample listed in the article's full sample set. |
| MD5 | 08d231c6a5303e543eb60d4181f6a4ea | Bundled com.mobile.applock.en proxyware payload. |
| MD5 | 0903d7fd3e1d4a599a7eb3c5d356779b | Enabler-family com.android.weiapps sample with forged Google Play installation provenance. |
| MD5 | 0a26a9d5f7ab91cb5eed852cf83ef078 | Malware sample listed in the article's full sample set. |
| MD5 | 0b0d8e995e6ff24d4e9d00417446c25e | Malware sample listed in the article's full sample set. |
| MD5 | 0b8d3cd264c191f4884a25d0cc5318b5 | Malware sample listed in the article's full sample set. |
| MD5 | 1150da1af88729e54a34b8da5a2741c7 | Malware sample listed in the article's full sample set. |
| MD5 | 1414d4ef2d1191080abc59a407dcb6c5 | Malware sample listed in the article's full sample set. |
| MD5 | 145b806282d247441751bb4957b71606 | com.audify.editor.pro payload installed by the enabler. |
| MD5 | 1da42505f1c83959c7f901f5139a158e | Malware sample listed in the article's full sample set. |
| MD5 | 20108557cacd24263e7e611afc327801 | Malware sample listed in the article's full sample set. |
| MD5 | 20cefb2c667f945d482daded7e698eea | Malware sample listed in the article's full sample set. |
| MD5 | 250205ee4b8de59e60c745856f439608 | Enabler-family com.android.non.szcz sample with forged Google Play installation provenance. |
| MD5 | 254bc5f6f81de1f3c47534e6febaf023 | Malware sample listed in the article's full sample set. |
| MD5 | 294ab3f586d76772ae89add417cf6324 | Malware sample listed in the article's full sample set. |
| MD5 | 2b784622422f4280e0b3e38b30dd87bc | Binary-confirmed com.android.sys.gmsprot enabler variant. |
| MD5 | 2b7f1a7d5f5515c05d0c8e3857155ae2 | Malware sample listed in the article's full sample set. |
| MD5 | 2c77653b889dfccd649b82446f8c0d1b | Malware sample listed in the article's full sample set. |
| MD5 | 2de346602433cdd1668f36b2e9db0be1 | Malware sample listed in the article's full sample set. |
| MD5 | 31b3280f1c0836c39c470932cf6c3e6f | Malware sample listed in the article's full sample set. |
| MD5 | 33b2d3ec9a35cfb0b5a5d7b24ce4140e | Malware sample listed in the article's full sample set. |
| MD5 | 345057421c7d9ac2b671c47449f35030 | Malware sample listed in the article's full sample set. |
| MD5 | 36deebfcda4012d18706cd170c1edf1f | Malware sample listed in the article's full sample set. |
| MD5 | 36f9e8cf47a28f9803fba427cf02a25c | Malware sample listed in the article's full sample set. |
| MD5 | 37f18a20b9cf32e6f07450e903eaad7c | Malware sample listed in the article's full sample set. |
| MD5 | 387f7af167530486adcf3d8546063462 | Malware sample listed in the article's full sample set. |
| MD5 | 3b20edff1125e146aa3d5153708b58f4 | appicon.diy.tools.prop payload installed by the enabler. |
| MD5 | 3b35d3c5667136134b20a8411803c97d | Malware sample listed in the article's full sample set. |
| MD5 | 3bb270d4927e2a8385793d9084a92fd3 | Malware sample listed in the article's full sample set. |
| MD5 | 3bc159537c909fa86bcc55eda127b5aa | Malware sample listed in the article's full sample set. |
| MD5 | 3c098465af131141996ff840bd34e791 | Malware sample listed in the article's full sample set. |
| MD5 | 3d3358b1057b1bfbd7e60577d8a31e0c | Malware sample listed in the article's full sample set. |
| MD5 | 42a9f64e75911c167ec7a163e8b24920 | Malware sample listed in the article's full sample set. |
| MD5 | 4507363415e7dc6d2cab14eeed137f6c | Malware sample listed in the article's full sample set. |
| MD5 | 4521a5bbe0f33a15da86bd80ff5d6d9c | Malware sample listed in the article's full sample set. |
| MD5 | 4a171f62d1bab01827b06ae73d4caafa | Bundled com.mobile.applock.wt ad-fraud and remote-code-loading payload. |
| MD5 | 4e46549122c0236307c5eef8891466f5 | Malware sample listed in the article's full sample set. |
| MD5 | 4f7d3c5859100d65ff02449884841b9c | Malware sample listed in the article's full sample set. |
| MD5 | 50e9cdc3ed145bbc688356eda07f8eb3 | Malware sample listed in the article's full sample set. |
| MD5 | 512a6db4a22244272826f39da020fb44 | Malware sample listed in the article's full sample set. |
| MD5 | 5400ffac371c5e5c9b7f3705ce9faca5 | Malware sample listed in the article's full sample set. |
| MD5 | 542ab80429ec42e8643dc645f58b716c | com.dmstudio.weather cover application installed by the enabler. |
| MD5 | 5b3a49938f455d1197736971c4c07228 | Malware sample listed in the article's full sample set. |
| MD5 | 5d29e9b24708c3ec36d1d59036124838 | Malware sample listed in the article's full sample set. |
| MD5 | 60bc23d3d453f258e2c4ca421cd086a9 | Malware sample listed in the article's full sample set. |
| MD5 | 61aac6a98abd6dcff0dc41bb88159786 | Enabler-family com.android.sys.dts sample with forged Google Play installation provenance. |
| MD5 | 642d84ed5660407b972f1df642acb192 | Malware sample listed in the article's full sample set. |
| MD5 | 66c6512b9a73425aba40c8bfa95d23a0 | Malware sample listed in the article's full sample set. |
| MD5 | 6739fe083cfa8dec9b4f989ccba0e99e | com.dl.guard.lock payload installed by the enabler. |
| MD5 | 6aca76699ec0bb8e51372d5c68c8359b | Malware sample listed in the article's full sample set. |
| MD5 | 6df909898f5f1394e78508d1152fab38 | Malware sample listed in the article's full sample set. |
| MD5 | 6ee2be3e5558085b532dacc8db61f3e9 | Malware sample listed in the article's full sample set. |
| MD5 | 6eea0568d5cc776ae03e09149cec3cd8 | Malware sample listed in the article's full sample set. |
| MD5 | 7322d8a65a56a7ab09f4d526cb343e3d | Malware sample listed in the article's full sample set. |
| MD5 | 7400c34f7c6f866499029f5e759f58bd | Malware sample listed in the article's full sample set. |
| MD5 | 7469c9c06e5f324ca608e0140156bbad | Malware sample listed in the article's full sample set. |
| MD5 | 765d3ce85a6393d05973c4cfa7738116 | Malware sample listed in the article's full sample set. |
| MD5 | 7f7747575980098bdc98e7b7aa362697 | Malware sample listed in the article's full sample set. |
| MD5 | 815b910f1efc95f38ba0c5b12c4f2129 | Malware sample listed in the article's full sample set. |
| MD5 | 836739fe7196437d8e998245b6f2b3b4 | Malware sample listed in the article's full sample set. |
| MD5 | 838dc8fcde1b28171e404ece1cfcde44 | Malware sample listed in the article's full sample set. |
| MD5 | 879168159c155758dbfd7a76e8f21548 | Malware sample listed in the article's full sample set. |
| MD5 | 8ec360829f4f7ae8dcae47c02b996762 | Malware sample listed in the article's full sample set. |
| MD5 | 90e0d27d808105167fdaa3a22b918217 | Malware sample listed in the article's full sample set. |
| MD5 | 92390cacdd20d2ee5405093669e7302c | com.solide.filemanager.lte payload installed by the enabler. |
| MD5 | 92f2fd8bcccc8ec4ffa64c7f6b3b9b8d | Malware sample listed in the article's full sample set. |
| MD5 | 998e9010e5dfc4e4645f5572cbbe5b53 | Malware sample listed in the article's full sample set. |
| MD5 | 9a3d04aa36654b5c4b21edd22e46f92d | Malware sample listed in the article's full sample set. |
| MD5 | 9a46098de785ae732e5fced55a2f3063 | Malware sample listed in the article's full sample set. |
| MD5 | 9e7b34e63d8d38e37667f88a945ae69a | Malware sample listed in the article's full sample set. |
| MD5 | 9f1e2249003ab22cf8a38048e0ff6f6c | Malware sample listed in the article's full sample set. |
| MD5 | a02f28387527abe90d73d2879f671972 | Malware sample listed in the article's full sample set. |
| MD5 | a13af0174bc211709e8b73bf60492a17 | Malware sample listed in the article's full sample set. |
| MD5 | a147cd8f72aadfcf78f7723db6813e86 | Malware sample listed in the article's full sample set. |
| MD5 | a57a1ba15364dfb35d334f644d7049e8 | Malware sample listed in the article's full sample set. |
| MD5 | a8847b68428fde206b6dff8001051f92 | Native malware core libeasy.so, which decrypts and drops cn.kw.lib.hex. |
| MD5 | aac942aaf6ec0773cbac87fde4a6b284 | Malware sample listed in the article's full sample set. |
| MD5 | ab8d6be686ca9413e27a11e85f9cef1a | Malware sample listed in the article's full sample set. |
| MD5 | abe12db77a62ecb99d6ab5dc4fff18c7 | Malware sample listed in the article's full sample set. |
| MD5 | ac8957a474f8aa812c7b233aafde4723 | Malware sample listed in the article's full sample set. |
| MD5 | af16072864ae0f9d755f8cf00fded359 | Malware sample listed in the article's full sample set. |
| MD5 | af7f1eef22bf5ee3d0a394f53ba7e1b8 | Malware sample listed in the article's full sample set. |
| MD5 | b3a4405d1b8d43545d07b10581008d32 | Malware sample listed in the article's full sample set. |
| MD5 | b6c5f7dfaf9d47cd67380a48df5e1731 | Malware sample listed in the article's full sample set. |
| MD5 | b7d0d5ae09b0d2d2f999c1087c450456 | Malware sample listed in the article's full sample set. |
| MD5 | b862681953e945439167a736ba4cd41b | Binary-confirmed com.android.system.lite sibling enabler build. |
| MD5 | b974ef4106af6b932df352563a9b8b3c | Malware sample listed in the article's full sample set. |
| MD5 | be22c91b4578ac2357a16133615df335 | Malware sample listed in the article's full sample set. |
| MD5 | c55c9d7e12cc273b812ceffca8f62d4b | Malware sample listed in the article's full sample set. |
| MD5 | c75ec7f3bcbc879aae9a21ad544d3232 | Malware sample listed in the article's full sample set. |
| MD5 | c8ea2a7c1f52c4c2474475c28373ee27 | Malware sample listed in the article's full sample set. |
| MD5 | ca7e2d265fc35aede432c4636a2cf4cb | Malware sample listed in the article's full sample set. |
| MD5 | cb19dbf279a3488aec76c17e8e122c14 | Malware sample listed in the article's full sample set. |
| MD5 | cde0490e11db8ad54737c1df59ec658b | Malware sample listed in the article's full sample set. |
| MD5 | cdfcc848e16660d607aba6ecf24567f4 | Malware sample listed in the article's full sample set. |
| MD5 | cf20de9d9ddc952bb2265002d26a916f | Malware sample listed in the article's full sample set. |
| MD5 | cf4f24fdd283f80313565b08fea9d06d | Malware sample listed in the article's full sample set. |
| MD5 | d145b14b9cc15799485f2592b2c16d9a | Malware sample listed in the article's full sample set. |
| MD5 | d3faec4f013c4a1e84a1d681448312c0 | Malware sample listed in the article's full sample set. |
| MD5 | d4ceb05682ecd60f4ebb4e76e02fcf7d | Binary-confirmed com.android.sys.prot enabler variant. |
| MD5 | d56158a2cc8d13778df850907733b2c4 | Malware sample listed in the article's full sample set. |
| MD5 | d5d88214170875386ab855172f881e51 | Malware sample listed in the article's full sample set. |
| MD5 | d6ba4044f9d57f7e86d83187982ed593 | Malware sample listed in the article's full sample set. |
| MD5 | d9fc6b2cd5eaa3929207f1029663d947 | Malware sample listed in the article's full sample set. |
| MD5 | da67e37be01c20566990152ecfb14ed1 | Malware sample listed in the article's full sample set. |
| MD5 | dce5b0dc0e7d7059b5ab8384a7c24ec4 | Malware sample listed in the article's full sample set. |
| MD5 | de66cac88f156c3227749e03bdf7cf54 | Malware sample listed in the article's full sample set. |
| MD5 | e250e5966c119a9098f7818fc6c080e5 | picturetranslate.extractor.text.lite payload installed by the enabler. |
| MD5 | e39bddf592016ad6d0784770df3e2ffe | Malware sample listed in the article's full sample set. |
| MD5 | e51c11442a529dcd06dc7c8e45974ec2 | Malware sample listed in the article's full sample set. |
| MD5 | e6650dc6721aaa27f8a289ff92e613ff | Malware sample listed in the article's full sample set. |
| MD5 | e75e183027bf897eda6447366c7acd01 | Malware sample listed in the article's full sample set. |
| MD5 | e7c56b4f580da53cd0e4f11d1a11e402 | Malware sample listed in the article's full sample set. |
| MD5 | e974cf4cc5d55cddc04f026dd3ea72b8 | Malware sample listed in the article's full sample set. |
| MD5 | e9b91e1d94bb3ff9a1c00b1c13eb7960 | Malware sample listed in the article's full sample set. |
| MD5 | e9ec6d7b50c1e54cd523283b9de55e10 | Malware sample listed in the article's full sample set. |
| MD5 | ed1a6bed83899952b464c27aef9752cc | Malware sample listed in the article's full sample set. |
| MD5 | ee4e778e53ce4d4339d7c7888d06384d | Malware sample listed in the article's full sample set. |
| MD5 | ee70ec99121f4d7c8b5a883e5ab3a858 | com.mb.applock.a02 payload installed by the enabler. |
| MD5 | f0b7b1c940ebcee97eb68f528682fc50 | Malware sample listed in the article's full sample set. |
| MD5 | f456f0c6b89bd3d5124699d43971d094 | Malware sample listed in the article's full sample set. |
| MD5 | f602230f54507cbddf5ef3014737d768 | Malware sample listed in the article's full sample set. |
| MD5 | fac6548a4a7a88156468b809c4f877f5 | Malware sample listed in the article's full sample set. |
| MD5 | fc812444baa071f5141ddad812d673de | Malware sample listed in the article's full sample set. |
| MD5 | fcb9f38cc687fc8a4637e0acdf91ab66 | Malware sample listed in the article's full sample set. |
| URL | hxxps[:]//api[.]weatherlive[.]world/br_upgrade/upgradeV2/getConfigs | Encrypted module-control endpoint supplying plugin versions and download configuration. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationNative code contains an RC4-encrypted framework, framework strings are AES-encrypted, and payload JARs or APKs use misleading .o or .png extensions.T1036 · MasqueradingMalicious packages impersonate system components or app-lock utilities, and some samples falsely record Google Play as their installer.T1059.004 · Unix ShellPrivileged code executes Android package-manager commands, including pm list package -3 and pm disable/enable com.android.vending.T1071.001 · Web ProtocolsThe module-control channel uses HTTPS POST requests to the weatherlive getConfigs endpoint.T1082 · System Information DiscoveryDevice registration reports model, Android release, SDK level, build ID and brand.T1090 · ProxyThe proxyware implements bidirectional TCP relaying to remotely supplied host-and-port targets; no relay targets were returned during the reported test.T1095 · Non-Application Layer ProtocolEnLoaderLib uses a raw TCP socket on port 6000 for its control channel rather than HTTP.T1105 · Ingress Tool TransferThe framework downloads updated kwlib.jar and C2-selected stage-3 plugins containing bundled payload APKs.T1140 · Deobfuscate/Decode Files or Informationlibeasy.so decrypts an embedded APK at initialization, and the framework decrypts encrypted strings at runtime.T1195.003 · Compromise Hardware Supply ChainThe malware arrives in device ROM before sale; researchers could not determine which supply-chain participant integrated it.T1518 · Software DiscoveryThe privileged framework enumerates third-party packages using pm list package -3.T1562.001 · Disable or Modify ToolsPlugins run pm disable com.android.vending before installation and re-enable it afterwards to suppress Play Protect scanning.T1573.001 · Symmetric CryptographyWeatherlive command and telemetry channels use AES-encrypted messages with HmacMD5-signed requests.
People
Malware
Android.Click.429.originAndroid.Phantom.5 (dropper) → Android.Click.429.originAndroid.Joker.310.originand references zhuifengzhe[.]top, which is a domain used by Android.Joker.310.origin (2021) (premium-SMS subscription fraud + remote code loading). This ties a multi-year operatorAndroid.Joker.310/242.originAndroid.Joker.310/242.originAndroid.Phantomto Shenzhen Zediel, delivering malicious apps, some of which are similar to those from Dr.Web’s Android.Phantom operator’s family, now with residential proxyware added.Android.Phantom.5Dr.Web’s Android.Phantom.5 entry lists our exact IOCs cgb.jingongbuxiao[.]com and 5.ahd187[.]com/thirdsdk/flowcashpack/, and references zhuifengzhe[.]top, which is a domain used by Android.Joker.310.origin (2021)com.android.non.szczcom.android.non.szczcom.android.sys.bcprotset of system-sounding names, including com.android.sys.prot, com.android.sys.gmsprot and com.android.sys.bcprot.com.android.sys.dtscom.android.sys.dtscom.android.sys.gmsprotcore shipping under a rotating set of system-sounding names, including com.android.sys.prot, com.android.sys.gmsprot and com.android.sys.bcprot.com.android.sys.protidentified the same malware core shipping under a rotating set of system-sounding names, including com.android.sys.prot, com.android.sys.gmsprot and com.android.sys.bcprot.com.android.system.liteThis system app - com.android.system.lite - was the first one identified, but it turned out to be the tip of the iceberg. As the investigation continued, we identified the same malware core shipping under a rotating setcom.android.weiappscom.android.weiappscom.mobile.applock.enThe same source was installing a wider cluster of payloads, including com.mobile.applock.en, com.dmstudio.weather, com.dl.guard.lock, appicon.diy.tools.prop and picturetranslate.extractor.text.lite.com.mobile.applock.wtwas silently installing and removing a rotating set of payloads on the same devices, among them com.mobile.applock.wt, an app presenting itself as an App Lock tool, while missing the functionality its name suggested.EnLoaderLibProxyware / EnLoaderLib
Vendors
BitdefenderBitdefender's security researchers have identified a malware campaign (dubbed Midnight Mimosa) running on low-cost, multi-brand Android devices built on MediaTek platforms.Cubotare genuine, named brands: "S200 X" is associated with Doogee and "KINGKONG X" is associated with Cubot. These brand names also appeared in a publicly reported firmware-update incident documented on the XDADoogeeThe two highest-volume models, by contrast, are genuine, named brands: "S200 X" is associated with Doogee and "KINGKONG X" is associated with Cubot. These brand names also appeared in a publicly reported firmware-updateGoogleTo top it off, we also discovered 13 apps currently present on Google Play that communicate with the same servers that control the malware. While these apps don’t have the rights that would allow them to be as maliciousMediaTekBitdefender's security researchers have identified a malware campaign (dubbed Midnight Mimosa) running on low-cost, multi-brand Android devices built on MediaTek platforms.Shenzhen Zediel Co., Ltd.Why Shenzhen Zediel Co., Ltd.
Products
AndroidBitdefender's security researchers have identified a malware campaign (dubbed Midnight Mimosa) running on low-cost, multi-brand Android devices built on MediaTek platforms.Bitdefender Mobile SecurityThe investigation began with App Anomaly Detection, a technology in Bitdefender Mobile Security, which flagged com.android.system.lite: a package carrying the name and appearance of a core system component whileGoogle PlayTo top it off, we also discovered 13 apps currently present on Google Play that communicate with the same servers that control the malware. While these apps don’t have the rights that would allow them to be as maliciousGoogle Play StoreThe malware disables the Google Play Store app just before installing a payload app (probably attempting to avoid a potential Play Protect detection).KINGKONG Xhighest-volume models, by contrast, are genuine, named brands: "S200 X" is associated with Doogee and "KINGKONG X" is associated with Cubot. These brand names also appeared in a publicly reported firmware-updatePlay ProtectThe malware disables the Google Play Store app just before installing a payload app (probably attempting to avoid a potential Play Protect detection).S200 XThe two highest-volume models, by contrast, are genuine, named brands: "S200 X" is associated with Doogee and "KINGKONG X" is associated with Cubot. These brand names also appeared in a publicly reported firmware-update
Tools
aapt2AndroidManifest.xml of the enabler (aapt2 dump). sharedUserId=android.uid.system + coreApp + persistent = firmware system component; the privileged permissions are what enable silent install/uninstall and silentADBby the normal route. Clearing the device requires firmware-level cleanup or disabling the component over ADB, and neither is realistic for most people who own these phones. The durable fix sits with the vendors andIDAlibeasy.so load chain (IDA offsets; ET_DYN, imagebase 0 so file offset = vaddr). The family build tag 20240425 is assembled in nativeInit.
Countries
BrazilThe geographic distribution is led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Below the top, there’s a long tail across Africa, Southeast Asia and the Middle East.FranceThe geographic distribution is led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Below the top, there’s a long tail across Africa, Southeast Asia and the Middle East.GermanyThe geographic distribution is led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Below the top, there’s a long tail across Africa, Southeast Asia and the Middle East.ItalyThe geographic distribution is led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Below the top, there’s a long tail across Africa, Southeast Asia and the Middle East.MexicoThe geographic distribution is led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Below the top, there’s a long tail across Africa, Southeast Asia and the Middle East.SpainThe geographic distribution is led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Below the top, there’s a long tail across Africa, Southeast Asia and the Middle East.United StatesThe geographic distribution is led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Below the top, there’s a long tail across Africa, Southeast Asia and the Middle East.