cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2505 articles

Threat Research · huntress.com

Huntress Traces Obfuscated PowerShell Reverse Shell to SSH Persistence

Huntress investigated an encoded PowerShell command on a partner’s system, tracing it to an SSH reverse shell and scheduled-task persistence. The process lineage pointed to the partner’s ScreenConnect instance.
Sep 13, 2022
Threat Research · huntress.com

Huntress Finds NPPSPY Used to Capture Cleartext Passwords in an Exchange Intrusion

Huntress documented NPPSPY deployed during an intrusion to capture cleartext credentials via a malicious Windows network provider. The investigation details the configuration, detection opportunities, and remediation.

Aug 16, 2022
Threat Research · wiz.io

Wiz Details PostgreSQL Flaws in Google Cloud and Azure Managed Services

Wiz researchers describe PostgreSQL service flaws in Google Cloud and Azure that enabled operating-system command execution. They report escalating access in Google Cloud and achieving cross-tenant database access in Azure.

Aug 11, 2022
Threat Research · wiz.io

OMI Vulnerability Let Attackers Predict a Secret and Escalate to Root

Wiz researchers explain how CVE-2022-29149 let attackers predict OMI’s time-seeded secretString, forge privileged messages, and escalate to root. OMI versions before 1.6.9-1 are affected; Microsoft recommends updating.

Aug 5, 2022
Threat Research · blog.talosintelligence.com

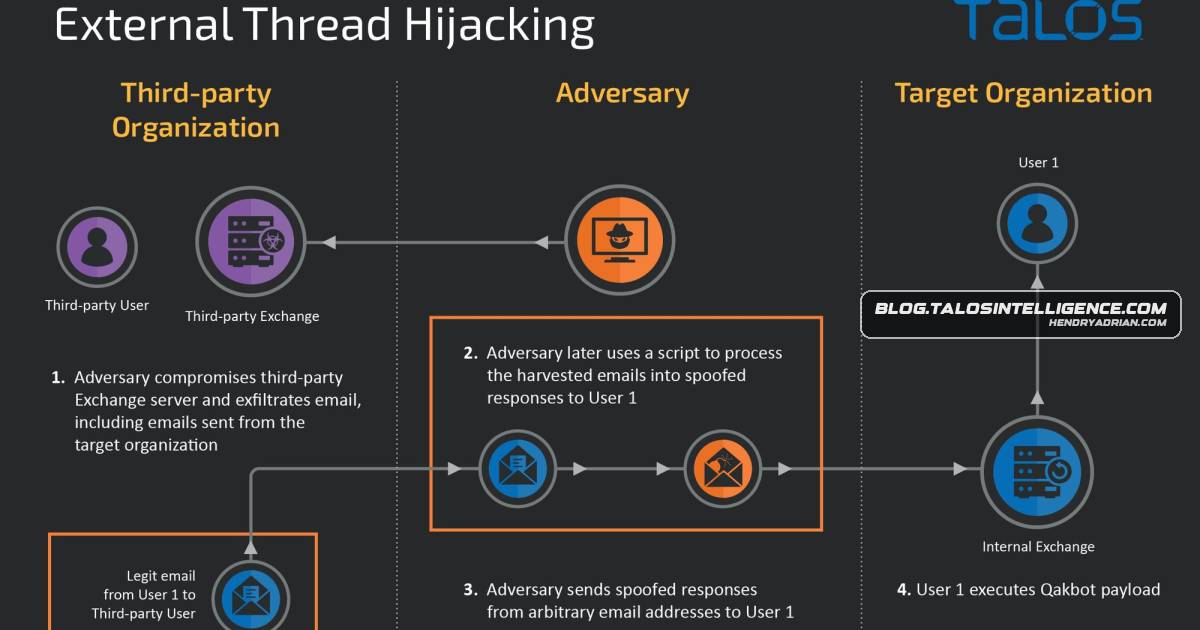
Talos Details Qakbot Campaign Using Hijacked Email Threads Harvested from Other Organizations

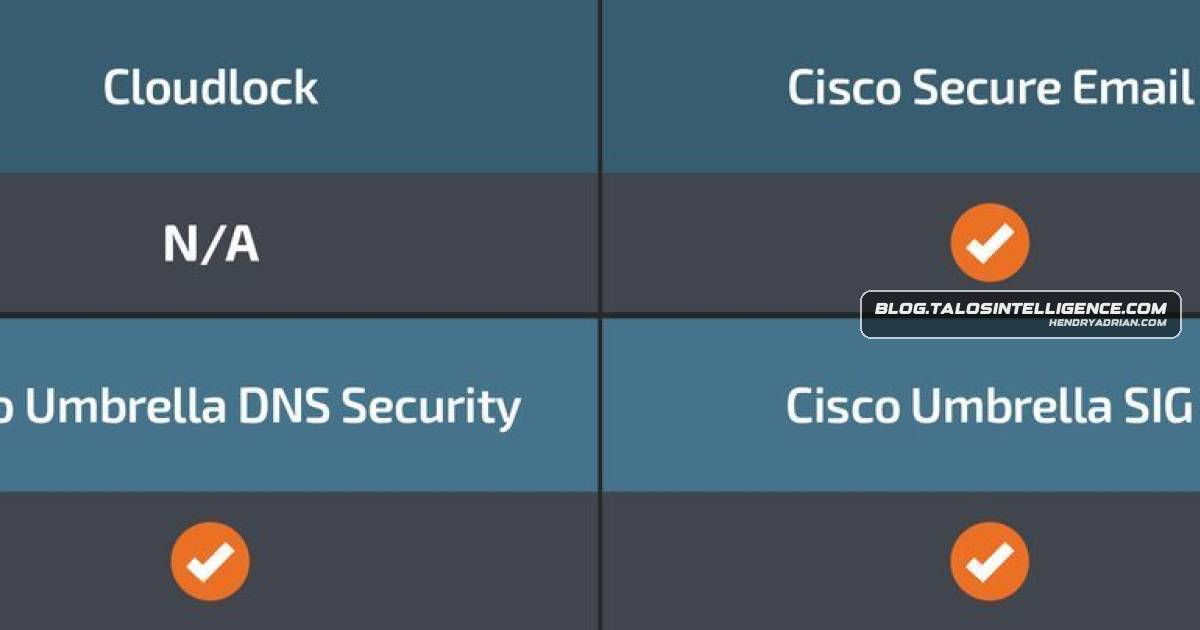
Talos describes a Qakbot campaign that used old email threads likely harvested during ProxyLogon compromises to craft phishing emails, and outlines indicators that distinguish this external thread hijacking from attacks using a victim’s own email system.

Jul 27, 2022
Threat Research · huntress.com

Huntress Traces SQL Server Intrusion Through Defender Alerts and Forensic Evidence

Huntress describes tracing an intrusion to brute-forcing of an internet-facing SQL server, then using Defender alerts, EDR data and server logs to investigate a malicious script that added antivirus exclusions.

Jul 21, 2022
Threat Research · blog.talosintelligence.com

AvosLocker Campaign Used Log4Shell to Enter Network and Deploy Ransomware

Talos detailed an AvosLocker campaign that exploited vulnerable VMware Horizon gateways affected by Log4Shell, then used tools including Sliver, Cobalt Strike and Mimikatz to move through a victim network and encrypt files.

Jun 21, 2022
Threat Research · huntress.com

Huntress Analyzes Follina MSDT Exploit in Microsoft Office Documents

Huntress analyzed how malicious Office documents could invoke MSDT to execute code, including through RTF preview. The article details the exploit, detection and mitigations, and reports that a Microsoft patch was later validated for Windows 10 and 11.

May 30, 2022
Threat Research · huntress.com

Huntress Details Seven Ways Attackers Evade Security Defenses

Huntress examines seven defense-evasion examples, including security-tool exclusions, agent removal, obfuscated scripts, malicious LNK files, AMSI/ETW bypass, user deception and reflective loading.

May 24, 2022
Threat Research · blog.talosintelligence.com

Talos Details BlackByte Ransomware Attacks and Tactics

Cisco Talos reports BlackByte remained active worldwide, using phishing or unpatched systems for access, then tools such as AnyDesk and LoLBins for lateral movement before deploying ransomware.

May 18, 2022
Threat Research · wiz.io

Wiz Details ExtraReplica Flaw Chain Enabling Cross-Tenant Access to Azure PostgreSQL

Wiz found an Azure PostgreSQL Flexible Server flaw chain enabling cross-tenant database replication via privilege escalation and certificate-authentication bypass. Microsoft patched it; public-access servers were affected, while VNet-private servers were not.

Apr 29, 2022
Threat Research · huntress.com

Huntress Analyzes Valak JScript Malware and Its Command-and-Control Mechanisms

Huntress analyzed a JScript sample identified in the community as Valak, tracing registry-loaded code, C2 endpoint generation and task execution. The sample polls multiple C2 domains for commands.

Apr 26, 2022
Threat Research · darkowl.com

Darknet Fraudsters Advertise Tax Refund Schemes and Stolen IRS Checks

DarkOwl reports darknet and Telegram offers for tax-refund fraud using stolen identities and falsified documents, alongside sales of checks stolen from mail, including checks payable to the IRS and state revenue departments.

Apr 18, 2022
Threat Research · huntress.com

Huntress Traces Targeted BABYSHARK Espionage to Voice of America Phishing Lure

Huntress reconstructed a BABYSHARK intrusion at a think tank linked to North Korean tradecraft. A fake Voice of America exchange delivered malicious Word macros, enabling persistence, C2 communications and nearly a year of undetected activity.

Mar 1, 2022
Threat Research · darkowl.com

DarkOwl Finds No Evidence Linking Ukrainian Darknet Data Leaks to January Attacks

DarkOwl analyzed Ukrainian government and civilian data offered on darknet forums and services, finding no evidence it was obtained in January’s cyberattacks. The review documented exposed personal and medical data while noting uncertainty about sellers and attribution.

Feb 24, 2022
Threat Research · huntress.com

Huntress Shows API-Hash Changes Can Evade Cobalt Strike and Metasploit Detection

Huntress researchers found that changing API-hashing logic in Cobalt Strike and Metasploit shellcode evaded many tested detections. They also developed a YARA rule targeting the hashing routine rather than fixed hashes.

Feb 16, 2022
Threat Research · huntress.com

Huntress Investigates Web Shells on VMware Horizon Servers Amid Log4Shell Attacks

Huntress traced Cobalt Strike alerts to VMware Horizon servers, found web shells on exploited hosts, and recreated a trigger that ran a command. Its Process Insights EDR exposed the process tree and enabled a detector for web shell activity.

Jan 25, 2022
Threat Research · huntress.com

Huntress Finds Cobalt Strike Delivered Through VMware Horizon Log4Shell Exploitation

Huntress found 18 of 180 analyzed VMware Horizon servers backdoored and reported a later Log4Shell exploitation wave delivering Cobalt Strike. Process-parent analysis suggested the new deployments exploited Horizon directly, not web shells.

Jan 15, 2022
Threat Research · wiz.io

ChaosDB Research Details Exploit Chain Exposing Azure Cosmos DB Customer Keys

Wiz details how ChaosDB chained Jupyter Notebook misconfigurations to expose Azure Cosmos DB customer keys and internal infrastructure. Microsoft disabled the vulnerable feature in August 2021; researchers observed some credentials being revoked.

Nov 11, 2021
Threat Research · blog.talosintelligence.com

Kimsuky Uses Malicious Blogs to Deliver Malware to South Korean Targets

Talos detailed a Kimsuky campaign targeting South Korean research institutions with malicious Blogspot content that delivered modular malware for reconnaissance, file exfiltration, keylogging, and credential theft. The blogs were taken down before publication.

Nov 10, 2021
Threat Research · blog.talosintelligence.com

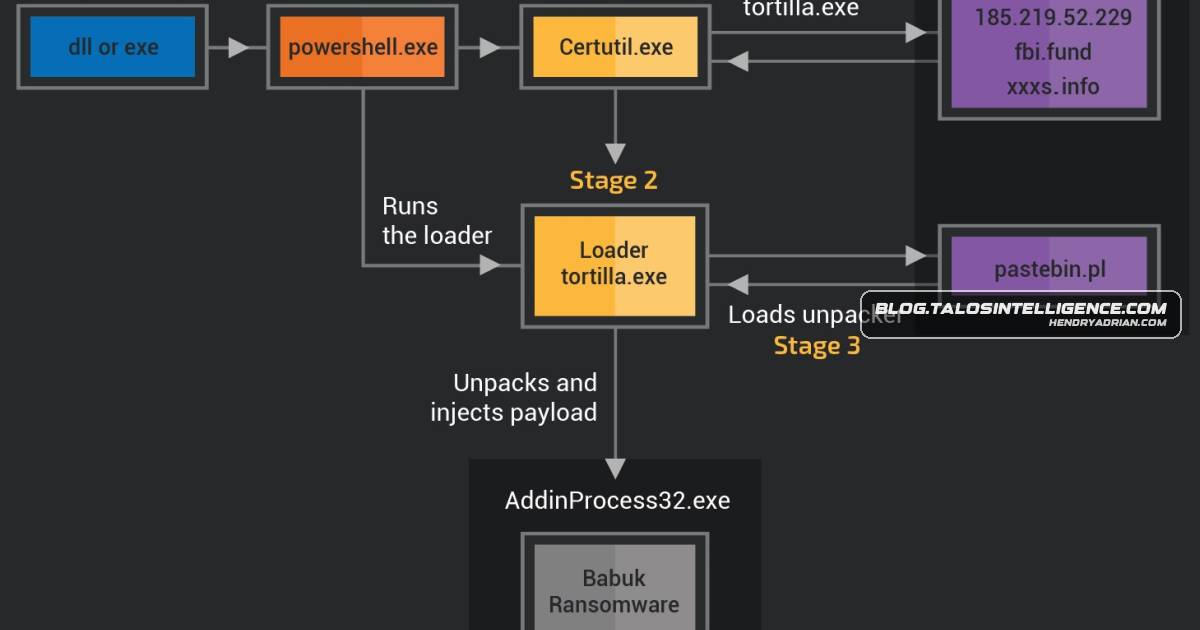
Tortilla Campaign Exploits Exchange Servers to Deploy Babuk Ransomware

Cisco Talos details Tortilla’s campaign exploiting ProxyShell vulnerabilities in Microsoft Exchange to deploy Babuk, disable backups, delete shadow copies and encrypt files. The chain uses PowerShell, staged loaders and pastebin[.]pl.

Nov 3, 2021
Threat Research · blog.talosintelligence.com

SQUIRRELWAFFLE Malspam Campaigns Deliver Qakbot and Cobalt Strike

Cisco Talos details SQUIRRELWAFFLE malspam campaigns that use stolen email threads and malicious Office documents to infect systems, then deliver Qakbot or Cobalt Strike. The article analyzes the loader, C2, and evasion methods.

Oct 26, 2021
Threat Research · blog.talosintelligence.com

Commodity RAT Campaign Targets Government and Diplomatic Entities in Afghanistan and India

Cisco Talos details a campaign targeting Afghan and Indian entities with malicious documents exploiting CVE-2017-11882, custom document infectors, and RATs including dcRAT, QuasarRAT and AndroRAT.

Oct 20, 2021
Threat Research · blog.talosintelligence.com

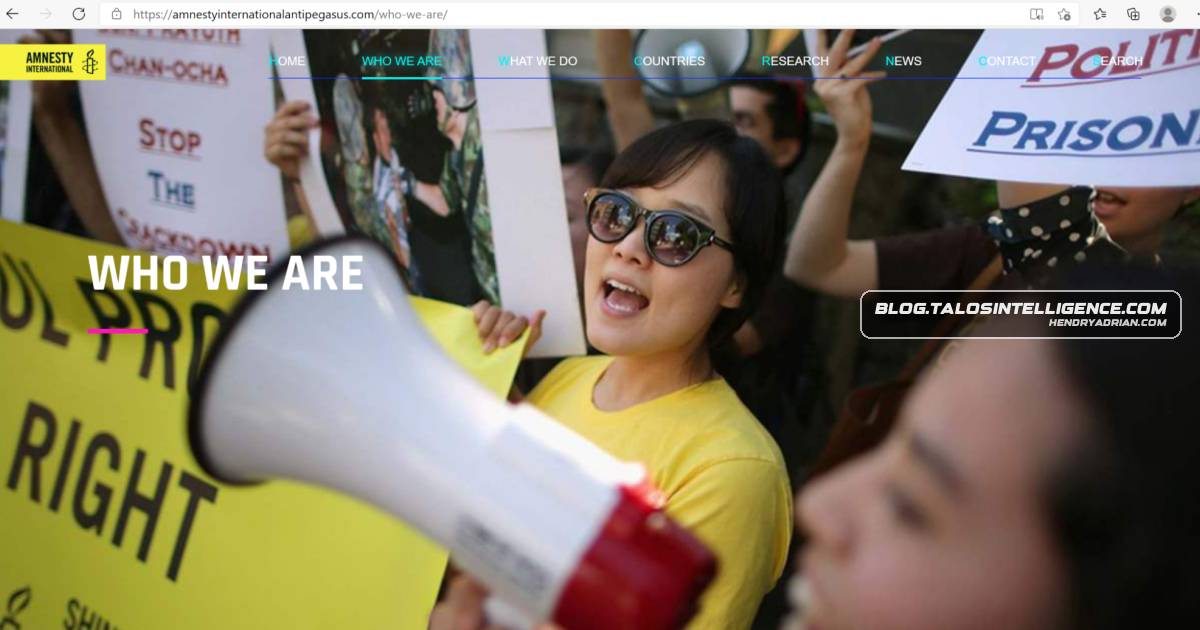
Fake Amnesty International Anti-Pegasus Tool Delivers Sarwent RAT

Talos found a fake Amnesty International site offering anti-Pegasus software that installs Sarwent RAT, enabling remote access, command execution and data theft. The actor’s identity and motives remain uncertain.

Sep 30, 2021
PreviousPage 103 of 105 Next
© 2026 cyber.hendryadrian.com