Fake Amnesty International Anti-Pegasus Tool Delivers Sarwent RAT
Summary
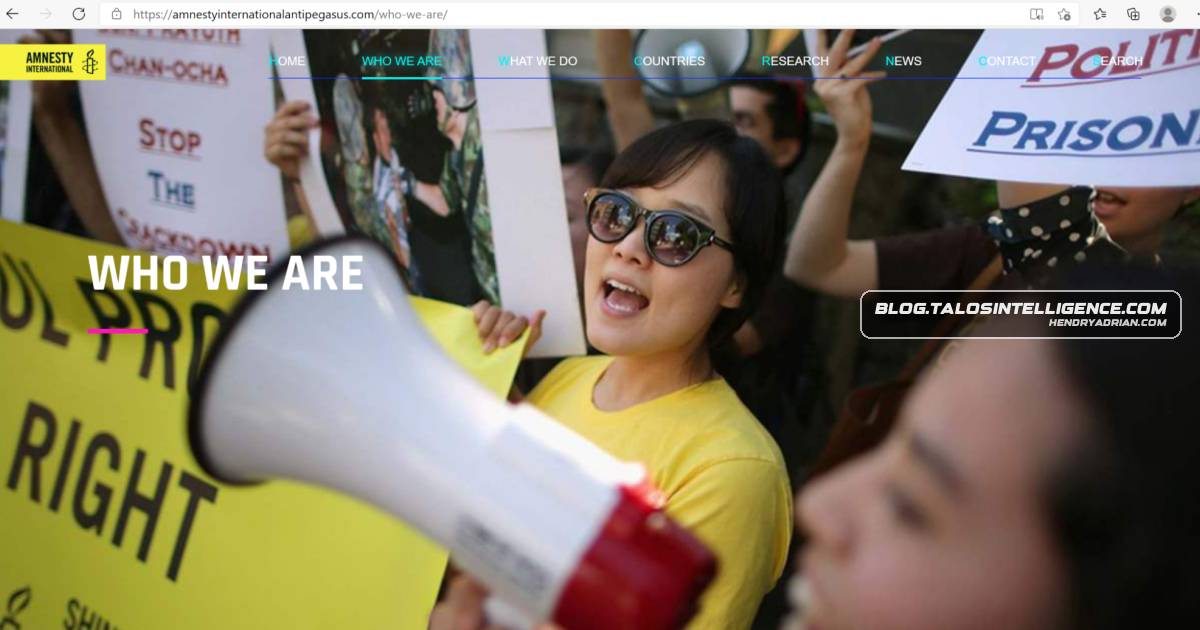
Talos found a fake Amnesty International site offering anti-Pegasus software that installs Sarwent RAT, enabling remote access, command execution and data theft. The actor’s identity and motives remain uncertain.
Key points
- The campaign lures people concerned about Pegasus with a counterfeit Amnesty International site and fake AVPegasus software.
- The download installs Sarwent, a remote access tool that can run commands, use RDP or VNC, upload tools and exfiltrate data.
- Talos observed the malware contacting medicalsystemworld[.]site for command-and-control activity and identified additional campaign domains.
- The campaign’s lures were accessed worldwide, but Talos reported low volumes and found no evidence of a widespread email campaign.
- Talos assessed with high confidence that the operator is Russian-speaking and located in Russia, but could not determine whether the activity was financially motivated or state-supported.
- Talos blocklisted two associated IP addresses and recommended user awareness of lures exploiting current events.
Article Details
- Attack Vectors
- A phony Amnesty International website advertised a fake anti-Pegasus antivirus, “AVPegasus,” that installed Sarwent malware.
- Sarwent contacted its command-and-control domain, beaconed victim system information, and allowed remote command execution and desktop access through VNC or RDP.
- The malware could download another copy of itself for updates, upload and execute additional tools, and exfiltrate data.
- Defensive Notes
- The article advises defenders and administrators to warn users about spam and lures exploiting current events.
- Cisco Talos blocklisted the two IP addresses associated with the campaign.
- The article lists Cisco Secure Endpoint, Secure Web Appliance, Secure Email, Secure Firewall, Secure Network/Cloud Analytics, Secure Malware Analytics, Umbrella, Snort rules, and Orbital queries as detection or blocking options.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | alwaysstriveandprosper[.]space | Inactive secondary domain contacted by the malware and assessed as a possible backup C2. |
| DOMAIN | amnestyinternationalantipegasus[.]com | Attacker-used lure domain hosting the fake Amnesty International site and malware offer. |
| DOMAIN | amnestyvspegasus[.]com | Attacker-used lure domain directing visitors to download the malware. |
| DOMAIN | antipegasusamnesty[.]com | Attacker-used lure domain promoting the fake anti-Pegasus software. |
| DOMAIN | medicalsystemworld[.]site | Sarwent command-and-control domain contacted by the malware. |
| DOMAIN | mementomoriforlife[.]ru | Domain whose passive DNS records linked it to IP addresses associated with the campaign. |
vitapruneaummi51@gmail[.]com | Registration email listed for the attacker-used lure domain amnestyinternationalantipegasus[.]com. | |
vladmakop@rambler[.]ru | Registration email listed for the attacker-used lure domain antipegasusamnesty[.]com. | |
| IPV4 | 185[.]215[.]113[.]67 | IP address associated with the campaign and blocklisted by Talos. |
| IPV4 | 194[.]9[.]71[.]129 | IP address associated with the campaign and blocklisted by Talos. |
| IPV4 | 87[.]249[.]53[.]124 | IP address associated with the campaign and blocklisted by Talos. |
| SHA256 | 59a447749878aec9ed0a9a71332b8a3d50eafee21de446b70a370786d548ee05 | Hash listed in the article’s indicators of compromise. |
| SHA256 | 5df8a6f08f0eeb1b05f949328674444778c4c078f03e35c0efff268c58dc6396 | Hash listed in the article’s indicators of compromise. |
MITRE ATT&CK
T1021.001 · Remote Desktop ProtocolSarwent could activate RDP to allow remote desktop access to the victim machine.T1021.005 · VNCThe adversary could access the victim desktop remotely via VNC.T1036 · MasqueradingThe malware was presented as a legitimate anti-virus program named “AVPegasus” to deceive users.T1041 · Exfiltration Over C2 ChannelSarwent could exfiltrate data from the victim computer, and its initial communication sent victim system information.T1059.001 · PowerShellThe malware allowed the adversary to issue commands via PowerShell.T1059.003 · Windows Command ShellThe malware allowed the adversary to issue commands via the command line.T1071 · Application Layer ProtocolSarwent beaconed to its command-and-control site over network communications.T1105 · Ingress Tool TransferSarwent attempted to download another copy of itself for updating and could receive additional malicious tools.
People
Malware
Vendors
Appleusers given the recent spotlight on the Pegasus spyware. In addition to Amnesty International's report, Apple also had to recently release a security update for iOS that patched a vulnerability attackers wereCiscoCisco Talos recently discovered this actor building a site that has almost the identical look and feel of Amnesty International's legitimate site. The original site has a white background behind the menu, but as you can
Products
Adaptive Security ApplianceCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.AVPegasusThe attacker-controlled homepage advertises the "Amnesty Anti Pegasus" software, which the actor is calling "AVPegasus."Cisco DuoCisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.Cisco Secure Network/Cloud AnalyticsCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.Cisco Secure Web ApplianceCisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.Firewall Management CenterAdditional protections with context to your specific environment and threat data are available from the Firewall Management Center.iOSIn addition to Amnesty International's report, Apple also had to recently release a security update for iOS that patched a vulnerability attackers were exploiting to install Pegasus. Many users may be searching forMeraki MXCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.PegasusA wolf in sheep's clothing: Actors spread malware by leveraging trust in Amnesty International and fear of PegasusSnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org. SIDs: 54357, 57901StealthwatchCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.Stealthwatch CloudCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.Threat Defense VirtualCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Threat GridCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.UmbrellaUmbrella, Cisco's secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.
Tools
PowerShellremote desktop protocol (RDP) and Virtual Network Computing (VNC), despite the malware having shell and PowerShell execution capabilities.RDPvery often in the wild. It has several means of executing remote tasks, including remote desktop protocol (RDP) and Virtual Network Computing (VNC), despite the malware having shell and PowerShell executionVNCmeans of executing remote tasks, including remote desktop protocol (RDP) and Virtual Network Computing (VNC), despite the malware having shell and PowerShell execution capabilities.
Countries
Colombiaaffected are the United Kingdom, the United States, Russia, India, Ukraine, Czec Republic, Romania and Colombia, as can be seen on the screenshot below.Czech RepublicGermanyfound victims in several countries including, but not limited to, Colombia, India, the United States and Germany. We were however unable to identify the kind of lures used in the previous campaigns.Indiaduring our investigation, the countries affected are the United Kingdom, the United States, Russia, India, Ukraine, Czec Republic, Romania and Colombia, as can be seen on the screenshot below.Romaniathe countries affected are the United Kingdom, the United States, Russia, India, Ukraine, Czec Republic, Romania and Colombia, as can be seen on the screenshot below.Russiathe C2 active during our investigation, the countries affected are the United Kingdom, the United States, Russia, India, Ukraine, Czec Republic, Romania and Colombia, as can be seen on the screenshot below.Ukraineour investigation, the countries affected are the United Kingdom, the United States, Russia, India, Ukraine, Czec Republic, Romania and Colombia, as can be seen on the screenshot below.United Kingdomlower volume. In the case of the C2 active during our investigation, the countries affected are the United Kingdom, the United States, Russia, India, Ukraine, Czec Republic, Romania and Colombia, as can be seen onUnited Statescase of the C2 active during our investigation, the countries affected are the United Kingdom, the United States, Russia, India, Ukraine, Czec Republic, Romania and Colombia, as can be seen on the screenshot below.