
Talos Details Qakbot Campaign Using Hijacked Email Threads Harvested from Other Organizations
Summary
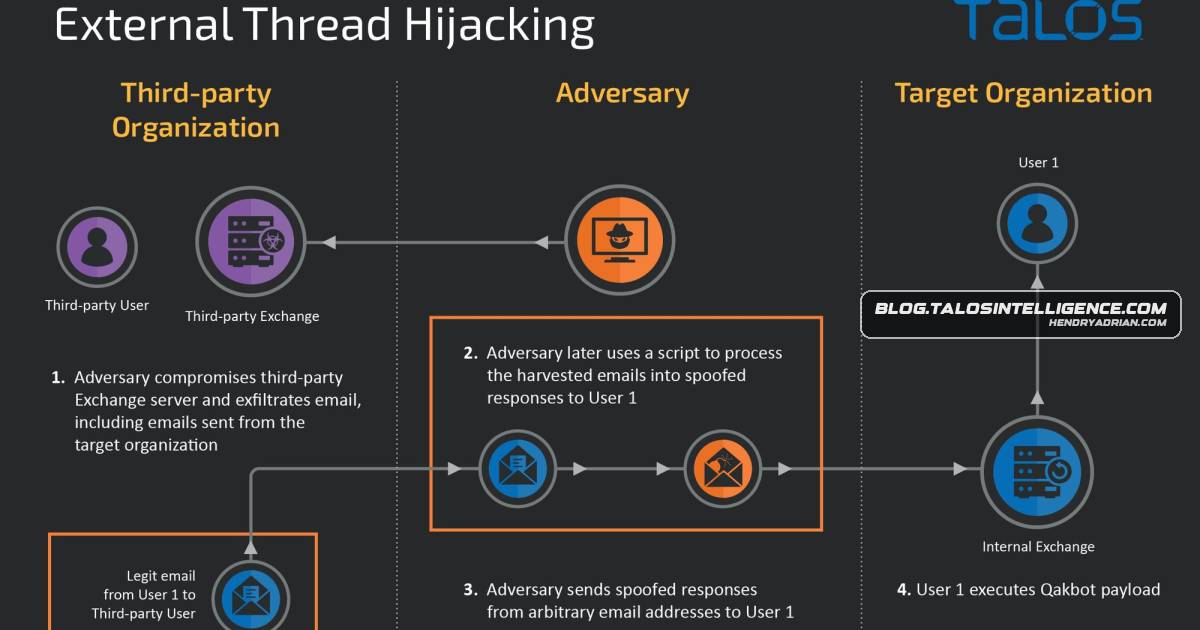
Talos describes a Qakbot campaign that used old email threads likely harvested during ProxyLogon compromises to craft phishing emails, and outlines indicators that distinguish this external thread hijacking from attacks using a victim’s own email system.
Key points
- Talos observed the campaign in June 2022; it used old emails likely harvested from multiple organizations during 2021 ProxyLogon compromises.
- Attackers selected threads involving target organizations, added malicious content, and sent phishing emails from external mailboxes.
- Unlike victim thread hijacking, this method did not require access to the target organization’s Exchange server or inboxes.
- Indicators include spoofed external senders, old threads, few internal-to-internal exchanges, malformed replies, and partially removed email addresses.
- Talos also observed repeated use of the same harvested threads across multiple phishing waves.
- Qakbot can steal financial and login information and load additional malware; Talos notes Snort rules and ClamAV signatures can detect it.
Article Details
- Attack Vectors
- In the June 2022 campaign, attackers used old email threads likely harvested from multiple organizations during 2021 ProxyLogon-related compromises to craft phishing emails targeting senders or recipients at other organizations.
- Attackers reportedly added malicious content to legitimate email-thread text and sent the resulting phishing emails from spoofed external mailboxes.
- In the described victim-thread-hijacking approach, attackers compromise a target organization's Exchange server or an individual email account, then use legitimate threads to craft and send malicious replies.
- Defensive Notes
- Look for spoofed external sender addresses, old email threads, few internal-to-internal threads, malformed replies, and email addresses partially removed from message bodies.
- Check for repeated use of the same harvested email threads across multiple phishing waves.
- Cisco Talos notes that Snort rules and ClamAV signatures can detect Qakbot deployment and that Snort rules can detect and prevent additional malware loaded from Qakbot C2 servers.
MITRE ATT&CK
CVE
Threat Actors
Malware
IcedIDon access to a victim’s Exchange server or individual email account. Most recently, this was seen in an IcedID campaign in early 2022 where the adversary compromised a victim’s Exchange server and used it as a baseQakbotWhat Talos Incident Response learned from a recent Qakbot attack hijacking old email threads
Vendors
Products
ClamAVRegarding the malware delivered in this campaign, there are numerous Snort rules and ClamAV signatures users can deploy to detect the deployment of Qakbot. While the primary focus of this post covers the process of howMicrosoft Exchangewe assess were likely harvested during the 2021 ProxyLogon-related compromises targeting vulnerable Microsoft Exchange servers.SnortRegarding the malware delivered in this campaign, there are numerous Snort rules and ClamAV signatures users can deploy to detect the deployment of Qakbot. While the primary focus of this post covers the process of how